
❌

Normal view

There are new articles available, click to refresh the page.
Yesterday — 29 October 2026Hackaday

Exploring What’s Left of Google’s VR Dreams

By: Tom Nardi
29 October 2026 at 10:00

You’re likely familiar with Google’s Cardboard, and the legions of cheap virtual reality headsets it spawned. By sticking a smartphone to the wearer’s head, all these headsets needed were some basic optics to provide a surprisingly effective VR experience. You may even know about Google Daydream initiative that came a few years later, which not only improved the basic Cardboard design but brought with it new software features such as VR-specific improvements to the Android operating system and a version of the Play Store dedicated to 3D games and applications.
But unless you’re a true Google devotee, what you may not know is that the search giant partnered with Lenovo to produce a stand-alone Daydream headset called the Mirage Solo in 2018. A full year before the Oculus Quest hit the market, the $399 device combined the guts of a smartphone with a 2560×1440 display running at 75 Hz, a pair of cameras in the front that let it see the world around the user in three dimensions, and a gyroscopic handheld controller to provide an immersive VR experience without having to be tethered to a computer. In addition to the standard consumer version, there was even a “Business Edition” of the headset specifically marketed to schools, offices, and hospitals as a way to deliver VR content without having to invest in any additional infrastructure.

So why isn’t the Mirage Solo better known? Because in classic fashion, just a few years after it was released, Google decided they were no longer interested in virtual reality and shuttered the entire Daydream program. The software components it introduced were stripped out of Android, the 3D Play Store was taken down, and the back-end mechanisms necessary to register new headsets were turned off. Almost overnight, the Mirage Solo became a stereoscopic paperweight.

Or at least that was the official story, anyway. I recently came across a Lenovo Mirage Solo at a thrift store for $25, and despite my initial Internet searches strongly indicating that it would probably be worthless, it seemed worth the gamble to find out for myself.

Know Before You Buy

Usually I’d just jump into the cool stuff, but I think in this case it’s probably wise to get some details clear before continuing. There’s a good chance that some of you may decide to pick up a Mirage of your own after reading this, or perhaps you’ve already got one and wandered in from an Internet search. However you’ve come to read this article, I don’t want to give you the wrong impression about the realities of the situation.
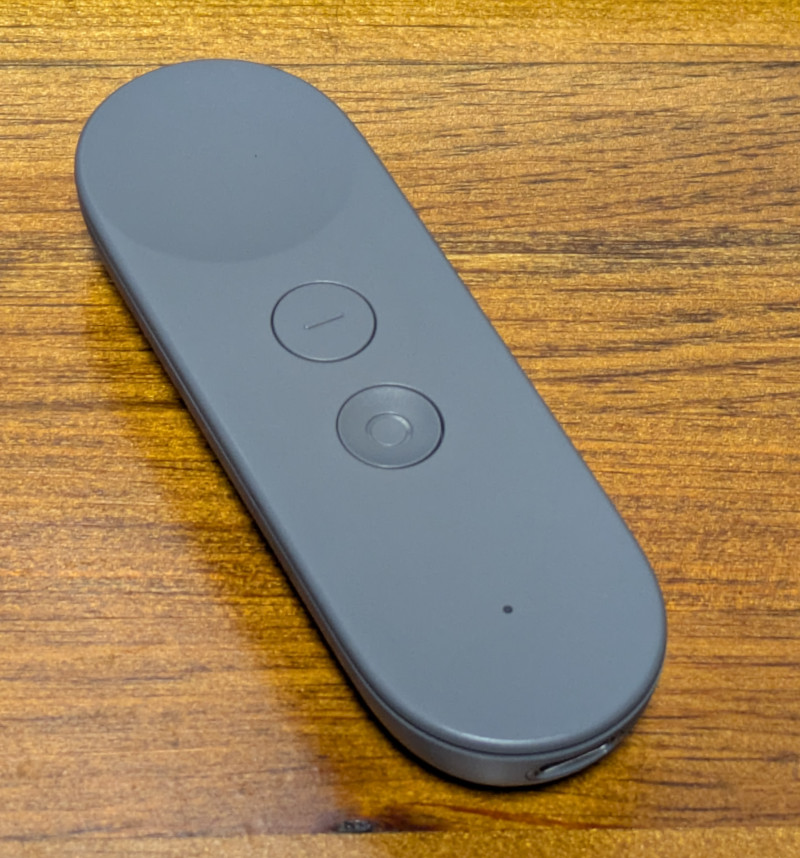
So let’s start with the most important thing: do not buy a Lenovo Mirage Solo unless it has the motion controller! I really can’t stress this one enough, as to my knowledge, there is no way to navigate the UI of the Mirage without it. Many of the cheap units you’ll find on the second-hand market are only priced that way because the controller is missing, so be careful. If you’re wondering, the controller doesn’t need to be the original one that was sold with the Mirage for it to work, but spare controllers are understandably in high demand and are usually priced accordingly.

The second thing to remember is that Daydream is a dead platform, and the software running on the Mirage is now at least six years out of date. Anything that still works on it only does so because whatever upstream service or API it relies on hasn’t yet changed enough to break anything. As of this writing, I personally believe enough of the software still works to make the Mirage worth picking up if you can get a good price on one, but that’s not necessarily going to be true forever.

Escaping Captivity

Alright, let’s assume you’ve just pulled a brand new Lenovo Mirage Solo out of the box in 2026 and want to use it, what does that look like?

The first time you boot it up, you won’t get very far. After it asks you to connect the controller and does some internal housekeeping, you’ll be presented with a dialog that walks you though connecting to a WiFi network and adding it to your Google account. Unfortunately, this process will never complete because Google has flipped some switch on their end — although you wouldn’t know it on the device, as the only feedback you’ll get is a pop-up message advising you that there’s been an unspecified problem and that you should try again later.

Thankfully, somebody over at Google left us a backdoor. If you click on the four corners of this dialog, starting with the top-left and working clockwise, you’ll be able to bypass the provisioning process. After some more loading and a bit of a tutorial about using the controller and navigating the user interface, you’ll be facing (literally) the next problem.

You are standing in an open field west of a…wait, no. Sorry that’s something else. You will be in a virtual forest though, and if you look around you’ll see waterfalls, a winding stream, and birds flying around.
It’s all very slick, but the thing we’re mainly worried about right now is the huge message in front of us saying the system can’t connect to the internet. What’s actually happened is that the system can’t connect to the mothership because the Daydream API has been turned off, but apparently there was no canned error message to convey that condition so this is what we get.

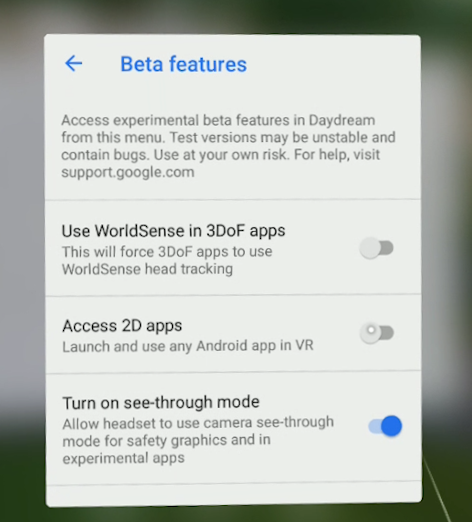
But again, the developers at Google have provided us a way forward. If you navigate to the settings screen there is an option for Beta Features, and underneath that section you’ll find an entry that says Access 2D Apps. Once you select it you’ll be warned that the behavior of standard Android applications in Daydream may be unpredictable, and the Mirage will reboot.

This is where things start to get interesting. Once the headset restarts there will now be a new tab in the application launcher labeled 2D, and under it you should see an icon for the standard Play Store. Once you go into the settings and add your Google account, you’ll be able to browse the Store and download whatever games or applications you want — so long as they don’t mind running on Android 8.0, anyway.

Android Apps…in Space!

Gaining access to standard Android applications opens up a huge world of possibilities. While the older hardware of the Mirage Solo and the outdated OS means you won’t necessarily be able to run the latest and greatest pieces of software, there’s still a lot you can do, from watching Netflix to working with spreadsheets in Google Docs and connecting to your Linux box over SSH. The on-screen virtual text input is good enough for simple tasks, but connecting a physical keyboard over USB or Bluetooth makes the whole experience vastly more enjoyable.
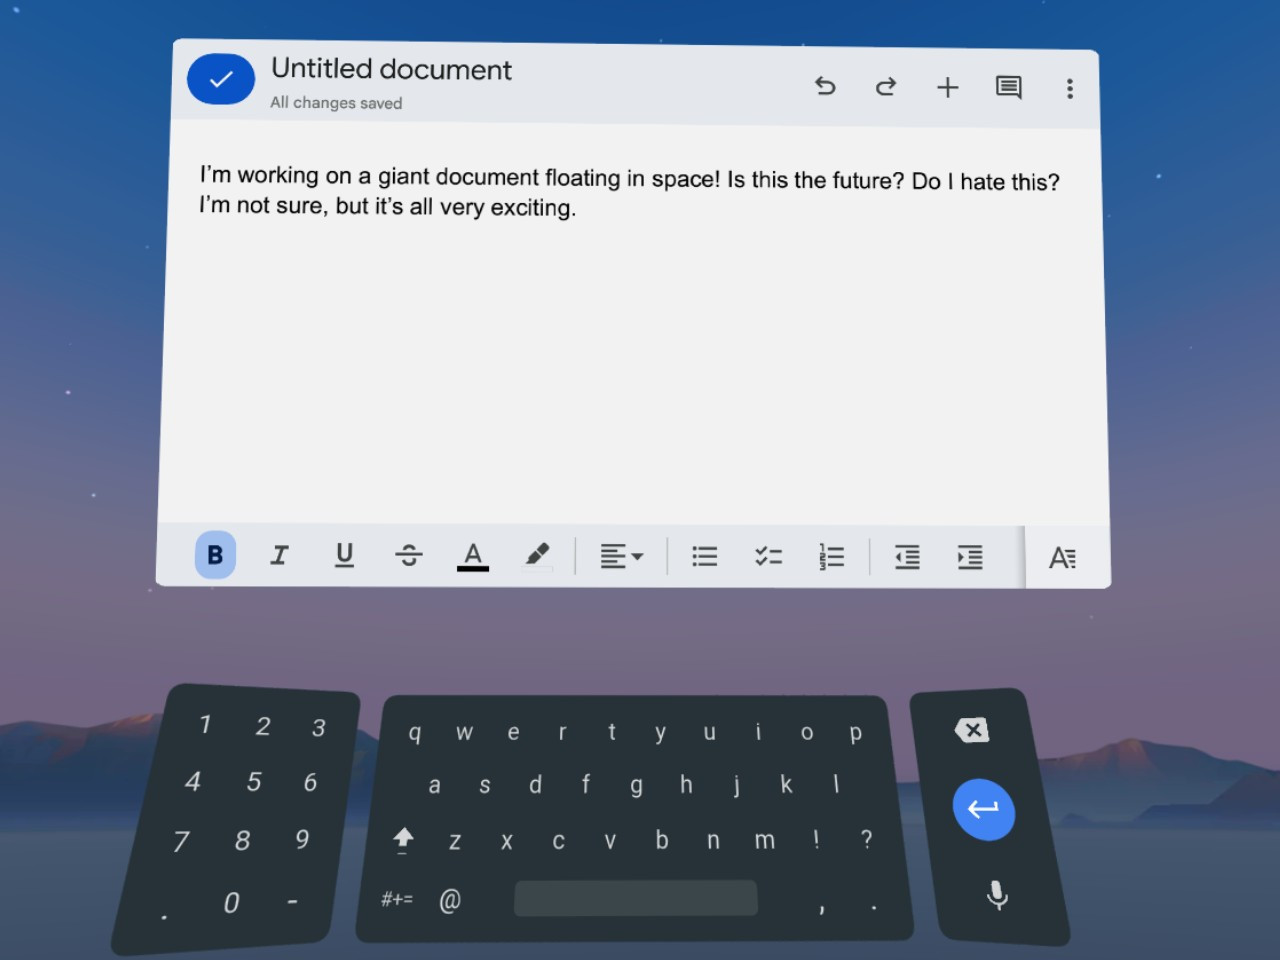
When running 2D applications in Daydream, they will appear as a giant display floating in front of you. Some of the apps will only work in portrait mode as if they think they are running on a normal phone, but in most cases you can grab the corner of the window and stretch it out into a landscape orientation that better fits the fairly impressive field of view offered by the Mirage.
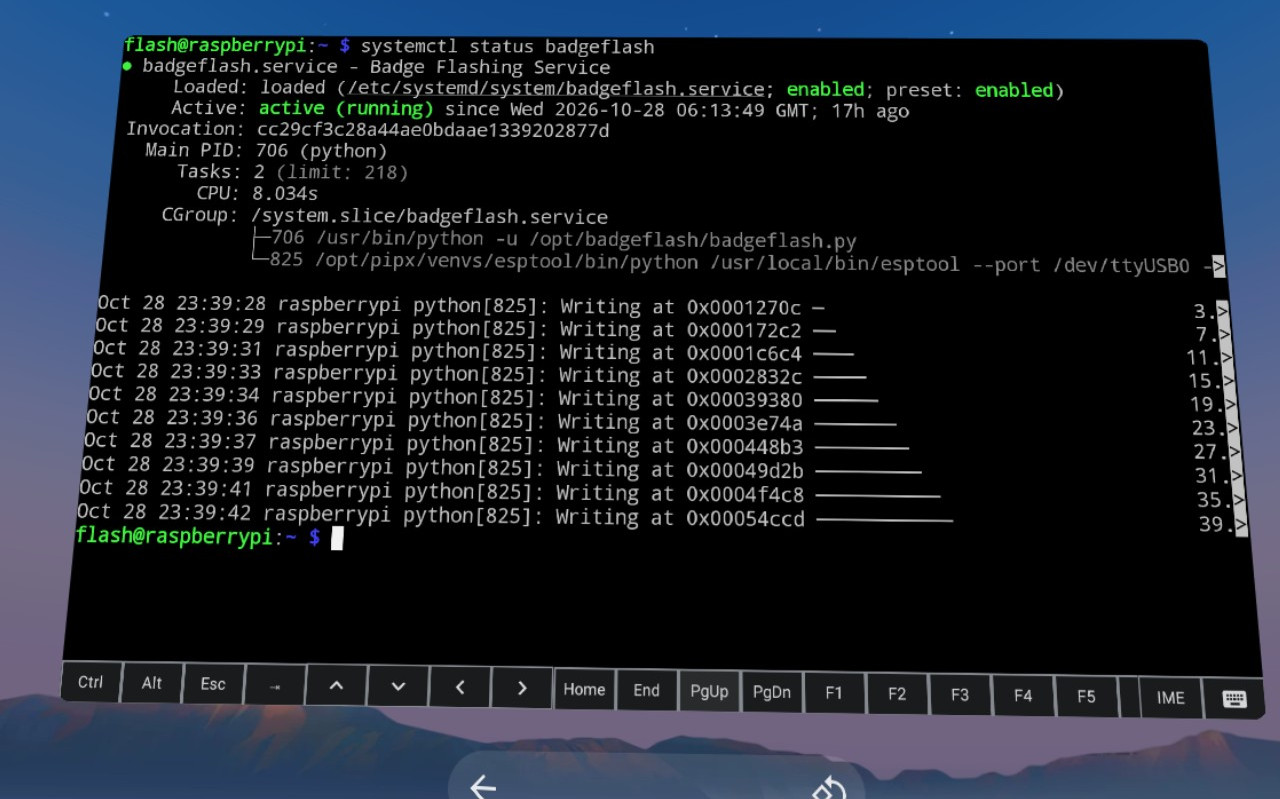
The only real issue with using 2D Android apps on the Mirage is how simplistic the window management is. You can move the window and resize it, but there’s no provision for having multiple windows open at the same time. In fact, under normal circumstances there doesn’t even appear to be a way to switch between running applications without having to go all the way back to the main menu — although I did discover that when you have a physical keyboard connected you can use Alt-Tab to bring up the stock Android task switcher, which helps.

Entering the Third Dimension

At the start of this article I explained that the 3D Play Store was shuttered, and with it, all the games and applications that were actually designed to take advantage of virtual reality. But as we all know, nothing is every really gone on the internet, and thanks to some dedicated fans at the Opendream project, much of the Daydream software has been preserved and can be installed on the Mirage.

I’ll leave exploring the catalog of available Daydream software as an exercise for the reader, but at the very least you should install Firefox Reality. It’s not only a far more capable browser than Android’s stock version of Chrome, but it’s an excellent example of how immersive Daydream could be when the software took advantage of the platform.
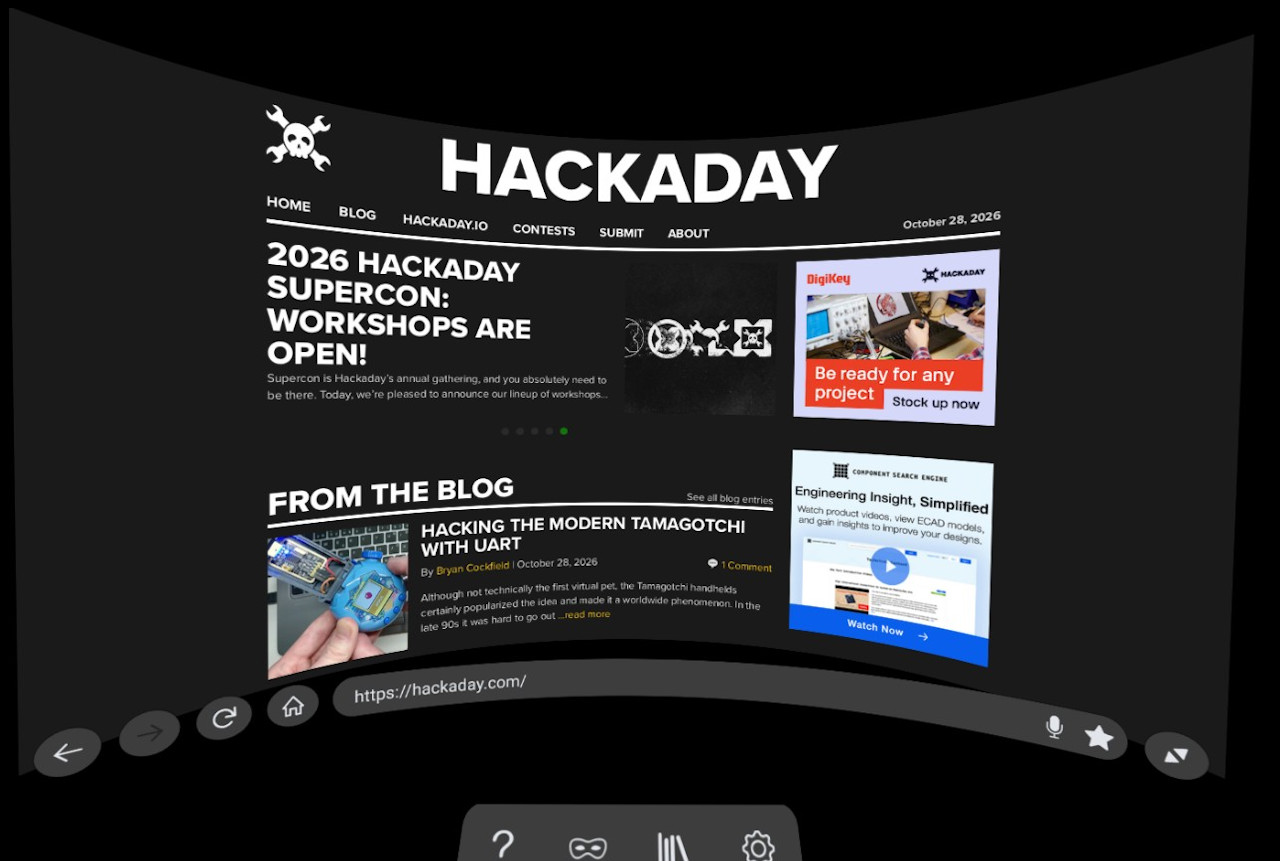
The browser still shows up as a giant floating display, but now you’ve been transported into a darkened environment and have far better control over how everything looks. It also features a far more pronounced 3D effect, with pop-ups that actually hover over the page, and a 3D render of the remote that moves around in space in front of you as you swipe around the pages. There’s even support for curving the entire display, which makes for a very unique browsing experience.

Speaking of a unique experience, I’ve saved my absolute favorite for last — YouTube VR. It’s so well implemented and immersive that I’ve actually watched whole movies with this thing on my head. While there’s plenty about Daydream that clearly needed some more time to cook, Google really pulled out all the stops for this one.

Everything works as you’d expect, including 360 degree videos and even purchased content that’s attached to your Google account. At least for me, I’d go so far as to say that the experience is good enough that it’s worth getting a used Mirage Solo just for watching YouTube alone.

Nothing Lasts Forever

As I said at the start, it’s important to understand that the Lenovo Mirage Solo still having any sort of functionality in 2026 is something of a fluke. It’s supposed to be a dead product, and neither Google nor Lenovo want anything to do with it. There are no updates coming, no tech support, and no warranty.

At any moment, the YouTube API could make some kind of breaking change, or your favorite apps might get an update that prevents them from working on such an old version of Android. You’d be absolutely crazy to buy this headset at anything near its full retail price.

That being said…if you can get a good deal, and by that I mean certainly under $100 and closer to $50 – $70 USD, I think there’s enough life left in the device to make it worth picking up. If you end up getting one and doing something cool with it, I’d love to hear about it.

Before yesterdayHackaday

Single Button, Handheld Gaming Console

14 October 2026 at 19:00

Those of us who grew up in the 70s and 80s might be familiar with the Atari 2600 console and its now relatively unrecognizable (by modern standards) controller with only a single button and stiff whole-hand joystick. By comparison, the Steam Deck has somewhere around 24 buttons and two joysticks depending on how they are counted. But even the Atari might be providing more user inputs than are really necessary for quality gaming. Take a look at the Dinoboy, a handheld console with only a single button.

Part of what makes this system work is that it’s playing the classic dinosaur jumping game first included in Google Chrome which loads when the browser can’t connect to the Internet, and the user’s single input was the space bar. In this case, the handheld has its single button where the user’s thumb naturally rests. The console itself is in two parts, hinged where the button is placed. When unfolded, the top half reveals a wide screen and the bottom half is held by the hand. The screen supports two color formats, a black and white style and another which replicates the dot matrix display of the original Game Boy.

The small handheld console has another trick up its sleeve too. [Paul], the system’s creator, built it as a way to stop doomscrolling so along with having this quick-deploying game on hand, there’s also an NFC tag hidden near the hinge which, when swiped passed a phone, also turns that phone’s airplane mode on. It’s a double-whammy of removing the gamer from the dark patterns and algorithms dominating the mainstream Internet. And, this isn’t [Paul]’s only dinosaur jumper console either. We recently featured a similar (but much larger) build of his housed in a classic arcade-style cabinet.

This Week in Security: New Spectre Attacks, Crushing Quantity of Linux Vulns, Google Gets Too Much AI, and Hacking Lawnmowers

9 October 2026 at 10:00

Just-in-time, or JIT, compilation could be considered a fundamental backbone of modern computing.  JIT compilation turns scripting languages like JavaScript or intermediary binary forms like Web Assembly into native code on the fly, giving web apps, and things that are web apps under the covers like Electron-based tools, near native speed.  A new paper explores leveraging JIT systems to revive Spectre-v2 attacks against processors.

Most modern processors gain performance by using a trick called “speculative execution”.  The processor guesses the likely result of a compare, and begins executing some of the next instructions before the results are actually known.  If the processor guessed right, things continue and there is a speed gain because it can jump ahead, but if the processor guessed wrong, any instructions that were run and any side effects of running them are discarded and execution resumes on the actual path.  In theory, anyhow.

In practice, the Spectre class of attacks targets branch prediction. It was discovered that when the wrong branch was chosen, not all of the results were truly hidden; Patterns of failures in guessing branches can be used to leak behavior processing encryption keys and other activities. The attacks evolved with the research dubbed Spectre-V2, which showed that non-privileged contexts, like non-root users and virtual machines, could poison the instruction prediction and use it to read arbitrary memory.  Fixes to the Linux kernel and other platforms were required to mitigate the worst of the effects.

The paper shows that by using self-modifying code in the JIT, the processor can be tricked into loading cached versions of the instructions.  The fixes to the kernel to prevent Spectre attacks include identifying malicious code patterns that attack the branch prediction, and stopping or changing them:  By causing the CPU to execute the cached copy of instructions instead of the live copy, the attack ignores the fixed instructions entirely and can attack the branch prediction algorithm.

To prove the attack is feasible in the real world, the researchers targeted several JIT compilers, including the SpiderMonkey JavaScript engine used by Firefox, the eBPF JIT found in the Linux kernel, and GraalVM, the JIT used in Python.  They found success with each, demonstrating that the attack is at least plausible.

Research like this is unlikely to be an instant world-melter, and will help find possible mitigations in the future to prevent these sorts of attacks.  Operating systems that support a high-security “lock-down” mode, like macOS and iOS, often disable JIT entirely, out of concern about these sorts of attacks.  There’s probably no need to start disabling JIT on every system, but attacks like these have a tendency to evolve.

Enormous List of Vulnerabilities Patched in Linux

Updated Linux kernels are available for most distributions, with a truly intimidating list of patched security issues.  As this Debian post states, “Several vulnerabilities have been discovered in the Linux kernel that may lead to a privilege escalation, denial of service or information leaks.”  Several, in this case, is a load-bearing word, and you should go check out the CVE list.  I’ll wait.

This, apparently, is what the AI Vulnpocalypse looks like today. After Windows patched over a thousand vulnerabilities in a single Patch Tuesday, we probably had a pretty good idea what would be coming. With over 1,200 vulnerability report IDs listed in the patch, manually understanding the security impact is extremely daunting if not entirely impossible. A random sampling shows vulnerabilities in compression handling, denial of service attacks from local users, and memory corruption that may or may not be exploitable, but with a list this huge that’s hardly exhaustive.

For normal admins and users, there isn’t much else to do besides apply the patches and hope they don’t cause new problems.  Linux overall has a better track record with patches not breaking they entire system, but it’s not unheard of, and with this much churn, the chances of something going wrong of course increases.  Patching is almost always a better option than not patching and hoping you don’t get owned, though!

Google Stops Bug Bounty Program Because of AI

“Stop hitting yourself” comes to mind. Google has stopped the Google Open Source Vulnerability Rewards Program, the bounty program offering rewards for finding bugs in the companies open source releases.

Surprising nobody, the bounty program has been flooded with “low effort” and “low quality” AI generated reports. Google says maintainers were overwhelmed with false reports containing AI hallucinations, and that the program would be re-evaluated in 2027. While AI-assisted, or even directed, security research is our new normal, if the results aren’t checked by someone able to confirm they’re legitimate, submitting them helps nobody.

Can’t help but feel some schadenfreude that a company shoving AI into every aspect of our lives is then impacted by AI being shoved everywhere, but in the end swamping developers with bogus reports keeps them from fixing the real bugs and benefits nobody, so it’s hard to find a positive takeaway on this one.

Retailer Asos Hacked, Ransomed

Customers of the Asos online clothing store who installed the Asos app got first-hand evidence that the platform was hacked by a ransomware crew.  The attackers used the Asos app push notifications to send an alert to all customers: “Dear Asos DPO and IT, we have fully compromised the Snowflake instance.  Engage with us, or we will leak it.”

Snowflake is a cloud-scale database company, and has been implicated in several other attacks over the past few years, including a large hack in 2024 by the ShinyHunters group that led to compromises of Ticketmaster, AT&T, Lending Tree, and others. It’s unclear how the Asos Snowflake instance was compromised.

Direct-to-consumer ransomware demands aren’t new, and apply pressure to the impacted company. The message itself is a well-phrased piece of propaganda, casting the hacked company as the villain who isn’t protecting the customers by engaging in the extortion demands. Asos so far indicates that “basic customer information” like name and contact information, but possibly not payment details.

Accenture Contractor Implicated in FBI Hack

The FBI has removed a contractor from the multinational tech company Accenture, after determining that the breach of the Oracle PeopleSoft instance that then led to the breach of the information of the entire FBI agent and employee system, was avoidable.

Details remain scarce, but this would imply that the vulnerability used by ShinyHunters wasn’t a zero-day after all. One of the most dangerous phases of the vulnerability lifecycle is when both the bug and patch are known, because researchers can often quickly deduce the vulnerability from the patch and write an exploit. This seems to be what happened here.

Rarely are specific individuals held directly responsible for patch cycles. Patching production services of large organizations is usually determined at an institutional level.  Reading between the lines, the individual may have been directly tasked with doing the work of installing the patches and didn’t.

Last week, the ShinyHunters group made public statements that it did not plan to leak the stolen information, and was simply using it as a means to get press coverage of their grievances against the FBI.  The promise not to leak the addresses of the families of agents is probably appreciated by the agents themselves, but unlikely to do much to slow the pursuit.

Domain Registrars Hacked to get TLS

Ars Technica reports that three domain registrars were hacked and the access used to obtain certificates for Google domains.

By hacking the registrars and changing the assignment of country-level Google domains for the “gh” (Ghana), “sl” (Sierra Leone), and “as” (American Samoa) top-level domains, the attackers were able to pass automated domain ownership checks required for obtaining SSL certificates.

To be usable, an attacker would have to be able to intercept and redirect the traffic between a user and the compromised domain, and the user would have to be attempting to connect to the Google domains in that country TLD in the first place. The attack may have been targeted against those specific countries, or may have simply been an opportunistic attempt to harvest credentials. Conceivably, the certificates could be used on malicious WiFi networks to try to capture user sessions from other Google domains and services.

Google has already implemented filtering for the specific certificates in Chrome, but these fixes do not help other browsers or services, and Google says it may not have identified all the compromised domains. Google also cautions that the domains of other companies were also compromised, and that those companies must take independent action to protect their users, but the impacted companies were not provided.

Hacking Lawnmowers

Researchers found a series of vulnerabilities in the Mammotion robot lawnmower platform. After spending “a few days on Mammotion’s cloud”, they demonstrated an admin account takeover and a full dump of all 337,000 customers, and for the cherry on top, unauthenticated access to first-person mode on mower. In case you wanted to help tidy up someones lawn or just go for a drive around the neighborhood.

After finding previous security issues in Mammotion products which were not, to put it delicately, fixed according the current norms of security patching in the industry, the company was on the radar.  In addition to discovering that there was no rate limiting on brute-forcing account recovery and changing any users password, the team also found that factory systems lacked any authentication at all, hard-coded authentication tokens were baked into the firmware, and it may be possible to add any customer’s mower to any account.

After repeated attempts by the team to get the company to set up security contacts and respond to the vulnerability reports, it appears that the issues whith are remotely testable have been resolved, but for a fun read be sure to check the article and the email threads as an example of how, probably, you shouldn’t handle security reports as a company.

❌
❌