❌

Reading view

There are new articles available, click to refresh the page.

Pentesting: Twelve Caesars – Community Tools for Offensive Security

Welcome back, aspiring cyberwarriors!

Recently a new project was released by Praetorian. Praetorian is open-sourcing the offensive tools their red team actually uses on engagements. They call it 12 Caesars and their team is planning to release one tool a week for twelve weeks. Every tool is written in Go and ships as a single binary with zero external dependencies.

Each tool is assigned a Caesar name and a blog post, where you can learn more about these tools.
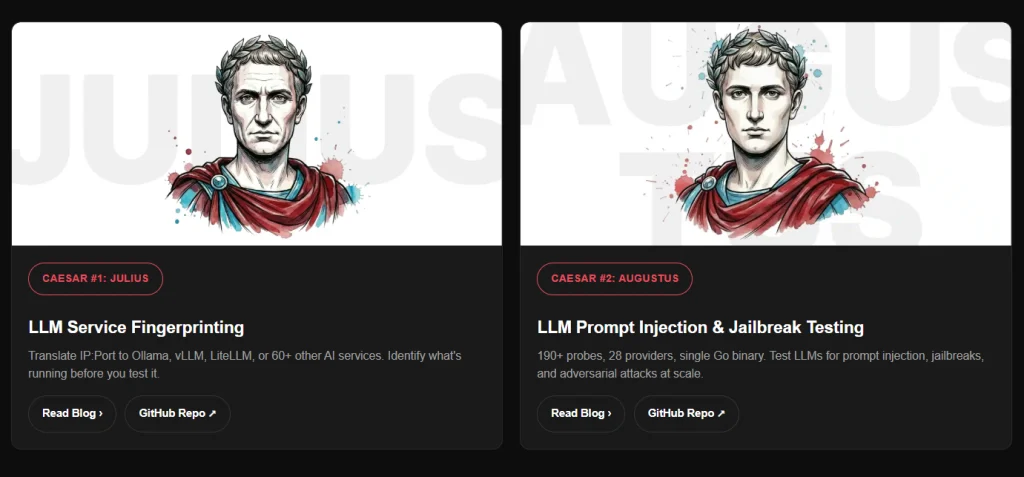
We’ll look at four of these tools, including the basic ones, to make this article suitable for everyone. Before we proceed, it’s important to remind you that you can only test systems you own or have explicit written authorization to test. We will use our lab for it.

Titus

Our first tool is Titus. Titus finds credentials, API keys, and tokens in source code, files, git history, container images, and more. The tool has 487 detection rules covering AWS, GCP, Azure, GitHub, Slack, databases and hundreds of other services. Similar to TruffleHog, it can validate credentials as it finds them by calling the provider APIs.

It’s also available as a Burp Suite extension and a Chrome extension.

kali > curl -sL -o titus https://github.com/praetorian-inc/titus/releases/latest/download/titus-linux-amd64
kali > chmod 777 titus
kali > ./titus --help
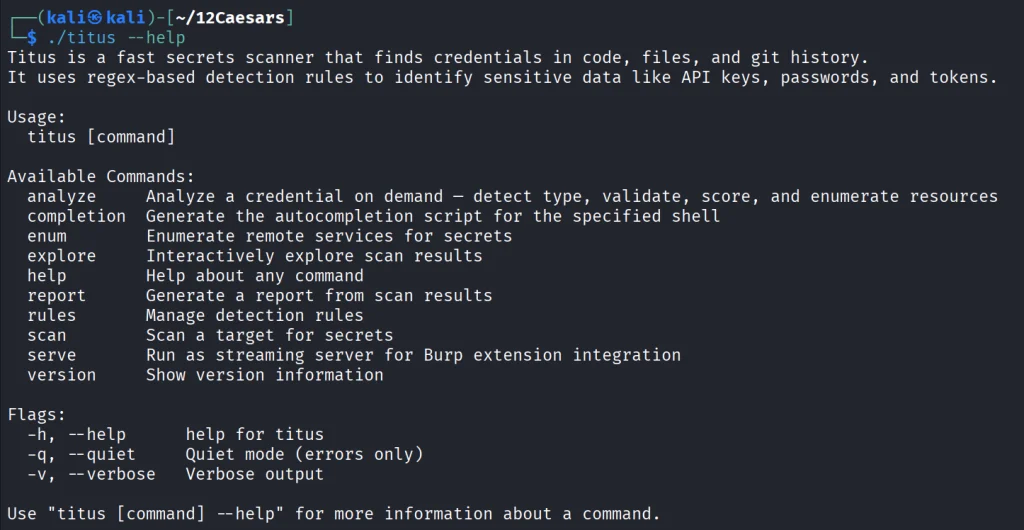
Let’s start by pointing it at test keys released by Truffle Security.
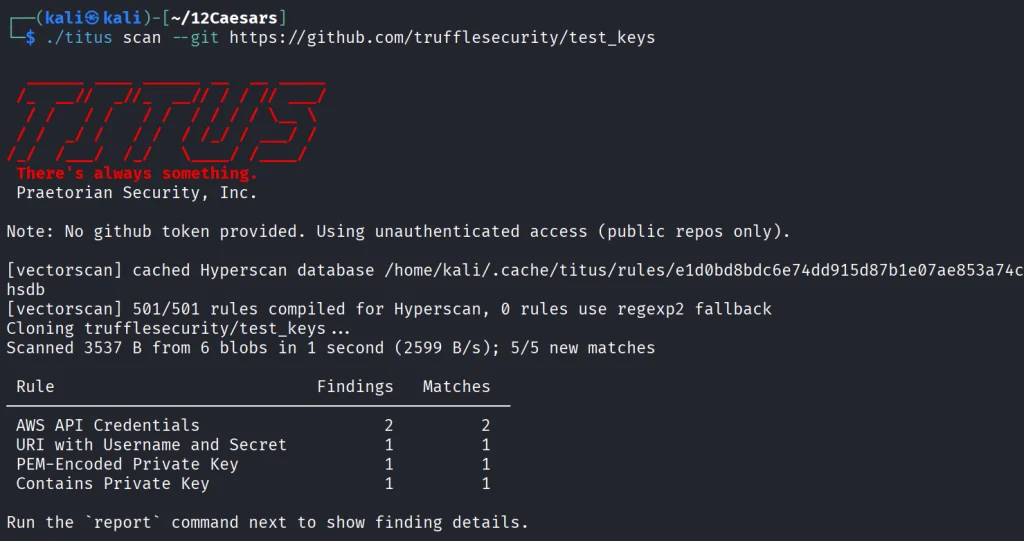
It found all the keys in the repo. Companies often publish their secrets by accident. Some live in the repositories for years, so it’s good to do regular checks to prevent unnecessary leakage.

Nerva

Nerva is a fingerprinter supporting 170 protocols across TCP, UDP, and SCTP, plus dozens of HTTP technology fingerprinters. You can feed it with open ports from naabu, nmap or other tools and it’ll tell you what’s actually running with its version.

kali > curl -sL -o nerva.tar.gz https://github.com/praetorian-inc/nerva/releases/download/v1.70.3/nerva_1.70.3_linux_amd64.tar.gz
kali > tar --no-same-owner -xzf nerva.tar.gz
kali > chmod 777 nerva
kali > ./nerva --help
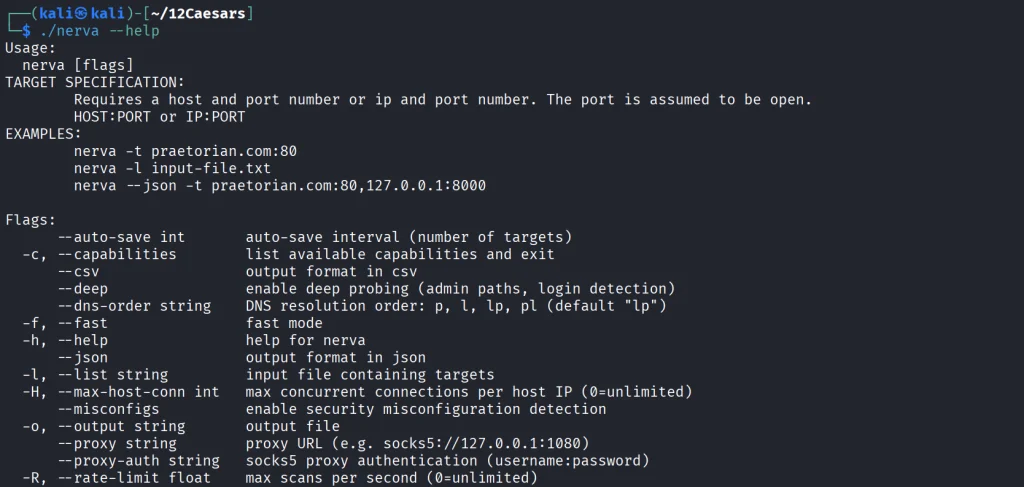
Now let’s use our Ubuntu to show a basic test.

kali > ./nerva -t 192.168.131.9:22,11434
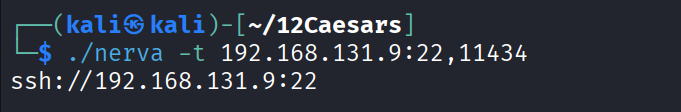
It will be way more useful when you work with big lists of corporate assets during a pentest.

Brutus

Brutus is a modern Hydra alternative. It supports more than 40 protocols including SSH, RDP, MySQL, PostgreSQL and a lot more. Brutus was built to work with Nerva or naabu output.

kali > curl -sL -o brutus.tar.gz https://github.com/praetorian-inc/brutus/releases/latest/download/brutus-linux-amd64.tar.gz
kali > tar --no-same-owner -xzf brutus.tar.gz
kali > chmod 777 brutus
kali > ./brutus --help     
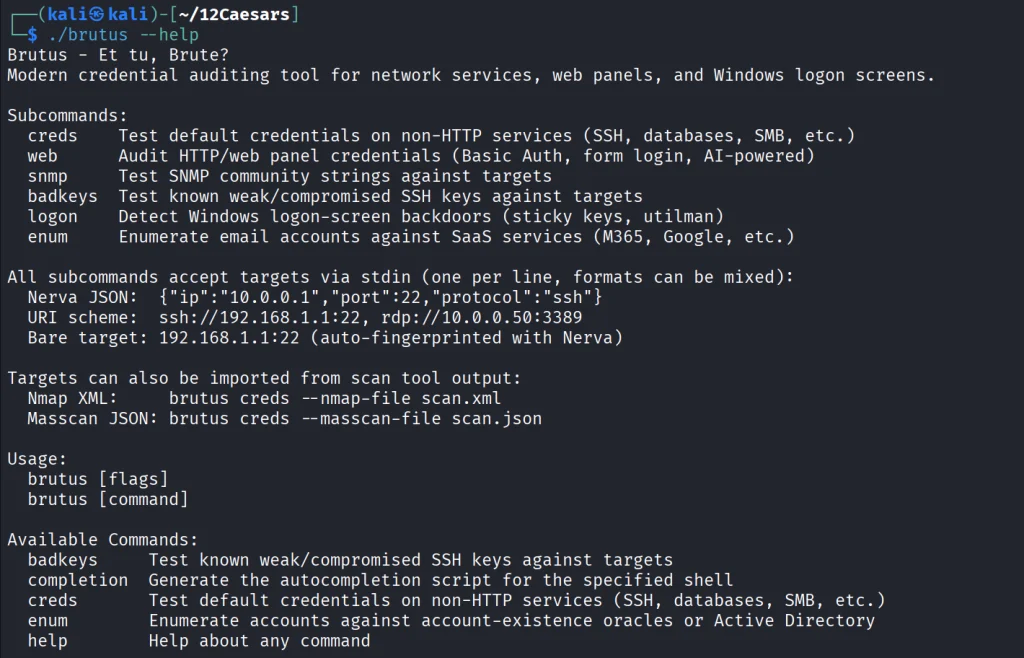
Each command has its own help menu to make it easy to work with.

kali > ./brutus creds --help
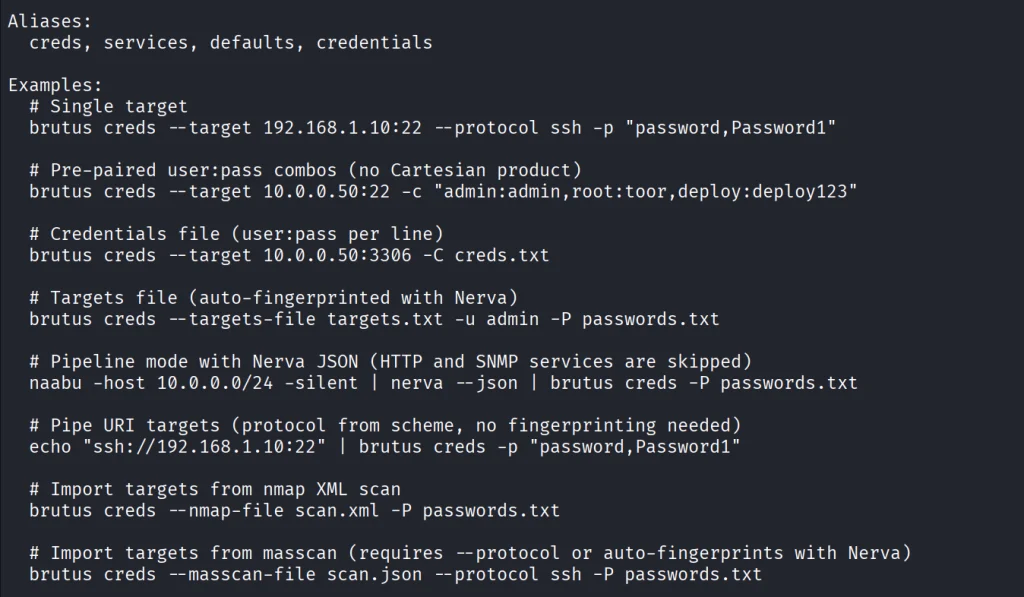
Now once again lets use our Ubuntu to spay passwords. 

kali > ./brutus creds --target 127.0.0.1:22 --protocol ssh “admin:admin”
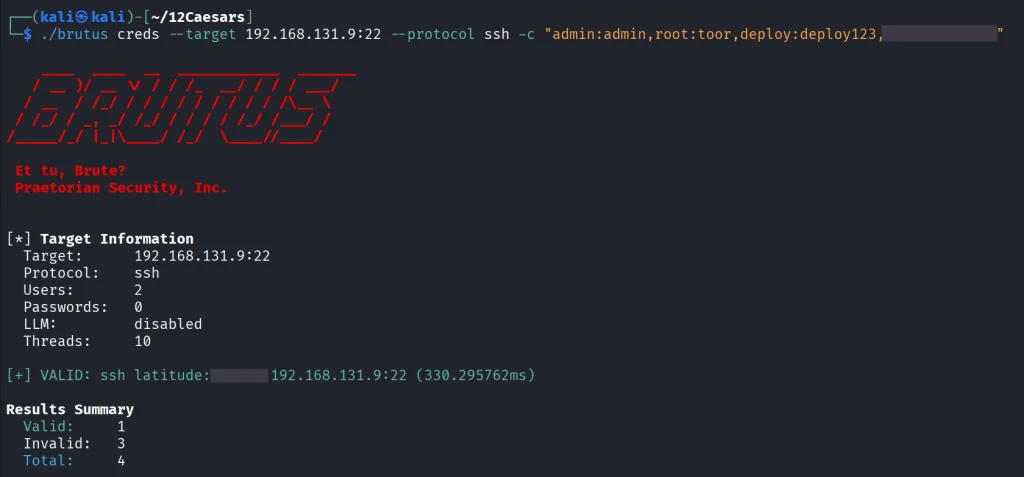
It was easy. As mentioned before, this tool chains with Nerva, and that’s how it becomes useful to test the entire infrastructure against common password and detection.

Julius

With AI services proliferating inside corporate environments, we want to know what LLM infrastructure is running on our hosts. Julius will fingerprint more than 60 AI services including Ollama, vLLM, LiteLLM, LocalAI, Hugging Face TGI, AWS Bedrock and AnythingLLM. It can also list available models from endpoints.

kali > curl -sL -o julius.tar.gz https://github.com/praetorian-inc/julius/releases/download/v1.5.1/julius_1.5.1_linux_amd64.tar.gz

kali > tar --no-same-owner -xzf julius.tar.gz
kali > ./julius --help
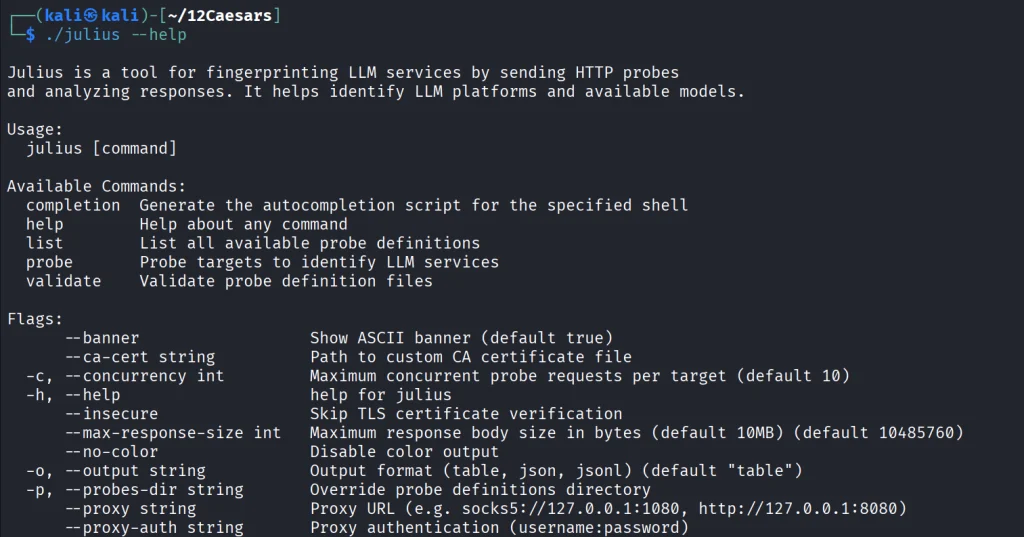
You can list all the AI services Julious can fingerprint: 

kali > ./julius list
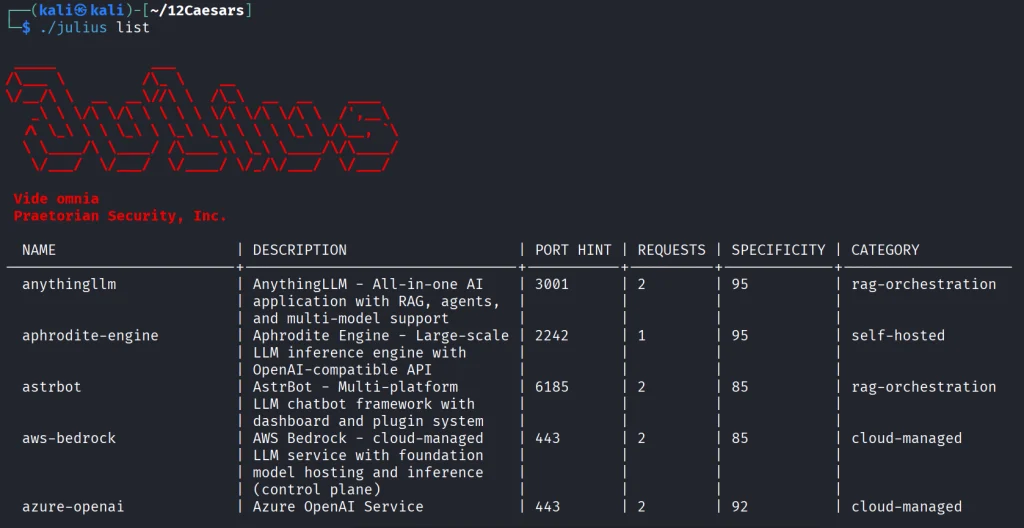
We will take a look at our machine.

kali > ./julius probe http://192.168.131.7:11434

Ollama sits on port 11434, and it’s important not to leave it exposed publicly, because everyone can use your models without authentication.

Summary 

There are more tools available in this project. Most of them are meant to be chained together and work well this way. The company says its team is actively using these same tools during their engagements. While you won’t need everything at once, experiment with those tools and see what fits you best.

If you like red teaming, we have our Red Team Operator training, where we cover more tools and techniques to help you emulate real APT work, so you can give a company a realistic stress test and help make it secure.

The post Pentesting: Twelve Caesars – Community Tools for Offensive Security first appeared on Hackers Arise.
Introduction to Web Application Firewall (WAF) and Ways to Bypass It

Welcome back, aspiring cyberwarriors and bug bounty hunters!

Hacking web applications nowadays requires not just a well-written exploit but also a way to bypass a Web Application Firewall (WAF). Despite being a staple of modern security architecture, WAFs are often misunderstood: they are usually treated as magic shields when, in fact, they are complex systems with strengths, limitations, and blind spots.

In this article, we will cover three core topics: WAF operation, WAF fingerprinting methods, and bypass techniques. Let’s get rolling!

Understanding Web Application Firewalls and Detection Logic

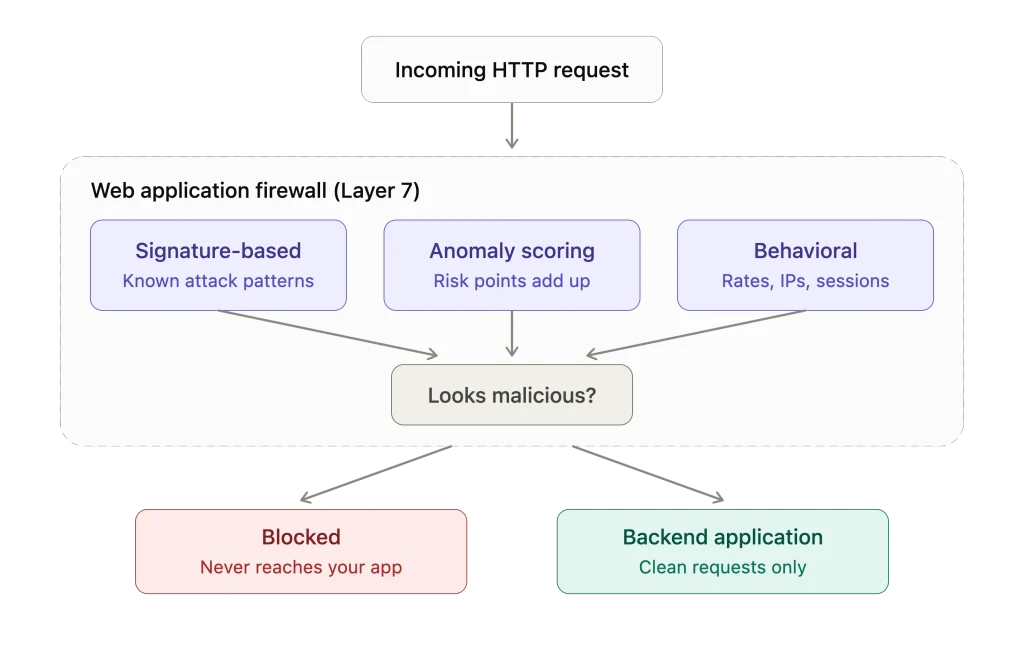
A Web Application Firewall (WAF) is a security tool that sits in front of your web app and checks every incoming request before it reaches your code. It operates at Layer 7 of the OSI model, the application layer where HTTP traffic lives. Unlike traditional network firewalls, a WAF looks at the actual content of requests, like headers and URLs, not just their source.

WAFs typically use three methods to assess requests.

First is signature-based detection, similar to antivirus software. The WAF compares incoming requests against a list of known attack patterns and blocks any matches. This method is fast and effective for common attacks, but it can miss variations.

Next, anomaly scoring assigns points for various suspicious elements within a request. When the total score exceeds a threshold, the WAF blocks the request. This method is flexible because a single odd detail isn’t concerning, but a combination is.

Finally, behavioral detection focuses on client activity over time. The WAF monitors request rates and patterns and shuts down suspicious behavior like automated login attempts, even if each request seems harmless.

Combining these strategies gives a WAF a strong understanding of traffic, making it a key defense for serious web applications.

Fingerprinting a WAF

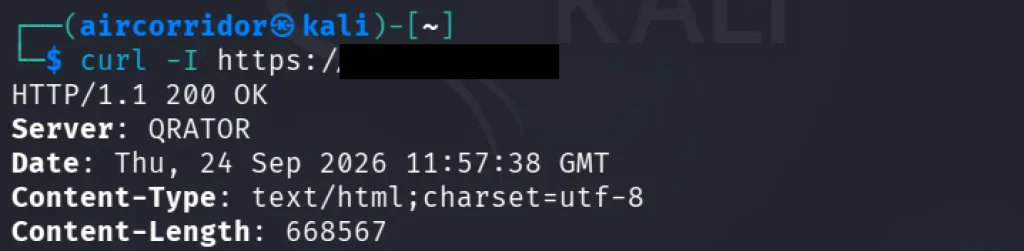
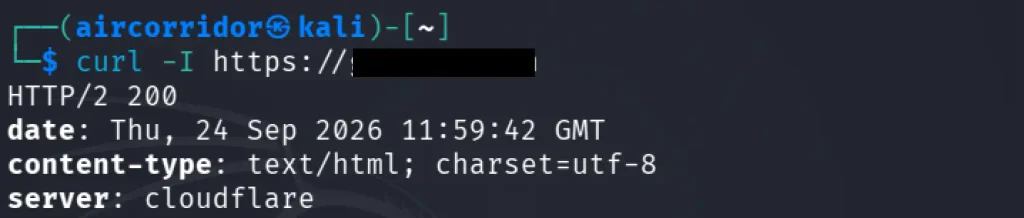
Before you do anything with the target, it’s smart to see whether they’re using a WAF at all. A good first step is to check the web application’s headers. You can easily do this with the curl command. Just type:

kali> curl -I target.com

In the screenshot above, we can see that the site uses Cloudflare and Qrator’s WAF. Usually, you can spot some hints in the headers that help identify it, like:

The unique transaction tracking ID: X-Qrator-Request-ID or X-Qrator-Req-ID

Server header showing: Server: QRATOR

Internal proxy metadata headers like X-Qrator-IP or X-Qrator-Upstream.

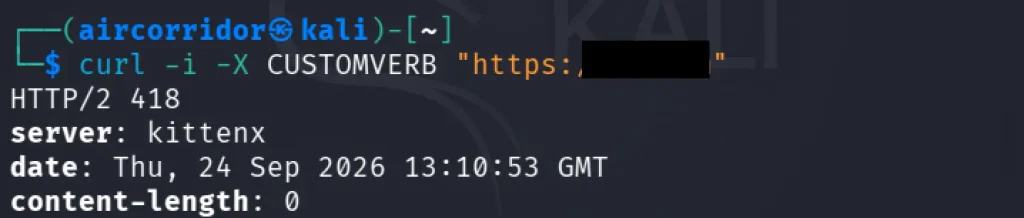
Another way to fingerprint the WAF is through behavior analysis. Here, we’re not just loading a webpage, but we send something that seems a bit malicious. For example, let’s try executing a random HTTP method:

kali> curl -i -X CUSTOMVERB “https://example.com/”

When you run into a 418 status code along with kittenx, it’s usually the edge layer stepping in as a bot-mitigation tool or a WAF block. This means that the incoming request hit a security rule, hit a rate limit, or didn’t pass automated fingerprint checks. Most of the time, you’ll see a 403 status code, which is the classic WAF block. Sometimes you might see other codes like 406, especially with ModSecurity CRS. Some vendors even show their own “Access Denied” HTML page when this happens.

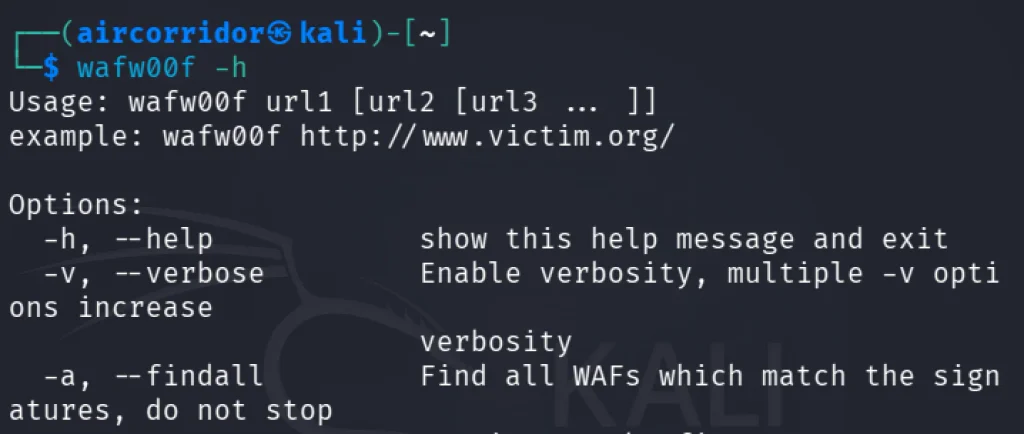
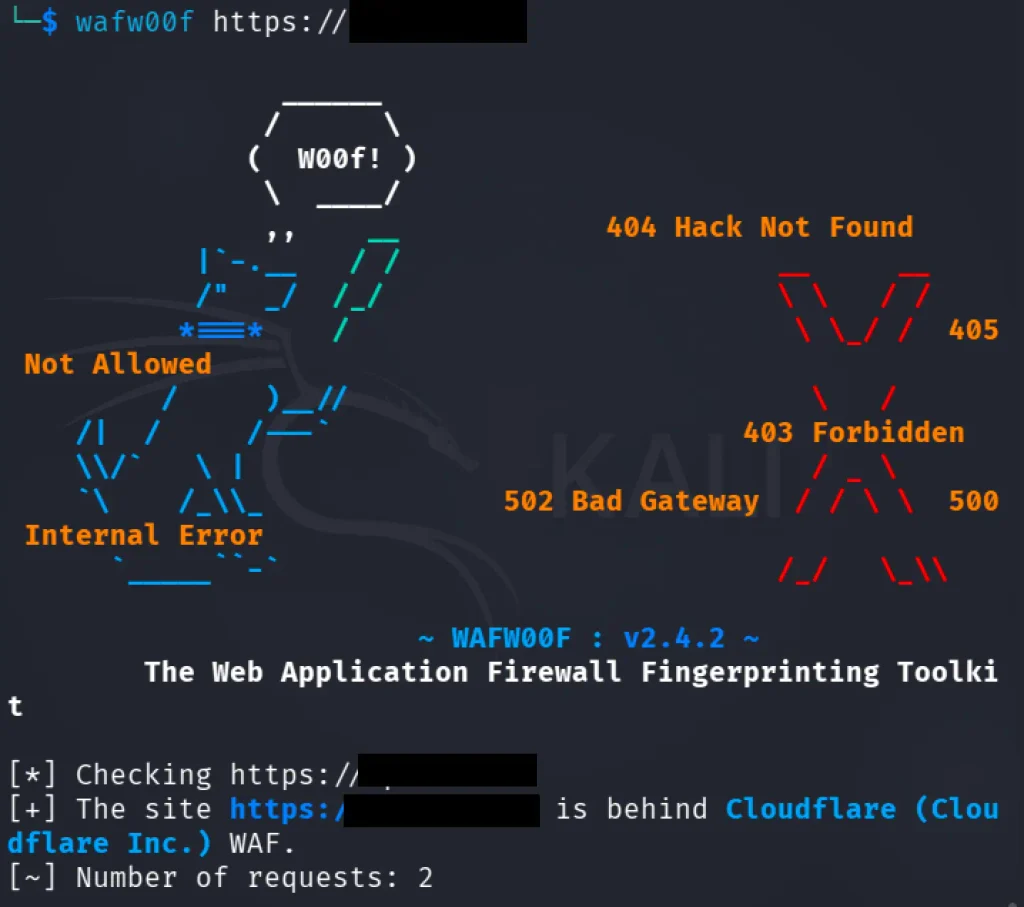
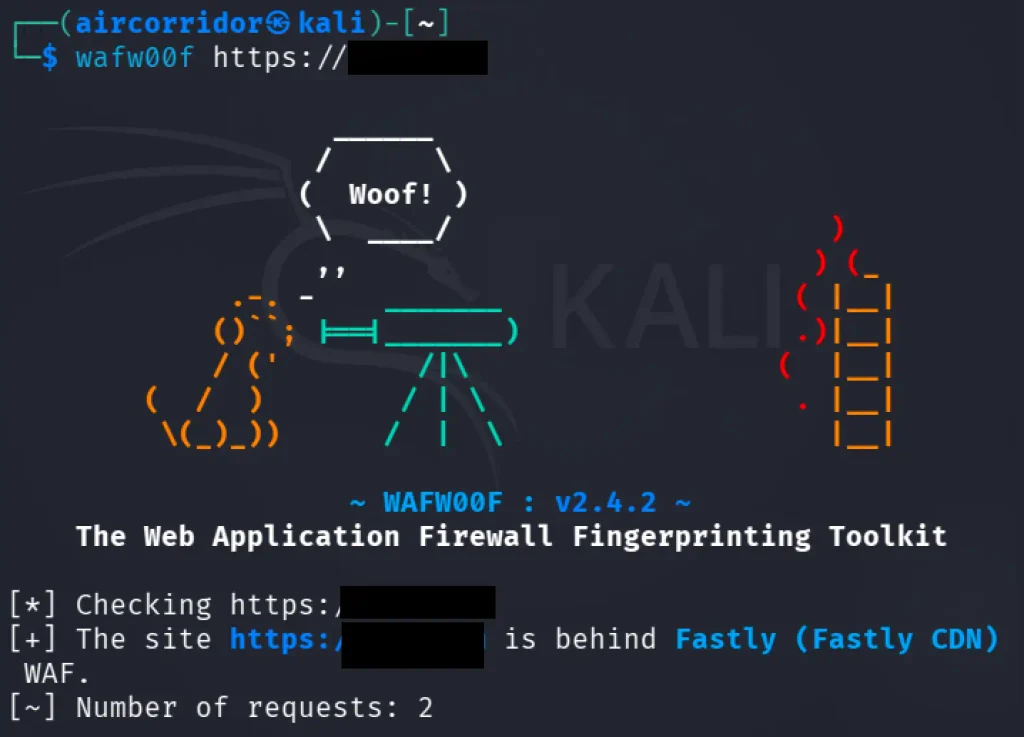
Instead of using curl to trigger different WAF rules manually, a cool tool called WAFW00F can do the identification for you. It starts by sending a normal HTTP request and checking the response to see which WAF solutions it can spot. If that doesn’t work, it sends potentially malicious HTTP requests to figure out which WAF is in play. If that still doesn’t yield results, it looks back at previous responses. It uses straightforward logic to guess whether a WAF or security tool is responding to its efforts. This tool is actually preinstalled on Kali Linux, so you can easily check it out by running:

kali> wafw00f -h

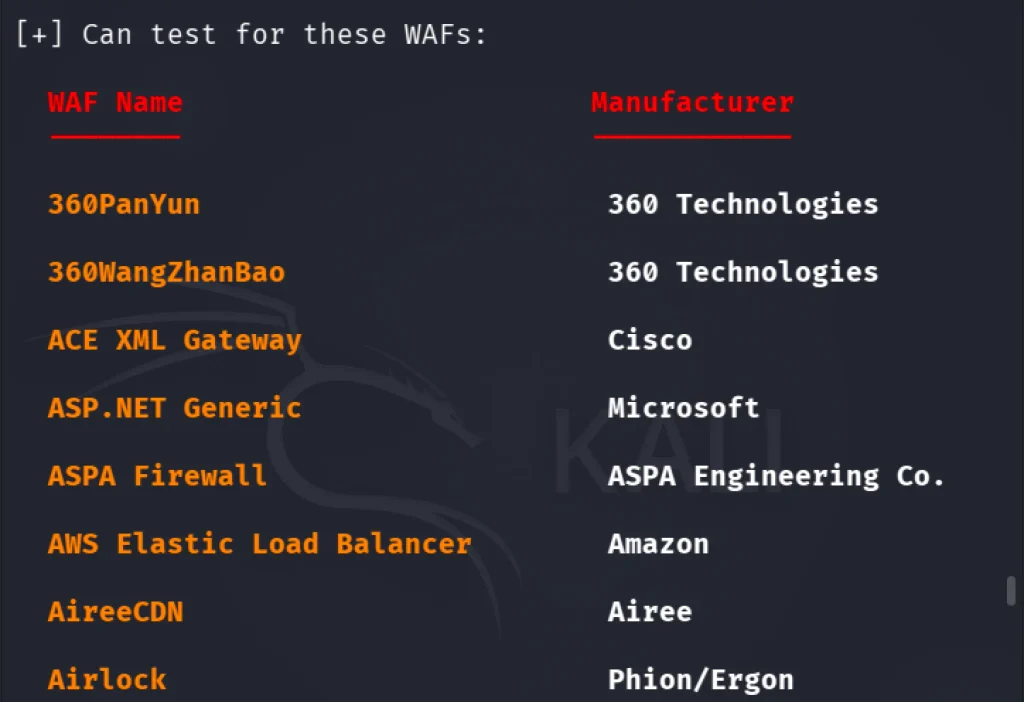
WAFW00F can spot plenty of firewalls. If you want to see the full list, just run this command:

kali> wafw00f -l


You just need to throw a URL in as an argument to get started.

Common WAF Bypass Techniques

Web apps handle lots of encoded text, and problems arise when they decode that text multiple times or in the wrong order compared to what a WAF expects.

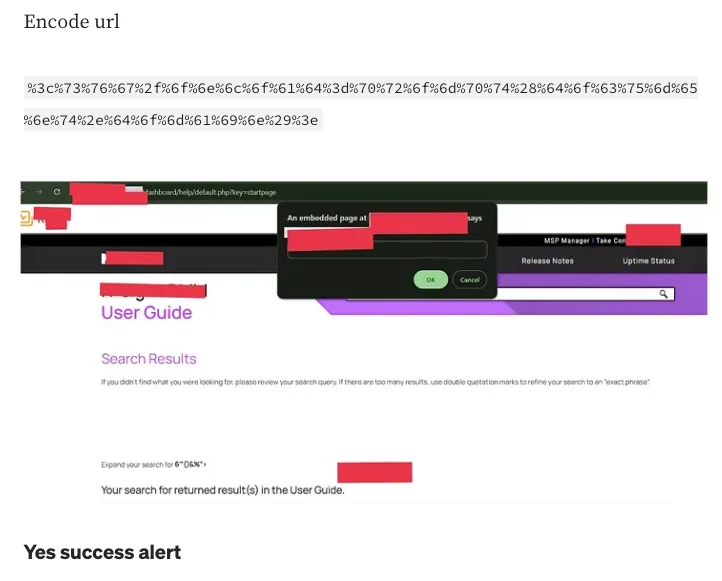
For example, double URL encoding can create vulnerabilities. If you encode a single quote twice as %2527, the WAF sees that and thinks it’s safe. But once the app decodes it twice, it turns into a real single quote, slipping past the WAF. This often leads to XSS.

Unicode normalization can also be tricky because characters can appear in different ways. For example, if a WAF looks for < (U+003C) but gets the full-width version (U+FF1C), it won’t catch it. When the app normalizes it back to <, it creates a vulnerability.

Then there is ASCII smuggling, where attackers use invisible Unicode tags (U+E0000 to U+E007F) to replace plain ASCII characters. To the bare eye or even a WAF, it looks like a space in a regular message. But when the application decodes those tags, the hidden payload shows up intact and ready to execute. It is all about hiding real characters behind an invisible disguise.

With the popularity of AI, we also encounter a new type of vulnerability. If an AI model doesn’t have appropriate security guidelines, ASCII manipulations can lead to data poisoning.

Summary

There are tons of ways to get past a WAF without being noticed. In this article, we quickly covered what a WAF is, how it works, and how to identify which WAF you’re dealing with so you can test specific bypass techniques. In a future article, we’ll cover automated solutions. Stay tuned!

The post Introduction to Web Application Firewall (WAF) and Ways to Bypass It first appeared on Hackers Arise.
Web App Hacking: Katana, A Next-Generation Crawling and Spidering Framework

Welcome back, aspiring cyberwarriors and bug bounty hunters!

When we work with web applications, we often need to effectively crawl and spider them to understand what we’re dealing with. But the main problem we might encounter is that a target web app is an SPA, or single-page application. This means that the website loads a single HTML file initially and dynamically updates the content within that page as the user interacts with it. Therefore, traditional crawling tools become ineffective with modern web applications.

To work with modern JavaScript frameworks, single-page applications, and sophisticated authentication mechanisms, we can use the Katana framework from ProjectDiscovery. Katana is a web crawler that allows you to discover hidden paths, parameters, and endpoints in web applications. It’s fast, modular, and supports multiple crawling techniques.

One of the most impressive aspects of Katana is its ability to handle JavaScript execution and dynamic content rendering. Traditional crawlers often miss critical functionality because they cannot execute JavaScript or understand how modern web applications dynamically generate content. Katana addresses this limitation by incorporating headless browser capabilities that allow it to fully render pages, execute JavaScript, and discover content that would otherwise remain hidden.

Let’s explore how to download, install, and utilize this powerful reconnaissance tool to enhance your web application security testing capabilities.

Installing Katana

There are few methouds of installing the tool. In this article, I’ll focus on installing using Go programming language.

First, verify if Go is already installed:

kali> go version

Install Katana using the Go package manager:

kali> go install github.com/projectdiscovery/katana/cmd/katana@latest

Verify the installation:

kali> katana -version

Crawling Modes

Katana supports two main crawling modes, each tailored to different types of web applications and use cases.

The Standard Mode is designed for speed and simplicity, making it ideal for traditional websites. It uses Go’s built-in HTTP library to handle requests and responses, parsing raw HTTP response bodies without executing JavaScript or rendering the DOM. This lightweight approach ensures fast performance but may miss endpoints in more complex applications that rely on browser-based events.

In contrast, the Headless Mode offers a more thorough crawl by simulating a real browser environment. This mode is especially useful for modern, JavaScript-heavy applications, as it captures both raw and rendered content. By mimicking a legitimate browser fingerprint (including TLS and user-agent headers), it improves coverage and detection of dynamic elements.

You can enable Headless Mode with the -headless flag and customize it further with several options:

  • -sc / -system-chrome: Use the locally installed Chrome
  • -sb / -show-browser: Show the browser window during execution
  • -ho / -headless-options: Pass custom Chrome options
  • -nos / -no-sandbox: Disable the Chrome sandbox (useful for root users)
  • -cdd / -chrome-data-dir: Specify a custom Chrome data directory
  • -scp / -system-chrome-path: Set a specific path to the Chrome executable
  • -noi / -no-incognito: Disable incognito mode

Basic Website Reconnaissance

Let’s start with a fundamental reconnaissance scenario where we need to map a target website’s structure and discover all accessible endpoints. For this example let’s try to understand application’s structure of Vesti.ru – Russian news website.

kali> katana -u https://example-target.com -d 5 -c 10 -o target-crawl-results.txt

-u: Specifies the target URL

-d 5: Sets maximum crawling depth to 5 levels

-c 10: Uses 10 concurrent threads for faster crawling

-o: Saves all discovered URLs to a file

JavaScript-Heavy Application Crawling

Modern web applications often rely heavily on JavaScript for content generation. Here’s how to handle an AngularJS-based single-page application.

kali> katana -u https://angular-app.com -js-crawl -headless -timeout 30 -delay 2 -o angular-results.json

-js-crawl: Enables JavaScript execution during crawling to handle AngularJS controllers and directives

-headless: Uses headless Chrome for rendering AngularJS templates and executing digest cycles

-timeout 30: Sets 30-second timeout for page loads to accommodate AngularJS bootstrapping

-delay 2: Adds 2-second delay between requests to allow AngularJS routing transitions

Known Files Discovery

Crawl for common files like robots.txt and sitemap.xml that often reveal valuable information about website structure and hidden content. These files can provide insights into:

  • robots.txt: Disallowed directories and files that may contain sensitive information
  • sitemap.xml: Complete site structure including pages not linked from main navigation
  • Other discovery files: Common configuration files, backup files, and administrative interfaces

kali> katana -u https://example.com -known-files all -d 3

Note that a minimum depth of 3 is required to ensure comprehensive discovery of all known files across the target application.

Filtering Capabilities

Katana offers robust filtering features that help users process, refine, and manage crawl output with precision. These capabilities make it easy to isolate valuable data, reduce noise, and tailor results to match specific goals.

Users can filter output by specific fields, include or exclude URLs based on extensions or regular expressions, and even define custom fields using a YAML configuration file. This flexibility is crucial for handling the often large volume of data produced during a crawl, ensuring that users can focus on the most relevant information.

Some key filtering options include:

  • -field or -f: Display specific fields (e.g., url, path, fqdn, rdn)
  • -store-field or -sf: Save selected fields to disk
  • -extension-match or -em: Show only URLs with specific file extensions
  • -extension-filter or -ef: Exclude URLs with specific file extensions
  • -match-regex or -mr: Include URLs that match a regex pattern
  • -filter-regex or -fr: Exclude URLs that match a regex pattern

Example:
To extract only .js URLs (including those with query parameters) and save their full URLs to a file, you could run:

kali> katana -u https://example.com -match-regex “\.js” -f url -sf url -o js-files.txt

Summary

Whether you’re conducting penetration tests, bug bounty research, or comprehensive cyberwar operations, Katana’s advanced capabilities and modern architecture make it an essential addition to your hacking toolkit.

If you’re serious about sharpening your offensive security skills, consider our Subscriber Pro package. It’s designed to take your expertise to the next level.

The post Web App Hacking: Katana, A Next-Generation Crawling and Spidering Framework first appeared on Hackers Arise.
WorkNest Secure Launches Continuous Vulnerability Scanning with GuardNest

WorkNest Secure has expanded its GuardNest platform with continuous vulnerability scanning, giving organisations ongoing visibility into security weaknesses rather than relying solely on periodic penetration tests.

The new capability is designed to help businesses monitor vulnerabilities across internet-facing systems, web applications, and internal environments, providing continuous oversight of their attack surface as threats and infrastructure evolve.

The launch comes as organisations face increasing pressure from customers, insurers, and regulators to demonstrate continuous vulnerability management and stronger cyber resilience.

Moving beyond annual penetration testing

While penetration testing remains a critical part of any cybersecurity strategy, WorkNest Secure says annual or point-in-time assessments no longer provide a complete picture of an organisation’s security posture.

The enhanced GuardNest platform combines automated vulnerability scanning with expert analysis and remediation support, allowing organisations to identify vulnerabilities as they emerge and prioritise the issues that present the greatest business risk.

Organisations can schedule scans, monitor vulnerabilities in real time, and manage remediation activities through a single dashboard.

The platform now supports external vulnerability scanning, internal vulnerability scanning, web application scanning, and agent-based internal scanning, allowing customers to tailor the service to their environment and compliance requirements.

Simplifying vulnerability management

Alongside continuous scanning, GuardNest introduces new remediation workflows designed to help security and IT teams manage vulnerabilities more effectively.

Organisations can assign remediation tasks, define service level targets based on vulnerability severity, and track progress through to resolution. Automated escalation and SLA tracking are intended to ensure vulnerabilities are actively managed rather than simply recorded in reports.

The platform also includes live dashboards, historical trend reporting, and automated reporting that can support compliance initiatives, cyber insurance renewals, customer due diligence, and certifications including ISO 27001, Cyber Essentials Plus, and PCI DSS.

Helping organizations focus on what matters

Kirsty Fowler, Managing Director of WorkNest Secure, said organisations need greater visibility into their cyber risks as environments continue to change.

“Cyber threats do not operate to an annual schedule, yet many organisations are still relying on point-in-time assessments to understand their security posture,” Fowler said.

“New vulnerabilities emerge every day and infrastructure changes constantly, so businesses need visibility of their risks as they exist today, not six months ago.”

She added that the new functionality is intended to reduce the complexity of vulnerability management by combining automation with expert support.

“By combining automated scanning with expert support and practical remediation guidance, we help organisations cut through the noise, understand what matters most, and know exactly where action is needed,” Fowler said.

Responding to changing security needs

The launch reflects a broader shift in how organisations approach cybersecurity investment, with many moving away from one-off security projects in favour of continuous monitoring and ongoing risk management.

WorkNest Secure said the new functionality is available immediately either as a standalone vulnerability management service or as part of existing GuardNest packages.

The latest release builds on the redesign of the GuardNest platform in 2025, which introduced a more collaborative and user-friendly approach to vulnerability management, penetration testing, and remediation.

The post WorkNest Secure Launches Continuous Vulnerability Scanning with GuardNest appeared first on IT Security Guru.

Pentesting: Using Grafana to Pentest a Fitness App

Welcome back, aspiring cyberwarriors!

During pentests, it’s not uncommon to find a Grafana somewhere inside an organization’s infrastructure. Sometimes it can even be exposed directly to the Internet. It’s always worth checking Grafana for vulnerabilities, as it has been affected by multiple security issues over the years.

What is Grafana

Grafana is an open-source monitoring and visualization platform used by organizations to display dashboards containing information collected from servers, applications, databases, cloud services and networking equipment. Administrators rely on it to monitor the health of their infrastructure in real time, making it one of the most widely deployed monitoring apps in enterprise environments. Since Grafana often connects to numerous backend services and contains valuable configuration information, compromising it can sometimes give hackers an excellent foothold into the rest of the network.

Of course, you could manually inspect every Grafana installation looking for known vulnerabilities, but that quickly becomes time-consuming, especially during larger engagements where multiple servers have to be assessed.

Fortunately, there is a Grafana-Final-Scanner. It’s a tool designed specifically to automate this process. Instead of manually checking every instance the scanner performs the work for you by checking whether the target is vulnerable to a collection of publicly known vulnerabilities.

Grafana-Final-Scanner

We’ll begin by downloading the repository and installing its dependencies.

kali > git clone https://github.com/Zierax/Grafana-Final-Scanner.git
kali > cd Grafana-Final-Scanner
kali > python3 -m venv venv
kali > source venv/bin/activate
kali > pip3 install -r requirements.txt
installing grafana

Once everything has been installed successfully, it’s worth taking a quick look at the list of vulnerabilities supported by the scanner.

vulnerabilities grafana scanner can find

At the time of writing, the tool is capable of checking for more than fifteen different Grafana vulnerabilities.

Now let’s point it at our target.

kali > python3 scanner.py -u https://target/grafana/login
scanning for the vulnerabilities

After a short scan, the tool analyzes the target and reports any vulnerabilities it successfully identifies.

results of the scan

In our case, the results were promising. The scanner identified CVE-2024-8118 and an OAuth Authentication Bypass vulnerability. It also gave us the URL. We opened the page and the application asked us for an administrator key that we obviously didn’t have.

login page

Fortunately, web applications don’t always behave exactly as their developers intended. Developers occasionally leave sensitive information inside the application’s front-end code. JavaScript, HTML comments, hardcoded credentials, authorization logic have all been discovered by hackers countless times over the years.

source code

With that in mind, we opened the page’s HTML source code to see exactly how the authorization process was implemented. The comments were written in Russian, but the logic itself was fairly easy to understand.

Instead of verifying a specific administrator key, the application simply checked whether any key existed. So the validation routine wasn’t actually validating the value at all. It simply checked if some key was provided.

The next step was straightforward. We opened the browser’s Developer Console and manually created the expected key.

The application accepted it. 

bypassed the login page

We bypassed the authentication and accessed the admin panel. 

Finding a vulnerability is only part of the pentest. Understanding how the application behaves after exploitation is equally important. Sometimes the scanners get you only halfway there, while manual analysis can help you find the remaining pieces needed to fully demonstrate the impact.

It’s also a good reminder that developers occasionally leave sensitive information hidden inside client-side code. You never know what useful information may have been left behind.

Web Interface

While running the scanner from the command line works perfectly for testing targets, the project also includes a convenient web interface.

This can be useful during larger pentests where dozens of Grafana instances need to be assessed.

You can start it with this command:

kali > python scanner.py --serve --db vulndb.json
web interface

Summary

Grafana is one of the most common monitoring platforms you’ll encounter during internal and external penetration tests. Because it frequently contains sensitive operational data and often communicates with numerous backend systems, compromising it can sometimes provide hackers with an excellent entry point into an organization’s network.

Grafana-Final-Scanner can make it much easier to determine whether your Grafana is exposed to known vulnerabilities.

If you enjoy web application pentesting and would like to improve your skills for bug bounty hunting, we have our Web Application Hacking training. You’ll gain the practical knowledge and skills you need to start finding web application vulnerabilities.

The post Pentesting: Using Grafana to Pentest a Fitness App first appeared on Hackers Arise.
❌