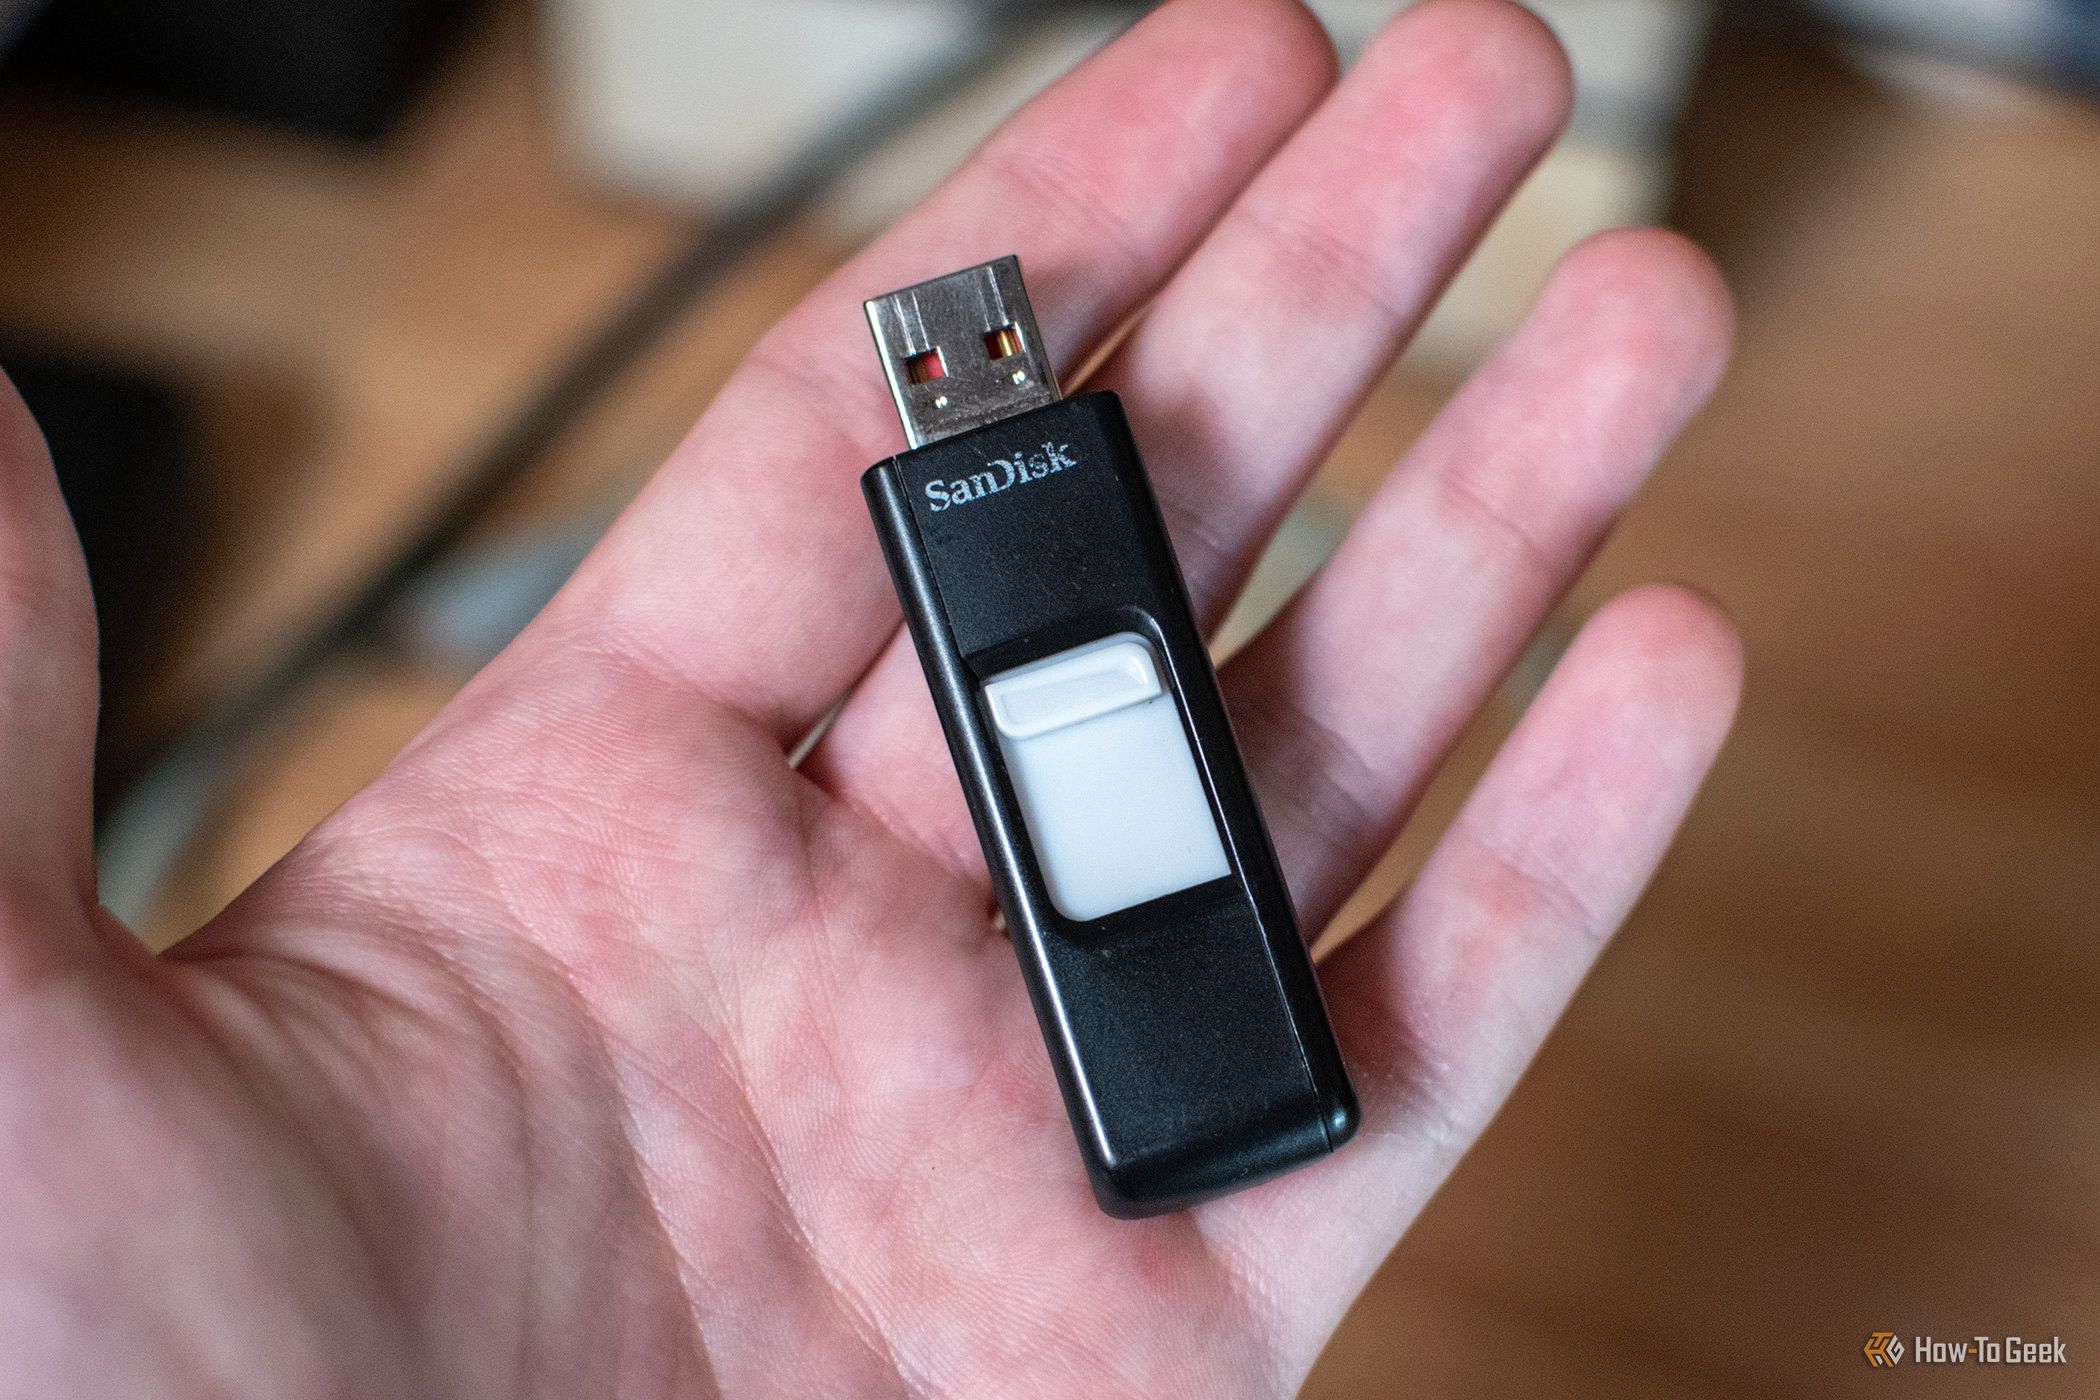
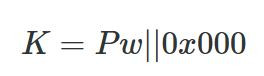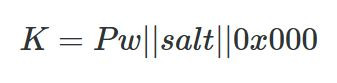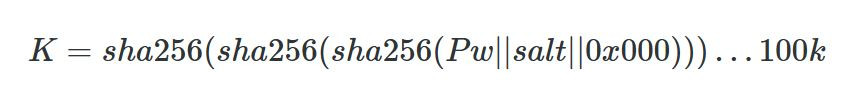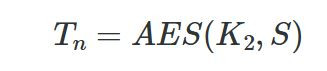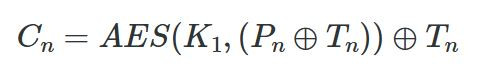At one point in time, USB drives were all the rage for file transfers. I kept one in my pocket at almost all times and I had several around the house for various purposes. Over time, USB drives quietly stopped being so popular. But I still have uses for them in my homelab, so here are the main reasons why I’ll never throw away old USB drives.
AI data centers are creating new challenges for power grids. Learn how emerging reliability standards and power technologies could reshape their operations.
AI data centers are creating new challenges for power grids. Learn how emerging reliability standards and power technologies could reshape their operations.
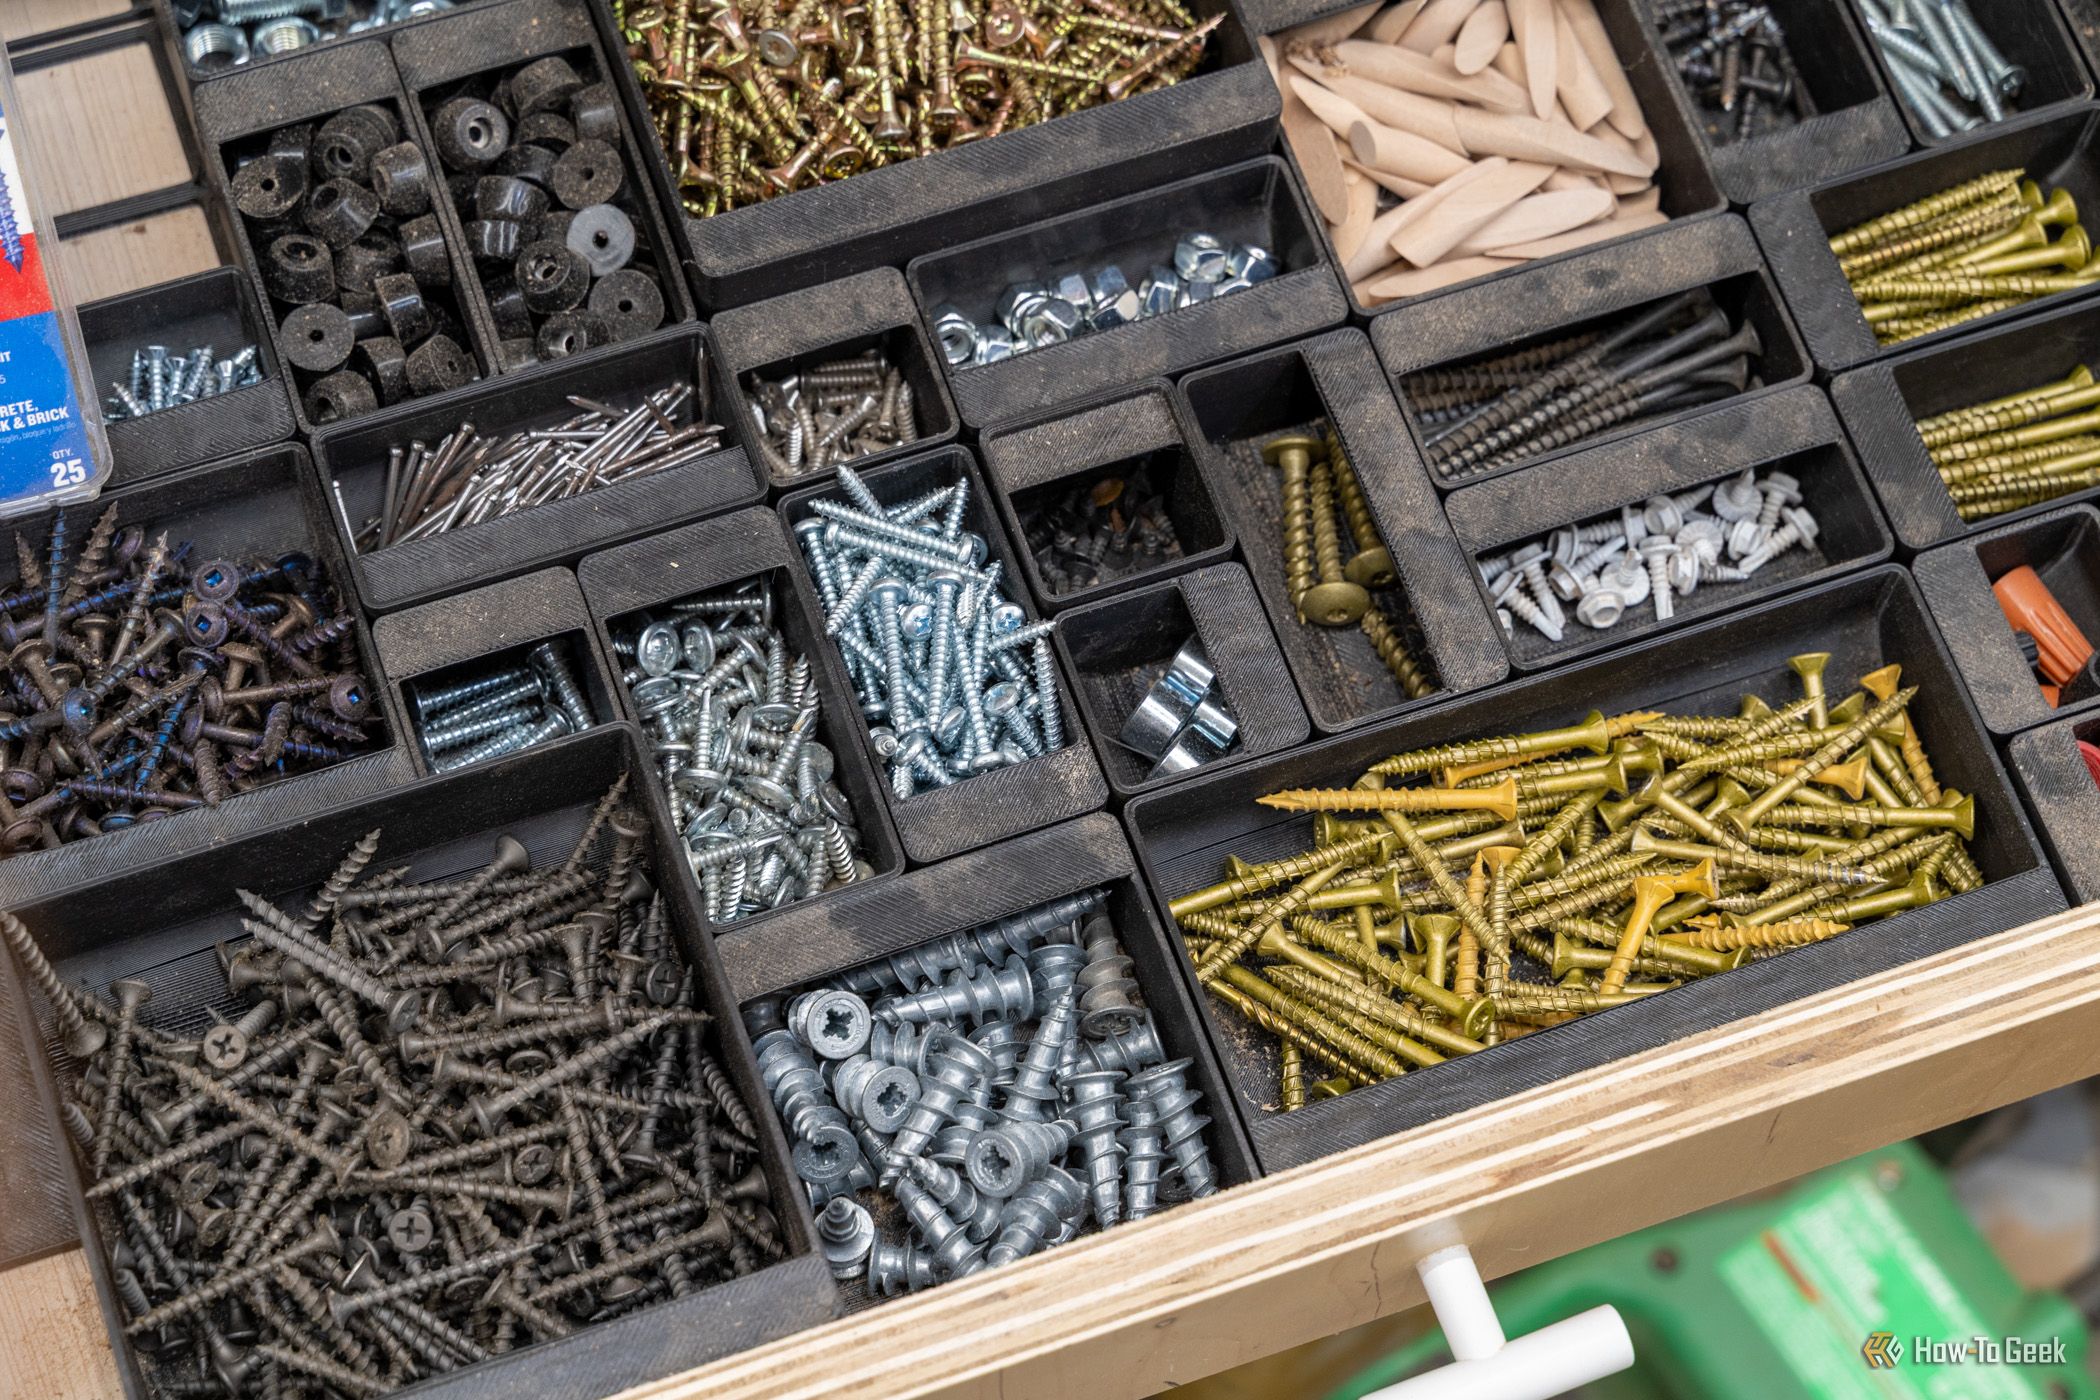
A rainy weekend stuck indoors is the perfect excuse to put your 3D printer to work on the house itself. While it hums along, you can line up new cabinet pulls without eyeballing them, replace that broken clip nobody sells anymore, and finally get the junk drawer under control. None of these projects need a garage full of tools, and by Sunday night something in your home will actually work better than it did on Friday.
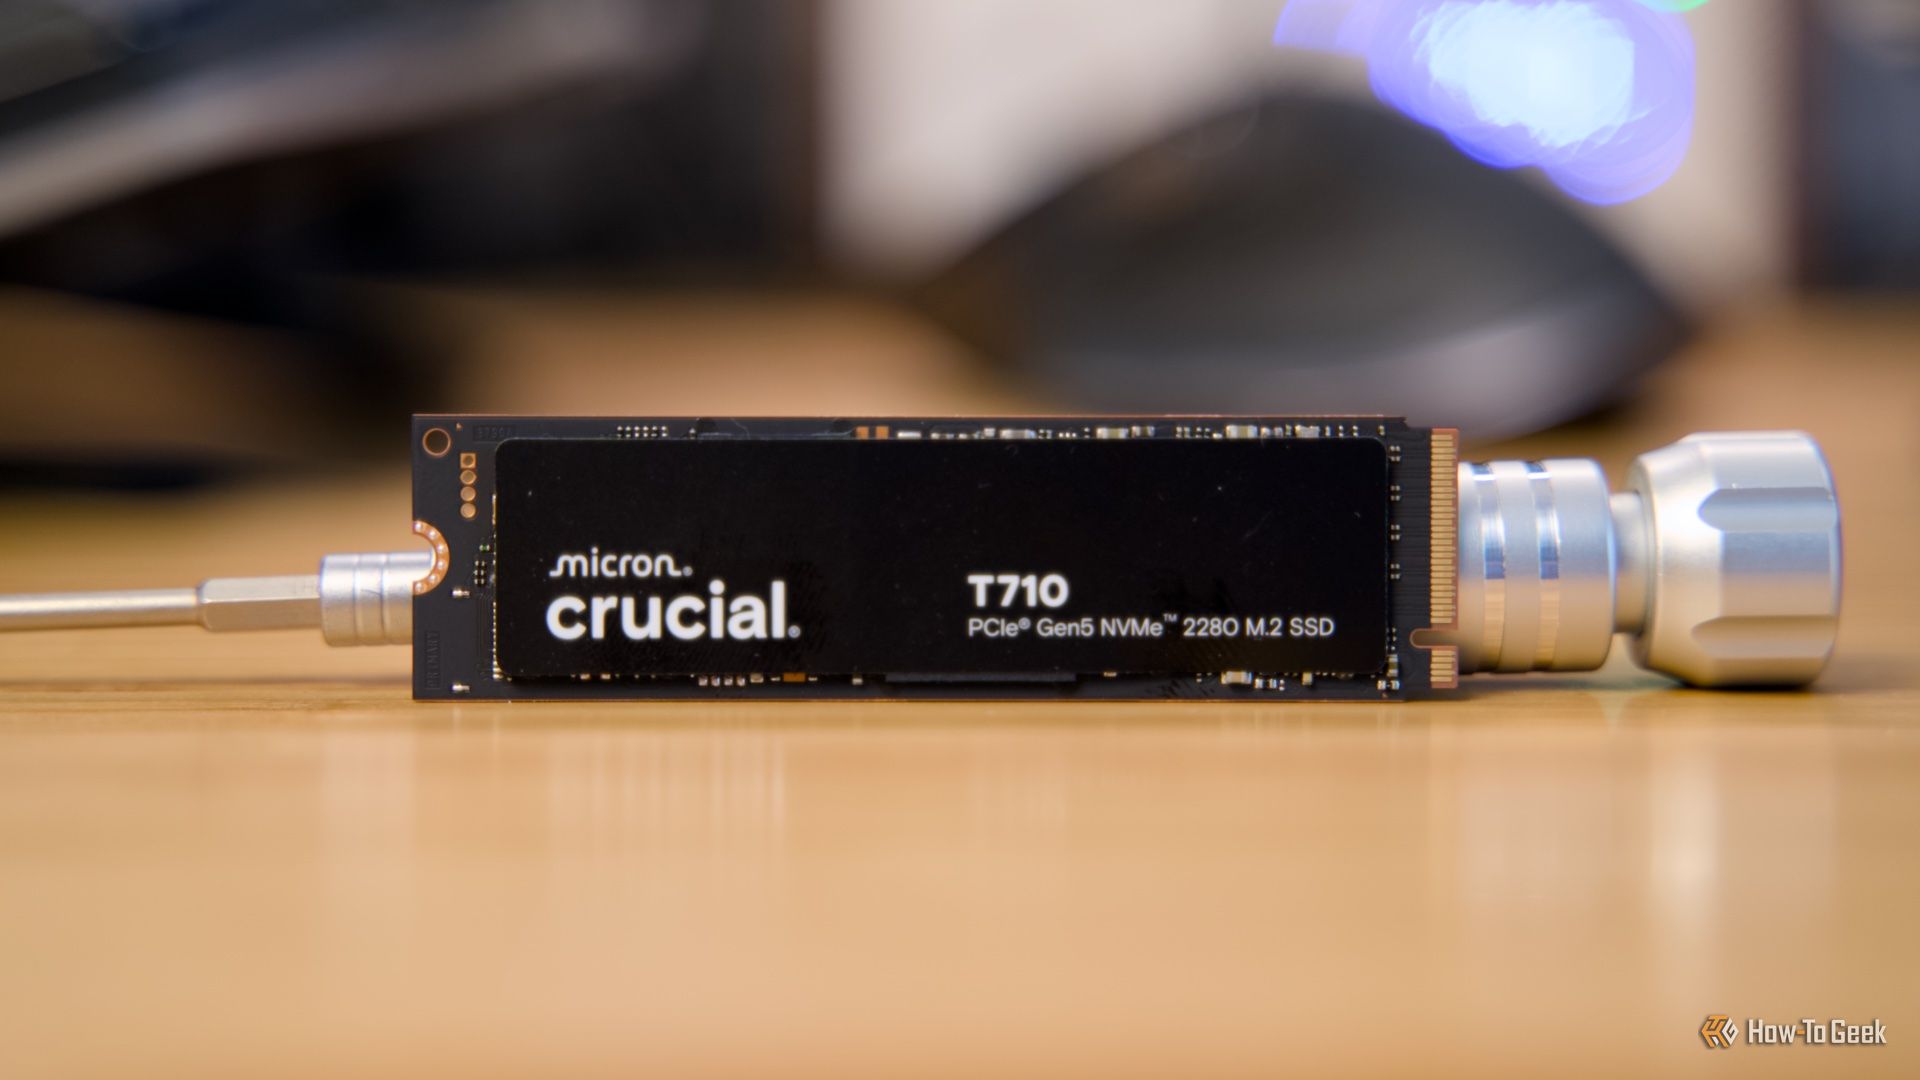
One of the most commonly repeated SSD tips is not to fill your drive all the way up to full. It makes perfect sense, and even manufacturers will tell you to leave 10-20% empty, so you should probably listen to them.
3D printers are a fantastic tool for making basically anything you could want. This weekend, I wanted to make my house a little less annoying. So, I set out to find three things I could fix that would make my everyday life a little better, and it took me under an hour to complete.
BeamFS creator Aurelien Desbrieres is not calling for a merge, but is requesting feedback on an 18-patch proposal that takes the place of FTRFS, an earlier filesystem he proposed in April.
The Linux/Open Source blog It's FOSS reports:
Filesystems that can repair damage, like Btrfs and ZFS, usually do it by falling back on a spare copy of the data. BeamFS skips that and stores Reed-Solomon error-correcting codes inside every block. Every read gets checked against those codes, and small amounts of damage are corrected before the data reaches the application. If the filesystem can tell the damage is beyond repair, the read fails with an error instead of returning the wrong bytes...
In his technical report, ext4 and ext3 returned wrong data without any error, while Btrfs refused to read the file. BeamFS returned the correct file every time except once, when a flip hit a pointer to the file's data and it refused the read.
"Aurelien says he used Anthropic's Claude to write the code, the tool that checks the patches, and the cover letter..."
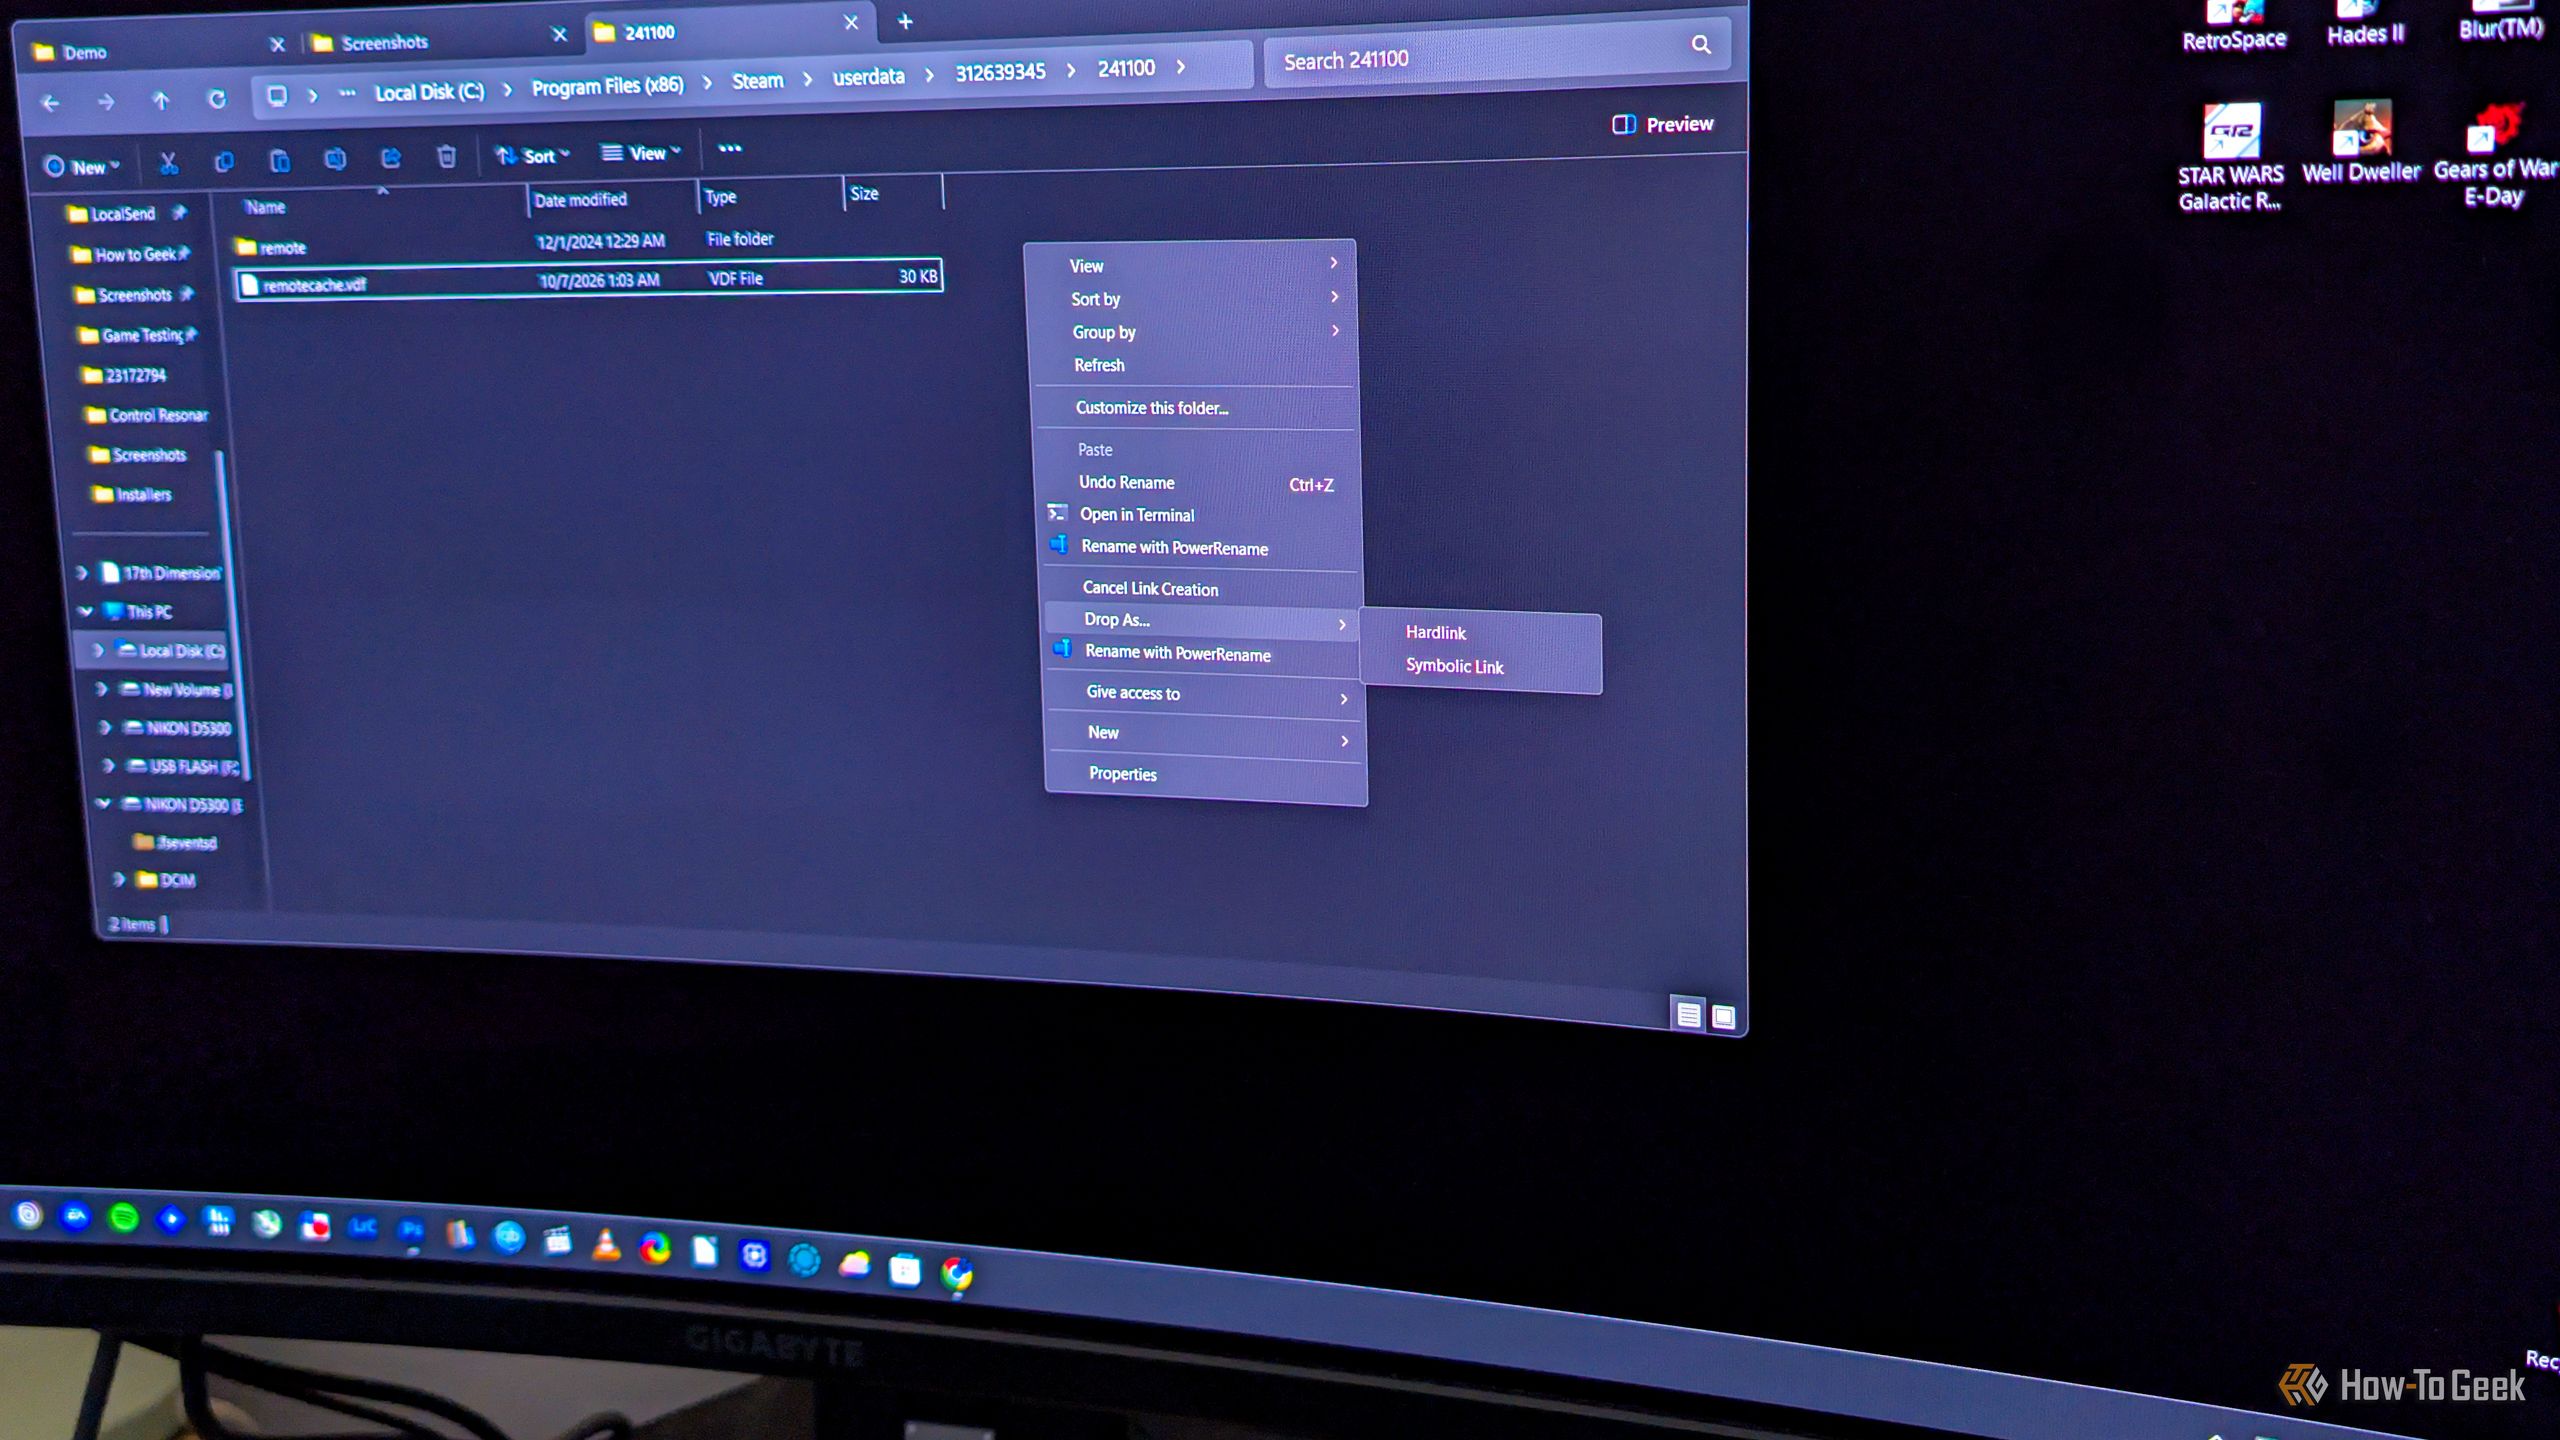
Say you want to copy a file to another folder on your Windows PC, but not for backup purposes. If you just want to have the same file appear in multiple folders, you don’t have to copy it the usual way, where each copy takes up the full amount of storage space. What you can do instead is hard link it, which makes the same file show up in another folder, indistinguishable from the original, with the benefit of this “copy” not using any extra storage.
I'm no stranger to finding weird things for my USB drives to do, such as repurposing them as "rescue drives." But this year, with the RAM shortage spilling over to every area of the PC market, I've found new ways to make good use of just about every piece of tech that I own. From a tiny file server to a retro gaming console, here's what I used my USB flash drives for in 2026.
A custom-built home is all about designing elements that feel perfectly adapted to your space and routine. With a 3D printer, you can retroactively apply this concept to the objects inside your home, to great effect.
You may know that privacy laws aren’t respected everywhere. In some places you can be forced to decrypt your files, or worse, get accused of a violation just for having encryption. A VeraCrypt hidden volume helps with the first problem but not the second. That’s why the project developer built Phantomdrive.
Phantomdrive is a fully open source USB drive that shows up as an 8GB disk when you plug it in. The OS has no way to detect the rest of the storage. To unlock the hidden partition, you open a text file on the visible part of the drive, type password: YOURPASSWORDHERE and save it. The drive disconnects, remounts the hidden partition, and AES-256 handles the encryption and decryption on the fly.
Design
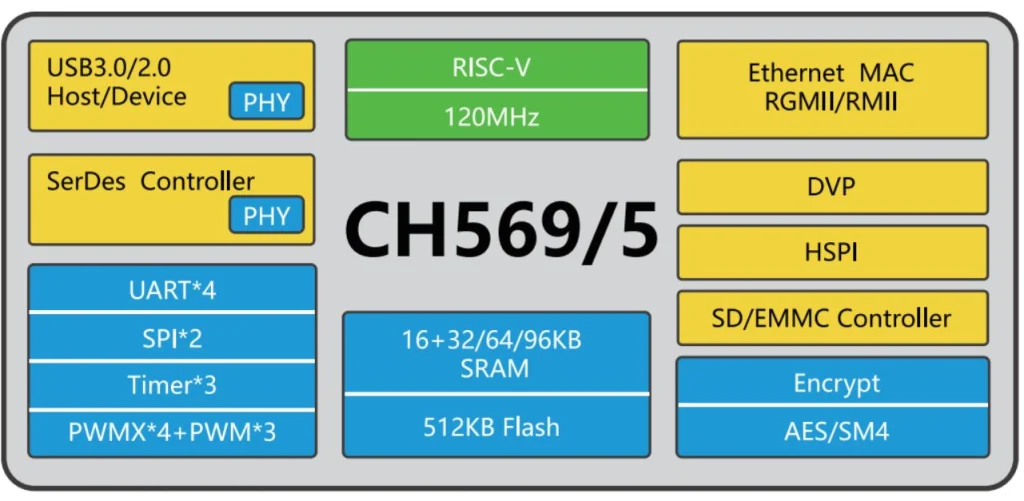
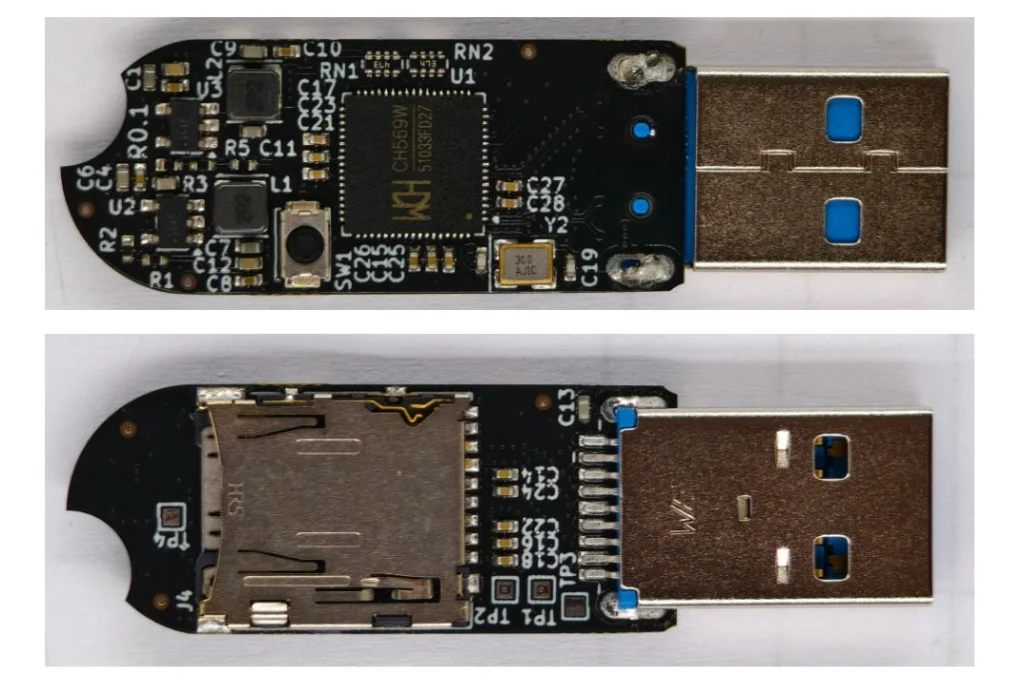
The hardware, firmware, and mechanical design are all open source. The developer built it around a small chip called the CH569, from the same company behind the CH340 USB-to-Serial chip you’ll find on most Arduino clones. It has USB3, SD/eMMC support, and a hardware AES block built in.
eMMC was too expensive due to AI-driven demand, so the developer went with an SD card instead. If someone tears the device apart they’ll find it, but everything on it is encrypted. The enclosure is sealed with epoxy, so any attempt to get inside means destroying it first. Once eMMC prices drop, a version using it will follow.
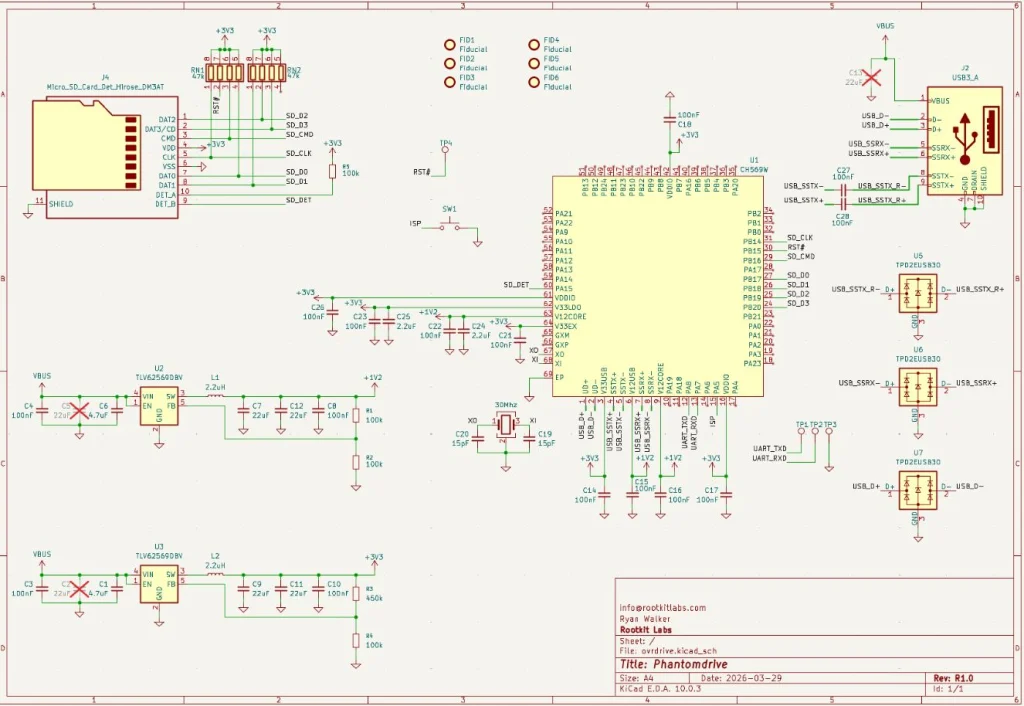
The board itself is simple. It’s a CH569 chip, a USB port, two buck converters, a firmware update button, an SD card, and some supporting components.
Cryptography
The developer verified encryption works through functional tests and ran it against OpenSSL’s AES implementation. Most of the GitHub issues that surfaced were AI-generated noise or already fixed bugs, with one real exception around AES-XTS covered below.
Key Derivation
A Key Derivation Function (KDF) turns your password into an encryption key. The naive approach is padding the password to 32 bytes and using it directly.
That’s weak. A precomputed table could crack it without even brute forcing. To fix that, Phantomdrive adds a unique salt per device.
With different salts, an attacker has to compute keys for each device separately, and you can’t swap the SD card between devices. You can read your salt like this:
udevadm info --query=property --name=/dev/sdc | grep ID_SERIAL_SHORT
ID_SERIAL_SHORT=Phantomdrive:34FC1FA7145467F7
So, 34FC1FA7145467F7 is the salt for this device, which you will need to recover the data if it ever fails. Save that value. You can also change the Phantomdrive name and the USB PID/VID in firmware if you want more stealth. On top of the salt, the KDF runs 100,000 rounds of SHA-256.
That adds about 3 seconds to unlock time, which is already at the limit of what the chip can handle. Argon2 isn’t an option since it needs too much memory. If you need stronger security, you can increase the round count, use a software encryption layer on top, or look for a different device.
AES Modes
AES is a block cipher that works on 16-byte chunks. Different modes turn it into a stream cipher.
AES-ECB is the naive approach, encrypting each block directly. The problem is that identical plaintext blocks produce identical ciphertext blocks, which leaks patterns. Attackers can also manipulate the ciphertext in predictable ways. Not good.
AES-CTR solves this by encrypting a counter and XORing the output with plaintext.
The main risk with CTR is nonce reuse. If an attacker copies your ciphertext twice and can guess one version, they can recover the other. The developer gets around 9 MB/s write and 20 MB/s read with AES-CTR.
AES-XTS is the disk encryption standard and uses two keys. K1 protects the data, K2 generates a tweak per sector.
Each 16-byte block gets its own adjustment (T0, T1… Tn), then blocks are encrypted one by one to produce the final ciphertext.
It’s more secure but slower, around 6 MB/s write and 10 MB/s read on this hardware.
Firmware
The firmware is built on two open source libraries:
BSP: https://github.com/hydrausb3/wch-ch56x-lib
ISP: https://github.com/hydrausb3/wch-ch56x-isp
Password Snooping
The device doesn’t understand file systems. It just handles raw USB WRITE10/READ10 commands and passes them to the SD card. To detect the unlock password, the firmware scans every write for the string password: before passing data through.
void phantomdrive_snoop_write(uint8_t *buf, uint32_t len)
{
    const char *prefix = "password:";
    const size_t prefix_len = 9;
    uint32_t i;

    for (i = 0; i + prefix_len <= len; i++) {
        if (buf[i] != 'p')
            continue;
        if (memcmp(buf + i, prefix, prefix_len) != 0)
            continue;

        size_t pw_start = i + prefix_len;
        size_t pw_end = pw_start;
        while (pw_end < len && (pw_end - pw_start) < sizeof(pending_pw) &&
               buf[pw_end] != '\n' && buf[pw_end] != '\r' && buf[pw_end] != '\0')
            pw_end++;

        size_t pw_len = pw_end - pw_start;

        memcpy(pending_pw, buf + pw_start, pw_len);
        pending_pw_len = pw_len;

        memset(buf + i, 0, pw_end - i);
        return;
    }
}
Once the password is found, it gets copied into RAM and the buffer gets zeroed out so the password never touches the disk. Keep in mind, if you store a lot of data on the unencrypted partition and any of it contains the string password:, you could get a false match. If that’s a concern, you can change the trigger string in firmware or look for a different approach.
Video
The developer has also published a video, if you want to get into details of this project.
Summary
Phantomdrive is an open source USB drive that shows up as a plain 8GB disk while hiding the rest of its storage. You unlock the hidden partition by saving a password in a text file on the visible disk. The firmware catches it in the raw write traffic, keeps it in RAM, and never writes it to disk. Encryption is AES-256 on a CH569 chip, with a per-device salt and 100,000 SHA-256 rounds for key derivation. It’s limited by the hardware, so it’s weaker than memory-hard options like Argon2.
If you want to go deeper into how privacy can be preserved on real systems and how forensic traces are created and analyzed, our Anti-Forensics training is your next step. We covered advanced techniques for preserving your privacy and understanding what investigators can still see even when you think you have covered your tracks.
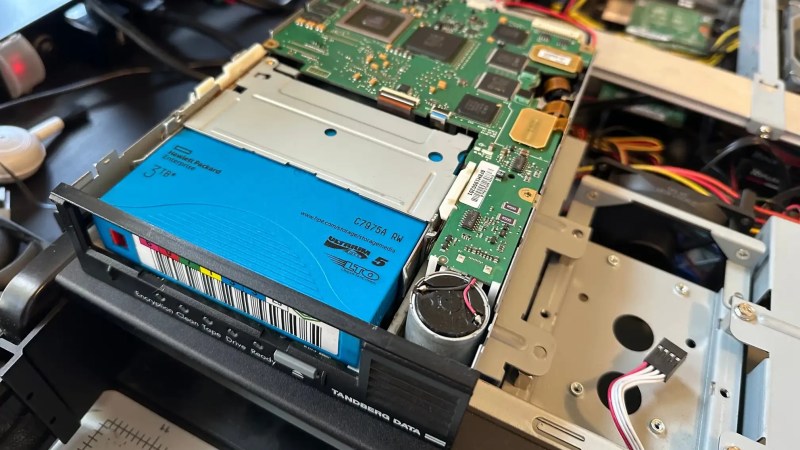
It’s one of the great mysteries of computing, how somehow in the Year Of OLlama 2026, tape remains the god of cheap storage. A while back [Ben Pettis] recounted his experience setting up an LTO-5 tape drive in his homelab, an experience which only becomes more relevant as hard drive prices stay high.
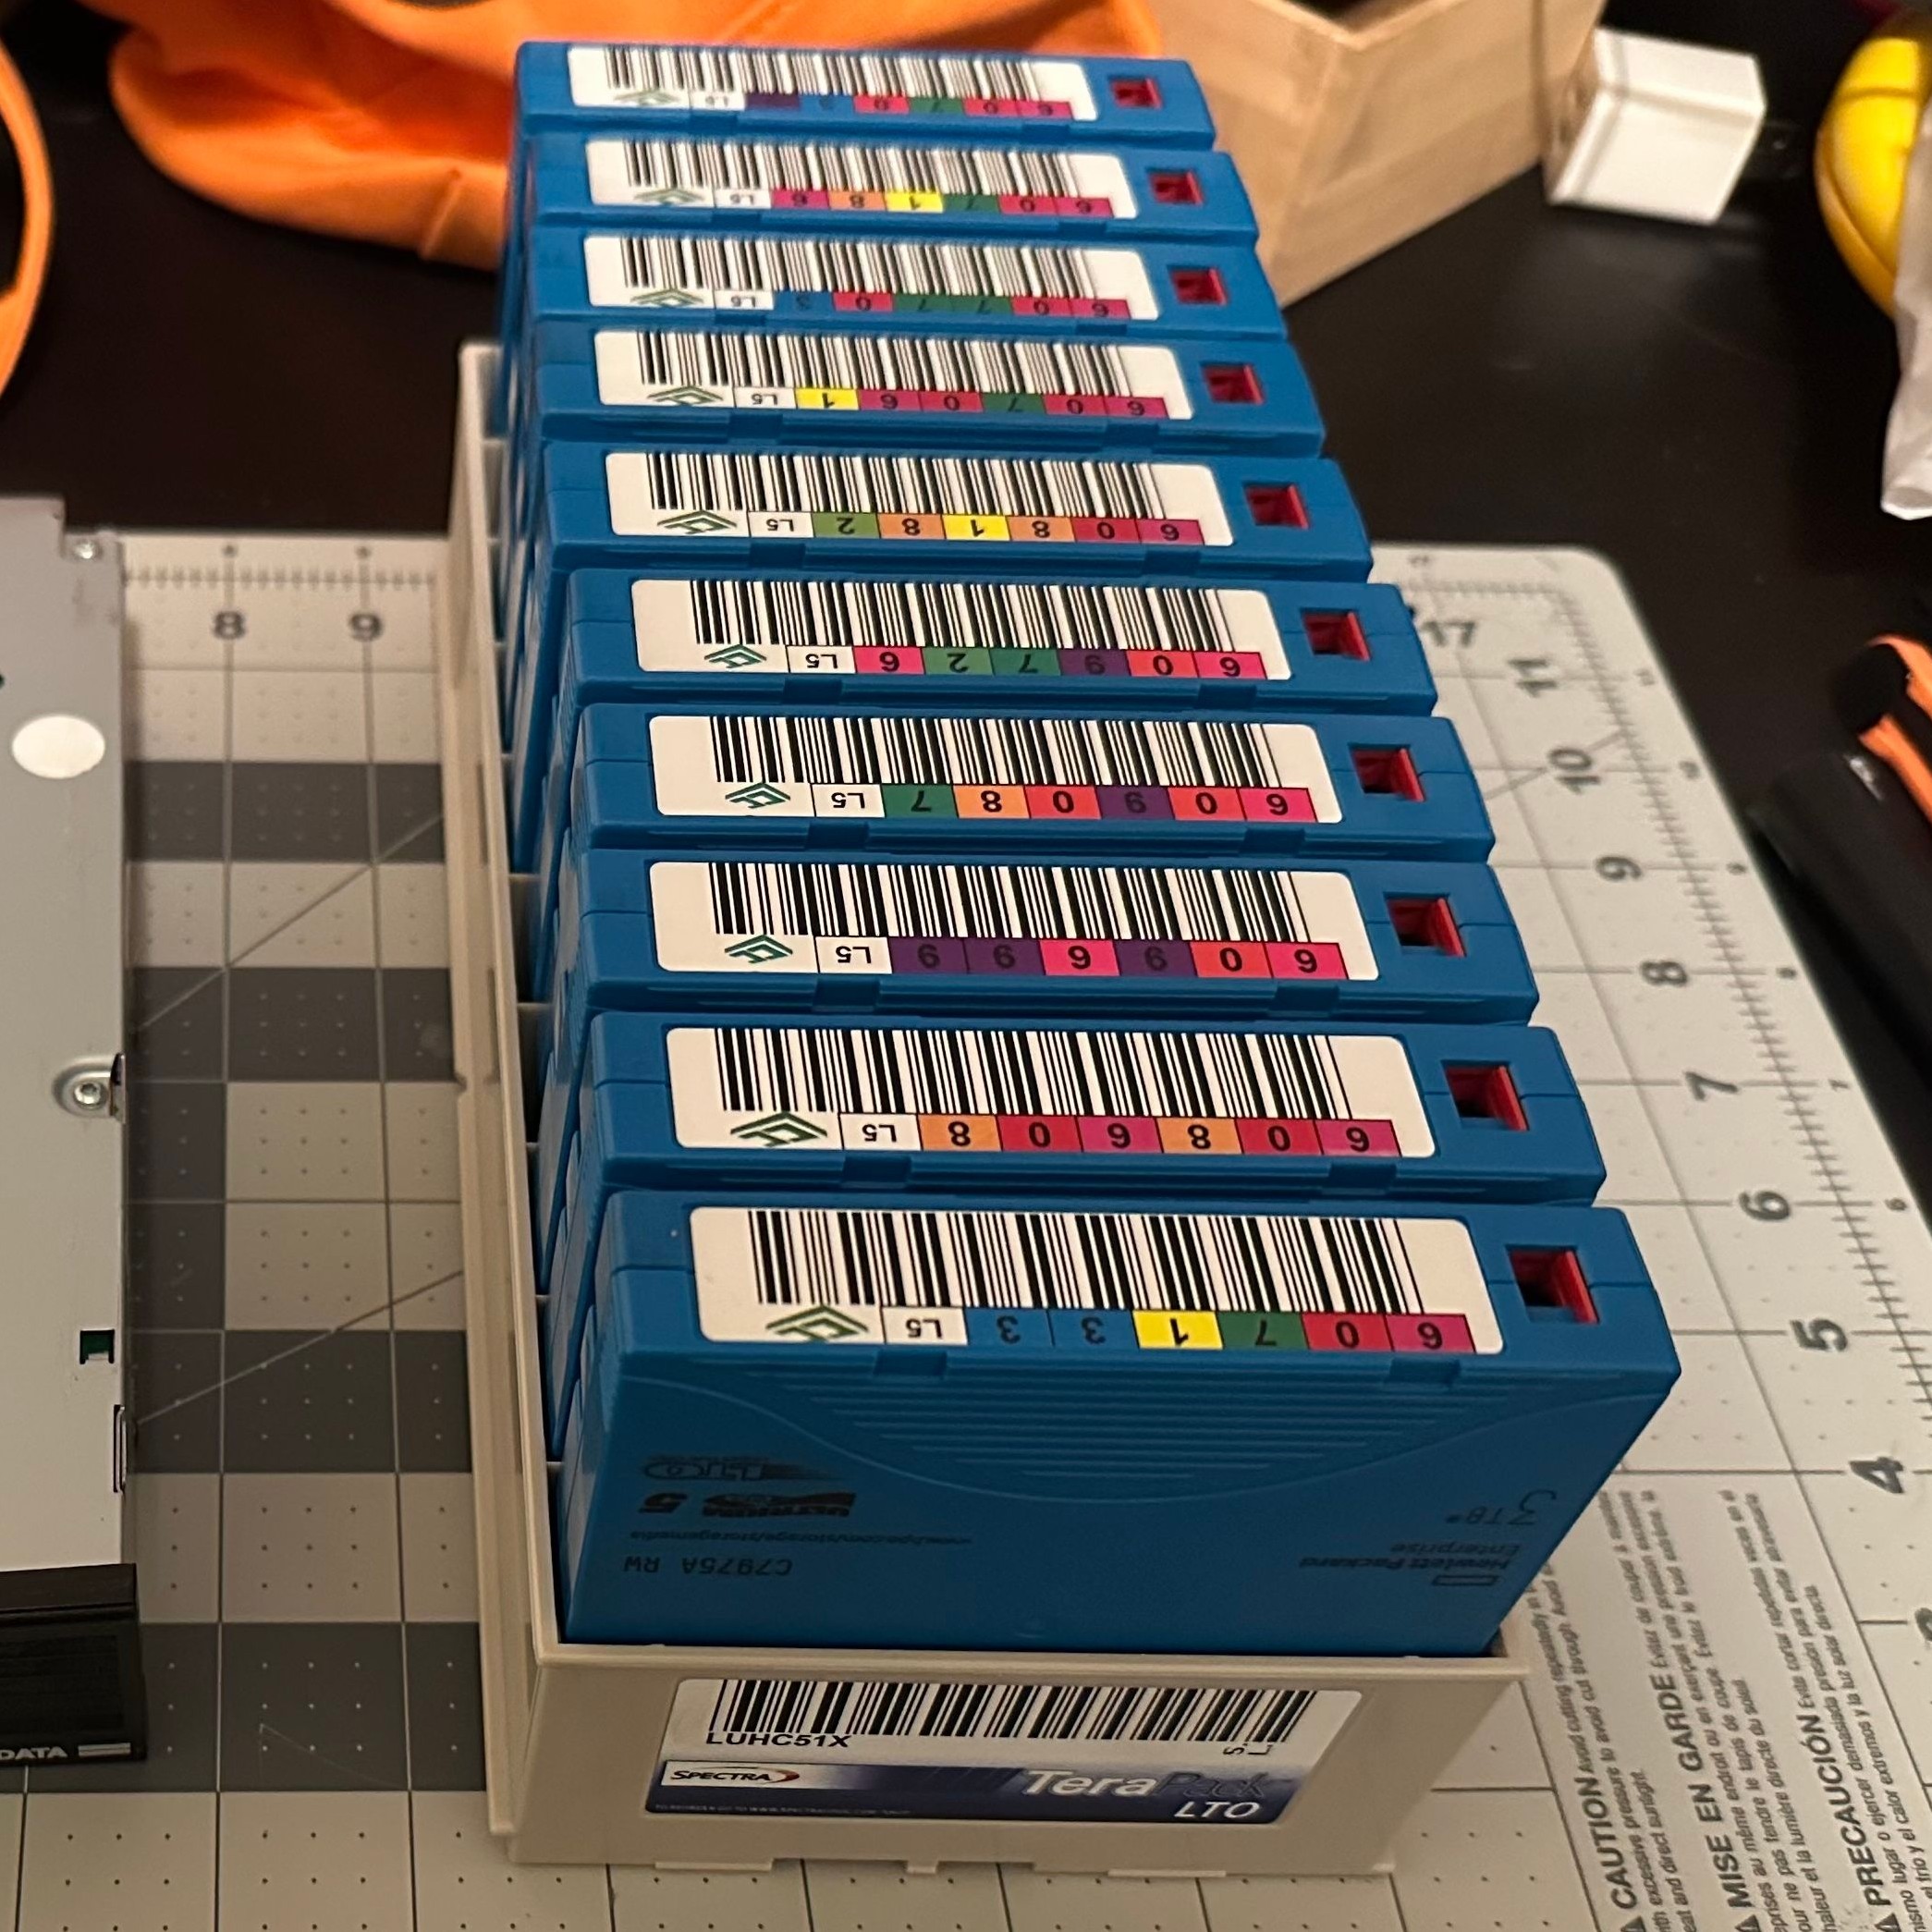
LTO-5 is already well out of date in the professional world, after all– a new server install would be debating the merits of LTO-9 versus LTO-10, but for the homelab it’s a matter of what’s affordable on the used market with decently-sized cartridges. If you can live with 1.5 TB of uncompressed data on a roughly palm-sized Linear Tape, Open cartridge then LTO-5 could be good enough. Yes, the tapes are advertized as 3TB, but that’s assuming a 2:1 compression ratio on the data, which you’re not likely to get on the photos and video that make up much of a data horder’s storage. That’s one thing [Ben] was quick to clear up for us. He also detailed his adventures with the cheaper-to-buy fiber channel model of drive.
The label would have you believe this box stores 30 TB.
Tape drives usually come with an SAS or fiber channel interface– fiber channel being, you guessed it, an optical solution unlike the SCSI-like SAS connection you may be familiar with for block storage devices. With a PCIe adapter it’s not hard to set up, provided you get the cables the right way around! That’s another detail we’re glad [Ben] shared so we can find it again if we have the same problem: with no switch in the circuit, you need a crossover cable to bring TX to RX. Which is obvious in retrospect, but obscure to those of us just learning about the standard.
The advantage, as [Ben] makes clear and everyone has always known is simply price. As of this writing, diskprices.com has 16$/TB as the lowest cost, while [Ben] was able to pick up lightly-used tapes on eBay for only 2$/TB. If you have a lot of data, those savings amortize the drive costs relatively quickly, since a used drive like [Ben]’s can be had for a few hundred bucks.
Storage vendors have been calling things “unified” for years. Sometimes that means one architecture. Sometimes it means several products sharing a management screen and a marketing budget. The term has accumulated enough baggage that a little skepticism is warranted. HPE Alletra Storage MP B10000 Release 6, announced in May, is now generally available. It brings block and file onto the same disaggregated scale-out architecture and OS code base, with independent scaling of performance and capacity and native ransomware detection across both. That’s important because enterprise storage is becoming less of an array decision and more of an architectural one. HPE was recently named a Leader in the 2026 Gartner® Magic Quadrant™ for Enterprise Storage Platforms, which provides useful context, but a quadrant is still a snapshot. GA code is where the architecture has to prove itself. Unified, but not universal The B10000 is not intended to become the answer for every file workload in the data center. Massive-scale, performance-oriented unstructured workloads such as AI, analytics, EDA and media remain better suited to HPE Alletra Storage MP X10000. The aim with the B10000 is narrower and, arguably, more useful: consolidating block and adjacent file workloads onto a common architecture without forcing customers to scale controllers and capacity together. That distinction matters. Vendors have offered “unified” storage before, but the harder question is what is actually shared underneath: protocols, scaling model, software stack and operational experience, or simply the management layer. The architecture is the product The B10000 separates compute from capacity with a “shared-everything” architecture, allowing each to scale independently rather than requiring customers to buy fixed controller-and-media increments. Release 6 extends that model across block and file while retaining a common operating environment and management plane. The interesting part is therefore not simply the addition of file protocols. It is whether customers can consolidate block and the file workloads that naturally sit alongside them without recreating the infrastructure silos they were trying to remove. Disaggregation also changes the economics. If performance and capacity requirements grow at different rates, the infrastructure can follow those curves separately rather than making one drive the other. AI moves closer to operations Release 6 also extends HPE’s AI-driven operations model. Within HPE Data Services Cloud Console, autonomous health assessments can evaluate areas such as capacity and performance, while Storage Copilot provides natural-language interaction, recommendations and the ability to take actions. Agentic Support Automation pushes that model further. Unlike legacy support approaches that depend on known issue signatures, predefined rules or thresholds, it is signature-less: AI agents continuously analyze operational behavior to detect emerging anomalies, investigate likely causes and help drive remediation—even when the specific issue has not been seen before. Capacity exhaustion is a useful example. Total system capacity can appear stable and generate no alert while a single service begins consuming capacity at an unusual rate. Traditional monitoring may not react until a threshold is crossed; agentic support automation can recognize the behavioral shift earlier, connect it to the underlying operating condition and help initiate corrective action before the change becomes a disruption. That is probably the more useful test of the increasingly fashionable word “agentic.” The question is not whether AI appears in the interface, but whether the software can move from describing an infrastructure problem toward helping resolve it. Cyber resilience becomes layered Ransomware defense follows much the same architectural logic. The B10000 now provides native real-time detection across block and file, while Zerto adds protection at the application layer and StoreOnce provides integrated data protection and recovery. No single feature solves ransomware. The more interesting model is multiple detection and recovery mechanisms operating at different points in the stack. Storage competition moves beyond the array None of this means the array is dead. Someone still has to store the bits. But the competitive unit is getting larger. Controllers, media and IOPS still matter. Increasingly, so do the operating model, cyber-resilience architecture, scaling economics and the ability to support multiple data types without multiplying infrastructure silos. The term “unified storage” has been stretched pretty far over the years. What matters now is whether the unification extends below the management layer and into the architecture itself. For more information, visit HPE Alletra Storage MP B10000 web page. Contributed by HPE

 Login