 Login

Apple’s touchscreen MacBook Pro pushes laptop pricing to a new extreme
Prepare to cough up around $14,549 if you want the new touchscreen MacBook Pro to have every upgrade.

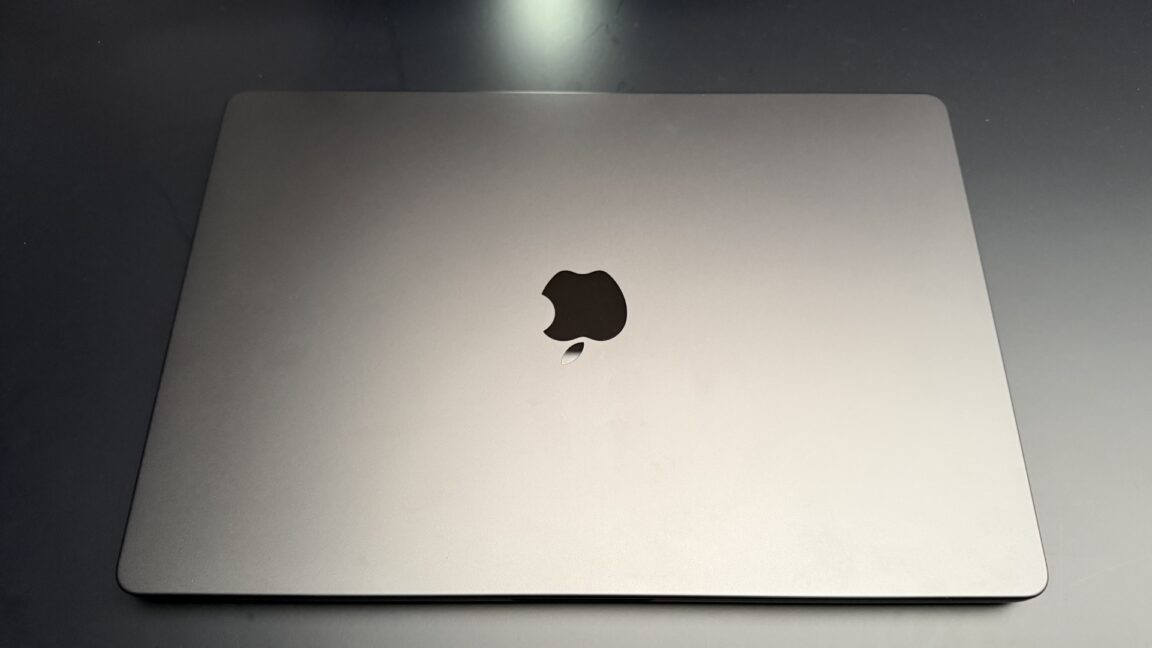
LOS ANGELES—For about five minutes on an extremely crowded showroom floor, I got to take pictures of the new MacBook Pro and test out some of its new features. First impressions: It's not as much of a departure from the previous design as I expected, but the outstanding OLED display steals the show regardless.
The first thing I noticed was that it's lighter. My daily driver is a 14-inch MacBook Pro (M1 Max), and it's a bit weighty for a 14-incher. Picking up the new model, I could immediately tell it was lighter. It's not like it's in a different general weight class, but it's a noticeable difference.
© Samuel Axon


 The U.S. Army has developed a smoke screen that hides soldiers and vehicles from enemy radar as well as from enemy eyes. The Millimeter Wave Screening Obscuration Module releases a cloud of coated fibers into the air, and that cloud blurs the radar signature of everything behind it. Engineers at the U.S. Army Combat Capabilities […]
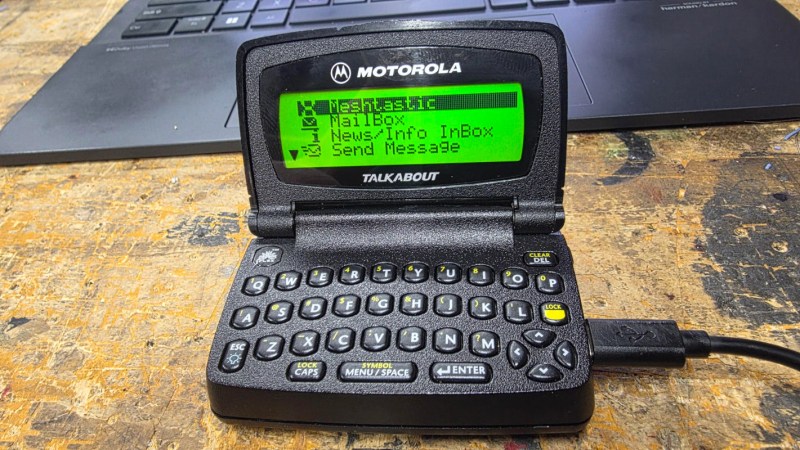
Text messaging has been around on cellular networks en masse for around three decades now. It’s so common that it’s difficult to remember a time without it. Its two-way quick messaging is incredibly useful, but for even simpler communications there’s a one-way system that predates it. Pagers are able to receive simple messages, but outside of hospitals are rarely used nowadays. Eventually some added in two-way communications like this Motorola T900, but they’re still mostly obsolete. That’s why [zindustries87] converted it to operate on the Meshtastic network instead.
To get this pager working, a lot of reverse engineering was needed. There is essentially no documentation on the chips in these devices, so the screen and keyboard both were reverse-engineered to work with other hardware. In this case, [zindustries87] found space for a Heltec V4 with an ESP32-S3, a popular Meshtastic node with a small form factor. Some programming was needed to get everything communicating together, but from the looks of things it seems to have basic functionality.
[zindustries87] points out that this is a prototype, and didn’t know going in if the keyboard and screen could be brought back to life, or if the other hardware would fit in the case. But with it working on this level, they plan to add a number of other features in and possibly build a drop-in PCB replacement for these devices. They were once fairly popular so there are plenty around, and they’re a good form factor for a dedicated Meshtastic device that doesn’t need a smartphone to work. The only other ways of bringing pagers back to life involve bootstrapping an entire pager network, and Meshtastic is a bit more useful than that now.
Welcome back, cyberwarriors!
In this part of the series, we’re looking at how PowerShell can cause serious damage when nothing is restricting it. We’ll show how it can slow systems down and knock them off completely. You’ll see how hardware interfaces can get disabled, license keys wiped and a blue screen forced with machines left unbootable.
All these techniques are destructive, but our goal here is to show you that you shouldn’t just monitor command execution in PowerShell, you should also experiment with Language Modes to limit the attack surface if a workstation gets compromised. If these scripts are misused in the wrong context, the results can be irreversible.
We’ll begin with the basics and then move toward the dangerous things.
The loadram.ps1 script works by aggressively consuming system memory. It allocates large arrays until nearly all available RAM is exhausted, leaving only a small buffer so the OS does not immediately collapse. The machine becomes unusable and applications stop responding.
This type of attack can be used as a DoS tactic to slow down a server, or it can act as a distraction, while other activity takes place.
PS > .\loadram.ps1
The loadcpu.ps1 script applies the same principle to processor cores, pinning usage at 100% until the script is terminated. Just as with RAM exhaustion, this script can serve as a cover while hackers are doing something else.
PS > .\loadcpu.ps1
The license.ps1 script clears Windows product keys by wiping out OEM, retail and volume license entries from the registry. The system becomes stripped of activation data. After restarting the Software Protection Service, Windows will be unlicensed and may refuse to validate against Microsoft servers.
PS > .\license.ps1Then you can check the product key:
PS > (Get-WmiObject -query 'select from SoftwareLicensingService').OA3xOriginalProductKey
The result should be empty.
You can also kill network adapters and USB controllers using killer.ps1 script. Once you run it, the mouse and keyboard will stop working. There will be no way to transfer files, connect to the network or even plug in a recovery device without significant intervention.
PS > .\killer.ps1
PowerSploit includes a module called Mayhem, which has two destructive PowerShell functions. These are Set-CriticalProcess and Set-MasterBootRecord. Both directly attack the operating system itself.
Windows protects smss.exe and csrss.exe by marking them as critical. If they are terminated, the system triggers a Blue Screen of Death. Set-CriticalProcess can tag any process with this critical status. Killing it immediately forces a system crash.
To use it, first copy the Mayhem module from the repository to:
C:\Program Files\WindowsPowerShell\Modules\
Then you can run Set-CriticalProcess:
PS > Set-CriticalProcess
Confirm with Y and expect the machine to blue screen in moments.
This is the most destructive of all. Unlike Set-CriticalProcess, this attack corrupts the Master Boot Record (MBR), which is the first sector of the hard drive. The MBR has the bootloader and partition table and without it Windows cannot load.
When it’s overwritten, the system may only display your custom message and will refuse to boot into the OS. Some malware does the same. The OS will work only if you fix the MBR, but chances are you will have to reinstall the OS.
In our article on Digital Forensics we were repairing a corrupted drive where the MBR had been overwritten.
PS > Set-MasterBootRecord -BootMessage 'Pwned by Cyber Cossacks!'
You can also force the system to reboot right after:
PS > Set-MasterBootRecord -BootMessage 'Pwned by Cyber Cossacks!' -Force -RebootImmediatelyIt will no longer boot into Windows.
We showed how far PowerShell can be pushed when used as a weapon. That alone should be enough to convince you to restrict its use and work with Language Modes to help protect your system. By default, workstations and servers are pretty permissive, which makes them comfortable to use. The same permissiveness is just as accommodating for a hacker who has breached a system through phishing. Restricted Language Mode is a must on workstations where users don’t need PowerShell in the first place.
Want to become a Powershell expert? Join our Powershell for Hackers training.
The post PowerShell for Hackers, Part 5: How to Crash and Burn Windows first appeared on Hackers Arise.
