For this curry, I used the mangoes readily available at Tesco for this simple mango curry. They are usually sweet and juicy, so there is no need to add any sugar or jaggery. A teaspoon Read More ...
TL;DR: BitGo has launched a research and product unit focused initially on AI and crypto. Its first projects include Gokubu, a consumer financial app that BitGo says is already live.
BitGo is moving further into the application business with a new unit intended to build products on top of its digital-asset infrastructure.
The company announced BitGo Labs on October 21, describing an initial focus on the intersection of artificial intelligence and crypto. The unit will develop applications and publish research, prototypes and reference implementations.
Its launch includes Gokubu, which BitGo describes as a consumer app combining an AI-assisted card, a personalized financial assistant and automated rewards features. BitGo says the product is live and accepts registrations.
From Financial Infrastructure To A Consumer Product
The move puts a different kind of execution challenge alongside custody and other infrastructure services. An application must persuade users that its convenience is worth adopting, then deliver that convenience consistently.
For an AI-assisted financial product, usefulness also depends on the boundary between suggestions and actions. Showing someone a possible saving is different from making a transaction on their behalf. Permissions, clear account information and understandable costs are part of the product experience, not details that can be left to the technology underneath.
BitGo’s announcement makes ambitious claims about the role crypto infrastructure could play in an economy of autonomous software agents. Those claims describe its strategy. They do not establish that the emerging applications have already generated material revenue or reached a particular scale.
Similarly, the release’s description of Gokubu does not provide a complete account of fees, jurisdictional eligibility or the terms governing every advertised benefit. Readers should treat it as a launch announcement rather than a review of the service.
The meaningful development is that BitGo has assigned a dedicated team to turn its infrastructure into applications and named an initial consumer product. Whether that approach creates a lasting business will depend on the behavior of those products in use, including how clearly they handle the financial decisions customers entrust to them.
The U.S. Air Force has sent military-style cargo into space and back aboard a SpaceX Starfall capsule as it tests whether rockets could one day deliver supplies to troops anywhere on Earth within hours. The Air Force Research Laboratory flew its own cargo pods inside the capsule on a commercial rideshare launch from Cape Canaveral […]
TL;DR: AnchorWatch has opened its Nevada-chartered Bitcoin custody service, pairing a choice of key-control structures with optional Lloyd’s-backed insurance.
Bitcoin custody is no longer just a question of who holds the private keys. For professional trustees, company treasuries and advisers, it also involves governance, recoverability and what happens if assets are lost through theft or coercion.
AnchorWatch Trust Company has entered that market as a Nevada-chartered qualified custodian. The company is offering a model in which it controls the keys required for custody while clients can retain additional signing authority, alongside a second arrangement distributing key control among AnchorWatch, BitGo and CoinCorner.
The firm says eligible customers can apply for insurance backed by Lloyd’s of London syndicates. Its launch announcement described a possible limit of up to $370 million per client, although coverage depends on underwriting approval and the terms of an individual policy. This is not blanket protection automatically attached to every Bitcoin in custody.
Pricing is also part of its pitch. AnchorWatch is positioning fixed-dollar custody charges, with a monthly ceiling of $10,000, against the percentage-based pricing common across institutional asset services. Insurance costs are separate.
The structure is aimed at customers who want the controls of regulated custody without concentrating every signing decision in a single institution.
Ultimately, the value of any such product depends on the actual key arrangements, policy exclusions, service reliability and how clearly clients understand the risks that remain uninsured.
Written by the News Desk and edited by Samuel Rae.
At Nvidia’s GTC in Berlin, Huang unveiled the company’s new plug-in data center—the DSX Pod—as the key to unlocking Europe’s AI infrastructure lag. Oh, and autonomous humanoid robotics.
TL;DR: AnchorWatch has opened its Nevada-chartered Bitcoin custody service, pairing a choice of key-control structures with optional Lloyd’s-backed insurance.
Bitcoin custody is no longer just a question of who holds the private keys. For professional trustees, company treasuries and advisers, it also involves governance, recoverability and what happens if assets are lost through theft or coercion.
AnchorWatch Trust Company has entered that market as a Nevada-chartered qualified custodian. The company is offering a model in which it controls the keys required for custody while clients can retain additional signing authority, alongside a second arrangement distributing key control among AnchorWatch, BitGo and CoinCorner.
The firm says eligible customers can apply for insurance backed by Lloyd’s of London syndicates. Its launch announcement described a possible limit of up to $370 million per client, although coverage depends on underwriting approval and the terms of an individual policy. This is not blanket protection automatically attached to every Bitcoin in custody.
Pricing is also part of its pitch. AnchorWatch is positioning fixed-dollar custody charges, with a monthly ceiling of $10,000, against the percentage-based pricing common across institutional asset services. Insurance costs are separate.
The structure is aimed at customers who want the controls of regulated custody without concentrating every signing decision in a single institution.
Ultimately, the value of any such product depends on the actual key arrangements, policy exclusions, service reliability and how clearly clients understand the risks that remain uninsured.
Written by the News Desk and edited by Samuel Rae.
TL;DR: BitGo and HashKey Cloud have expanded an earlier staking relationship into a broader Asia-Pacific partnership covering staking, trading, custody and real-world asset tokenization. HashKey will support validator services for eligible BitGo clients, initially across Ethereum and Solana.
BitGo and HashKey are turning an existing staking relationship into a wider institutional crypto infrastructure partnership across Asia.
The companies signed an expanded agreement in Singapore covering four areas: staking, trading, custody and real-world asset tokenization.
HashKey Cloud will become a validator partner on BitGo’s platform, initially supporting Ethereum and Solana staking for eligible institutional customers.
The two firms also plan to cooperate on institutional trading flows.
On the custody side, BitGo will make its infrastructure available to HashKey Capital and associated funds, subject to onboarding and individual agreements.
BitGo is also set to become a custody partner for HashKey’s real-world asset tokenization initiatives.
Taken together, those pieces form something closer to a full institutional asset stack than a single product partnership.
A fund entering crypto increasingly needs more than somewhere to store tokens.
It may need staking infrastructure for proof-of-stake assets, trading liquidity, regulated custody and systems capable of handling tokenized traditional assets.
Providing those services through connected partners can reduce some of the fragmentation that institutions face when entering digital markets.
The geographic focus matters too.
HashKey has built a substantial presence in Hong Kong and the broader Asia-Pacific crypto market, while BitGo has spent years developing regulated custody and institutional infrastructure.
BitGo’s Abel Seow said institutions in Asia increasingly want infrastructure covering the full lifecycle of an asset rather than isolated services.
The agreement attempts to provide exactly that.
The two companies had already been working together around staking before broadening the relationship.
The latest deal therefore looks less like a speculative memorandum and more like an expansion of an existing integration.
Asia has become one of the most competitive regions for institutional digital-asset infrastructure.
Hong Kong, Singapore and other financial centers have been building regulatory frameworks intended to let established financial firms engage with crypto without relying on the looser models that defined the industry’s early years.
That creates demand for providers able to combine regulated custody with blockchain-native services.
BitGo and HashKey are betting that the winning institutional platforms will need both.
The New Members Are Joining More Than A Trade Group
LF Decentralized Trust sits underneath a collection of open-source projects used across enterprise and blockchain systems.
Its portfolio includes technologies such as Hyperledger Fabric and Besu, along with broader identity, interoperability and tokenization tooling.
That makes membership more practical than simply signing up to an industry association.
Members can contribute engineering resources, governance and funding to infrastructure intended to remain openly available.
Swift joining is particularly notable.
The global financial messaging network is already experimenting with shared-ledger infrastructure and tokenized bank deposits.
Wells Fargo brings another major regulated financial institution into the same open-source environment.
Their arrival reflects how blockchain adoption inside large financial firms is changing.
Institutions are increasingly interested in shared standards and neutral infrastructure rather than proprietary experiments that cannot easily connect to one another.
Tokenization And Cross-Ledger Connectivity Get New Projects
LF Decentralized Trust is also launching two new initiatives.
Panarus is focused on tokenization infrastructure, while the Cross-Ledger Protocol Research lab, or CLPR, will explore ways for separate ledger systems to communicate and coordinate.
Interoperability is becoming one of the central problems in institutional tokenization.
Wireless security monitoring in the 2.4 GHz spectrum often depends on active probing, which can not only make the monitoring infrastructure vulnerable to attackers but also clutter the radio frequency environment. On the other hand, taking a passive approach by listening without transmitting allows security teams to detect malicious wireless activity more discreetly and reliably.
To put this idea into practice, the project Travel WiFi Canary was developed. This system serves as an early-warning mechanism using ESP32 microcontrollers. By operating the Wi-Fi radio in promiscuous mode, the device passively captures raw IEEE 802.11 management frames and traffic patterns. This helps identify potential threats such as deauthentication attacks, beacon spam, rogue access points often referred to as Evil Twins, and unauthorized probe requests. Eventually, it provides comprehensive insights into the wireless environment, enabling you to act proactively rather than reactively.
In this article, we will guide you through configuring, flashing, and running Travel WiFi Canary on the LilyGo T3 V1.6.1 development platform. Let’s get rolling!
What is Travel WiFi Canary?
The Travel WiFi Canary is a project that turns a low-cost ESP32 microcontroller into a passive 2.4 GHz threat-detection device. It operates continuously by alternating between active network enumeration and passive promiscuous packet capturing across specified channels.
At its core, the device’s Wi-Fi chip listens directly to raw radio signals passing through the air rather than connecting to a specific network.
When a wireless signal arrives, a fast automated responder checks the basic structure of the incoming data instantly. It identifies network management signals, such as connection requests, disconnection commands, or nearby network announcements, and separates them from standard web traffic.
To handle intense bursts of wireless activity without getting overwhelmed or missing crucial information, the chip places these flagged security signals into a temporary holding queue. This allows the main system to process and analyze the data safely in the background while keeping the hardware radio free to capture new incoming signals without interruption.
The central intelligence of the project relies on a dynamic confidence-scoring engine rather than rigid binary alerts. As the system processes the ring queues and periodic active scans, it evaluates detected anomalies against a local memory table built during the startup baseline phase.
Active scans check nearby Access Points for structural security violations. If an Access Point using an encrypted baseline protocol like WPA2 or WPA3 is detected operating without encryption, the system identifies an open clone attack. Security downgrades, unexpected vendor prefix mismatches on familiar SSIDs, or sudden disappearances of legitimate Access Points during an active open broadcast instantly contribute points to the global confidence score.
Simultaneously, the passive sniffer thread drains the lock-free queues to detect airborne attacks. Deauthentication frame floods are monitored over rolling time windows, assigning score penalties if threshold limits are breached by single sources or broadcast addresses.
The sniffer also inspects the payload fields inside beacon frames to detect Pwnagotchi signatures, parsing JSON structures hidden in vendor tags to determine if the device is operating in an active attack state.
All calculated points feed into a unified state machine. Aggregate scores between zero and two keep the device in a normal state, scores between three and five push it into a caution state, and scores of six or higher escalate the device into an active alert state.
To prevent temporary radio noise or brief packet anomalies from causing permanent alarm states, a background timer executes a score decay routine every minute. This routine gradually reduces the aggregate threat score over time, allowing the system to automatically transition back to a normal state once threat vectors clear the area. Hardware outputs, such as status LEDs or connected display controllers, continuously mirror the internal state variable to provide real-time visual monitoring.
What is LilyGo T3 V1.6.1?
The Travel WiFi Canary was initially made for the M5Stack Atom Lite development board. However, in this demonstration, I will test it on the LilyGo T3 V1.6.1.
The LilyGo T3 V1.6.1, also called the TTGO T3 LoRa32 V1.6.1, is an open-source development board designed for Internet of Things (IoT) projects and long-range RF communication. It has an ESP32 chip that allows for packet sniffing and Wi-Fi scanning. It gives us all the necessary functionality for wireless threat detection required by the Travel WiFi Canary project.
Getting Started with Travel WiFi Canary
The best way to flash the Travel WiFi Canary is by using Visual Studio Code along with the PlatformIO IDE extension. The installation process is fairly simple, so let’s move on to the next step, which is cloning the repository. I will use the modified version designed for the LilyGo T3 device. Here’s the command to do that:
Next, connect your LilyGo T3 V1.6.1 to your computer using a data-capable Micro-USB cable. In Visual Studio Code, click on the PlatformIO status bar at the bottom and select env:esp32dev. Then, you can either click the checkmark icon in the status bar or press Ctrl+Alt+B to compile the firmware.
Once that is complete, click the right arrow icon in the status bar to start the upload process. PlatformIO will automatically detect the serial port, trigger the ESP32 to enter bootloader mode via auto-reset circuitry using the DTR and RTS lines, erase the necessary flash sectors, and upload the binaries seamlessly.
After the upload is complete, you can monitor the device with the built-in command:
pio device monitor -b 115200
At this point, the state machine and scanning engine are fully operational. During its initial scan, it detected seven nearby access points, recording their SSIDs, BSSIDs, signal strengths, channels, and encryption methods in memory.
Now, let’s simulate an open clone of a known encrypted network. The README file provides the following instructions:
I created a Wi-Fi access point from my phone with the same name as the network to which my system is connected, but without a password. Let’s observe how the WiFi Canary responds.
The script successfully identified the clone and granted 4 points to the score, changing the state to caution. The rogue open clone remained active in the following 20-second scan with a strong RSSI, adding another 4 points, which brought the total score to 8 and changed the state to alert. At the 310-second mark, the decay timer activated, decreasing the score from 8 to 7. However, since the score remained above the SCORE_ALERT threshold of 6 or higher, the system continued to maintain its alert state until the threat was resolved and the score naturally decayed back to zero.
Limitations
Despite the benefits of confidence scoring in reducing unexpected alerts, the possibility of false positives still exists. This is particularly true in enterprise networks, multi-node mesh setups, and crowded public venues, which can display behaviors that resemble attack patterns. On the flip side, false negatives may arise if a skilled attacker impersonates a legitimate BSSID while carefully adjusting their transmission power to fit in with normal signal strength variations, thus evading detection.
The limitations of the physical hardware create additional coverage boundaries. Passive detection of deauthentication relies heavily on the distance from the receiving device, meaning that low-power or far-off transmitters may be beyond the reach of the antenna. Furthermore, monitoring is confined solely to the 2.4 GHz spectrum, leaving the 5 GHz and 6 GHz bands completely unmonitored.
Lastly, the design of the radio architecture leads to a temporary gap in scanning whenever the chip switches between promiscuous packet sniffing and active environment scanning, resulting in a three-second blind spot where airborne deauthentication bursts can go unnoticed.
Summary
For many travelers and remote workers, understanding whether the Wi-Fi around them is secure is crucial. Private messages and sensitive information can be easily compromised when malicious actors set up fake hotspots or disrupt local connections. A device like the Travel WiFi Canary can continuously monitor the airwaves and alert you the moment a wireless attack is detected.
This device uses active Wi-Fi scanning and passive signal listening to find threats in real time. It constantly checks nearby networks against a trusted standard to spot fake open hotspots, duplicate routers, or security issues. At the same time, it listens for harmful activities like deauthentication attacks or rogue scanning tools. When it detects a threat, it raises a danger level with an internal scoring system and triggers a clear visual alarm. This alerts you immediately, giving you a warning before your devices may face any risk.
If you’re interested in improving your knowledge of wireless security, take a look at our Wi-Fi Hacking training. This course will guide you on how to assess the security of wireless networks and equip you with modern strategies to protect them effectively.
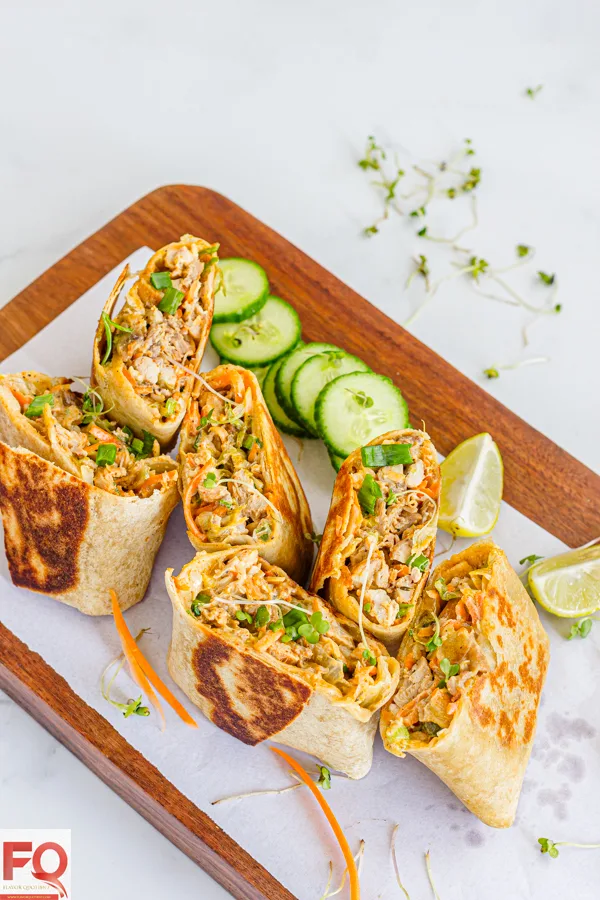
If you love a good chicken wrap but want something lighter, fresher and packed with protein, this high-protein chicken salad wrap is exactly what you need!
Looking for a lunch that is high in protein, packed with crunch and actually exciting to eat? This high-protein chicken salad wrap might just become your new favorite!
Creamy, crunchy, juicy and incredibly satisfying — all wrapped up into one wholesome, protein-packed meal. Perfect for a quick lunch, easy dinner or a delicious meal-prep option!
And there are more than 5 reasons why you will fall for this recipe!
They are high in protein while being low in calories thanks to the Greek yogurt instead of mayo.
Loads of crunch from fresh veggies giving every bite plenty of texture.
Big on flavor from paprika, garlic powder and Italian seasoning.
Perfect for meal prep where you can assemble the wraps whenever you need a quick meal when you have the salad ready!
Skillet-toasted for extra deliciousness - that final golden toast takes these wraps from good to seriously addictive!
What is a High-Protein Chicken Salad Wrap?
A High-Protein Chicken Salad Wrap is a wholesome, satisfying wrap made with tender seasoned chicken, crunchy fresh vegetables and a creamy protein-rich dressing, all wrapped in a soft tortilla.
Unlike a traditional chicken salad that often relies heavily on mayonnaise, this version uses Greek yogurt as the base of the dressing, giving it a creamy texture while adding extra protein.
The chicken is seasoned with paprika, garlic powder, black pepper and Italian herbs, pan-seared until golden, then shredded and tossed with crisp iceberg lettuce, carrot, celery and spring onion greens.
The finished chicken salad is tucked into a wholewheat tortilla and lightly toasted on a skillet until golden and crisp.
The result is a fresh, creamy, crunchy and protein-packed meal that works beautifully for lunch, dinner or a quick meal-prep option.
That solved where my infrastructure notifications should go. It did not solve who was supposed to notice that a VPS was running out of disk space, waiting for a reboot or quietly collecting failed systemd units like

 Login

 The U.S. Air Force has sent military-style cargo into space and back aboard a SpaceX Starfall capsule as it tests whether rockets could one day deliver supplies to troops anywhere on Earth within hours. The Air Force Research Laboratory flew its own cargo pods inside the capsule on a commercial rideshare launch from Cape Canaveral […]