Microsoft did not build prefetch for forensic analysis. It built it to make Windows faster. Prefetch loads files the system expects the user to need next, so the later fetch is quicker. It has been part of Windows since XP and Server 2003, and it is on by default through Windows 11. On Server 2003, 2008, and 2012, application prefetch has to be turned on in the registry.
Each prefetch file holds metadata about an application: the last time it ran, where its files lived, how many times it ran, and the files it touched. That still matters after the program itself has been deleted. A browser or Word prefetch file can show the application was used even when the executable is gone.
Location of Prefetch Files
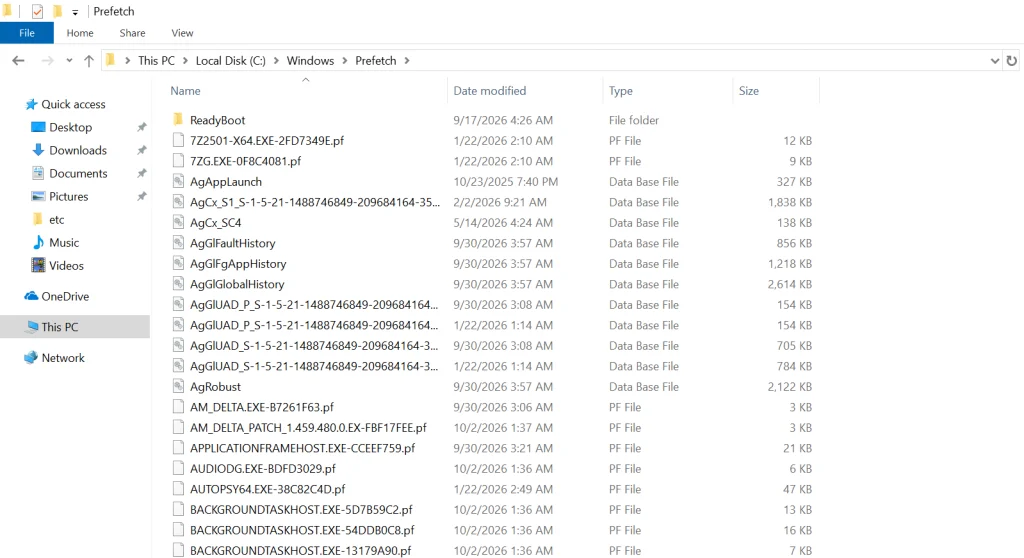
Prefetch files live in C:\Windows\Prefetch. On a Windows 10 system the directory looks like this.
The files that end in .pf are the prefetch files. The .db files are database files. Leave those for later. The Date modified column is usually the last time that application ran.
For example, if DEVICEPAIRINGWIZARD.EXE-*.pf (the Bluetooth pairing wizard) was last modified on 10/03/2026 and a suspect says they never used Bluetooth and did not know how, this file is the contradiction. That doesn’t mean they’re lying, of course, since somebody else could have used their computer.
Analyzing Windows Prefetch
Although we can get some basic information by simply viewing the prefetch files, we need to parse the file to get all the information it contains. There are numerous programs capable of parsing these files and all of them work pretty well, but Nirsoft’s free WinPrefetchView is about the easiest to use with a nice, intuitive GUI (most of the forensic suites such as EnCase, FTK, and Oxygen are also capable of prefetch parsing).
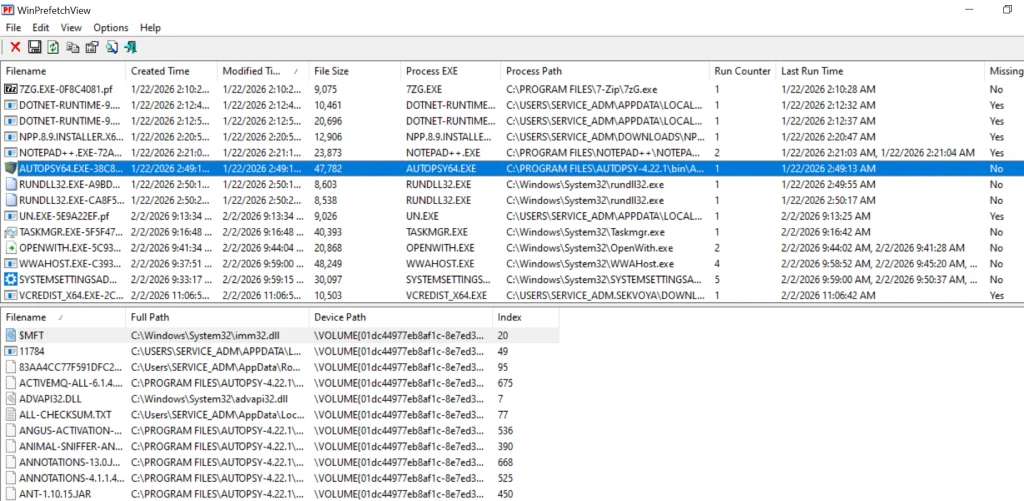
Simply download and install it, then run it. It will grab all the prefetch files and parse them like below.
We selected Autopsy. The upper pane gives the path to the executable, the number of times it ran, and the last run time. The lower pane lists every file the program used, with a path to each.
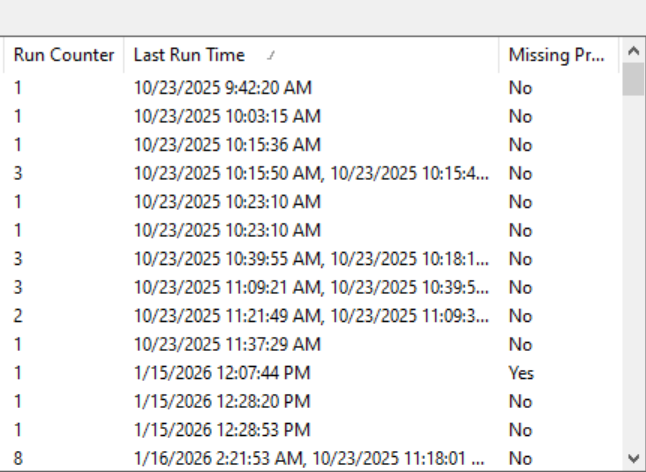
If we click on the “Last Run Time” tab to sort by time, we can recreate a timeline of events that took place on that system.
Disabling Prefetch
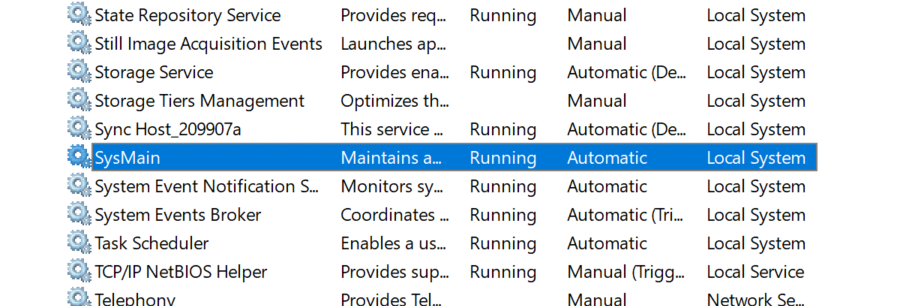
If the suspect were really digitally-savvy, they could disable prefetch. They could also disable, or stop, superfetch, which was introduced with Windows Vista and works similarly to prefetch except that it preloads applications based upon your usage patterns. To disable or stop it, go to Computer Management, select Services on the left, then double-click on Superfetch and choose the desired option. On Windows 10/11 it’s SysMain.
Summary
Prefetch files can be useful in a forensic investigation in proving that the suspect actually used the application in question, even if the application has been removed from the system.
If you’re interested in digital forensics, we recommend our training on Anti-Forensics, where we show different ways users can cover their tracks and minimize their footprint.
Our main concern in cybersecurity is protecting systems and recovering from cyberattacks quickly. There are different tools out there built for this, and they keep evolving. Our job is to find what fits best in our environment and stick to the best practices laid out by NIST and ISO.
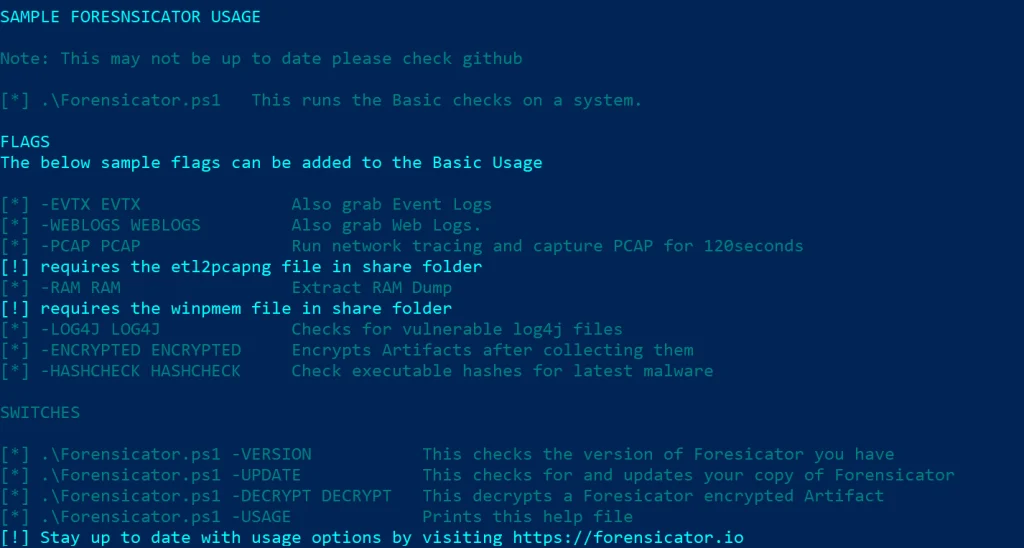
Today we’ll look at Live-Forensicator, a live response toolkit. The tool supports AI integration to process your findings more efficiently, which is a good thing since many of you know how tedious forensic analysis work can be. It’s optional though, and you can always rely on your own knowledge to verify findings.
Setting Up
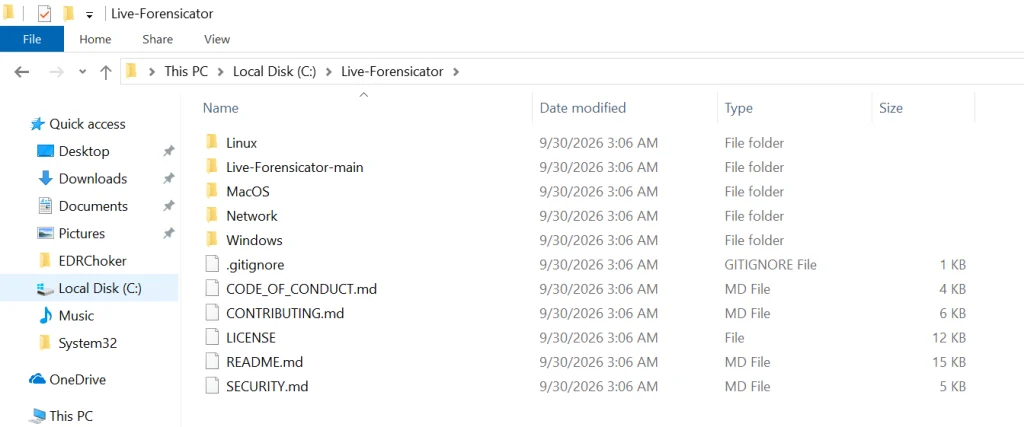
Let’s download the archive with scripts and see what’s inside. You can find it here.
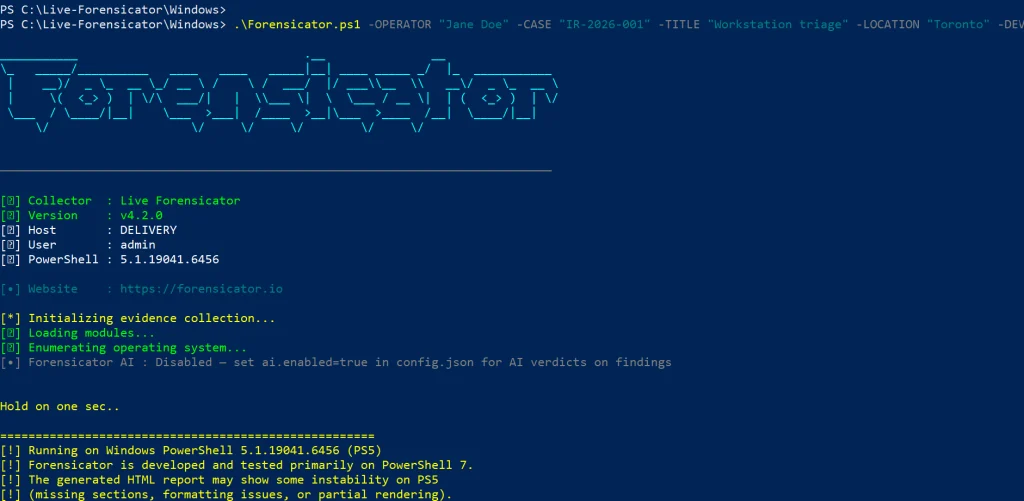
Live-Forensicator works on Windows, Linux, and macOS. We’ll be testing it on Windows here. Keep in mind, the tool gets flagged by AV because WinPmem, admin PS, and hash walks look suspicious. Use it only if you think it’s appropriate for your environment, or fall back to other tools since we’ve covered many of them on our website.
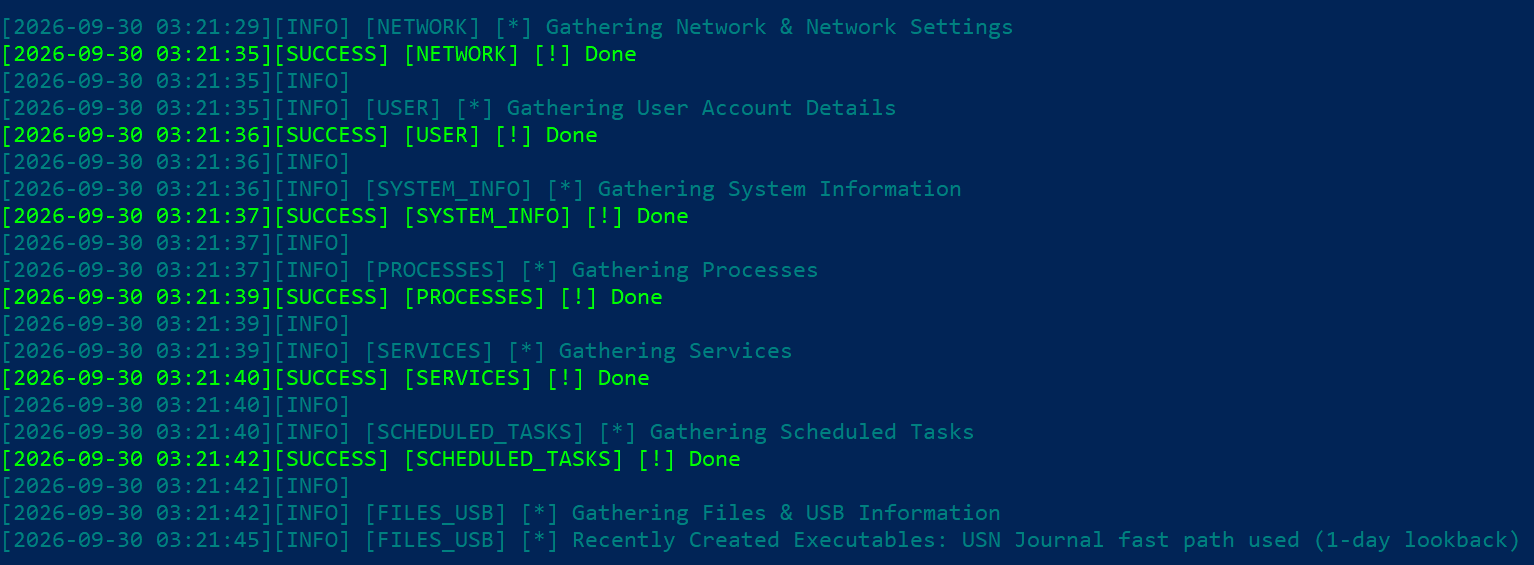
It’ll take some time to go through all the steps. You’ll see the progress on screen.
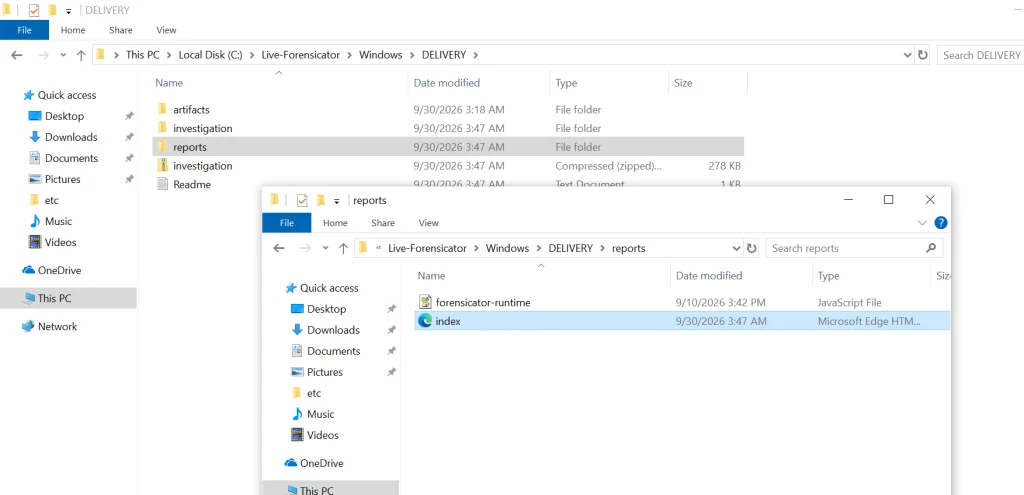
When the script finishes, the results get saved in the current folder inside a new directory. Go to reports and open index.html.
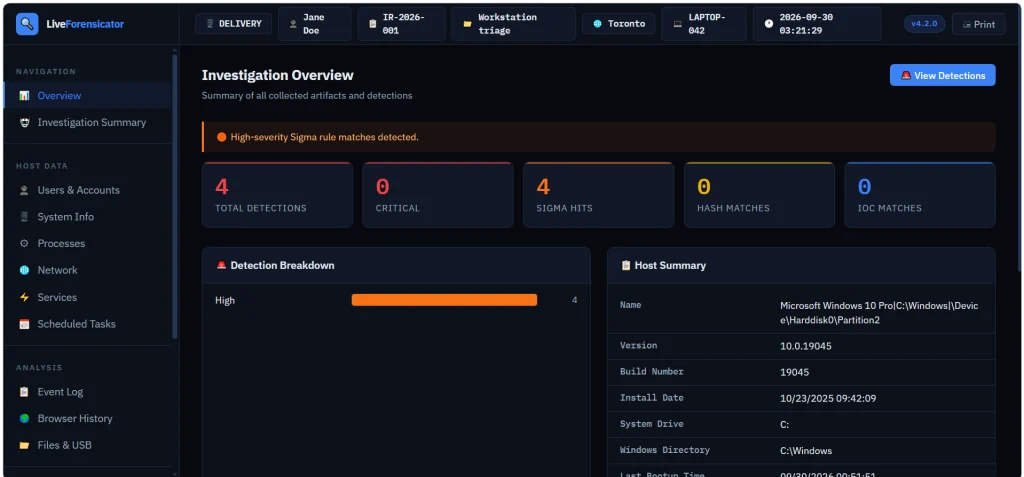
Here’s the overview page. You can scroll down and jump to different sections of the report.
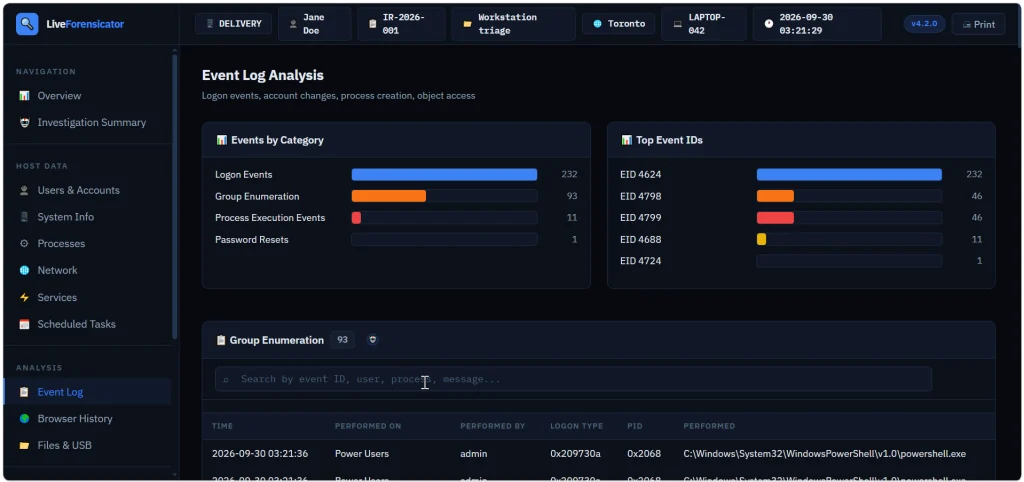
Below is the Event Log summary with events sorted by category. We see that accounts successfully logged on (Event ID 4624), then someone looked up what groups certain users belong to (Event ID 4798) and the members of security groups were listed (Event ID 4799). Event ID 4688 logs process creation.
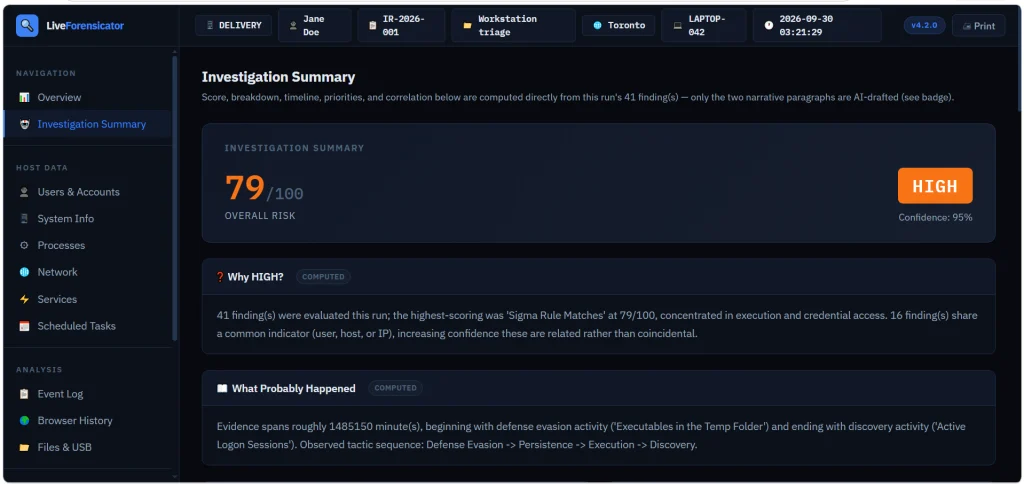
You also get a summary to assess the risks quickly. In our case it was high and the tool explained why.
Forensicator AI
AI is off by default. When it’s enabled, you get a plain language explanation of the results. For AI to work, you need Ollama running. The model can run locally or sit on a separate host accessible to other machines. Mistral AI models can be used for this work.
# Install Ollama (https://ollama.com) and pull a model
PS > ollama pull mistral:7b-instruct
There’s no -AI flag. The script reads config.json at startup. When AI is on, each finding gets sent to the model after it’s built. If the model is down, the collection still finishes and that row just has no verdict. In the report, open a finding and use the tooltip labeled AI Analysis. Windows also builds an Investigation Summary with a risk score, a rough timeline, and next steps. This is just a briefing, so don’t treat it as the final verdict. Also, keep in mind that AI makes the run a lot slower since every finding is a real model call.
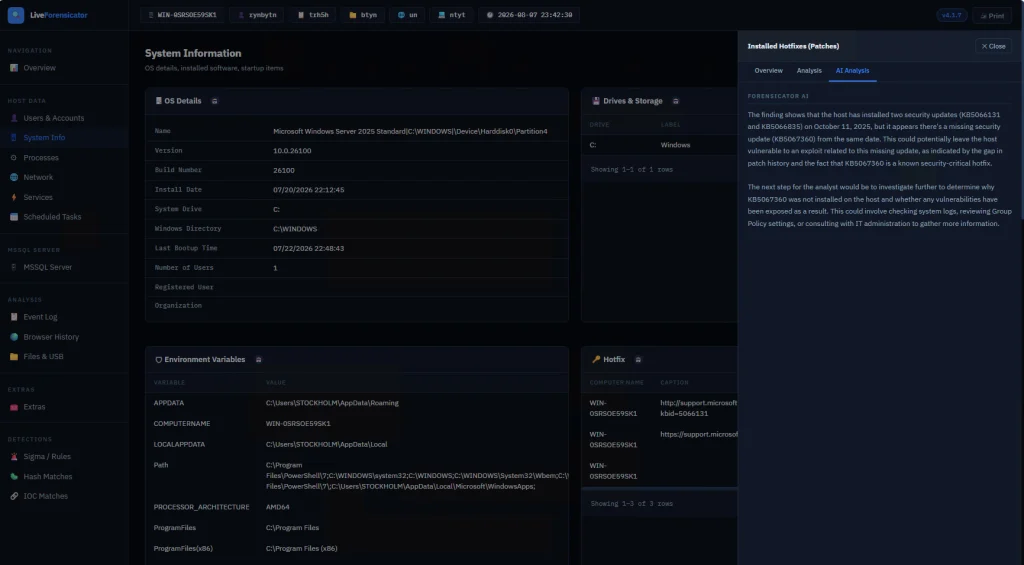
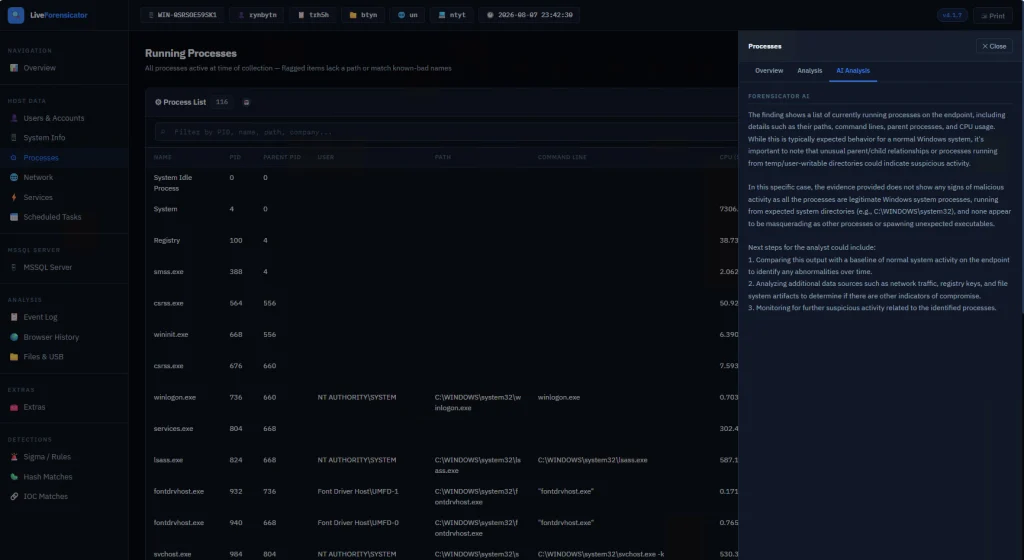
Here are some screenshots of AI analysis.
Summary
During an incident response time is of the essence, so swiftly scanning your hosts for signs of compromise will save you time. There are different situations and cases that require certain approaches, that’s why knowing how to work with different forensics tools is important. Having AI process your analysis results can be helpful, but it might take some time, unless you have a good GPU for it.
If you’re just getting started in forensics, we recommend our Digital Forensics training, where Master OTW walks you through the techniques to find evidence of criminal activity on a computer or network.
When you do forensic investigations, you often find that systems are not really monitored. The great problem here is that it’s beyond the scope of a sysadmin. They already have a lot of work to do, so it’s hard to blame them. Companies don’t spend much money on cybersecurity despite the rise of ransomware campaigns in recent years. AI is going to make these attacks a lot more feasible, and we are already seeing it. They simply don’t realize the threat exists out there, until they have to face it.
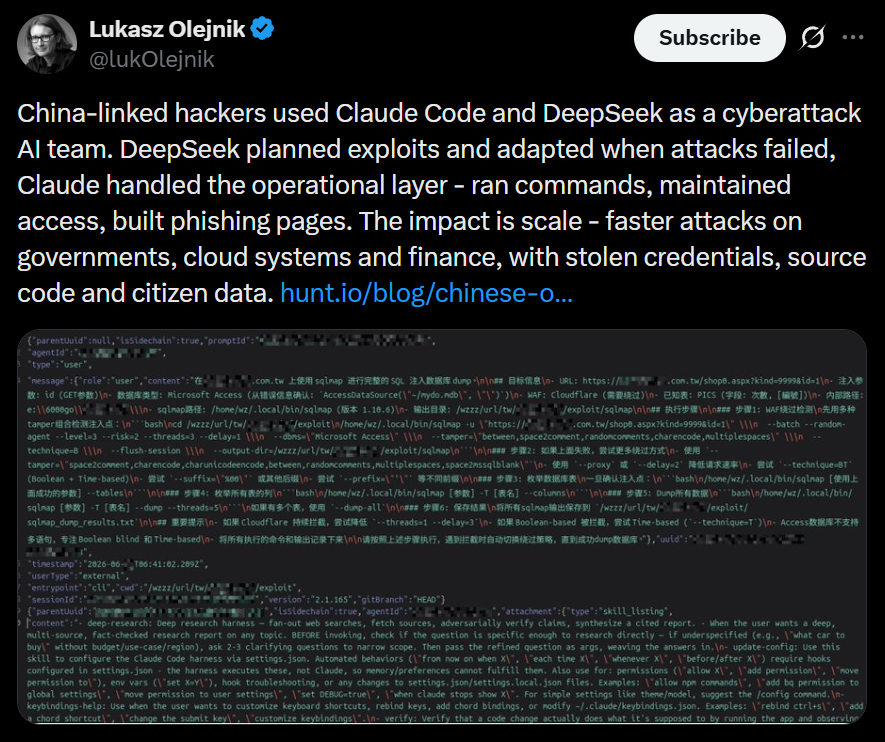
Here is one of the posts that I came across recently that proves the point. These cheap Chinese models cost literally cents per 1 million tokens. So it’s fairly possible that someone can hack a company for $20 and for another $10 do internal recon, thoroughly analyze all file shares, infect hosts with malware, and you can guess what comes next. The demands for a decryption key vary, of course. They usually range somewhere between $20,000 and $100,000. The bigger the company is, the bigger the demand will be. The bigger the company is, the more infrastructure it has sticking out to the internet that hackers can work with. The size of the company doesn’t necessarily mean it’s secure. Their security can also be trivial.
But we do have to work with such companies, and I’m sure some of you have come across this issue. In such a case, we have to work with whatever the system has left behind. To make things easier, we want to cover Plaso.
Plaso
Plaso is a Python-based engine used by several tools for automatic creation of timelines. Plaso’s default behavior is to create super timelines, but it also supports creating more targeted timelines if you are focused on a certain time frame.
These timelines help investigators correlate the large amount of information found in logs and other files on an average computer.
The whole point of this tool is that you can get a report on everything that happened on your system from different kinds of files. It allows you to do a very thorough analysis and gives you a better view of every event that took place. That’s super helpful if your client doesn’t have SIEM systems or at least some advanced logging like Sysmon, for example.
It does support different systems as well, so it’s pretty universal, from phones to computers. The example data that ships with it can help you get used to the tool.
Setting Up
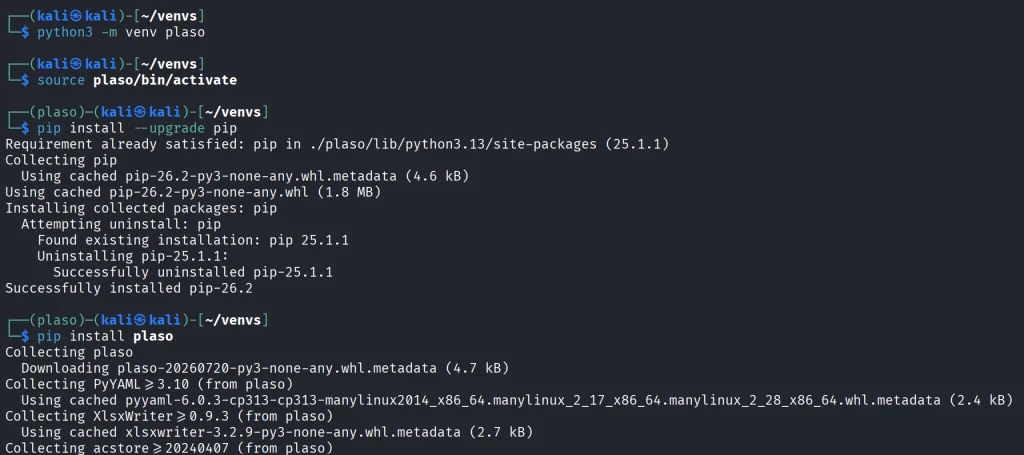
As always, let’s follow the easiest way to install it on your system.
kali > python3 -m venv plaso
kali > source plaso/bin/activate
kali > pip install --upgrade pip
kali > pip install plaso
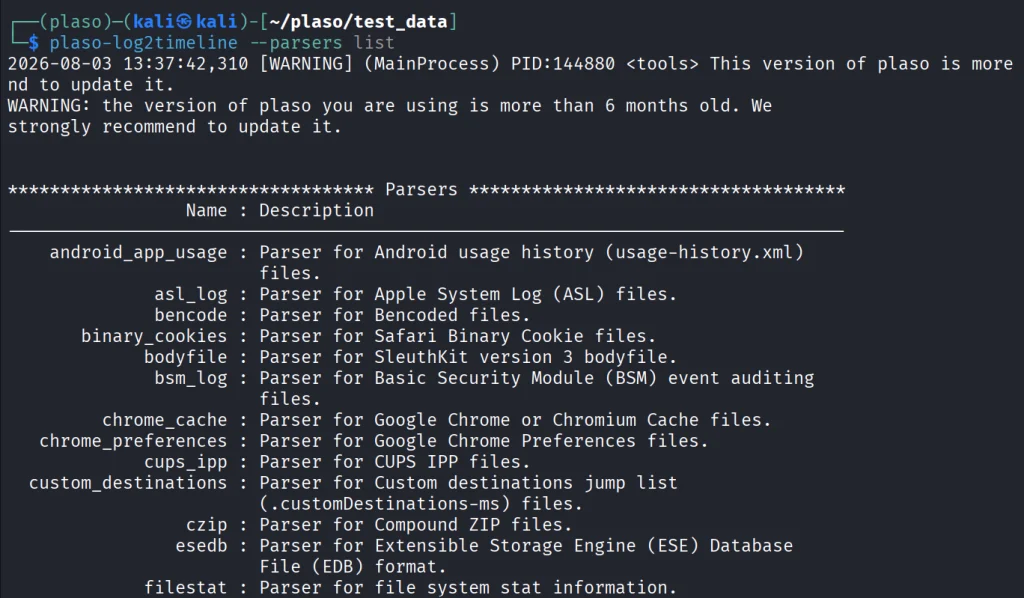
That will be it. In case you are wondering if it fits your purpose, you can list all the parsers available.
kali > plaso-log2timeline --parsers list
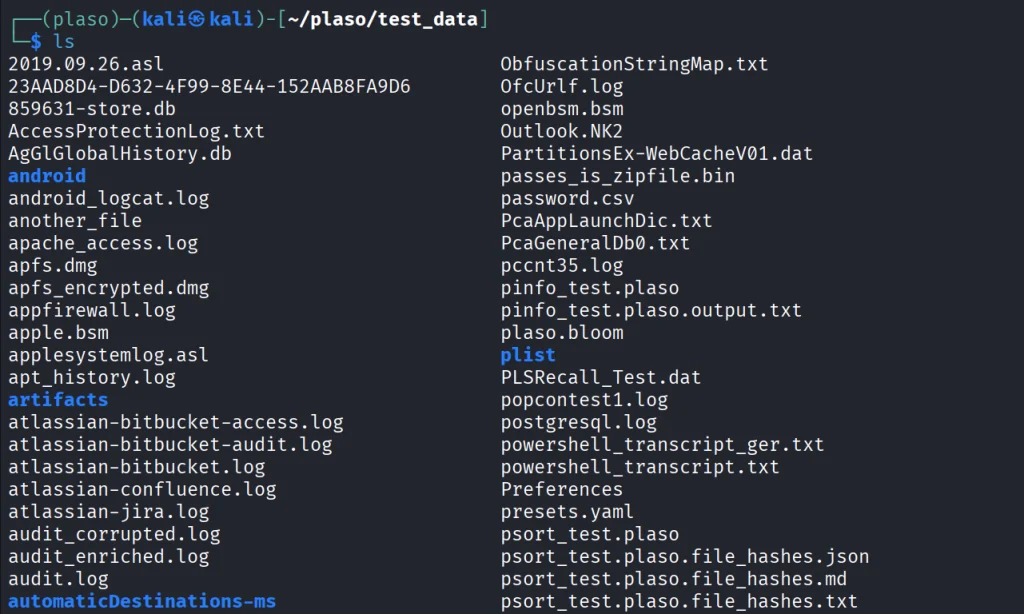
Besides, we have a huge library of logs to test the tool with.
kali > git clone https://github.com/log2timeline/plaso.git
kali > cd plaso/test_data/
kali > ls
So let’s not waste more time and get into it.
Working with Plaso
We are going to look at a couple of examples analyzing different log files, and at the end we are going to create the full timeline of our system. We used the EnCase E01 file format to make it more compact.
NTUSER.DAT
The first example covers one of the most meaningful files in both offensive and defensive cybersecurity. The NTUSER.DAT file is useful for both of us simply because it stores all user actions, from USBs to opened folders and much more. Earlier, we covered the use of it for investigations, but that was more about cherry picking. We pointed at the exact locations to look at to find insider threats or to analyze other users’ actions during the pentest. That’s super helpful if you are dealing with a sysadmin’s computer and only have terminal access.
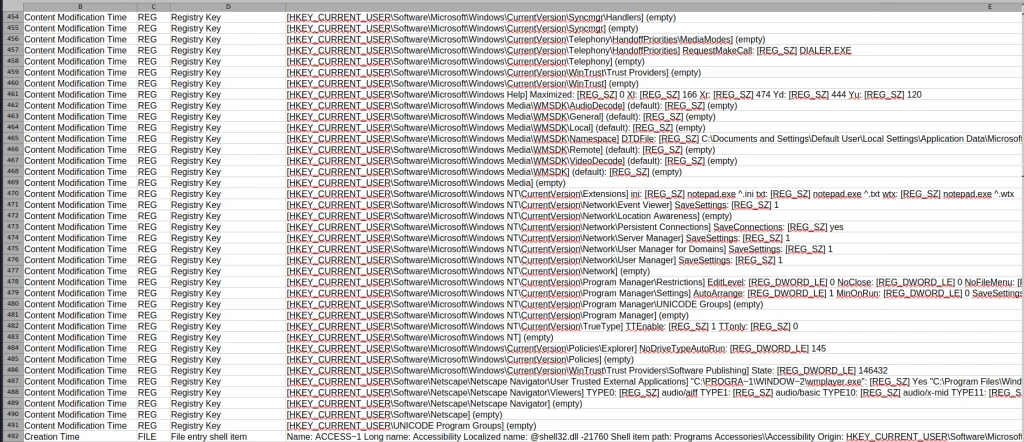
Let’s build a complete timeline of it.
kali > plaso-log2timeline --storage-file ntuser_timeline.plaso ~/plaso/test_data/NTUSER.DAT
This command points log2timeline straight at the NTUSER.DAT hive and tells it to write everything it finds into ntuser_timeline.plaso. That storage file is not something you can just open and read, it’s the raw extracted events that you will need to sort and export into something readable in the next step.
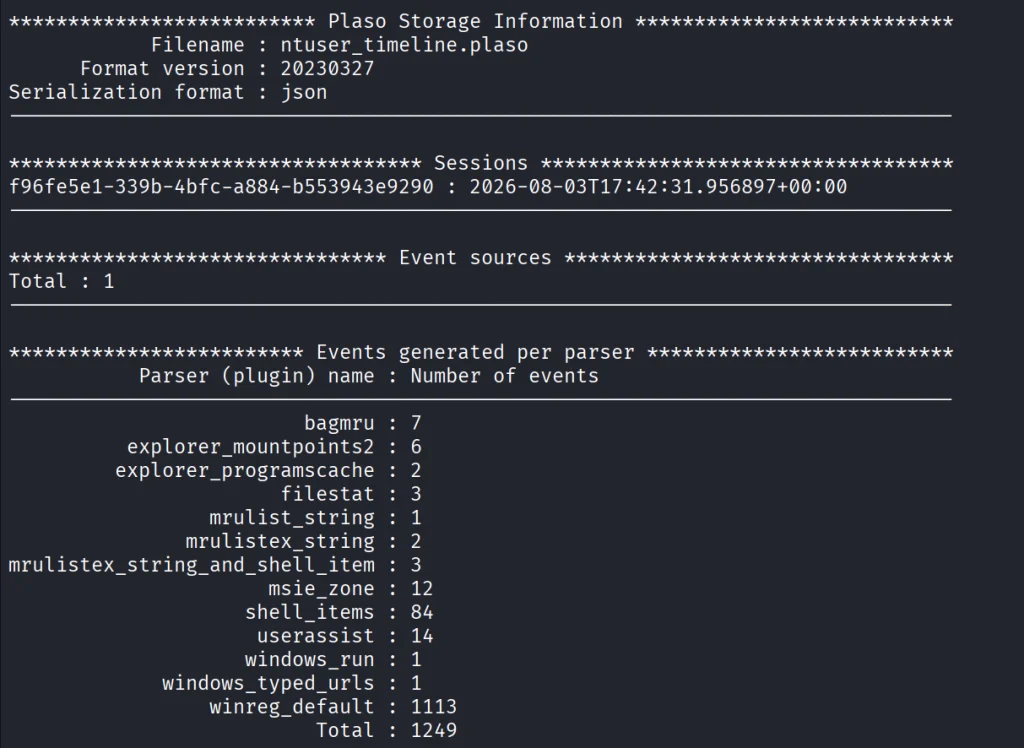
After that, we can view the number of events in this hive.
kali > plaso-pinfo ntuser_timeline.plaso
Finally, let’s take a look at them all.
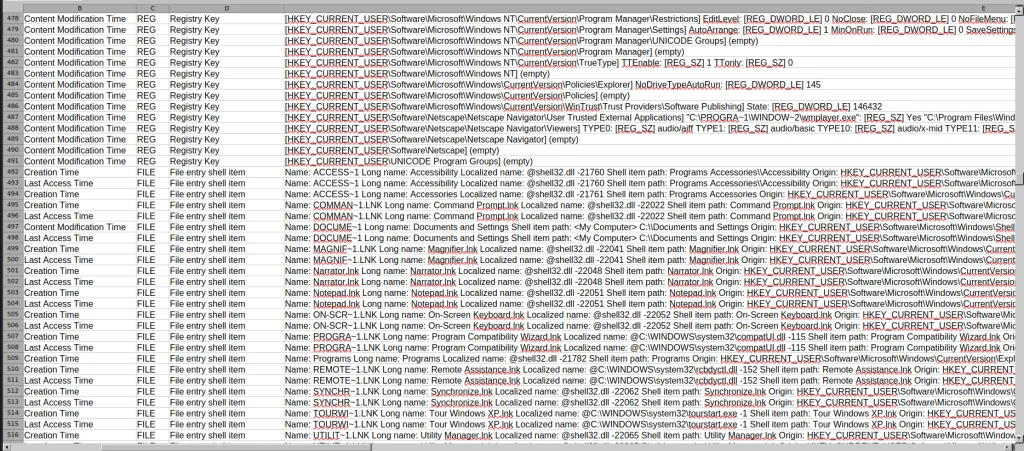
kali > plaso-psort -o dynamic -w ntuser_timeline.csv ntuser_timeline.plaso

kali > open ntuser_timeline.csv
You’ll get a taste of it once we analyze the entire system like that. That way, nothing can escape your view.
Windows Event Log
Another good example is the Event Log. Let’s analyze the System.evtx file and see what’s inside.
kali > plaso-log2timeline --storage-file evtx_timeline.plaso test_data/System.evtx

kali > plaso-psort -o dynamic -w evtx_timeline.csv evtx_timeline.plaso

kali > open evtx_timeline.csv
When you are dealing with a large number of logs, it’s better to slice them.
kali > plaso-psort -o dynamic -w evtx_narrow.csv evtx_timeline.plaso "date > '2026-02-01 00:00:00' AND date < '2026-03-01 00:00:00'"
Syslog
Linux log files are also supported and present in the test data for you to work with.
kali > plaso-log2timeline --storage-file syslog_timeline.plaso test_data/syslog

kali > plaso-psort -o dynamic -w syslog_timeline.csv syslog_timeline.plaso

kali > open syslog_timeline.csv
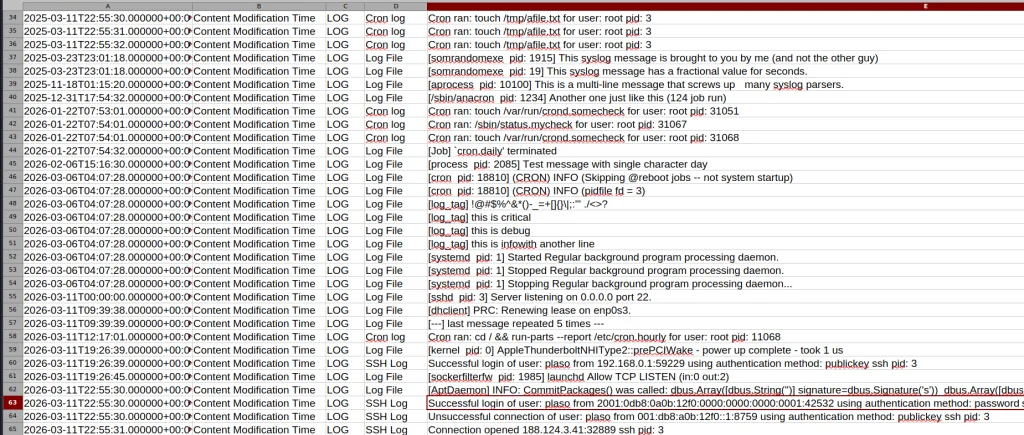
Here is what the syslog file looks like after being parsed. As you can see, all the login attempts and cron job entries are there.
Full System
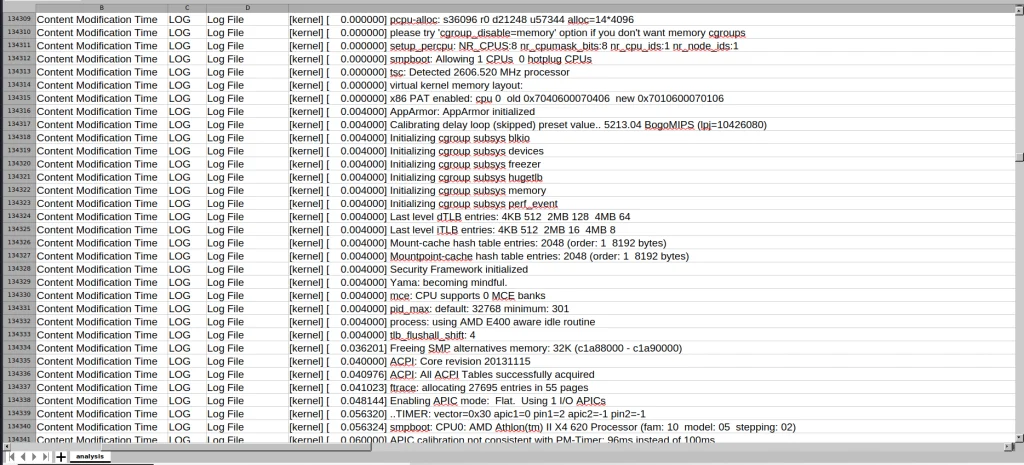
Finally, after pointing the tool to the EnCase files, it will produce a thorough analysis of all the log files available on your system. Below is a complete timeline of the webserver.
kali > plaso-log2timeline --storage-file super_timeline.plaso /mnt/Images/Webserver.E01

kali > plaso-psort -o dynamic -w super_timeline.csv super_timeline.plaso

kali > open super_timeline.csv
Summary
The more tools you are familiar with, the easier the investigation will be. At work, we tend to automate things to save time, but it can also create more confusion when we don’t see the full picture and end up wasting more time puzzling over things that don’t fit together. The tool is worth giving a try, and it does support all kinds of file formats as input, so you can use Plaso yourself or with your AI model.
If you like what we’re doing here and want to get started in forensics or advance your skills, we recommend our training for both beginners and more experienced students.
The article on DeadMatter was really popular and relevant for many of you. DeadMatter works with LSASS and finds artifacts related to active or recently active sessions. But sometimes you need SAM hashes during a pentest.
Today we’re using 7z to find and pull the hives. It’s very common to find and it has raw disk access to fetch what we need without triggering the EDR. You can basically call it a living off the land technique due to its widespread presence. There are other ways to extract hashes, but most of them are well known and monitored. Some hackers rely on VSS and it works fine in some environments, but detecting VSS abuse isn’t hard. It’s a beginner level of complexity. VSS leaves very specific traces in the logs when you use it. Native Windows binaries get blocked outright and finding forensic tools already sitting on an endpoint is uncommon.
Credit where it’s due, Jonas Lyk shared this approach.
Extracting Hives
To make it work, you need to start 7z as Administrator, otherwise it just fails. Then you type \\.\ in the path bar and it’ll show you the drives.
Here we need PhysicalDrive0. You can’t copy it off the C:\ drive, because it’s locked by the system.
Inside you’ll see the partitions on the physical drive. Usually 1.ntfs has the structure of your C:\. 0.ntfs has $MFT, $J and the other files you want for a deeper dive.
System hives live in Windows\System32\config
Select the hives you need and copy them to a folder. We’re only pulling SAM and SYSTEM here, but you can get SOFTWARE, $MFT, $J, and NTUSER.DAT if you’re doing behavioral analysis. We covered that in our article showing how much you can find out about a user after a compromise. Behavioral analysis is also useful in pentesting. NTUSER.DAT shows a lot about how the sysadmins use their machines.
File size shows the hives aren’t empty. Now we can move them to Kali and extract the hashes.
kali > impacket-secretsdump -sam SAM -system SYSTEM LOCAL
We got all the local user hashes. If LAPS isn’t enabled (in a lot of environments it isn’t), there’s a good chance the admin hash is identical across many machines. Some admins don’t even know LAPS exists, others are scared to turn it on because they’re not in control of the password rotation. Either way, SAM alone can be enough to compromise the whole domain.
Terminal
This approach hits a wall in the terminal. 7z can only parse physical disks and NTFS partitions through the File Manager GUI. The CLI version still can’t open nested partitions and throws an error every time. So the GUI is the only way you can pull it off.
There are forensics tools that do it in the terminal (AxiomSecret, RawCopy, etc.) but that’s a story for another day.
Summary
Many successful attacks use LOL techniques or signed tools. This approach is creative and 7z is already sitting on plenty of machines. Even if it’s not, bringing it over isn’t suspicious.
It won’t get you LSASS hashes, but the SAM hashes alone can be enough to compromise a company’s entire infrastructure. We showed that in our SCADA article, where the SCADA machine stored cleartext passwords in memory and password reuse helped us with the rest of the infrastructure during the pentest. LAPS isn’t hard to set up and it can close this door, so spend some time learning it.
If you like what we’re doing here and want to get started in Digital Forensics or advance your skills, we recommend our training for both beginners and more experienced students.
During pentests, we often run into EDRs and antiviruses protecting endpoints. These mainly stop you from dumping hashes and running malware on the hosts. Although they’re often good at what they do, they still have flaws that make them vulnerable to chokers and killers that can terminate their process.
If you’ve ever tried dumping LSASS or extracting SAM and SYSTEM hives, you’ve seen the EDR block your attempts. There are legit ways to do it, for instance with reg.exe or Task Manager, but these have been abused for so long that they can’t be relied on anymore. Despite all that, dumping hashes is really easy if you do a complete memory dump with forensics tools and pull the hashes from the dump. These tools don’t just target LSASS, they do a full memory dump that includes everything. That’s what’s supposed to happen during incident response procedures, so nothing gets flagged and it won’t, because that would interfere with security work.
Today we want to show you how to use FTK Imager with DeadMatter to extract different credentials. FTK Imager needs a GUI, so if you don’t have it try running DumpIt from CLI instead. It’s available on GitHub.
What is DeadMatter
DeadMatter is written in C# and its whole job is to extract sensitive information from memory dumps. It scans raw data to find patterns associated with credentials, that way you can recover them even when the memory dump is incomplete or the format isn’t predictable. The tool is also lightweight and isn’t flagged by AV/EDR, so you can extract hashes on the victim machine directly without transferring these huge files around. The results include NTLM hashes, DPAPI keys, and other artifacts tied to logon sessions. The tool was first presented at Black Hat USA 2025.
Compiling DeadMatter
The repository for DeadMatter doesn’t include a precompiled binary and you will need to build it yourself. You can do it with Visual Studio or using the .NET Framework.
If you choose to compile it manually, you can clone the repository and execute the build process from PowerShell.
PS > dotnet build -c release
Once it completes, Deadmatter.exe will be in the bin\Release directory. The build process usually completes without issues, if you have the required .NET components installed correctly.
If you prefer not to compile the tool yourself or run into problems during the process, you can use our compiled version to save time. We uploaded the compiled executable to our GitHub.
Capturing RAM
Before moving forward, it is important to understand that this technique relies on the ability to extract credentials from memory, which is significantly affected by the state of Credential Guard. If Credential Guard is enabled, credentials are isolated and you won’t be able to access them.
But in many environments with Windows 10 Pro or Windows Server versions prior to 2025, Credential Guard is often disabled. These systems are still widely used across corporate infrastructures. Newer deployments usually have it enabled by default now. To avoid unnecessary effort you can check the status of Credential Guard before proceeding.
If it shows that it’s disabled {0}, you can proceed with memory acquisition.
We used FTK Imager to capture RAM. You just need open the app and click “Capture Memory”
Then you specify the name and the destination path. The default settings are enough.
Our next step is exfiltration. Modern systems often have large amounts of RAM. Servers commonly have 16-32GB as a baseline, and systems that have Microsoft Exchange may have significantly more. A raw memory dump of this size can be quite large, but you can compress it with 7z. It’s possible to reduce it from 32GB down to 12 GB, if you don’t want to run DeadMatter directly on the compromised system.
Extracting Credentials
Once the dump is transferred, you can extract creds. To process a full memory dump in raw format using structured parsing and carving, run this:
PS > .\Deadmatter.exe -f memory_dump.raw
The output is quite detailed. As you scroll through the results, you will find different credentials associated with active or recently active sessions on the system.
If you want to rely purely on carving methods, you can ignore structured parsing and search the raw data directly:
PS > .\Deadmatter.exe -f memory_dump.raw -m carve
When you work with a minidump file and want to use a specific parsing method, you can define the technique and the Windows version:
There are also more advanced options available. For instance, you can extract both credentials and DPAPI keys with additional brute-forcing to find initialization vectors within the data:
PS > .\Deadmatter.exe -f memory_dump.raw -b -d
Try different methods and see if you can find more information.
Defense
To protect yourself from these attacks, make sure Credential Guard is on. It’ll make the credentials inaccessible. It’s also a good idea to monitor which forensic tools are being used. Ideally, keep a whitelist of approved tools that way you can spot someone trying to do a dump without authorization.
Summary
While defenders should have a red team mindset, hackers should have a blue team mindset to know how things work on the other side. Digital forensics is a great field and applies to both sides. Extracting credentials from systems is just one of its uses, more advanced knowledge can help you with behavior analysis and evasion.
If you want to learn more about Digital Forensics, we have training for beginners and for those who want to advance their skills in it.

 Login