❌

Reading view

There are new articles available, click to refresh the page.

Alleged Wagyu Leak Contains 4,580 Completed Crypto Swaps Linking Monero Wallets to IP Addresses

An alleged leak from cryptocurrency swap service Wagyu.xyz contains 4,580 completed cross-chain swaps linking incoming transaction hashes, Monero receiving addresses, and client IP addresses. The dataset reportedly includes 38,628 order records from July 18–October 26, 2026, plus an activity index covering 10,139 distinct IP addresses. Hudson Rock has not independently authenticated the files’ alleged breach […]

The post Alleged Wagyu Leak Contains 4,580 Completed Crypto Swaps Linking Monero Wallets to IP Addresses appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
11 User & Entity Behavior Analytics (UEBA) Tools: The 2026 Buyer’s Verdict Guide

UEBA earns its keep on attacks that look like logins stolen credentials used plausibly, insiders drifting toward exits and fails on unexplainable scores nobody acts on. Roster honesty first: our sheet listed Exabeam and LogRhythm separately, but their merger makes them one company, so this is an eleven-vendor verdict guide spanning SIEM-embedded analytics, standalone timelines, […]

The post 11 User & Entity Behavior Analytics (UEBA) Tools: The 2026 Buyer’s Verdict Guide appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
12 Cyber Threat Intelligence (CTI) Feeds & Services: The 2026 Buyer’s Verdict Guide

CTI services answer different sentences who targets us, what’s leaked about us, which alerts are noise, whose infrastructure is that and no provider owns them all. This verdict guide maps twelve feeds and services to the sentences they answer best, spanning frontline-IR intel, noise-filtering specialists, preemptive infrastructure hunting, underground depth, and the regional players with […]

The post 12 Cyber Threat Intelligence (CTI) Feeds & Services: The 2026 Buyer’s Verdict Guide appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
CISA Adds Actively Exploited VMware ESXi Logging Flaw to KEV Catalog

The Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2026-41709, a vulnerability related to insufficient logging affecting Broadcom VMware ESX, to its Known Exploited Vulnerabilities (KEV) catalog. This decision was made after evidence of exploitation in the wild was discovered. The announcement, made on October 28, 2026, raised the priority of addressing this flaw, despite its […]

The post CISA Adds Actively Exploited VMware ESXi Logging Flaw to KEV Catalog appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
12 Threat Intelligence Platforms (TIP): The 2026 Buyer’s Verdict Guide

A TIP earns its keep in decisions changed per month blocks pushed, hunts launched, patches reprioritized and 2026’s field spans premium all-source graphs, open-source standards, exposure-fused challengers, and infrastructure-truth specialists, with ownership moves (Mastercard’s, Securonix’s) adding mandatory RFP questions. This verdict guide judges twelve platforms on operationalization, not feed counts. Actionable threat intelligence feeds provide […]

The post 12 Threat Intelligence Platforms (TIP): The 2026 Buyer’s Verdict Guide appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Cisco Patches Actively Exploited SSL VPN Vulnerability Affecting ASA and FTD Firewalls

Cisco has released security updates that address a critical vulnerability in the Remote Access SSL VPN service on its Secure Firewall Adaptive Security Appliance (ASA) and Threat Defense (FTD) software. This vulnerability, tracked as CVE-2026-76418, lets unauthenticated attackers trigger unexpected device reloads, causing a denial of service. The flaw is categorized as high severity, with […]

The post Cisco Patches Actively Exploited SSL VPN Vulnerability Affecting ASA and FTD Firewalls appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
12 SOAR Tools: The 2026 Buyer’s Verdict Guide

SOAR’s 2026 question is sustainability: which builder model code, low-code, or no-code will your actual team keep shipping with after the demo glow fades? This verdict guide judges twelve options across the honest lanes: bundled-SIEM automation, enterprise playbook monoliths, the no-code velocity trio, intel-fused orchestrators, and one absorbed lineage flagged where the sheet still lists […]

The post 12 SOAR Tools: The 2026 Buyer’s Verdict Guide appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
12 SIEM Tools: The 2026 Buyer’s Verdict Guide

SIEM purchases fail by buying someone else’s SOC the wrong pricing architecture for your log profile, the wrong engine for your team’s skills and 2026 adds consolidation homework: QRadar’s lanes split, Exabeam carries a merger, Splunk answers to Cisco. This verdict guide judges twelve platforms on pricing-architecture honesty, analyst-loop quality, and estate gravity, spanning the […]

The post 12 SIEM Tools: The 2026 Buyer’s Verdict Guide appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

INJ3CTOR3 Malware Steals FreePBX Credentials to Enable Fraudulent Calls Even After Server Cleanup

INJ3CTOR3 has expanded its FreePBX toll-fraud campaign with automated credential theft, letting attackers keep billing unauthorized calls to victims even after infected servers are cleaned. September 2026 artifacts described in the supplied research show the installer targeting 17 configuration files containing telephony, database, management, and mail-relay secrets. The change separates the attacker’s revenue stream from […]

The post INJ3CTOR3 Malware Steals FreePBX Credentials to Enable Fraudulent Calls Even After Server Cleanup appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

CISA Warns of Active Attacks Exploiting Critical Node2Shell RCE Vulnerability in Node.js

CISA has added CVE-2026-111497, a critical vulnerability in Google Brotli that affects Node.js, to its Known Exploited Vulnerabilities catalog following confirmed evidence of exploitation. Added on October 27, 2026, this flaw allows unauthenticated attackers to corrupt memory, disrupt services, disclose sensitive information, or potentially execute arbitrary code through maliciously crafted compressed streams. Federal agencies have […]

The post CISA Warns of Active Attacks Exploiting Critical Node2Shell RCE Vulnerability in Node.js appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Cloudflare Image Transformation Flaw Allows Hackers to Bypass CSP and Execute Malicious JavaScript

Security researchers have demonstrated an attack chain against Cloudflare’s Image Transformations service that bypasses SVG sanitization and Content Security Policy (CSP), enabling malicious JavaScript execution on a targeted website’s origin. Published on October 28, 2026, the research combines an XML serialization flaw, Chromium cache behavior, and redirects that circumvent image source restrictions. Exploitation depends on […]

The post Cloudflare Image Transformation Flaw Allows Hackers to Bypass CSP and Execute Malicious JavaScript appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Security Researchers Demonstrate Chrome Sandbox Escapes, Telegram Zero-Click Attacks and iOS Zero-Day Research

Security researchers at OffensiveCon Japan 2026 explored topics including Chrome sandbox escapes, zero-click attack surfaces in Telegram, and newly discovered iOS zero-day vulnerabilities. This two-day program took place on October 27–28. The published agenda also covered hypervisor exploitation, Windows privilege escalation, Linux kernel techniques, and AI-assisted security research. However, session titles alone do not indicate […]

The post Security Researchers Demonstrate Chrome Sandbox Escapes, Telegram Zero-Click Attacks and iOS Zero-Day Research appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Hackers Turn Compromised Websites Into Fake Cloudflare Verification Traps for Windows and Mac Users

Attackers are using compromised websites to present fake Cloudflare verification pages that steer Windows and macOS users toward executing malicious commands. The findings establish a delivery attempt, not a confirmed infection or identified malware family. The activity exploits the familiarity of browser security checks. Instead of completing a legitimate verification, visitors receive instructions intended to […]

The post Hackers Turn Compromised Websites Into Fake Cloudflare Verification Traps for Windows and Mac Users appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

WordPress 7.1.4 Security Update Patches 22 Vulnerabilities Affecting Millions of Websites

WordPress has released version 7.1.4 to address 22 vulnerabilities, including issues related to remote code execution, stored cross-site scripting, information disclosure, and authorization weaknesses. This security update was published on October 28, 2026, and it is recommended that users upgrade immediately. The fixes encompass core functionality, including content blocks, administrative screens, the Customizer, and the […]

The post WordPress 7.1.4 Security Update Patches 22 Vulnerabilities Affecting Millions of Websites appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
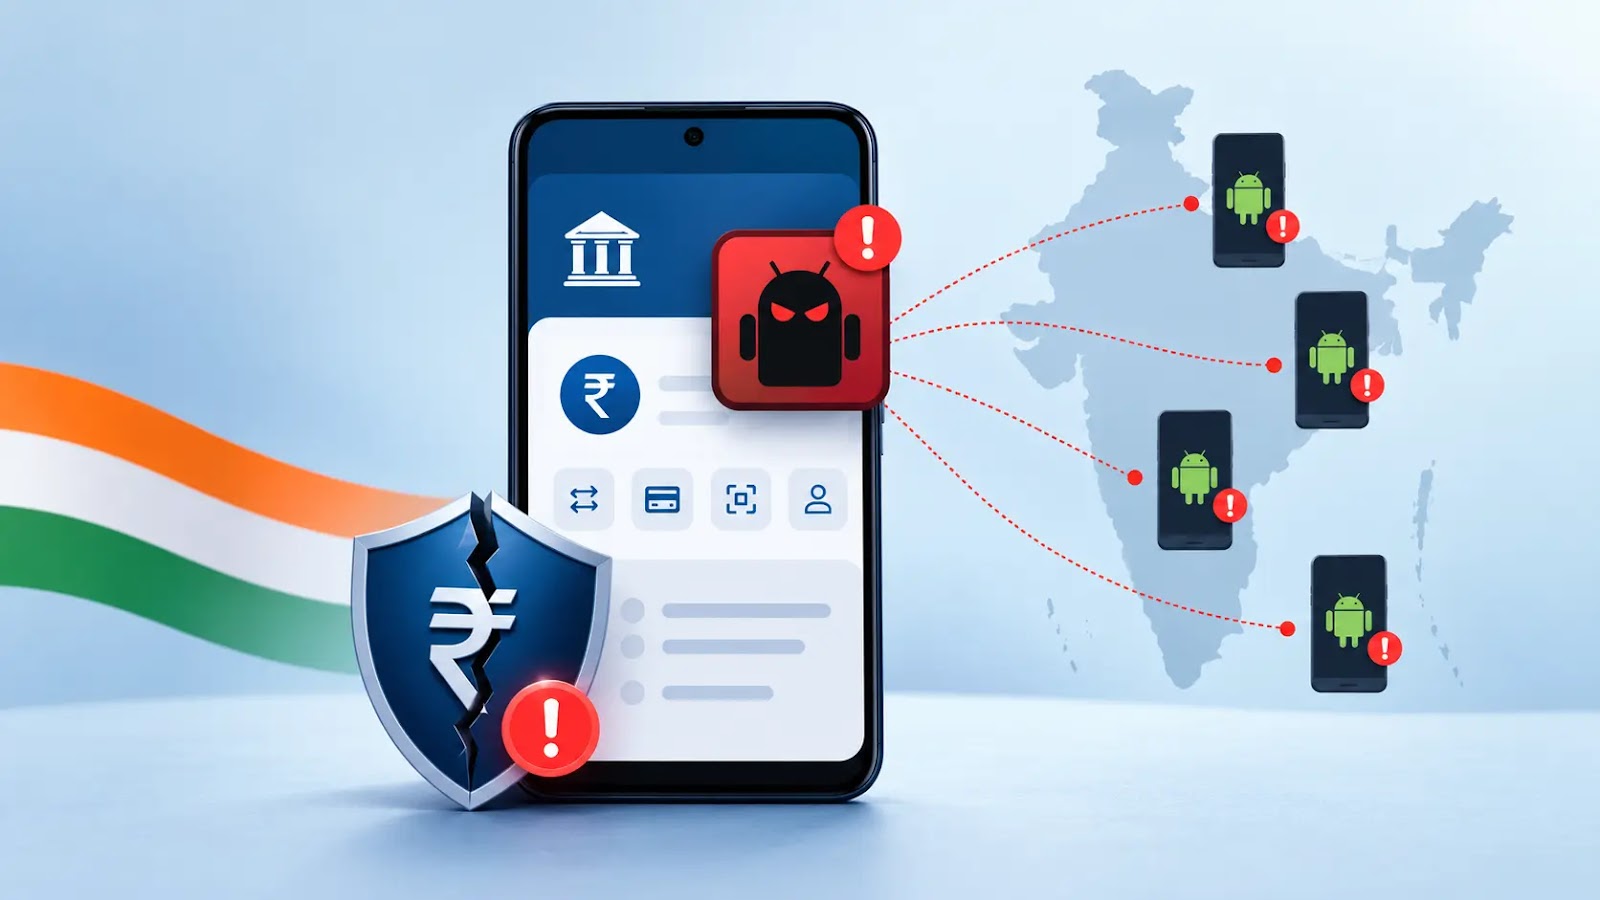
CyberDakait Hackers Target Indian Banking Users, Compromise 17,960 Android Devices

CyberDakait, a financially motivated Android malware operation targeting Indian banking customers since July 2025. Researchers identified at least 17,960 compromised devices and 7,611,443 intercepted SMS messages, exposing a campaign that combines banking credential theft, remote device control, and cryptocurrency mining. Although their technical implementations differ, Group-IB clusters them together because of overlapping distribution methods, phishing […]

The post CyberDakait Hackers Target Indian Banking Users, Compromise 17,960 Android Devices appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
US Homeland Security Data Breach Exposes Personal Details of Over 41,000 Employees

A newly disclosed data leak has exposed personal and professional information on more than 40,000 U.S. Department of Homeland Security employees, including personnel in surveillance, human intelligence, and undercover operations. Distributed Denial of Secrets announced the publication on October 28. It attributed the information to an entity calling itself “Department of Peace.” The reported exposure […]

The post US Homeland Security Data Breach Exposes Personal Details of Over 41,000 Employees appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Exploit PHP2Shell Vulnerabilities to Gain Root Access on 25 Firewall Servers

Hackers chained PHP2Shell vulnerabilities with a Linux kernel privilege escalation flaw to gain root access on 25 servers, including three systems associated with a United States government-affiliated environment, according to Dream researchers. Discovered on October 25, the operation progressed from exposed firewall management interfaces to credential theft, persistent tunneling, and Active Directory reconnaissance. Dream recovered […]

The post Hackers Exploit PHP2Shell Vulnerabilities to Gain Root Access on 25 Firewall Servers appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Use Fake Phantom, Jupiter, and Bitget Firefox Extensions to Target Cryptocurrency Wallets

Three malicious Firefox extensions impersonating Phantom, Jupiter, and Bitget to steal cryptocurrency wallet recovery phrases and private keys. The campaign combines deceptive branding, bundled credential stealers, and remotely delivered JavaScript, with stolen information routed through infrastructure under bonto[.]io. All three listings were removed before Socket published its findings on October 27, 2026. Phantom’s impersonator advertised […]

The post Hackers Use Fake Phantom, Jupiter, and Bitget Firefox Extensions to Target Cryptocurrency Wallets appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Reuse XWorm Malware Loader Across Phishing Campaigns Targeting Colombia and the UK

A judicial-themed phishing campaign targeting Colombian organizations that delivers XWorm through obfuscated scripts, encrypted PowerShell, and a reusable .NET loader. The recovered loader is binary-identical to one documented in a September 10, 2026, UK-linked case, connecting otherwise differently packaged delivery chains. The overlap establishes loader reuse, not common attribution. Different payload hashes, execution targets, and […]

The post Hackers Reuse XWorm Malware Loader Across Phishing Campaigns Targeting Colombia and the UK appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Anthropic’s Claude Chains One-Click and Zero-Click Exploits to Bypass Chrome, Android and Linux Security

Anthropic announced that an unreleased research model called Claude successfully developed working exploit chains for Chrome, Safari, Android, Windows, and Linux. The company’s Frontier Red Team shared these findings on October 27, 2026. Many exploit chains required minimal or no user interaction, and the team reported every identified flaw to the respective vendor before publication. […]

The post Anthropic’s Claude Chains One-Click and Zero-Click Exploits to Bypass Chrome, Android and Linux Security appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
❌