
 Login

Digital Forensics: iOS Forensics – Basics
Welcome back, aspiring investigators!
Today we’re going to cover the basics of iOS forensics and find out what makes these devices vulnerable. We will see what a phone actually holds in different states. Modern iPhones encrypt almost everything file by file, and the keys live inside a separate chip called the Secure Enclave, not the disk itself. So the question is which keys are unlocked right now and how long you’ve got before that changes.
What’s On the Phone
Apple does not encrypt “the disk” as one volume key. Each file is assigned a class when it is created. The class decides when that file can be decrypted.
Class A files only decrypt while the phone is unlocked and lock again fast once the screen goes dark. Mail bodies live here.
Class B can be written while locked but only read if it was already open.
Class C is the one you care about most. It unlocks the first time the passcode is entered after a reboot and stays unlocked even after the screen locks again. App data, chats and photo libraries sit here.
Class D never needs a passcode at all, wrapped with a device only key.
BFU and AFU
Before First Unlock (BFU) means the phone rebooted and nobody’s entered the passcode since. The Secure Enclave hasn’t released the keys yet, Face ID and Touch ID are dead and almost nothing decrypts. What you get from a BFU phone is triage at best. Device info, iOS version, maybe a thin slice of metadata.
After First Unlock (AFU) means the passcode has been entered at least once since the last reboot. Class C data is live and stays live even after the screen locks again. This is the state you want. Analysts usually say AFU gets you around 95% of what a full dump would give you, next to almost nothing under BFU.
The 72 Hour Clock
Since iOS 18.1, a phone that sits idle too long reboots itself. No setting turns this off. The window is around 72 hours. A Faraday bag isn’t a place to park evidence for a week anymore. Labs have already had properly isolated AFU phones reboot themselves back into BFU just from sitting in storage.
How You Actually Pull Data
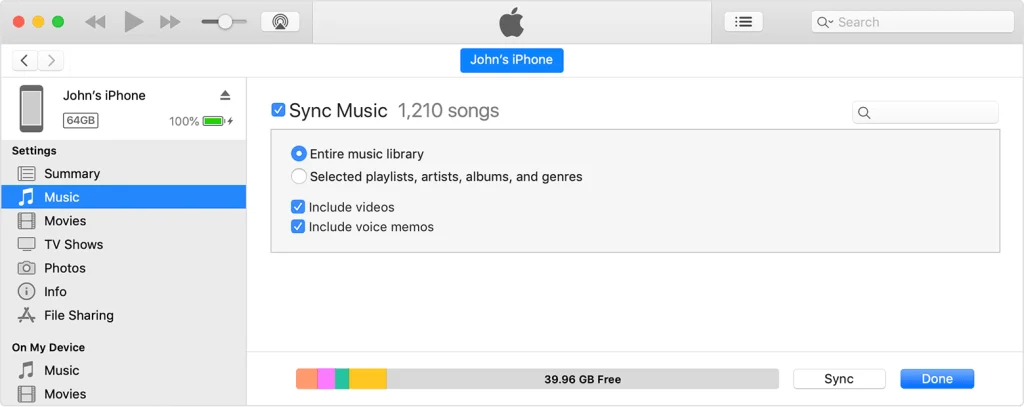
The simplest is a standard logical backup through iTunes or Finder. An unencrypted backup is a partial picture at best, since Keychain and Health data only come along encrypted. One step up is advanced logic, which adds access to the camera roll, books and other shared media a plain backup skips.
Full file system extraction is usually done through a signed agent while the phone’s still AFU. This gets you app sandboxes, full SQLite databases with their WAL and SHM files and the behavioral stores a backup never touches. Agent support for new chips lags behind hardware releases and current A19 and M5 chips with Memory Integrity Enforcement are already a wall some agent chains can’t get past.
Older phones, iPhone X and earlier, can sometimes be opened with bootrom exploits like checkm8, which run below the OS entirely and can work even in BFU. That doesn’t apply to anything shipping today.
iCloud is its own separate source. It can hold things the phone doesn’t and end-to-end encrypted categories still need real credentials or lawful process.
Pairing, USB Locks & Lockdown Mode
A pairing record gets created the moment someone taps Trust This Computer. That record lives on the host machine, and it can let a lab computer talk to a locked AFU phone without another unlock. So every computer the owner used matters just as much as the phone itself.
USB Restricted Mode is separate and much simpler, it’s just a timeout. After roughly an hour locked, the port stops carrying data even though it keeps charging. An old pairing record won’t work once that timer’s up, so every locked phone has a short window.
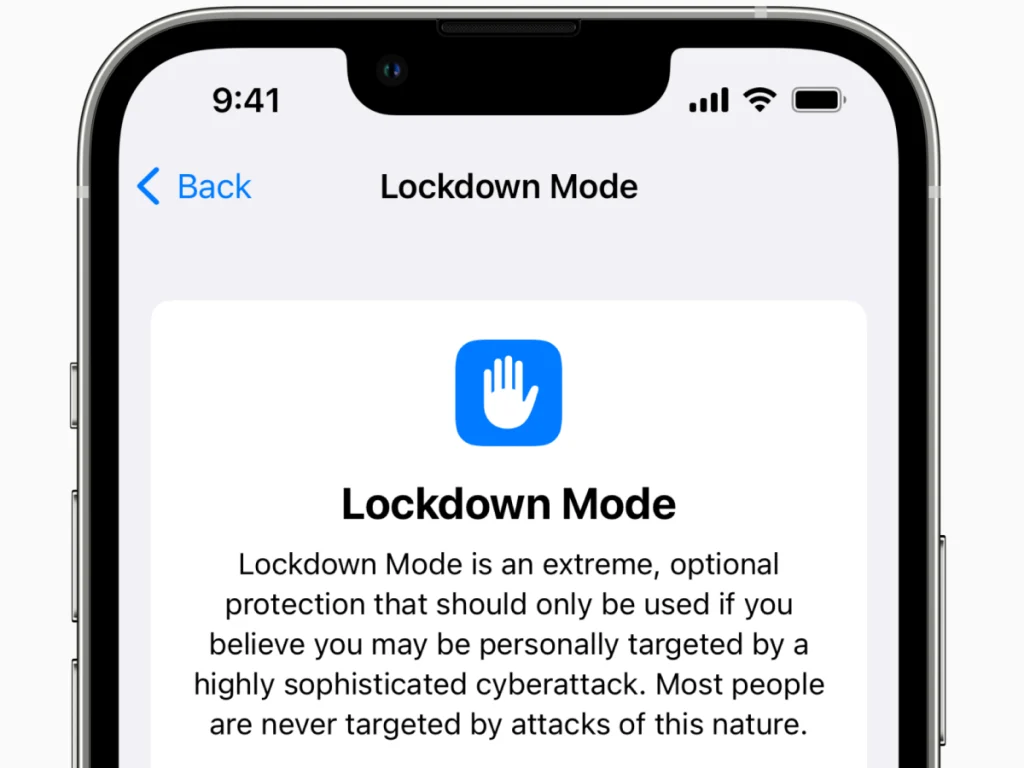
Lockdown Mode is a different thing entirely. It’s a user enabled hardening feature aimed at spyware, and while it’s active, wired accessories need an unlocked phone. That’s the mechanism that reportedly stopped FBI investigators from extracting a seized reporter’s iPhone in early 2026, even though the phone was powered on and charging right in front of them. Turning Lockdown Mode on or off also reboots the phone, so flipping it yourself kills AFU instantly.
Jailbroken Phones
Some devices may be jailbroken. These are softer targets, but they can’t be trustworthy. Jailbreaking modifies the filesystem and tweaks change or hook app behavior. That can overwrite artifacts, add artifacts that aren’t from normal use and give opposing counsel a way to challenge integrity.
Cellebrite
Cellebrite’s old UFED, Premium and Physical Analyzer lineup is mostly folded into one suite now called Inseyets, though Premium and PA7 are both still running too. Their own docs use AFU and BFU just like everyone else, because the same rules apply. AFU with a supported device opens up fully. BFU on current phones mostly doesn’t, no matter which Cellebrite tool you’re running. Support trails Apple by weeks or months after every iOS release, and brute force support stays limited to specific older models on specific iOS ranges, not a blanket “any locked iPhone” claim.
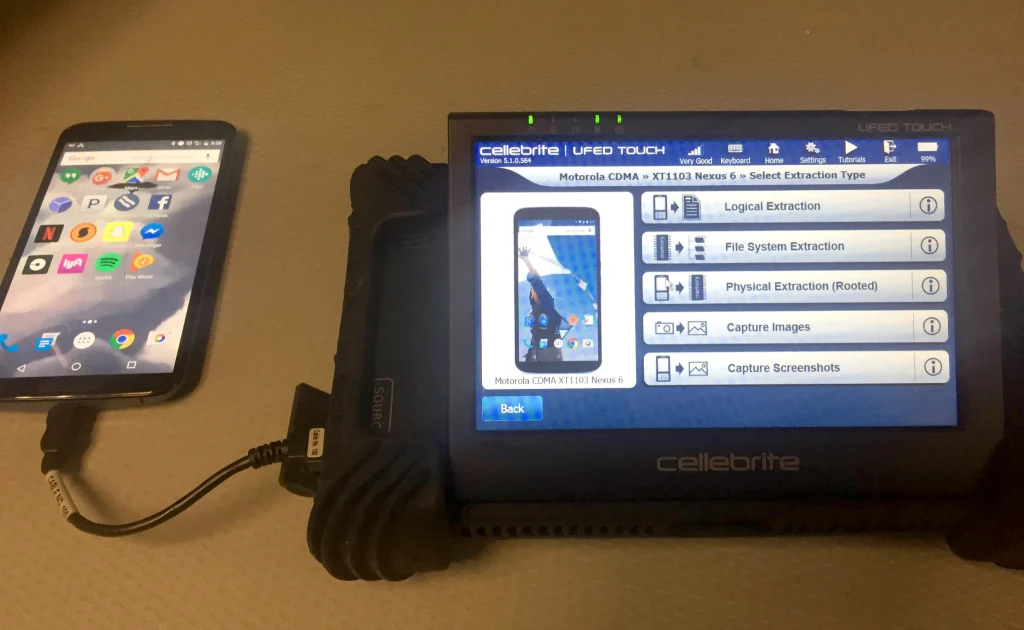
For old hardware, iPhone 5s through X, they lean on the same checkm8 style bootrom exploit covered earlier.
Worth remembering too, in 2021 Signal’s founder found real bugs in the tool itself
What You Actually Dig Through
Chat apps like iMessage, WhatsApp, Signal and Telegram each keep their own SQLite database, and deleted rows often still sit in the freelist or the WAL file until the database gets cleaned up. Always grab the WAL and SHM files alongside the main database, not just the .db file by itself.
The real skill jump in this field is using behavioral stores. KnowledgeC and its newer replacement, Biome, track which app was in focus, unlock events, notifications, even web activity. That’s how you reconstruct what was actually on screen at a given moment. PowerLog backs that up by confirming the phone was genuinely powered on and connected at a given time.
Photos.sqlite covers hidden and recently deleted images along with iCloud sync state. As you can see, deletion on iOS basically means the key gets destroyed and the database gets cleaned up later, there’s no recycle bin sitting in unallocated space waiting for you to carve out. If someone claims they recovered deleted iMessages from raw flash on a modern iPhone, that claim needs real scrutiny.
Summary
Keep your iPhone protected by updating the firmware and upgrading the device itself regularly. Old devices are prone to certain attacks, and as years go by more vulnerabilities get discovered. Analysts are already using these vulnerabilities to bypass protection and extract data from older iPhones. Keeping backups off iCloud adds an extra layer of protection. Don’t connect your iOS device to your computer and don’t accept anything that pops up on the screen afterward. iOS 18 adds some protection by bringing the phone from AFU back to BFU after 72 hours. These recommendations can help if your life is threatened by people who don’t respect the law. If you’re a forensic investigator, use this knowledge to bring justice to the case. Stay safe out there!
The post Digital Forensics: iOS Forensics – Basics first appeared on Hackers Arise.


