Login

FutureBit Apollo Solo Miner Finds Bitcoin Block 973262, Earning 3.154 BTC
Bitcoin Magazine
FutureBit Apollo Solo Miner Finds Bitcoin Block 973262, Earning 3.154 BTC
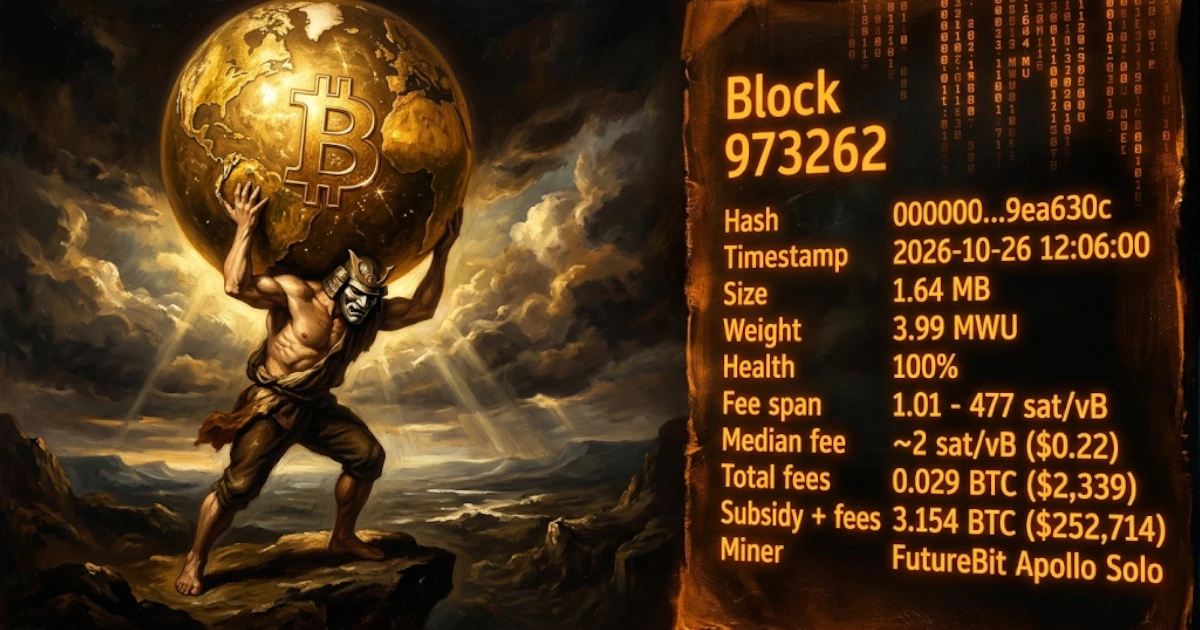
A miner operating through FutureBit’s Apollo Solo setup found Bitcoin block 973,262 earlier this week, collecting the full reward of 3.154 BTC plus fees from 2,477 transactions. Multiple explorers, including mempool.space, list the finder as “FutureBit Apollo Solo,” and the coinbase transaction includes text referencing FutureBit and Apollo.
FutureBit posted about the find on X: “Gradually, then suddenly. We (the people) hit a Bitcoin block today. Bitcoin belongs in the hands of sovereign individuals. And we’re building to keep it there.” The company stated that an Apollo device or Solo Node running its built-in solo pool assembled the block template, served the work, and submitted the completed block to the network. The public record does not identify the exact hardware or hashrate that produced the winning hash. It could have been an Apollo BTC, Apollo II, Apollo III, or other compatible machines pointed at a Solo Node, according to FutureBit’s account of the block.
This marks at least the fourth block attributed to FutureBit Apollo Solo. Earlier ones include blocks 867,760, 881,423, and 888,737. FutureBit designs its Apollo hardware for operators who want to run a full Bitcoin node and mine independently at home rather than through large commercial pools. The most recent model, the Apollo III, is rated for up to 18 TH/s in turbo mode with an integrated full node. Bitcoin Magazine covered the Apollo III launch in February 2026 and previously examined FutureBit’s approach to home mining in a July 2025 piece.
Solo mining, is often called lottery mining because of the low odds relative to the size of the reward, remains uncommon against a network hashrate that has recently sat near 1,070–1,087 EH/s. A home-scale setup in the 10–18 TH/s range still faces expected times to a block measured in centuries under current difficulty, yet verified solo finds continue to appear on-chain. Bitcoin Magazine examined the mathematics of these odds in an article titled Why Bitcoin Lottery Mining Has Better Odds Than The Powerball. It compared continuous Bitcoin block attempts with the much lower frequency of major lottery draws.
Another solo block was found the following day via CKPool Solo, illustrating that individual operators can still capture full rewards even as industrial pools produce the large majority of blocks. For users running FutureBit hardware, the company notes that the individual users control both the node and the solo pool, retaining the full reward when a block is found. Solo mining also has significant privacy benefits, and hardware and energy costs can be written off against taxes in some jurisdictions.
The October 26 block is one more validation that solo mining can be viable. Satoshi Nakamoto’s original Bitcoin design intended the full Bitcoin node to be able to mine blocks, not just validate and audit the blockchain. Improvements in hardware and mining optimizations later on led to the creation of mining pools, which created a very competitive and industrial mining sector. The secondary effects of industrial Bitcoin mining, such as reliable energy demand that can stabilize the grid, have been a boon for states like Texas.
However, the dream of bringing mining back to homes and end users remains alive through companies like FutureBit, Bitaxe, and HeatBit, among others, that are converting heating appliances into Bitcoin miners or designing hardware of the sort for the home.
This post FutureBit Apollo Solo Miner Finds Bitcoin Block 973262, Earning 3.154 BTC first appeared on Bitcoin Magazine and is written by Juan Galt.
 Taiwan detected six Chinese military aircraft, seven People’s Liberation Army Navy ships and one Chinese official ship operating around the island in the 24 hours to 6 a.m. local time on Oct. 29, the Ministry of National Defense said on social media. Five of the six aircraft sorties entered the northern, central and southwestern parts […]