At least 19 wallets linked to prediction market platform Predict.fun have reportedly been drained of approximately 105 ETH, worth $260,000, with investigators tracing the suspected stolen funds through Ethereum to cryptocurrency mixer Tornado Cash. On-chain investigator Naeven reported the suspected…
Hardware wallet manufacturer Keystone has confirmed that hackers stole a device authentication key and exposed personal information belonging to 25,964 customers, forcing the company to destroy 18,835 devices and suspend shipments. According to the company’s October 26 security announcement, attackers…
Government websites in France and Finland and hospital sites in the Netherlands are offline, Cloudflare is seeing attack traffic, and Britain’s National Cyber Security Centre is telling organizations to pull systems if they can’t patch fast. Bitcoin Magazine technical editor Shinobi joins Grace Remington and Sean Hagan to explain what broke in PHP, why memory management mistakes are the most common security flaw, and why AI finding the exploit in hours changes the pace of hacking but not its nature. He also answers the question every Bitcoiner is asking: is Bitcoin exposed?
Chapters: 0:00 The PHP Exploit Takes Government and Hospital Websites Offline 0:54 AI Found the Flaw in Hours: The “Cyber Pandemic” Warning 1:45 What Actually Broke: Memory Management Mistakes Explained 3:06 Why PHP Was Never Secure and Why This One Is Different in Scale 3:47 Is the AI Hacking Story Sensationalized? AI Does 95% of the Work 5:08 The Rough Adjustment Period and Why Shinobi Is Confident About the Other Side 6:41 No Serious Software Will Ship Without an AI Security Audit 7:23 Is Bitcoin Exposed? libsecp256k1, Bitcoin Core and Why Slow Development Was Right 9:30 Take Your Lightning Node Offline and Keep Your Coins in Cold Storage 12:09 Multisig and Sparrow Setup Checks, and Where to Follow Security Engineers
DISCLAIMER: The views and opinions expressed in this show are those of the participants and do not necessarily reflect the official policy or position of BTC Inc., Bitcoin Magazine, or any affiliated entities. This content is provided for informational and educational purposes only and should not be construed as investment, legal, tax, or accounting advice. Nothing contained in this show constitutes a solicitation, recommendation, endorsement, or offer to buy or sell any securities or financial instruments. Viewers should consult their own advisors before making financial or business decisions.
Electrum releases version 4.8.3 after malicious servers exploit a Bitcoin wallet flaw to redirect payments through fake fee bumps, causing confirmed losses.
Initia has halted its layer-1 blockchain and rollups after security researcher Spreek reported unauthorized token minting and approximately $2.6 million cashed out by an attacker. Initia confirmed in its Oct. 23 statement that the suspension took effect at 3:41:30 p.m.…
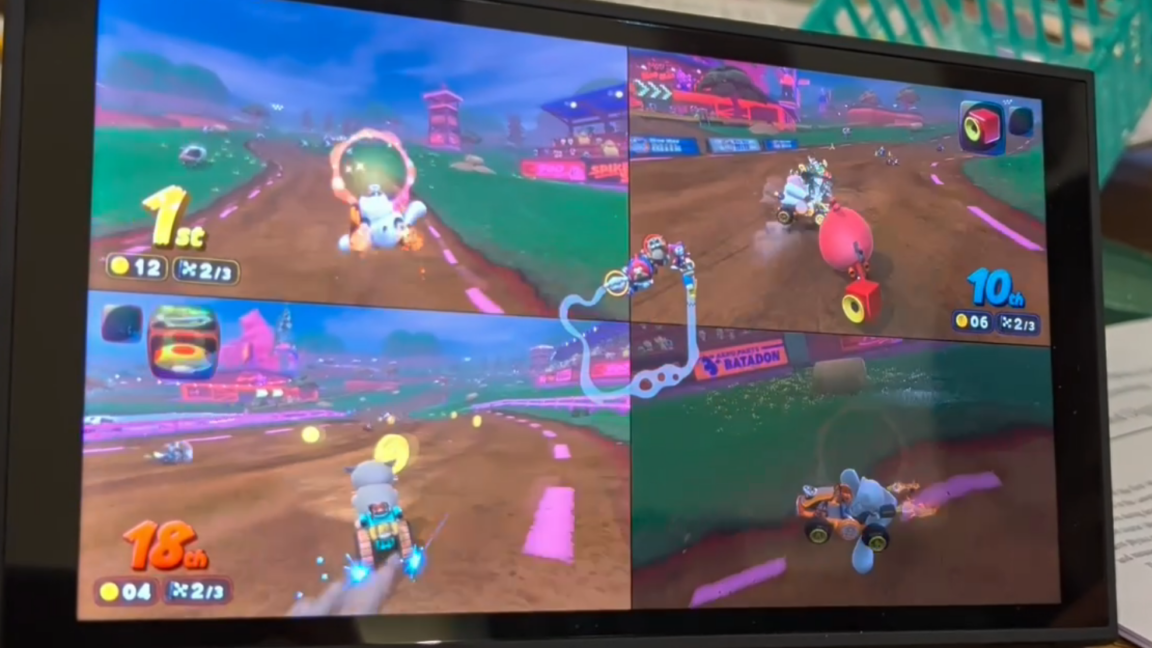
A security researcher has demonstrated a software-only partial jailbreak of the Switch 2, gaining "userland" access that he says "lets us run homebrew, reverse engineer and mod Switch 2 games, back up save files off the Switch, and access most of the Switch 2’s peripherals through MMIO."
The hack relies on the original Switch version of SmileBasic 4, the latest in a long-running series of programming environments and interpreters that run on Nintendo hardware. The so-called "tethered" hack also requires access to a macOS or Linux PC on the same network to run a node.js package that helps enable privileged system access.
Researcher Sammy Hajhamid writes that he used OpenAI's Codex to poke at SmileBasic's language interpreter, using a custom harness that could send USB commands to the system and view results via HDMI (as well as power cycling via a Bluetooth light switch flipping device). After "substantial effort for ~2 weeks," that harness discovered a 32-bit integer overflow that occurs when removing items from an array in SmileBasic. That error gives access to an array pointer, which in turn allows read-and-write access to portions of system memory.
Amazon has warned that vulnerabilities in a programming language that underpins much of the Internet, discovered using AI tools, are being “broadly exploited” as governments and companies rush to secure their systems.
The world’s largest cloud computing provider on Wednesday said it had identified an attempt by hackers to exploit the bug four days before the weakness was disclosed to the public.
Amazon added the flaws were “now being broadly exploited in the wild.”
Unknown hackers hijacked more than 300 Tor exit nodes and reconfigured them to favor unencrypted email traffic and redirect SSH connections through servers they controlled, a researcher reported Tuesday.
The hijacking began in late August, when, according to Tor volunteers, the attacker used a valid password that had been reused to gain access to a Tor management server. The attacker then installed Ebury, a backdoor written for Linux that was discovered 12 years ago.
Mysteries remain
Then the attacker connected from the management server to a second Tor server, called Switzerland2, through SSH, using an RSA key that, for unknown reasons, investigators couldn’t find among Switzerland2’s authorized keys. With administrative control of Switzerland2, the attackers installed Ebury there as well. Finally, the attacker reconfigured settings on two exit nodes that Switzerland2 hosted.
Qubic halted its network after attackers exploited weakly generated wallet credentials to remove roughly $1.4 million in cryptocurrency from more than 1,400 accounts, according to the project’s account of the incident.
TL;DR: The reported loss involved 1,404 wallets and around 2.94 trillion QU. The issue was traced to wallet seed generation rather than a confirmed compromise of the blockchain’s consensus rules.
The distinction matters. Users can lose control of coins even when the underlying network continues to process transactions exactly as designed. If the randomness used to create a private key is predictable, attackers may be able to reconstruct the key and sign transfers that appear valid to everyone else on the chain.
Qubic developers linked the weakness to seed generation in a web-wallet environment, with reports pointing to the use of JavaScript’s Math.random function. That function was never intended to supply cryptographically secure entropy for protecting money. Strong randomness, obtained from appropriate operating-system cryptographic interfaces, is essential when generating wallet secrets.
The project responded with an emergency network halt while investigators and validators worked through containment options. Pausing a decentralized system can reduce immediate movement of funds, but it also prevents normal users from transacting and raises difficult questions about authority and any possible rollback.
People holding QU should rely on official security instructions before importing or moving affected wallet credentials. Generating a fresh address using a patched wallet is not the same as safely recovering funds already transferred away.
The incident is a reminder that wallet security begins before a transaction is broadcast. A flawless ledger cannot compensate for a secret key that was never truly secret.
Written by the News Desk and edited by Samuel Rae.
$1.2 million was paid out at Pwn2Own Ireland 2026 for exploits targeting phones, printers, smart speakers, smart home hubs, and AI infrastructure and coding tools.
Widespread Infrastructure Breaches and Novel AI Threats Several significant security breaches and new exploitation patterns are highlighted in the Check Point Research threat bulletin, which was released on August 24,...
The Vulnerability Apple fixed a major security vulnerability in their image handling framework for both desktop and mobile devices on August 18, 2026. The vulnerability, which is tracked as CVE-2026-65346,...
Critical Flaw Disclosed in Building Automation System A serious vulnerability in Johnson Controls’ Metasys building automation technology was reported in an industrial security alert (ICSA-26-225-14) released by CISA on August...
Incident Overview On July 27, 2026, the Cloud Security Alliance (CSA) released its initial post-mortem detailing the first publicly documented end-to-end autonomous AI cyberattack that was titled “Hugging Face”. The...
Overview of the Advisory On July 23, 2026, CISA, the NSA, the FBI, and their international partners issued a joint cybersecurity advisory alerting organizations to ongoing Russian state-sponsored activity. The...
Escalating Threats to Critical Infrastructure On July 22, 2026, federal agencies led by the FBI, CISA, and NSA released an updated joint alert warning that cyberattackers with ties to Iran...
How HollowGraph Operates On July 20, 2026, Group-IB security researchers released a study describing an implant known as HollowGraph that converts a hacked Microsoft 365 calendar into hidden communication channel....
Record-Breaking Fixes Tackle Two Exploited Zero-Days On July 14, 2026, Microsoft dropped a record-shattering Patch Tuesday update that delivered 622 security fixes in a single day. This unprecedented volume, which...
A newly disclosed use-after-free in the Linux kernel's epoll code, CVE-2026-46242, lets an unprivileged user get root on affected Linux and Android systems. A fix is out, but it took two attempts.

 Login