❌

Reading view

There are new articles available, click to refresh the page.

SDR (Signals Intelligence) for Hackers: Scanning Wireless Devices Using FieldWatch

Welcome back, aspiring cyberwarriors!

As you know, there are thousands of Bluetooth and WiFi signals we pass through daily, especially if we live an active life in a big city. That includes tags, smartphones, WiFi routers, drones, surveillance devices, vehicles, body cams and mesh radios. Clearly it doesn’t stop here and the list goes on.

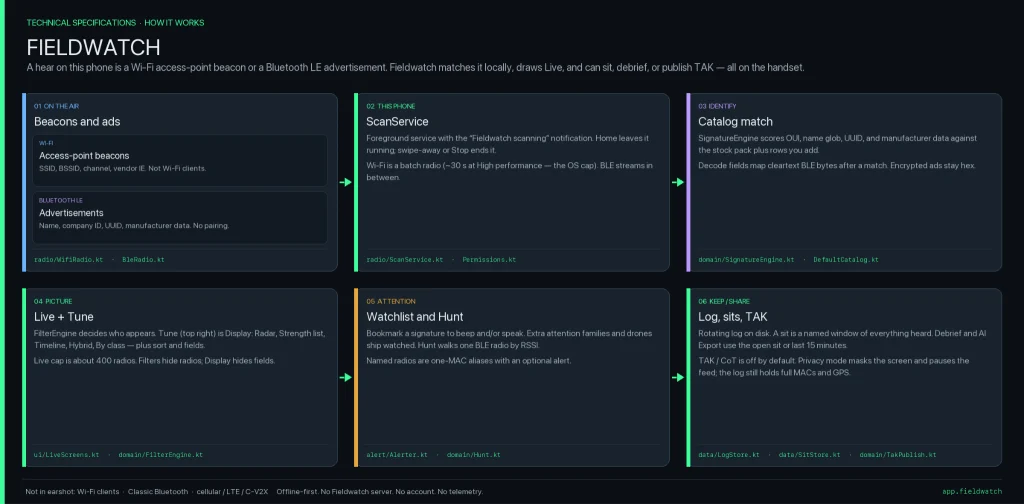
Many of you are privacy focused individuals and want to know what’s going on around you and whether you’re being tracked or watched by someone. That’s okay, protecting your privacy is a good thing. FieldWatch was made for this. It matches what it hears against an editable signature catalog of roughly 250 device types and shows the results in live views, recorded sessions, path maps and reports. Everything runs on the device and works fully offline.
FieldWatch

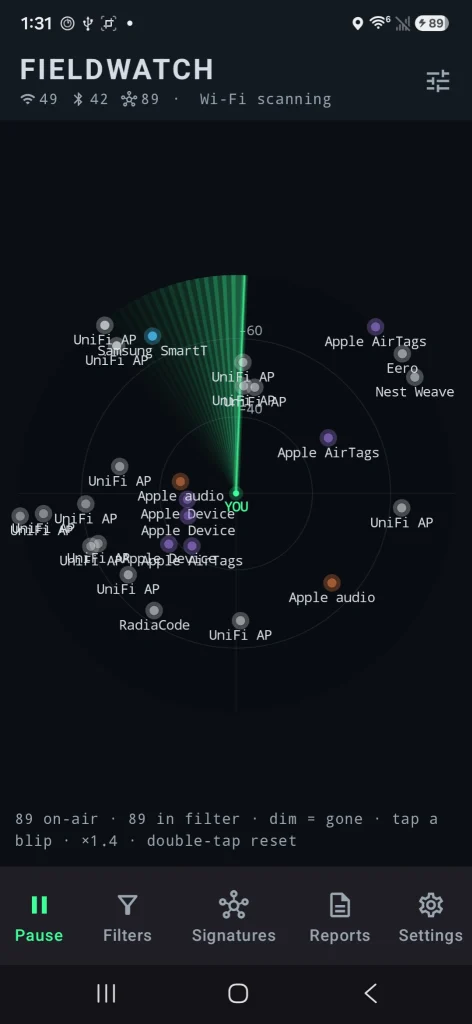
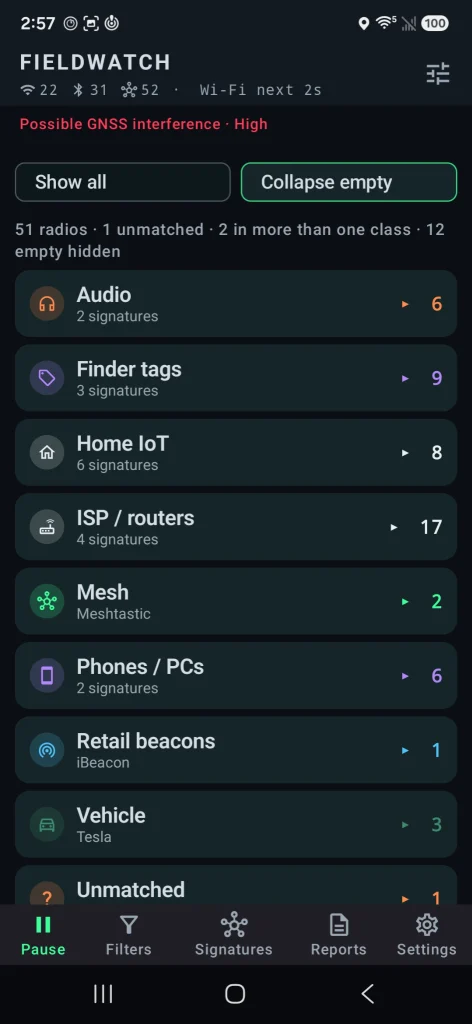
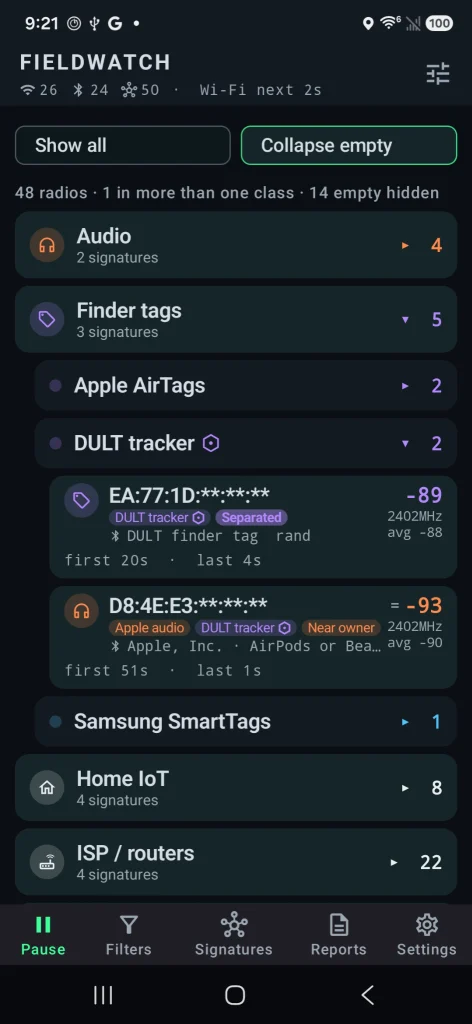
FieldWatch is a free, open-source Android app that listens to nearby Wi-Fi and Bluetooth signals using the radios already in your phone. It compares what it hears against a list of known device signatures and shows them. It only receives signals. It never transmits.Β 

Source: OGridPete
Source: OGridPete

You can set alerts for specific devices, record what’s present during a walk or drive, and later compare sessions. All the findings are sorted under their category. It also has basic GNSS interference detection and can send results to mapping tools like TAK. Matches are based on patterns, not guaranteed identifications, and the app only sees what the phone’s radios and Android allow it to see.

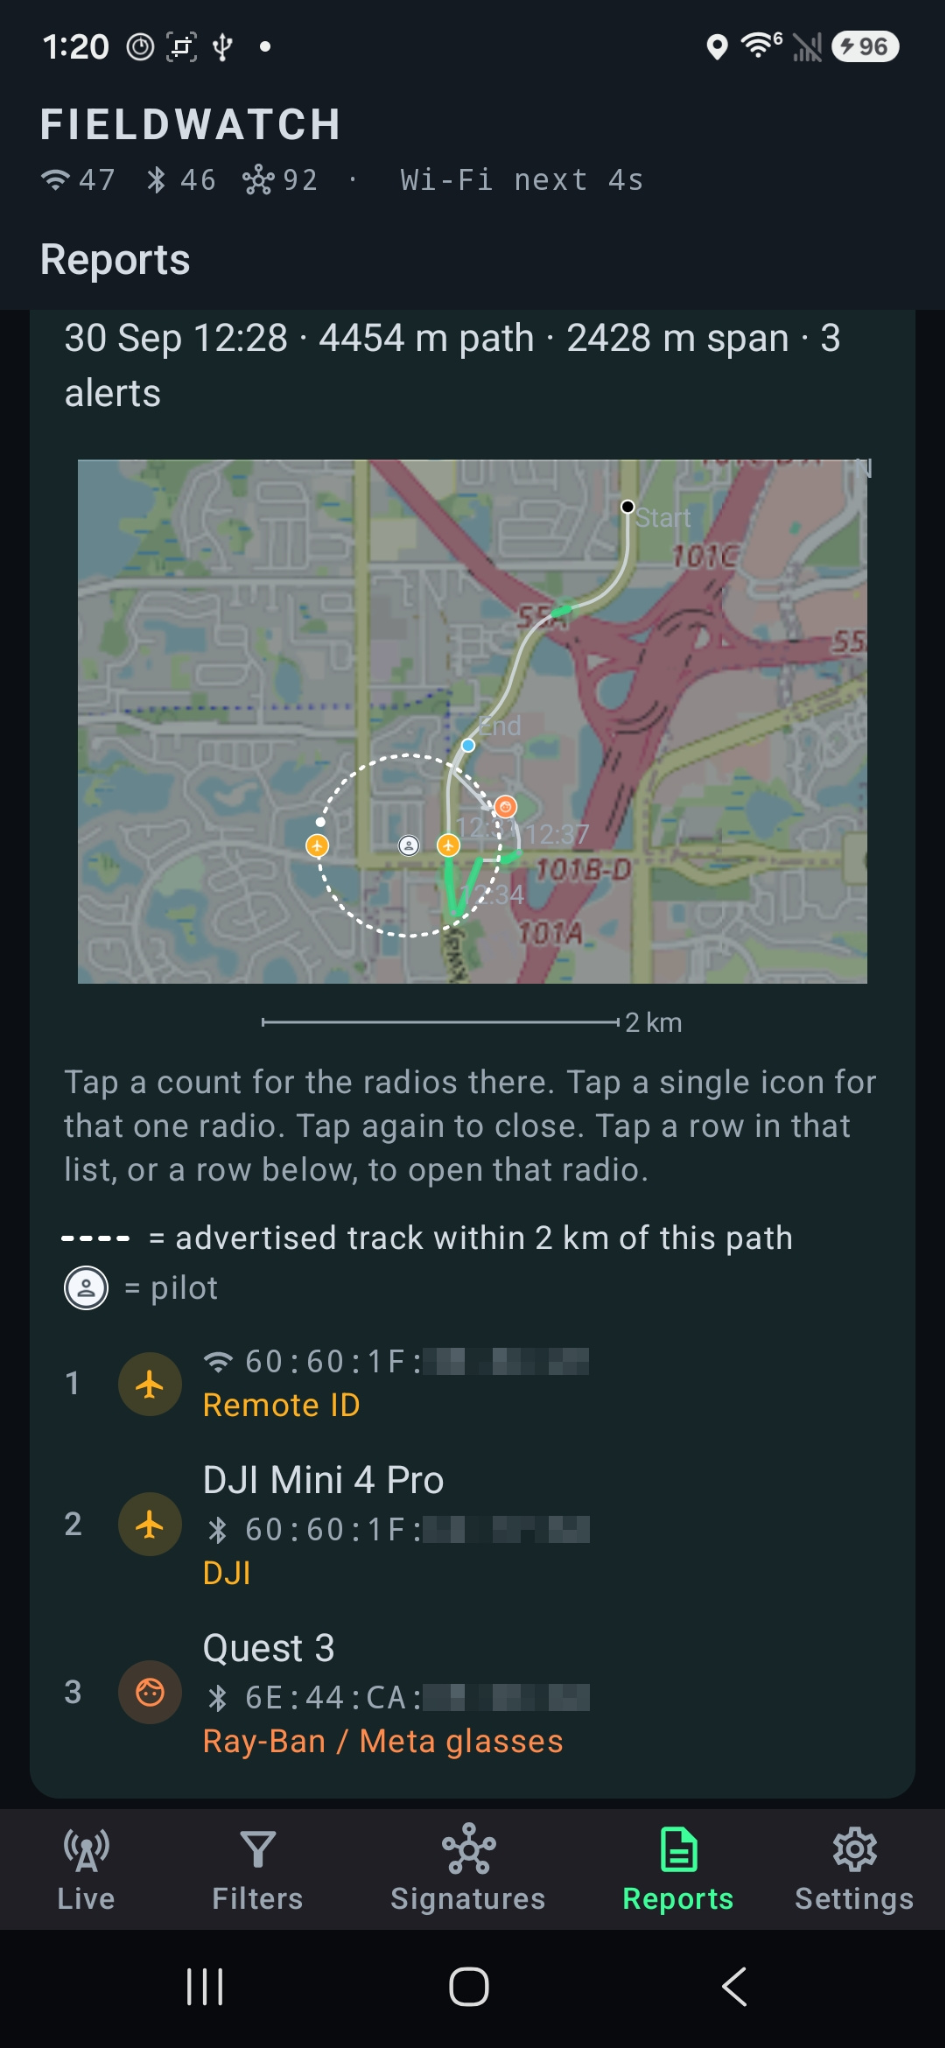
Depending on your preferences, you may want to see these devices on a radar or on a map. The app found the location of the drone operator as well as the drone itself.
Source: OGridPete
Source: OGridPete

TAK Support

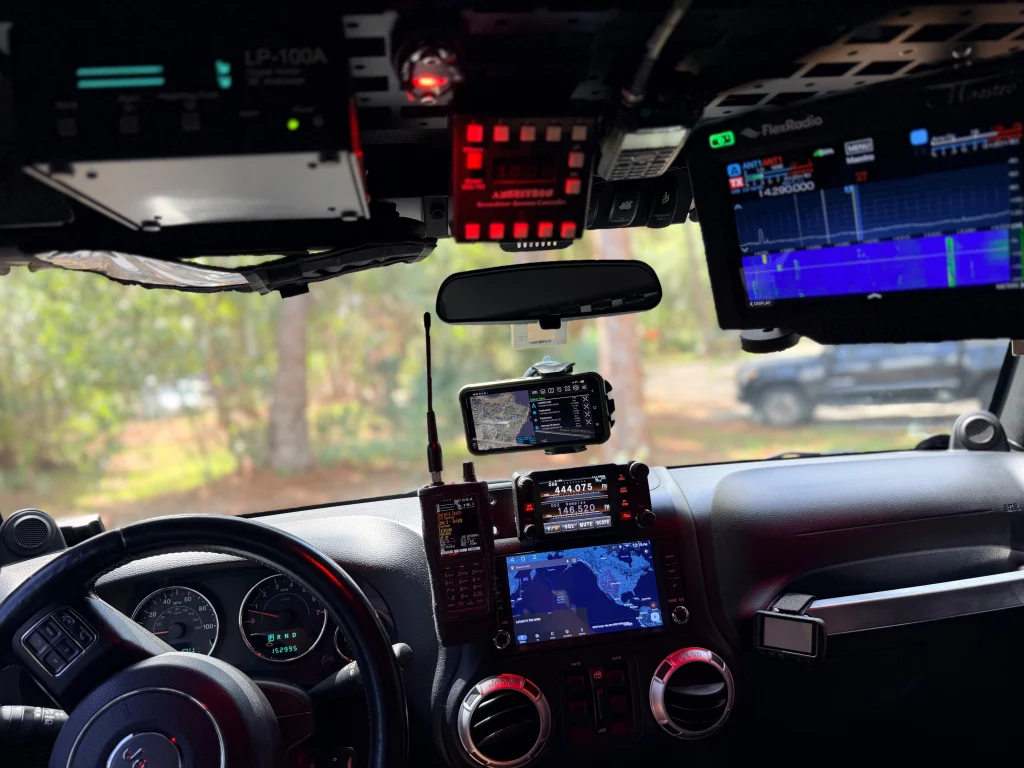
TAK and ATAK are free mapping apps used by military, emergency responders and some civilians to share locations and information on a map in real time. FieldWatch can send what it detects straight to TAK over the local network.

When FieldWatch sees a drone that’s broadcasting Remote ID, it can place a moving marker on the TAK map for the drone and a second marker for the pilot if that location is available. Other devices it finds, plus any GNSS interference alerts, can also appear as markers. Several phones running FieldWatch can send data to the same map at the same time, so a team sees the same picture.
Source: OGridPete

GNSS Interference Detection

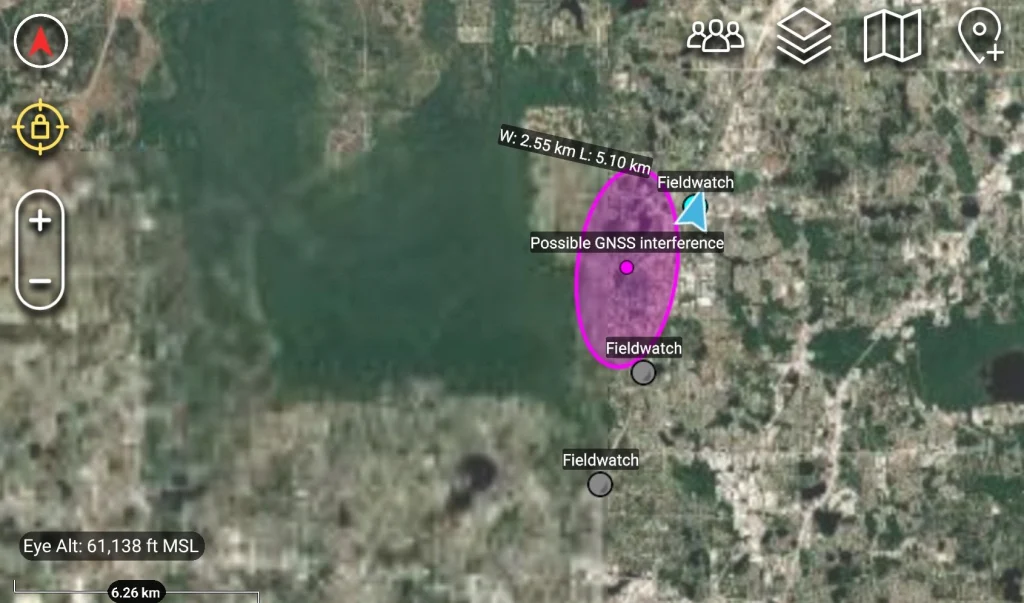
Newer versions check for signs of GPS interference or spoofing using the phone’s own receiver. After a short outdoor calibration, it can alert you and mark the spot on your path or on a TAK map. It shows where you were, not where the interference came from.
Source: OGridPete

Limits

Now let’s talk about its limits. It isn’t a direction finder. Also, it doesn’t scan Bluetooth Classic, cellular networks or full Wi-Fi traffic. Matches are based on patterns and those are not confirmed identities. Your results depend on the phone and what Android lets the app see. For better results use newer phones. Official versions only come from the GitHub repo.

Android App

Download the APK from the official GitHub page and sideload it. Android 10 or newer is required. Android 11 has more functions that can be used with this app. A short instruction file and manual are included. The repository has all the answers in terms of the app. It works on a cheap phone with no SIM card. OffGridPete recently posted that he used a Moto G for $30 for his test and it worked well. If you decide to use it, use it for your own privacy and security, and be respectful of other people’s privacy.

Summary

You can use your cheap phone as a scanner for devices nearby, and find jamming and tracking. There are different apps that do similar things, but they’re bound to Linux only, which is very inconvenient. FieldWatch works on an Android phone to find trackers, cameras, drones, body cams and more.

If you enjoy experimenting with frequencies and trying new things, we recommend signing up for our SDR for Hackers training. With Master OTW, you’ll learn how to use your computer and inexpensive SDR hardware to explore and hack a wide range of radio signals.

The post SDR (Signals Intelligence) for Hackers: Scanning Wireless Devices Using FieldWatch first appeared on Hackers Arise.

Bluetooth Hacking and Security: The WhisperPair Exploit and Bluehood Surveillance

Welcome back, aspiring cyberwarriors!

Bluetooth is often seen as something short range and therefore harmless. Many people think that because it only works over a limited distance, it must also be secure by design. But that’s not true. Bluetooth is convenient, but convenience often comes at the cost of security and privacy. A big number of vulnerabilities show that Bluetooth devices can expose much more information than many realize. At a technical level, they constantly announce their presence to the surrounding environment. Even when you are not actively using them, they still send small pieces of data. Over time these pieces form patterns that show detailed information about people’s lives.

Hackers can take control of devices, pair with them without permission and even use them as remote listening tools. In other cases, simply listening is enough.Β 

WhisperPair Vulnerability

In January 2026, researchers from KU Leuven disclosed a critical Bluetooth vulnerability known as WhisperPair (CVE-2025-36911). This vulnerability affects hundreds of millions of Bluetooth audio devices, including headphones and headsets that rely on modern pairing mechanisms. The attack takes advantage of a feature called Fast Pair in Android. Fast Pair was designed to simplify the user experience. With a single tap users can connect their Bluetooth accessories and synchronize them with their account. It’s convenient and widely adopted.

However, some devices don’t properly ignore pairing requests when they aren’t in pairing mode. A hacker can exploit this by sending crafted pairing initiation packets to a vulnerable device. Even if the device isn’t actively trying to connect, it may still respond. Once the hacker receives that response, they can establish a normal Bluetooth connection.

whisperpair-cli
Source: WhisperPair

From that point on, the hacker gains control over the accessory.Β 

scanning for nearby ble devices
Source: WhisperPair

Then they can activate the microphone to record conversations. The attack works from up to 14 meters away, which is plenty for offices, cafes or public transport.

hijacking ble devices
Source: WhisperPair

This can be combined with device tracking. Some Bluetooth accessories integrate with Google’s Find Hub network, which allows lost devices to be located using nearby Android devices. If a vulnerable accessory has never been paired with an Android device before, a hacker can register it under their own Google account. In doing so, they become the β€œowner” of the device in the tracking system.

ble device surveillance with Find Hub
An attacker tracks the victim’s location through the Find Hub network. Source: WhisperPair

The victim may eventually receive a notification about unwanted tracking, but the alert can appear misleading. If the user’s own device is responsible for tracking, that will cause confusion and reduce the likelihood that the threat is taken seriously. Meanwhile, the hacker continues to track the device over time. It affects multiple vendors, chipsets and product lines. As a result, exploitation is likely to continue well beyond 2026.

Bluehood Scanner

Sometimes, attacks are completely passive. In February 2026, a developer released a Bluetooth scanner called Bluehood. It looks like a monitoring tool and shows how much information can be extracted from the environment without ever connecting to a device.

showing devices in bluehood

Bluetooth is almost always enabled. Phones, laptops, smartwatches, headphones, cars and even medical devices continuously broadcast signals. Bluehood listens to that data and builds patterns over time. By passively listening to this traffic over days or weeks, hackers can reconstruct behavior.

For example, you can find out when delivery vehicles arrive and whether the same driver appears regularly. You can see daily routines by tracking when certain devices appear and disappear. You can also correlate devices that are always seen together, such as a phone and a smartwatch, which likely belong to the same person. You can even determine approximate schedules when someone leaves for work or returns home.

You don’t need to buy hardware for that. In many cases, a laptop will do the job. If you want, you can get a Raspberry Pi with a Bluetooth adapter.Β 

bluehood alert configuration

Some devices are designed to always keep Bluetooth active. Hearing aids, for instance, rely on Bluetooth Low Energy for configuration and diagnostics. Pacemakers may also broadcast BLE signals for similar reasons. These aren’t devices that users can simply turn off.

Many cars use Bluetooth for diagnostics, driver assistance and connectivity features. Consumer devices add even more noise to the environment. Smartwatches, pet trackers and fitness equipment all give off signals. Together, they create a dense network of signals that can be analyzed.

bluehood

Bluehood works only in passive mode. It doesn’t try to connect to devices. It identifies them based on manufacturer data and BLE service UUIDs, then tracks when they appear and disappear. The tool also includes a web dashboard. It generates hourly and daily heatmaps, tracks dwell time and has filters. New devices often use randomized MAC addresses for privacy and Bluehood can detect and filter these.

Installation

You can installΒ  the tool quickly using Docker.

kali > git clone https://github.com/dannymcc/bluehood.git
kali > cd bluehood
kali > docker compose up -d
setting up bluehood with docker

Alternatively, you can install it using package managers and Python tools.

kali > sudo apt install bluez python3-pip
kali > pip install -e .
kali > sudo bluehood

After the installation you can start the scanner.

# Start with web dashboard (default port 8080)
kali > bluehood

# Specify a different port
kali > bluehood --port 9000

# Use a specific Bluetooth adapter
kali > bluehood --adapter hci1

# List available adapters
kali > bluehood --list-adapters

# Disable web dashboard (scanning only)
kali > bluehood --no-web

Keep in mind that if you installed the app with Docker Compose, it should be accessible at http://localhost:8080.

bluehood dashboard

Collected data is stored in SQLite, and the tool can optionally send notifications through ntfy.sh when devices arrive or leave a location.

Summary

Bluetooth security is often underestimated because the technology feels invisible and low risk. That’s not the case though. There are active and passive techniques that can be used for tracking. Big cities often have listeners scattered around public places and stations, working like Bluehood. Active techniques like WhisperPair can lead to full device compromise with tracking and audio surveillance.

If you enjoy experimenting with frequencies and trying new things, we have our SDR for Hackers training. With Master OTW, you’ll learn how to use your computer and inexpensive SDR hardware to explore and hack a wide range of radio signals.

The post Bluetooth Hacking and Security: The WhisperPair Exploit and Bluehood Surveillance first appeared on Hackers Arise.

OSINT: WireTapper – Mapping Surveillance and Wireless Devices Around You

Welcome back, aspiring cyberwarriors!

Take a second and think about how many devices are actually working around you right now. Cameras on street corners, routers sitting inside nearby homes, Bluetooth earbuds in someone’s pocket, cell towers just outside of view. All of that is happening constantly, yet almost none of it is visible to the average person walking by. If you actually wanted to check what devices were nearby today, you would probably end up jumping from one app to another, waiting for each one to load, and still walking away without the full picture. It is slow, it is frustrating, and honestly, it takes all the fun out of exploring what is really going on around you.

A lot of these devices are not just sitting there minding their own business. Many of them are built specifically to track you. A recent video on X showed this. It captured a flock camera taking several pictures of a moving vehicle, running those pictures through some kind of analysis, and then filing everything away in an indexed format.

In the screenshot above, you can see the guy picking up the signal coming straight off the camera, while the camera itself keeps emitting a steady beam of infrared. Here is the full video.

Privacy is not a crime, and you have every right to know what might be watching you. The real challenge has always been figuring out where all of these surveillance devices are hiding. That’s where WireTapper can help us. It pulls data from Wigle, Shodan, and OpenCelliD one at a time. That way, you can see every one of these devices in your area.

WireTapper

WireTapper is a wireless OSINT tool designed to discover, map, and analyze radio based devices using passive signal intelligence. WireTapper detects and correlates signals coming from all the common wireless technologies you would expect to run into. This helps you understand what devices actually exist nearby and where they are likely located all without ever having to actively intrude on anything.

WireTapper can identify leaked Wi-Fi network credentials, and it does this through a privacy-protecting k-Anonymity query scheme, meaning it can check for exposed passwords without ever exposing your own search to the outside world.

Setting Up

Let’s quickly walk through the installation process. It’s a lot simpler than it looks.

kali > git clone https://github.com/h9zdev/WireTapper.git
kali > cd WireTapper
kali > python3 -m venv venv; source venv/bin/activate
kali > pip3 install -r WireTapper.txt

Once that finishes, you will need to grab API keys from each of the services mentioned above. Do not worry too much about Shodan, since its API is paid and WireTapper will still run fine without it. There are two ways to plug these keys into the app. You can either open app.py and enter them directly, or you can use app-env.py instead, which pulls the keys in through environment variables.

After you have picked your method, we recommend also installing python-dotenv, since it makes handling those environment variables a lot smoother.

kali > pip3 install python-dotenv

Working with WireTapper

Once everything is installed, you are ready to start the app and open the web interface.

kali > python3 app.py

The web interface will be waiting for you right here: http://localhost:8080/map-w

This is the dashboard you will land on the moment you open the page. It takes a little while to load everything, so give it a few minutes before you start clicking around. Once it settles in, you can zoom into whatever area you are curious about and start picking apart what is actually hiding there.

Just keep in mind that you need valid API keys for the app to work the way it is meant to. Without them, WireTapper will simply generate dummy data so you can still see how everything normally looks inside it. On Wigle specifically, your email needs to be verified before the connection will work properly.

At the top of the dashboard, you will notice a switch that lets you jump between Wi-Fi uplink and Bluetooth scanners. That is how you filter what you are looking at.

Flip the switch back the other way, and you get the same kind of view but for Wi-Fi devices instead. This side usually includes things like cameras, routers, and other similar devices.

Exporting Results

All of these results can be exported complete with their names and coordinates, in case you decide to use them somewhere else later on.

The example above is just a taste of how those exported results are going to look. You can use this JSON file with other tools.

Summary

There is far more happening around us than most people realize. WireTapper makes it easier to visualize that activity by bringing together information about nearby wireless infrastructure in one interface. If you’re into OSINT, privacy, or wireless security, it’s a handy tool.Β 

OSINT is a valuable skill in many areas, especially when it comes to privacy, cybersecurity, and cyber warfare. The more you understand what information is publicly exposed, the better you can protect yourself and your digital assets. Our Ultimate OSINT Beginner training covers OPSEC, tracking, investigations, and much more across 23 lessons and 7.5 hours of video content.

We’re also hosting a live Remaining Anonymous training on August 11-13 at 3:00 PM UTC for all Subscriber and Subscriber Pro students.

The post OSINT: WireTapper – Mapping Surveillance and Wireless Devices Around You first appeared on Hackers Arise.

❌