
 Login

Browser Forensics: Analyzing Suspicious Extensions with ExtAnalysis
Welcome back, aspiring cyberwarriors!
These days, most of our online activity happens in web browsers. They’re our main way to access the internet, but they can also make it easy for malware to slip into our systems. While there are known vulnerabilities in browsers, the real trouble often comes from malicious browser extensions.
So, in this article, we’ll take a look at a tool called ExtAnalysis that acts as a first line of defense against sketchy plugins. It helps you do some forensic research and static code analysis quickly and visually. Let’s get rolling!
Getting Started with ExtAnalysis
ExtAnalysis is an open-source security framework designed to scan, analyze, and extract threat intelligence from Chrome, Firefox, Edge, and Brave extensions. It runs locally as a web application powered by a Flask backend.
To install it, we need to clone the repository from GitHub and run the main Python script:
kali> git clone https://github.com/Tuhinshubhra/ExtAnalysis
kali> cd ExtAnalysis
kali> pip3 install -r requirements.txt --break-system-packages
kali> python3 extanalysis.py
By default, ExtAnalysis binds to 127.0.0.1 on port 13337 and automatically opens a browser window to http://127.0.0.1:13337.

ExtAnalysis supports different formats. First of all, we can just provide a link to the plugin published on the Chrome Web Store or Firefox Add-ons. Secondly, it supports local extension scanning. And lastly, we can manually upload unpacked or packed extension archives in .crx, .xpi, .zip, and .tar formats. For this demonstration, I’ll just provide a link to a random crypto wallet published in the Chrome Web Store.
After entering the URL, ExtAnalysis will start analysis. Depending on the size of the plugin, it can take time. Eventually, you will see the report as below.

On the basic info tab, we can see data like name, author, version, extracted URLs, etc. Also, this tab has a built-in viewer for reviewing manifest.json configuration blueprints.
By changing the tab to Files, we can explore an interactive network graph. It constructs an interactive network graph mapping all extension source files, internal scripts, outbound external URLs, and domain relationships.
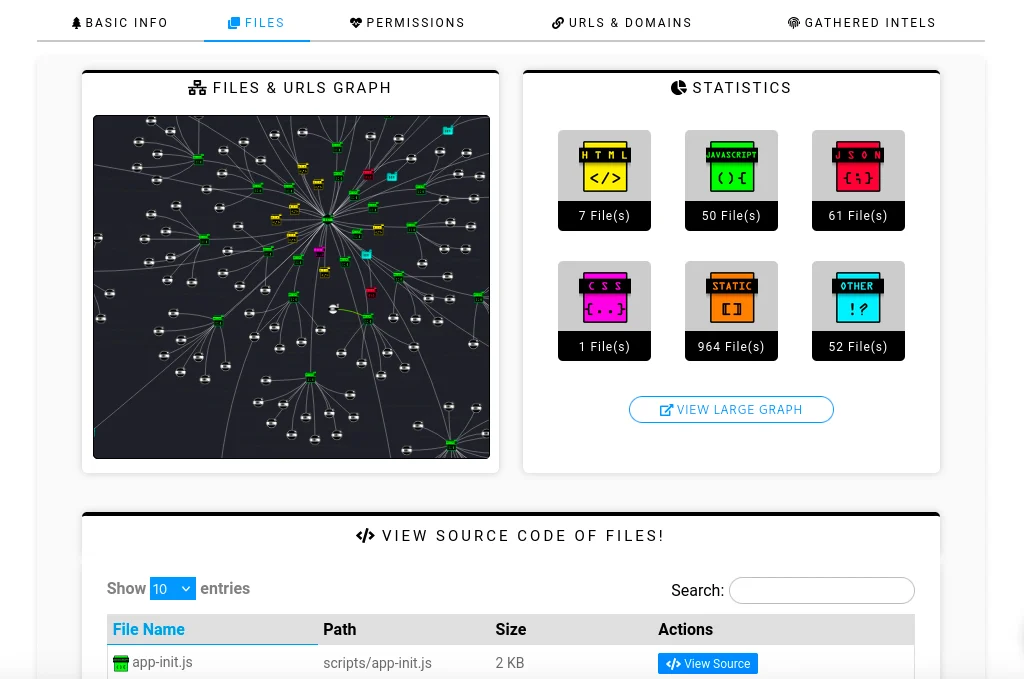
As you can see at the bottom of the screenshot, ExtAnalysis also allows viewing the source code of the files. It features an embedded tool to de-minify and restructure obfuscated or dense JavaScript and CSS files for manual code audits.
Next, we have the permission risk assessment tab.

ExtAnalysis parses requested permissions and categorizes them into risk levels (High, Medium, etc) to highlight capability escalation.
After that, we have the URL Reconnaissance Suite tab.

This tab provides extracted domains, URLs, and external JS files. For full functionality, navigate to the settings menu inside the web interface and enter your VirusTotal API key to enable automated hash and domain scans.
And last but not least is the tab with extracted intelligence.


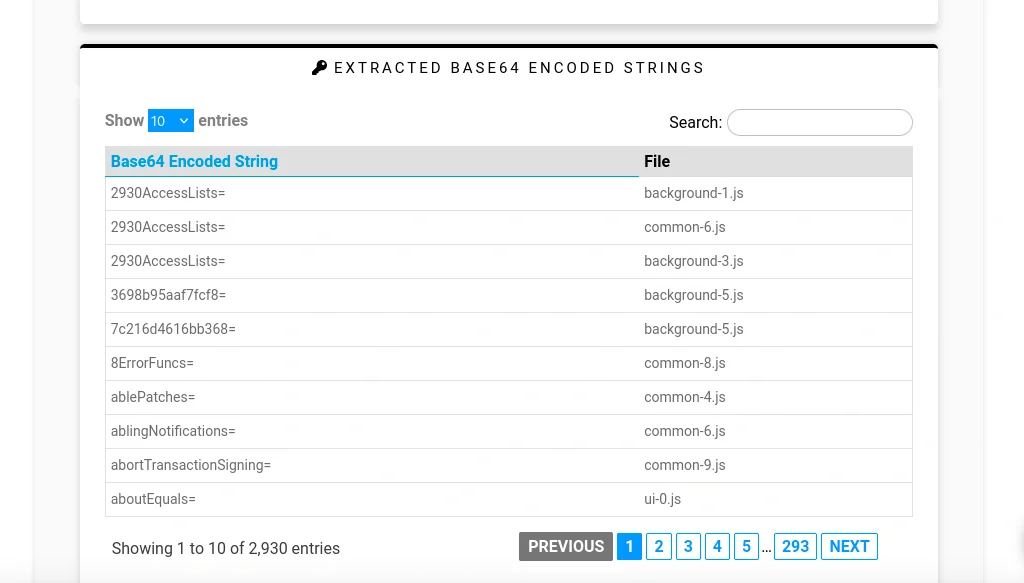
ExtAnalysis automatically scans all extension files to parse and extract hardcoded threat indicators, including IPv4 and IPv6 addresses, domains, full URLs, Bitcoin wallet addresses, and email addresses. It also detects Base64-encoded strings and raw file comments.
Workflow for Analyzing an Extension
Start by submitting the target extension for analysis. Next, review its manifest file and requested permissions to identify any overreach or suspicious capabilities. Then, inspect the interactive visual graph to map external domains, C2 infrastructure, and suspicious third‑party endpoints. After that, extract intelligence and IOCs by checking the dedicated tabs for hardcoded IP addresses, Base64 strings, Bitcoin wallet addresses, and other indicators of compromise. Finally, perform a code audit by opening JavaScript files in the built‑in viewer, applying the code beautifier, and inspecting background scripts for keyloggers, credential‑harvesting triggers, or other malicious logic.
Important Limitations to Keep in Mind
ExtAnalysis performs static analysis only, scanning extension source files without capturing runtime execution or behavior triggered dynamically. Heavily obfuscated JavaScript or sandbox‑evasion scripts can obscure its automated analysis, reducing visibility into malicious logic. For this reason, security researchers typically use ExtAnalysis as a fast first‑step reconnaissance tool to map structure and permissions before proceeding to dynamic analysis.
Summary
Web browser plugins make our lives easier, but if plugin developers have malicious intent, they can introduce significant security risks. In this article, we explored static analysis of extensions using the ExtAnalysis tool. Always pay attention to what you install, and stay secure.
The post Browser Forensics: Analyzing Suspicious Extensions with ExtAnalysis first appeared on Hackers Arise.
