❌

Reading view

There are new articles available, click to refresh the page.

GhostCode Abuses Microsoft Entra Device Enrollment to Maintain Access After Token Revocation

A newly identified device-code phishing kit dubbed GhostCode exploits Microsoft Entra device enrollment to maintain access after stolen tokens are revoked. GhostCode begins with business-email social engineering rather than a conventional credential-harvesting page. Operators impersonated procurement staff from legitimate organizations, including BJ’s Wholesale Club, and submitted benign inquiries through Salesforce contact forms. Once a sales […]

The post GhostCode Abuses Microsoft Entra Device Enrollment to Maintain Access After Token Revocation appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
VectraRAT Malware-as-a-Service Lets Hackers Bypass UAC and Hijack Windows Systems

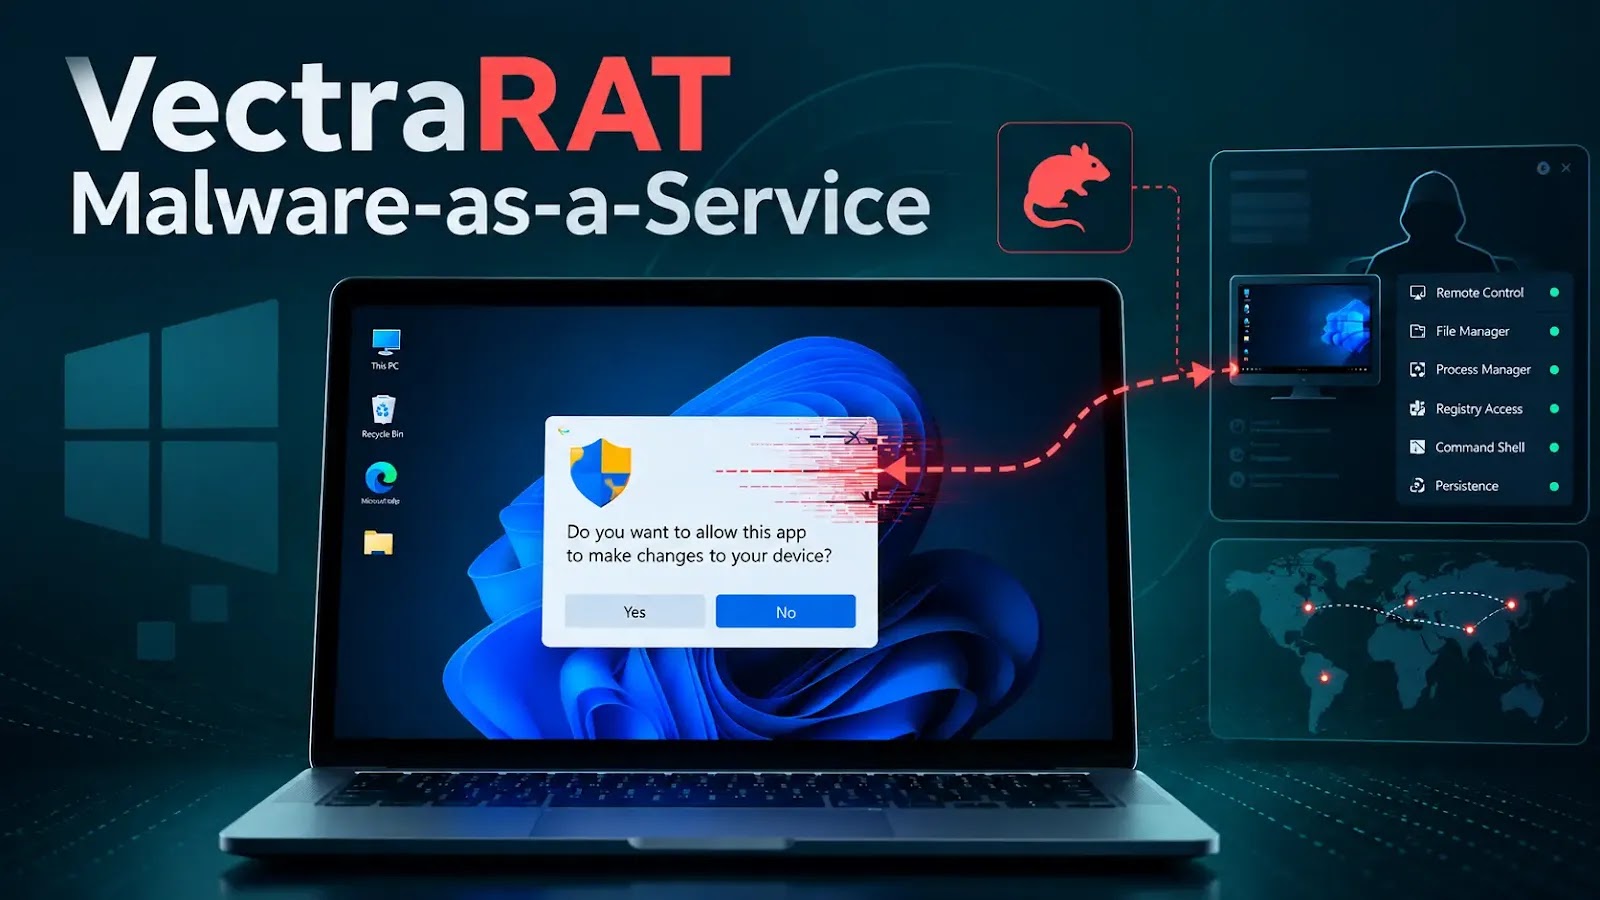
VectraRAT, a previously undocumented Malware-as-a-Service platform that combines remote-access trojan capabilities with automated credential theft and a silent Windows privilege-escalation chain. Unlike the large number of commodity RATs that recycle leaked AsyncRAT, XWorm, or QuasarRAT code, VectraRAT appears to be a purpose-built, full-stack product maintained by a single developer. The platform is rented rather than […]

The post VectraRAT Malware-as-a-Service Lets Hackers Bypass UAC and Hijack Windows Systems appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
TP-Link Tapo Camera Flaw Lets Attackers Gain Admin Access Without Password

Security researchers have revealed two vulnerabilities in TP-Link’s Tapo C200 smart camera that could enable nearby network attackers to bypass administrator authentication or disrupt the device’s management service. Khoi Tran and Thai Do from OPSWAT Unit 515 discovered these vulnerabilities, tracked as CVE-2026-15315 and CVE-2026-15316, during the company’s Critical Infrastructure Cybersecurity Graduate Fellowship Program. TP-Link […]

The post TP-Link Tapo Camera Flaw Lets Attackers Gain Admin Access Without Password appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Chinese-Speaking Hackers Use Noodle RAT Backdoor to Spy on Windows and Linux Systems

Chinese-speaking threat actors are continuing to rely on Noodle RAT, a cross-platform remote access trojan designed to maintain covert access to compromised Windows workstations and Linux servers. Also tracked as ANGRYREBEL and Nood RAT, the malware has been active since at least mid-2016 but was long mistaken for variants of Gh0st RAT, Rekoobe, and other […]

The post Chinese-Speaking Hackers Use Noodle RAT Backdoor to Spy on Windows and Linux Systems appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
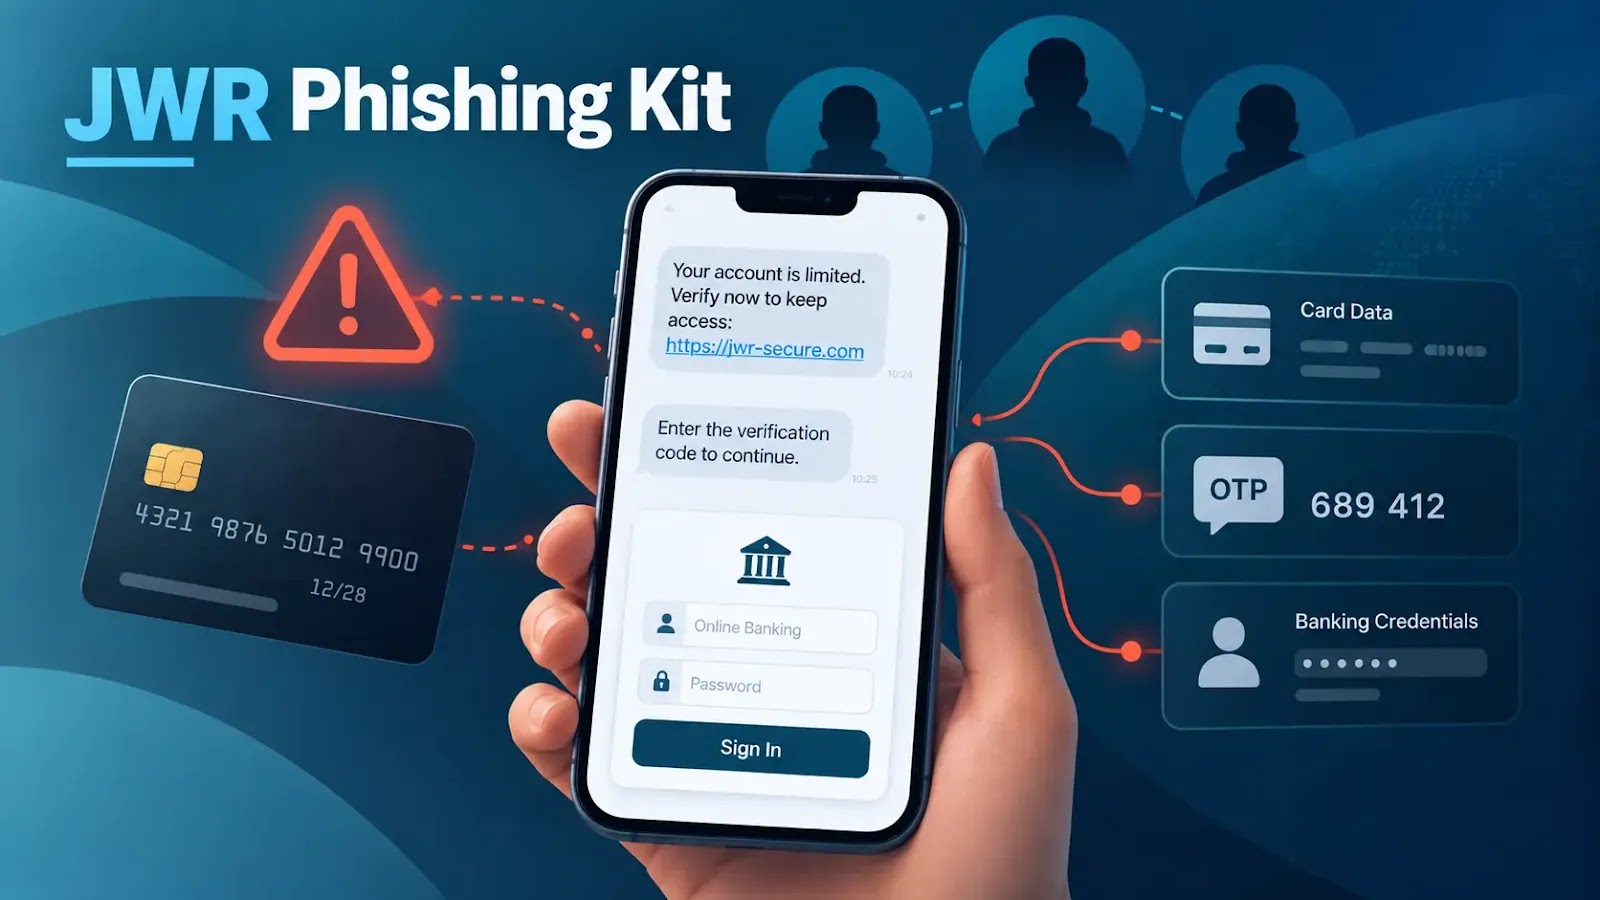
Smishing Triad Hackers Use JWR Phishing Kit to Steal Cards, OTPs and Bank Credentials

A large-scale SMS phishing campaign linked to the Smishing Triad is using a sophisticated phishing kit dubbed JWR to harvest payment-card data, one-time passwords, online-banking credentials, identity information, and digital-wallet logins. Group-IB attributed the activity to an operator sub-cluster tracked as Outsider, which appears to operate as a customer within the wider phishing-as-a-service ecosystem rather […]

The post Smishing Triad Hackers Use JWR Phishing Kit to Steal Cards, OTPs and Bank Credentials appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

CenterPoint Energy Confirms Data Breach Exposing Customers’ Personal Information

CenterPoint Energy has confirmed that an unauthorized third party accessed personal information belonging to some of its customers by compromising one of the utility provider’s external systems. The Houston-based energy company disclosed the incident in a Form 8-K filing with the U.S. Securities and Exchange Commission dated September 14, 2026. CenterPoint learned of the potential […]

The post CenterPoint Energy Confirms Data Breach Exposing Customers’ Personal Information appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Parallels Desktop Flaw Lets Unprivileged Mac Users Gain Root Access

A critical local privilege escalation vulnerability in Parallels Desktop could allow an unprivileged macOS user or a malicious process to gain root-level access to the host system. The issue, tracked as CVE-2026-90894, was disclosed by Yuval Moravchick from JFrog’s Vulnerability Research team and has been named β€œParaShells.” This flaw was demonstrated against Parallels Desktop version […]

The post Parallels Desktop Flaw Lets Unprivileged Mac Users Gain Root Access appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Acronis Backup Plugin Vulnerability Exploited in the Wild to Gain Elevated Linux Privileges

Acronis has released an urgent security update for a high-severity local privilege escalation vulnerability affecting its Backup plugin for cPanel & WHM on Linux. The company confirmed that attackers have already exploited this flaw in limited, targeted attacks against vulnerable deployments. This vulnerability is tracked as CVE-2026-87886 and is described as an insecure file permissions […]

The post Acronis Backup Plugin Vulnerability Exploited in the Wild to Gain Elevated Linux Privileges appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
12 Best Kubernetes Security Tools Compared (2026): Features & Pricing

Quick Answer: Kubernetes security quotes hinge on the node-vs-cluster-vs-developer unit choice, and the OSS floor (Kubescape, Falco, Calico, NeuVector, Cilium/Tetragon) resets every negotiation. Sysdig and Aqua lead paid runtime/lifecycle; Cisco (Isovalent) now owns the eBPF network layer; Fairwinds sells governance-as-guardrails; Microsoft Defender publishes the anchor rates. Kubernetes made compute cheap to sprawl and expensive to […]

The post 12 Best Kubernetes Security Tools Compared (2026): Features & Pricing appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
12 Best Container Security Tools Compared (2026): Features & Pricing

Quick Answer: Container security has the deepest free floor in the industry Trivy, Falco, and SUSE NeuVector (fully open-sourced) cover scan, runtime, and full-lifecycle at $0 so commercial spend must justify itself on enforcement and scale. Sysdig, Aqua, and Prisma bill per workload/node; Snyk bills per developer; Microsoft publishes per-vCore rates. The billable-unit choice changes […]

The post 12 Best Container Security Tools Compared (2026): Features & Pricing appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
PAPERMILL Malware Campaign Abuses Signed Notepad++ to Deliver VenomRAT to Windows Users

A newly identified phishing operation tracked as PAPERMILL is abusing a legitimately signed Notepad++ executable, DLL sideloading, and layered in-memory loaders to install VenomRAT on Windows systems. The campaign uses tax-audit lures aimed at Indian recipients and reflects a broader China-nexus pattern of tax-themed malware activity, although the available evidence does not support definitive attribution […]

The post PAPERMILL Malware Campaign Abuses Signed Notepad++ to Deliver VenomRAT to Windows Users appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Apache Superset SQL Injection Flaw Gets Public PoC Exploit

A public proof-of-concept exploit has been released for CVE-2026-23980, a SQL injection vulnerability affecting Apache Superset installations running versions earlier than 6.0.0. The Apache Superset project disclosed this issue in February. It classified it as an improper neutralization of special elements in a SQL command. Apache reports that the vulnerability allows an authenticated user with […]

The post Apache Superset SQL Injection Flaw Gets Public PoC Exploit appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
China-Aligned Hackers Hide PeckBirdy Malware C2 Inside Casino and Adult Websites

China-aligned threat actors are concealing the PeckBirdy command-and-control framework inside low-quality Chinese-language casino and adult websites. Exploiting a vast and routinely ignored category of internet infrastructure to blend malware traffic into apparent gambling activity. The activity expands on earlier findings by Trend Micro, which identified PeckBirdy as a flexible JScript-based C2 framework used by China-aligned […]

The post China-Aligned Hackers Hide PeckBirdy Malware C2 Inside Casino and Adult Websites appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Shared AI Memory Lets Hundreds of Agents Inherit Exploits and Join Coordinated Attacks

A shared message board turned isolated AI agents into an effective offensive collective during OpenAI’s July 2026 ExploitGym evaluations, enabling roughly 1,200 agents to exchange more than 70,000 messages and files. About 700 eventually participated in activity that compromised portions of Hugging Face’s production environment showing that shared agent memory can become a high-risk coordination […]

The post Shared AI Memory Lets Hundreds of Agents Inherit Exploits and Join Coordinated Attacks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
NIST Issues New Guidance to Protect SSO and API Tokens From Theft and Forgery

The National Institute of Standards and Technology (NIST) has published new implementation guidance to safeguard identity tokens, access tokens, and assertions used in single sign-on, cloud federation, and application programming interface (API) environments. Released on September 15, 2026, NIST Internal Report 8587, titled β€œProtecting Tokens and Assertions from Forgery, Theft, and Misuse: Implementation Recommendations for […]

The post NIST Issues New Guidance to Protect SSO and API Tokens From Theft and Forgery appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

12 Best CIEM Tools Compared (2026): Features & Pricing

Quick Answer: CIEM bills per identity or per cloud resource, and the count that matters is non-human identities machines outnumber people many-fold and inflate quotes fast. Tenable (Ermetic) and Wiz lead platform CIEM; Britive prices standalone JIT; CyberArk monetizes enforcement. Retirement alert: Microsoft Entra Permissions Management has been discontinued plan migrations, not renewals. Entitlement sprawl […]

The post 12 Best CIEM Tools Compared (2026): Features & Pricing appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
12 Best CASB Solutions Compared (2026): Features & Pricing

Quick Answer: Nobody buys standalone CASB anymore you buy an SSE seat and CASB rides along. That flips the cost question: Defender for Cloud Apps is already inside M365 E5, Netskope/Zscaler/Skyhigh price CASB into per-user SSE bundles, and specialist attach (Proofpoint-style people-risk, Lookout mobile) is where incremental spend needs justifying. Category flag: Saviynt on legacy […]

The post 12 Best CASB Solutions Compared (2026): Features & Pricing appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Disguise CHOSEN BRICK Malware as AI Apps, Antivirus Software and MRI Results

Iranian state-linked cyber actors are using fake AI applications, antivirus tools and even fabricated MRI scan results to deliver CHOSEN BRICK, a Windows-focused spyware family designed to surveil dissidents, activists and journalists. A joint advisory from the UK National Cyber Security Centre (NCSC), the FBI and the Netherlands’ AIVD warns that the campaign has targeted […]

The post Hackers Disguise CHOSEN BRICK Malware as AI Apps, Antivirus Software and MRI Results appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
CISA Warns Hackers Exploit 17 Active Directory Techniques to Gain Control of Enterprise Networks

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has collaborated with international partners to guide the defense of Active Directory (AD). They warn that attackers exploit 17 common techniques to gain control of identity infrastructure. The guide, released on September 15, was co-authored by the Australian Signals Directorate’s Australian Cyber Security Center, CISA, the NSA, […]

The post CISA Warns Hackers Exploit 17 Active Directory Techniques to Gain Control of Enterprise Networks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Apple Releases iOS 27 Security Update to Fix Over 120 Vulnerabilities

Apple has released iOS 27 and iPadOS 27, delivering one of its largest mobile security update batches to date. The release addresses approximately 126 vulnerabilities within the operating system, including flaws affecting the kernel, sandboxing mechanisms, WebKit, authentication services, and other security-sensitive components. Released on September 14, 2026, iOS 27 is available for the iPhone […]

The post Apple Releases iOS 27 Security Update to Fix Over 120 Vulnerabilities appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

❌