Login

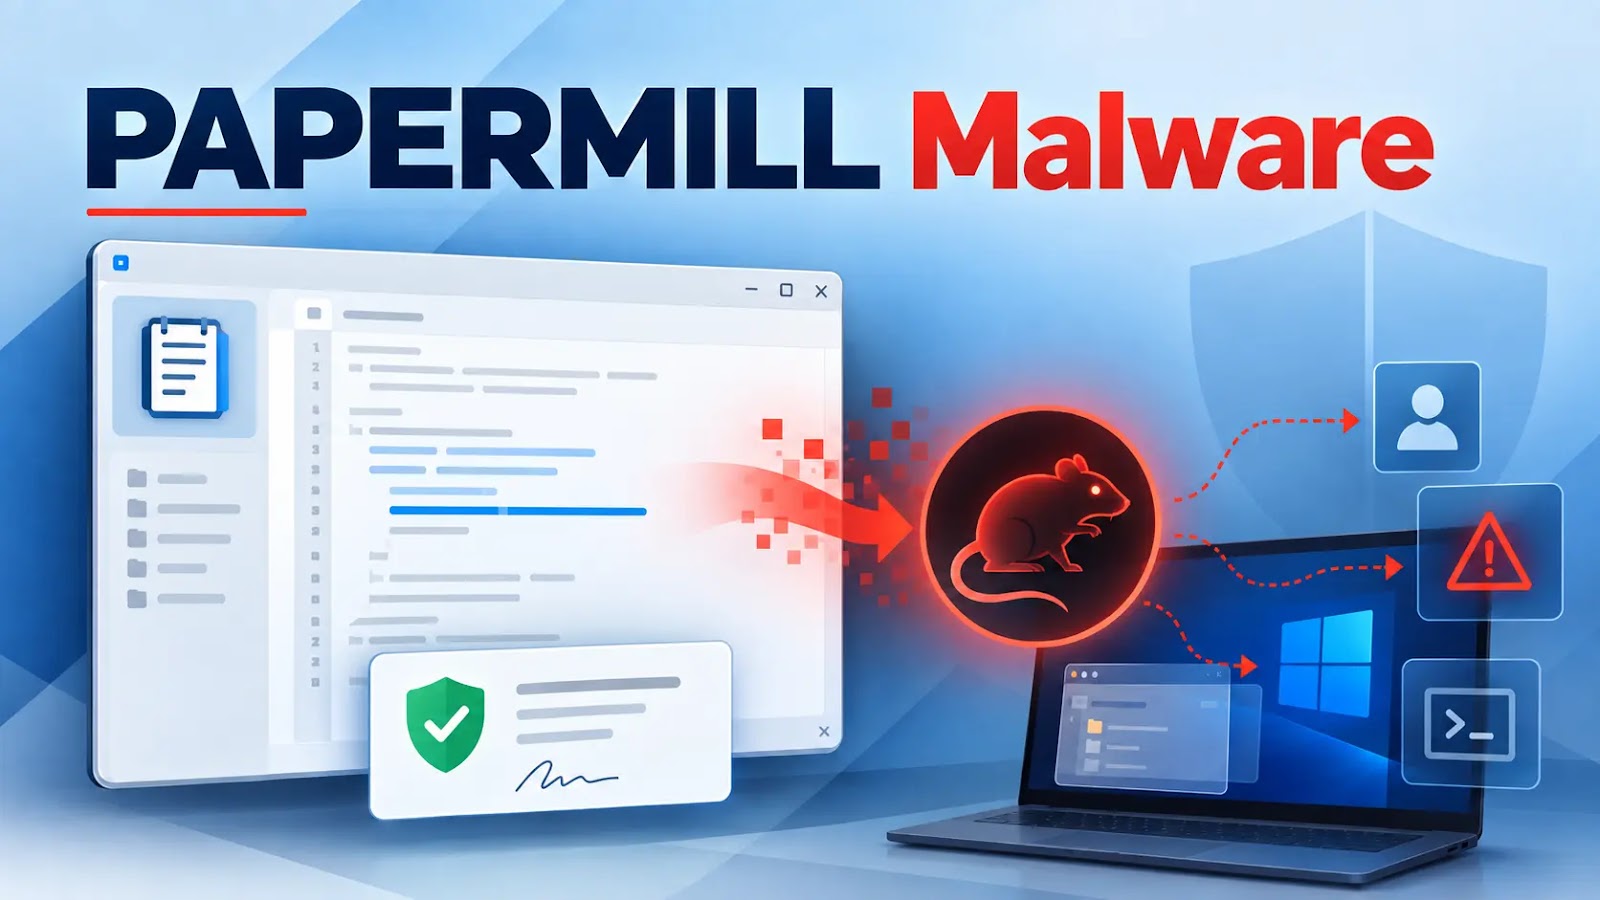
PAPERMILL Malware Campaign Abuses Signed Notepad++ to Deliver VenomRAT to Windows Users
A newly identified phishing operation tracked as PAPERMILL is abusing a legitimately signed Notepad++ executable, DLL sideloading, and layered in-memory loaders to install VenomRAT on Windows systems. The campaign uses tax-audit lures aimed at Indian recipients and reflects a broader China-nexus pattern of tax-themed malware activity, although the available evidence does not support definitive attribution […]
The post PAPERMILL Malware Campaign Abuses Signed Notepad++ to Deliver VenomRAT to Windows Users appeared first on GBHackers Security | #1 Globally Trusted Cyber Security News Platform.