Illicit software on the computers of some of the world’s best online poker players allowed the accused cheater to see what cards were in the victims’ hands—and trounce them at the tables.
Bluesky tells WIRED it blocked links to a leaked archive of information on 41,000 ICE, CBP, and other DHS workers because it contains people’s contact information, shared without their authorization.
The leaked records include the locations of ICE and CBP facilities, workers’ cell phone numbers, and the members of groups tied to wiretap programs, Palantir software, and xAI’s Grok chatbot.
The PHP scare may have faded from your feed, but the cleanup is far from over. Last week, two critical bugs in the open source language behind roughly 70% of websites left organizations scrambling to fix their systems, with some taking sites offline until the vulnerabilities could be patched. According to researchers who found the […]
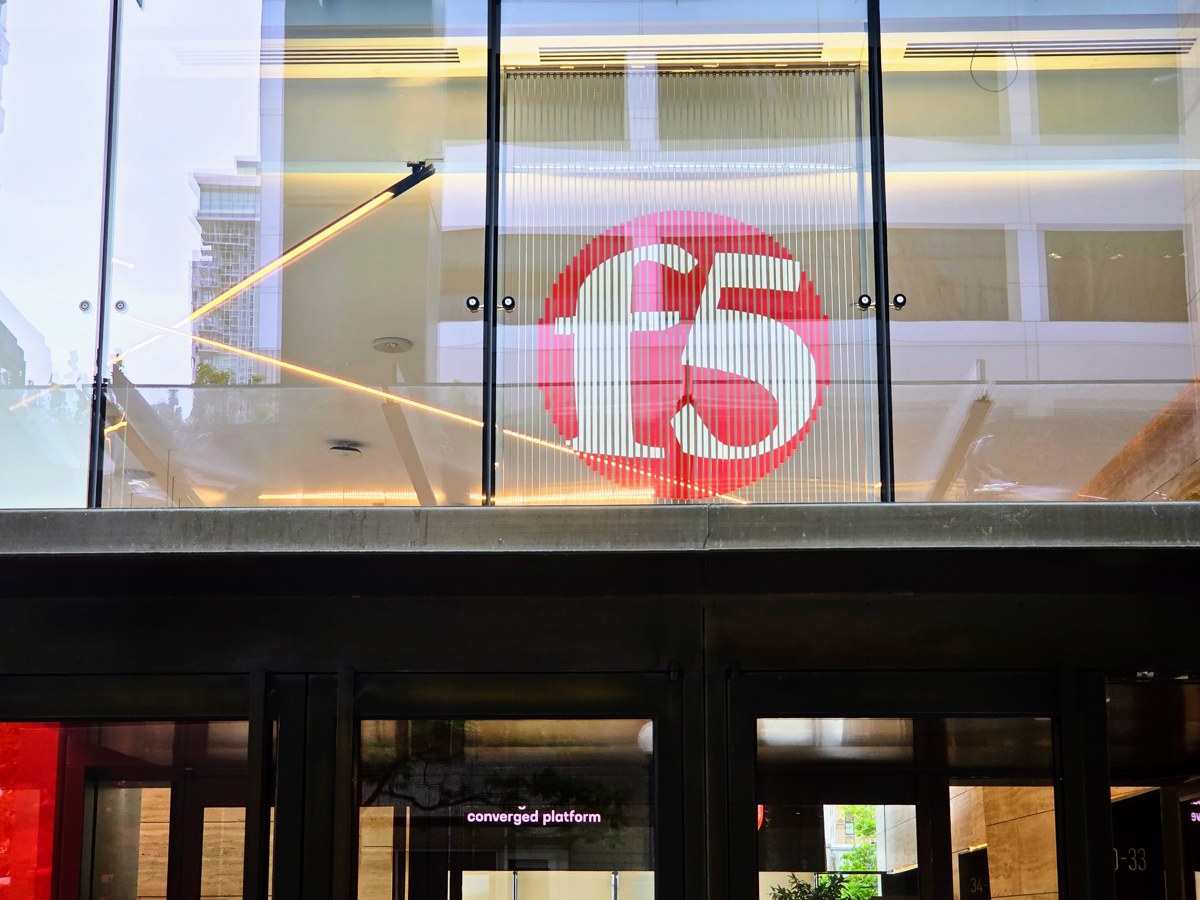
F5’s logo at the entrance to F5 Tower in downtown Seattle. The company’s stock fell about 20% Wednesday after it forecast slower growth and lower margins, along with more spending on AI security. (GeekWire Photo / Todd Bishop)
Shares of F5 fell about 20% on Wednesday, a day after the Seattle-based company beat Wall Street’s estimates and said it would boost spending to capitalize on expected growth in the AI security market.
The application security and delivery company’s stock was trading around $368 late Wednesday morning, down from $459 at Tuesday’s close, wiping out about $5 billion in market value. That put F5 on pace for its biggest one-day drop in more than 13 years, according to Barron’s. Before the drop, F5’s shares had climbed nearly 80% this year.
F5’s revenue for its fiscal fourth quarter rose 13% to $917 million, and product revenue jumped 23%. Adjusted earnings of $4.42 a share beat estimates of about $4.30.
Slower growth ahead: Investors seem to be focused on the outlook. F5 expects revenue to grow 8% to 9% in fiscal 2027, down from 11% this year, and adjusted earnings per share to grow 3% to 5%. It’s also projecting lower margins as memory and storage components get more expensive, and as it doubles its team of AI security sellers.
F5’s hardware business is also cooling off. Systems revenue jumped 29% in the quarter as customers replaced aging equipment, but F5 Chief Financial Officer Cooper Werner said on the earnings call that those replacements will taper off in the second half of fiscal 2027.
The AI bet: F5 is spending more to go after AI security. CEO François Locoh-Donou said on the call that the company will double its team of specialist AI security sellers in fiscal 2027 and more than double its marketing in that area. It’s also adding compensation incentives for all of its field sellers to discuss AI security with customers.
F5’s adjusted operating margin fell to 33.7% in the quarter, from 37% a year earlier.
Locoh-Donou said F5’s AI-related bookings topped $100 million in fiscal 2026, up about 300%. Most of that came from AI data delivery, which moves data to and from AI systems, rather than security. More than 300 customers are using an AI-powered web application firewall that F5 launched in March.
The company estimates the AI market it sells into will grow from about $1 billion this year to $11 billion by 2030.
Wall Street reaction: Piper Sandler downgraded the stock to neutral, according to The Motley Fool. Analysts at William Blair, which rates F5 “market perform,” wrote in a research note that “the AI opportunity has yet to contribute meaningfully to the top line.”
We’ve contacted F5 for comment on the stock decline.
F5 has been building out its AI security business, including its acquisition of SurePath AI. Locoh-Donou talked about the company’s path from the early web to AI security on a GeekWire Podcast episode marking F5’s 30th anniversary. He said companies adopting AI are losing track of what those systems can access, and that juggling separate tools to manage it is a burden, which is why F5 is building a single AI security platform.
This week, F5’s board authorized an additional $1.5 billion in stock buybacks, on top of $322 million remaining in its existing program.
Vietnam and India are advancing AI, cybersecurity, and digital payments partnerships, but key projects and cross-border payment services remain in development.
Most of us download and install new apps and self-hosted services without a second thought, but if you do anything important on your PC, it can be a significant security risk.
ICE’s Homeland Security Investigations is engaged in far-reaching spying against left-wing activists that rivals the FBI and CIA crackdowns on the Civil Rights and anti-war movements.
Ars Technica's Dan Goodin reports: Defenders across the world face the burden of responding to yet another botched code-execution vulnerability, this time in boot-time firmware used by most of the world's server vendors and data centers. The vulnerability, with a severity rating of 9.5 out of 10, resides in the TianoCore EDK II, an open source codebase that hardware makers and cloud providers use to create the UEFI firmware that runs during the boot-up sequence. Last year, a representative of the UEFI Forum called (PDF) EDK2 the "preeminent solution / implementation of the UEFI specifications." Virtually all UEFI suppliers (sometimes still called IBVs or independent BIOS vendors), including AMI, Insyde, and Phoenix, use the reference code extensively. Project Mu, Microsoft's hardened EDK2 fork, used the code containing the vulnerable component as well.
The vulnerability, tracked as CVE-2026-97631, is a memory-corruption flaw in an ICMP component that attackers can exploit to execute malicious code that runs before the operating system and firmware can implement defenses like Secure Boot, which establishes a chain of trust for all code, including the Trusted Platform Module (TPM), loaded during boot. While final payloads delivered by CVE-2026-97631 have no persistence -- meaning they run only once -- they can give attackers a wide opening to install other payloads that also run each time early in the boot process.
The parties that discovered CVE-2026-97631 -- Alex Matrosov of Anthropic and Dan Holmes of Google -- had arranged for it to stay under wraps until a coordinated disclosure that was scheduled for January. AMI, a maker of motherboards and other hardware, published this pull request last month that detailed the vulnerability and included a code fix. Once the post came to the attention of the discovering parties, TianoCore Project members published a public advisory last week. With publicly available patch code, it will be trivial for advanced hackers to learn how the vulnerability is triggered and to build working exploits. Further compounding the urgency, patching UEFI code vulnerabilities in millions of end devices sold and used by thousands of hardware makers and cloud providers is cumbersome and time-consuming.
Defenders across the world face the burden of responding to yet another botched code-execution vulnerability, this time in boot-time firmware used by most of the world’s server vendors and data centers.
The vulnerability, with a severity rating of 9.5 out of 10, resides in the TianoCore EDK II, an open source codebase that hardware makers and cloud providers use to create the UEFI firmware that runs during the boot-up sequence. Last year, a representative of the UEFI Forum called EDK2 the "preeminent solution / implementation of the UEFI specifications." Virtually all UEFI suppliers (sometimes still called IBVs or independent BIOS vendors), including AMI, Insyde, and Phoenix, use the reference code extensively. Project Mu, Microsoft's hardened EDK2 fork, used the code containing the vulnerable component as well.
The vulnerability, tracked as CVE-2026-97631, is a memory-corruption flaw in an ICMP component that attackers can exploit to execute malicious code that runs before the operating system and firmware can implement defenses like Secure Boot, which establishes a chain of trust for all code, including the Trusted Platform Module (TPM), loaded during boot. While final payloads delivered by CVE-2026-97631 have no persistence—meaning they run only once—they can give attackers a wide opening to install other payloads that also run each time early in the boot process.

 Login