At least four espionage groups, most with suspected links to China, are using a new exploit kit that chains two Chromium-based browser flaws and one Microsoft Windows bug to break into organizations' networks in the US and Southeast Asia. Mark Kelly, a threat researcher at email security shop Proofpoint, told The Register that the researchers don't know exactly who was targeted, nor how, and so far the damage appears limited. “In terms of organizations targeted, we saw fewer than 20 organizations globally targeted across the activity highlighted," he said. "However, the true number is almost certainly higher than this.” Proofpoint’s threat hunters spotted the new kit, which they named BlueMoon, and said its first observed use started on August 28. This is when a Beijing-backed crew they track as TA412, also known as Violet Typhoon and APT31, used BlueMoon to “repeatedly” target non-governmental organizations (NGOs), mining companies, and physical commodity trading firms in the US. TA412 is a cyberespionage group linked by US authorities to China's Ministry of State Security (MSS), and American prosecutors previously charged seven alleged members with conspiracy to commit computer intrusions and wire fraud, alleging they broke into computer networks, email accounts, and cloud storage belonging to numerous critical infrastructure organizations, companies, and individuals. Just days after Proofpoint documented the late-August activity, “several other espionage-motivated clusters began using BlueMoon, the majority of which have a suspected China nexus,” Kelly and fellow researchers Greg Lesnewich, Konstantin Klinger, Saher Naumaan, Julia Paluch, David Galazin, and Stuart Del Caliz said on Wednesday, noting that there may be other, non-China-nexus attackers using the exploit kit as well. “BlueMoon was developed and deployed rapidly, and shared across multiple threat actors within days,” Kelly told The Register. “This may reflect a reduced cost and barrier to entry for this class of capability, which has historically been rare and high value, as AI agents increasingly enable threat actor exploit development. That is particularly true for open-source codebases such as Chromium, where publicly accessible upstream patches create a ‘patch-gap’ window for rapid reverse engineering and exploit development ahead of downstream stable releases.” A Google spokesperson declined to comment beyond what Proofpoint wrote. Microsoft patched the Windows bug (CVE-2026-85880) on Tuesday, and a spokesperson reiterated that customers who applied that patch are protected. BlueMoon attack chain The kit chains together three vulnerabilities. The first is a V8 type confusion (CVE-2026-85046) flaw that allows remote code execution and affects all Chromium-based browsers, including Google Chrome and Microsoft Edge. Google patched this bug in Chrome on September 3, and at the time warned that it “is aware that an exploit for CVE-2026-85046 exists in the wild.” Microsoft published a security advisory saying it fixed the flaw in Edge Stable version 152.0.4191.62 on September 2. The second is a Chrome V8 sandbox escape. This one also affected all Chromium-based browsers. It does not have a CVE because Google doesn’t issue them for sandbox escapes. Finally, the third bug is a privilege escalation vulnerability in Windows Advanced Local Procedure Call (CVE-2026-85880) that Microsoft patched on Tuesday, as noted above. Redmond also warned that this flaw had been exploited as a zero-day prior to the security update. The Proofpoint researchers also note that both V8 vulnerabilities are what’s called "patch-gap" zero-days at the time of the observed activity. This means they were known and fixed in upstream Chromium source code – a change containing the fix for CVE-2026-85046 was committed on August 7. But they remained unpatched in the latest stable releases of Chrome and Chromium-based browsers available to the public for weeks. “It is likely that the exploit kit developer used these publicly available Chromium patches to weaponize the browser exploit chain,” the researchers note. From phishing to browser surveillance The attacks start with a phishing email that tricks victims into clicking on an actor-controlled URL. This triggers the two V8 bugs to allow remote code execution and escape the browser sandbox. The attack chain then exploits the Windows bug to download multiple payloads including browser-surveillance malware, credential-stealing backdoors, and others, depending on the group using the exploit kit. TA412’s first campaign, which began on August 28, used a range of lures. Some of the emails purported to come from university students interested in internships at the targeted organizations, and some were more target-specific exchanges, intended to build trust with the individual before ultimately sending a malicious link via email. In these instances, the exploit chain “ultimately downloaded and ran a loader executable on the infected host, which then installed a malicious browser extension disguised as Google Gemini on the victim's Chromium-based browser,” the team wrote. This browser extension, which Proofpoint tracks as GemStone, allowed the Beijing spies to issue commands through a command-and-control (C&C) channel, steal cookies and other sensitive data, take screenshots, and inject a keylogger into a browser tab. The malware also contains a keyword monitor, which injects an attacker-specified keyword list into the top frame of each page, scans the HTML body for these keywords, and triggers a screenshot if it finds any. A few days later, beginning on September 2, a second China-aligned spy crew that Proofpoint tracks under the temporary group designator UNK_LateNight used BlueMoon to target multiple US aerospace companies. The phishing emails used request-for-quotation lures specific to defense industry organizations, and included links to attacker-controlled domains spoofing a variety of US aerospace companies. These websites also served the BlueMoon exploit kit and ultimately loaded a backdoor called ShadowPad, which has been shared among multiple China-aligned groups since 2019. Around this same time, on September 2, another suspected espionage group that Proofpoint tracks as UNK_DoubleCheck targeted a Vietnamese manufacturing firm with messages sent from a compromised Southeast Asian government email address. The fourth campaign began a day later, and involved suspected China-linked spy crew UNK_QuietRacket using BlueMoon to target government, consulting, and financial-sector organizations in Indonesia and Singapore. These phishing emails used lures related to Indonesian conferences, such as the Indo Startup Expo and Forum 2026 and the World Conference on Creative Economy (WCCE 2026). Proofpoint warns that BlueMoon will likely be used by both cyberspies and financially motivated attackers. “The broader dynamic revealed by this activity - rapid exploit development that leverages the open source patch-gap – is likely to recur beyond BlueMoon as this development model becomes accessible,” the team wrote. ®
As the world's largest search engine, Google is often a target of Europe's Digital Markets Act (DMA), which seeks to rein in Big Tech. The European Commission hit Google with a hefty 460 million euro ($543 million) fine in July for preferring its own services in searches for travel and shopping. Google has now made changes in accordance with the European Union's wishes, but it claims the result is a massive reduction in search quality.
If you don't live in Europe and perform a search for, say, hotels, Google will helpfully provide myriad sponsored links, booking recommendations, and price-comparison tools in its results. The problem is that this content isn't organic—Google includes links and offers contingent on its business interests. To get to the regular search results for these types of lucrative searches, you have to scroll way down the page. Companies that partner with Google can get more exposure, but the European Commission says this creates an unlevel playing field.
"To comply with DMA requirements, we're making significant changes to Search in Europe," Google's Nick Fox told Reuters. "These changes degrade the user experience for Europeans, boosting online intermediaries at the expense of local businesses and removing helpful features people rely on every day."
Data theft and extortion crews are stealing companies’ proprietary AI data and threatening to leak it if the victim organizations don’t pay a ransom, according to Google’s threat hunters. In one case that Google’s Mandiant incident response team investigated, the crooks broke into a healthcare company and exfiltrated corporate data and drug research, including AI research and a proprietary AI model. The criminals then threatened to publish the data unless the company met their extortion demand. In another breach at a company that specializes in AI media generation, attackers stole sensitive AI data including source code, prompts, skills, model scripts, and secrets before demanding a payment and threatening to dump the AI assets publicly if the ransom wasn’t paid. Google detailed these two intrusions for the first time in its most recent AI Threat Tracker, published Tuesday and shared in advance with The Register. “But it's certainly not limited to that,” John Hultquist, chief analyst at Google Threat Intelligence Group, said in an interview with The Register. Mandiant responded to several of these data-theft-and-extortion operations during the second quarter of 2026, he said. The intrusions affected companies in the technology, healthcare, pharmaceutical, and media and entertainment sectors in North America and Europe. “It’s become a really valuable target where organizations are spending a lot of money and investment, and they don't necessarily want their IP exposed to the open world, so they're willing to pay in an extortion scheme,” Hultquist said. “Criminals attacking AI systems is an area that's not received as much attention as it probably should, and as we incorporate these systems, it’s going to come with brand-new risks,” Hultquist added. “There are certainly threat actors who are ahead of others when it comes to that problem – TeamPCP has been extremely successful.” Since March, TeamPCP has pulled off several very large scale open source supply chain attacks targeting ecosystems including PyPI, npm, and Docker Hub. After compromising these open source packages and registries, TeamPCP, which Google tracks as UNC6780, typically deploys stealers to scoop up cloud and AI system credentials. “Evidence indicates that UNC6780 created a malicious GitHub Actions workflow for the company’s proprietary AI repository, and that the extortion actor exfiltrated a copy of this AI repository,” the report says. “Beyond these demonstrated tactics, UNC6780 has also implemented more than half a dozen different methods to target or exploit AI tools and open source software development practices.” While Google’s earlier AI tracker, published in February, documented attackers experimenting with agentic AI to support certain pieces of the attack chain, in the past quarter they’ve gone on to integrate agentic capabilities into multiple stages of an attack lifecycle, according to the researchers. In one example, Mandiant observed miscreants who compromised an organization’s cloud infrastructure in an autonomous, multi-agent credential-harvesting attack that took less than six hours. During that time, the agents autonomously scanned for vulnerabilities, performed real-time troubleshooting, and executed IP rotation logic without manual intervention. “Like scanning – but with a brain,” Hultquist said. In another case detailed in the report, Google Threat Intelligence observed a China-linked espionage group using Gemini to design a dynamic, automated penetration-testing framework that could reason through actions, execute tasks, and change course as needed in unpredictable environments. Google disabled the assets associated with this particular crew. “That’s where we are headed,” Hultquist said. “We're kind of in this interim place where threat actors are inserting agentic AI into certain parts of their operations, but we've not gotten to the place where they are able to sort of remove themselves entirely. We're right on the precipice of that.” ®
Google has dodged an effort to break up its ad business, but a judge said Wednesday that the company will need to adjust its business to benefit competitors.
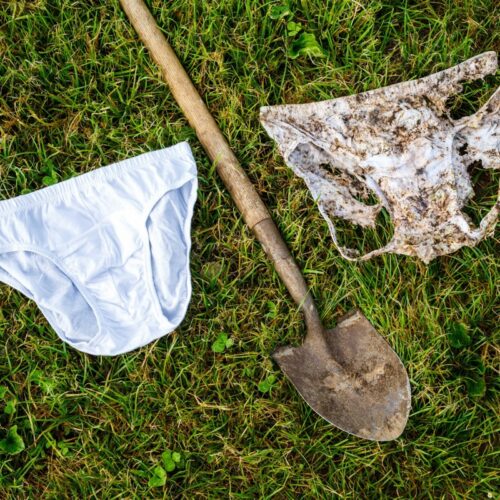
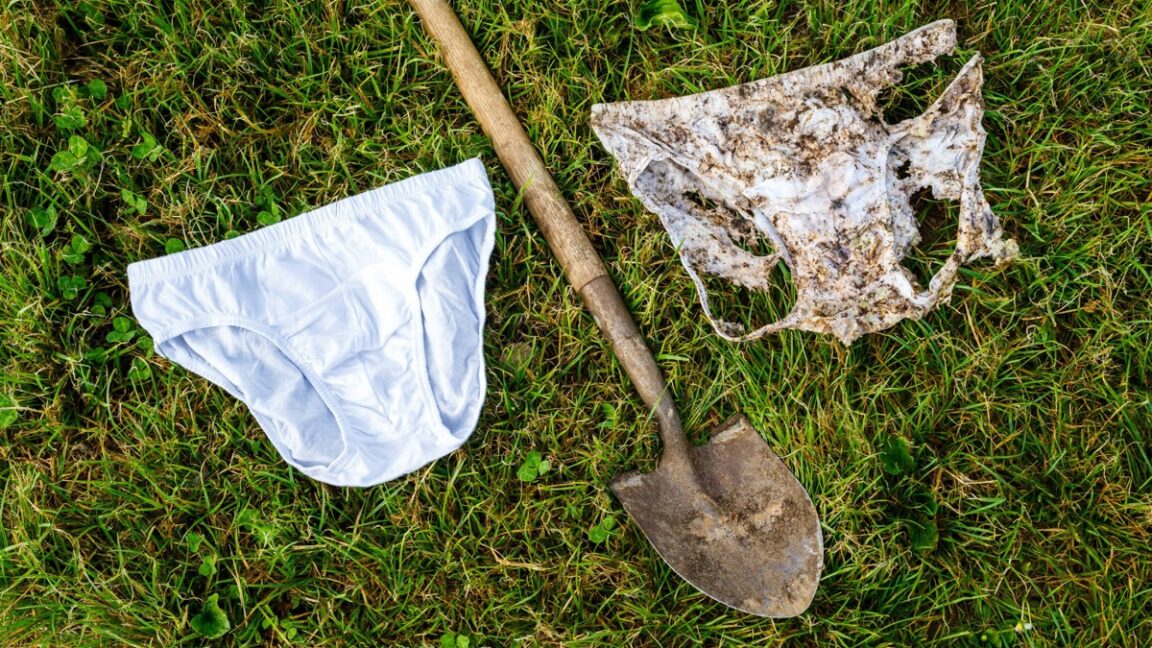
A thousand people voluntarily buried their cotton underpants for two months—not to keep the Underpants Gnomes from stealing them, but as part of a citizen science project to map out soil health in 25 countries around the world. The results of this unique experiment were reported in a new paper published in the journal Plants People Planet.
“Our results show that how soil is managed can significantly affect both soil life and soil quality,” said co-author Marcel van der Heijden, an agroecologist at the University of Zurich. “Healthy, biologically active soil is crucial for fertility, nutrient cycling and many other ecosystem services.”
Soil health is critical for agriculture and, by extension, food security, not to mention a healthy global ecosystem, but it has been declining worldwide, per the authors. One key indicator of soil health is decomposition rates of complex organic matter, breaking down stuff like leaves, wood, even cadavers into simpler organic and inorganic compounds, releasing C02 and nutrients in the process. There have been relatively few large-scale national decomposition studies involving different land use types, although smaller studies have shown that how humans use a site can significantly affect the soil's biological diversity.
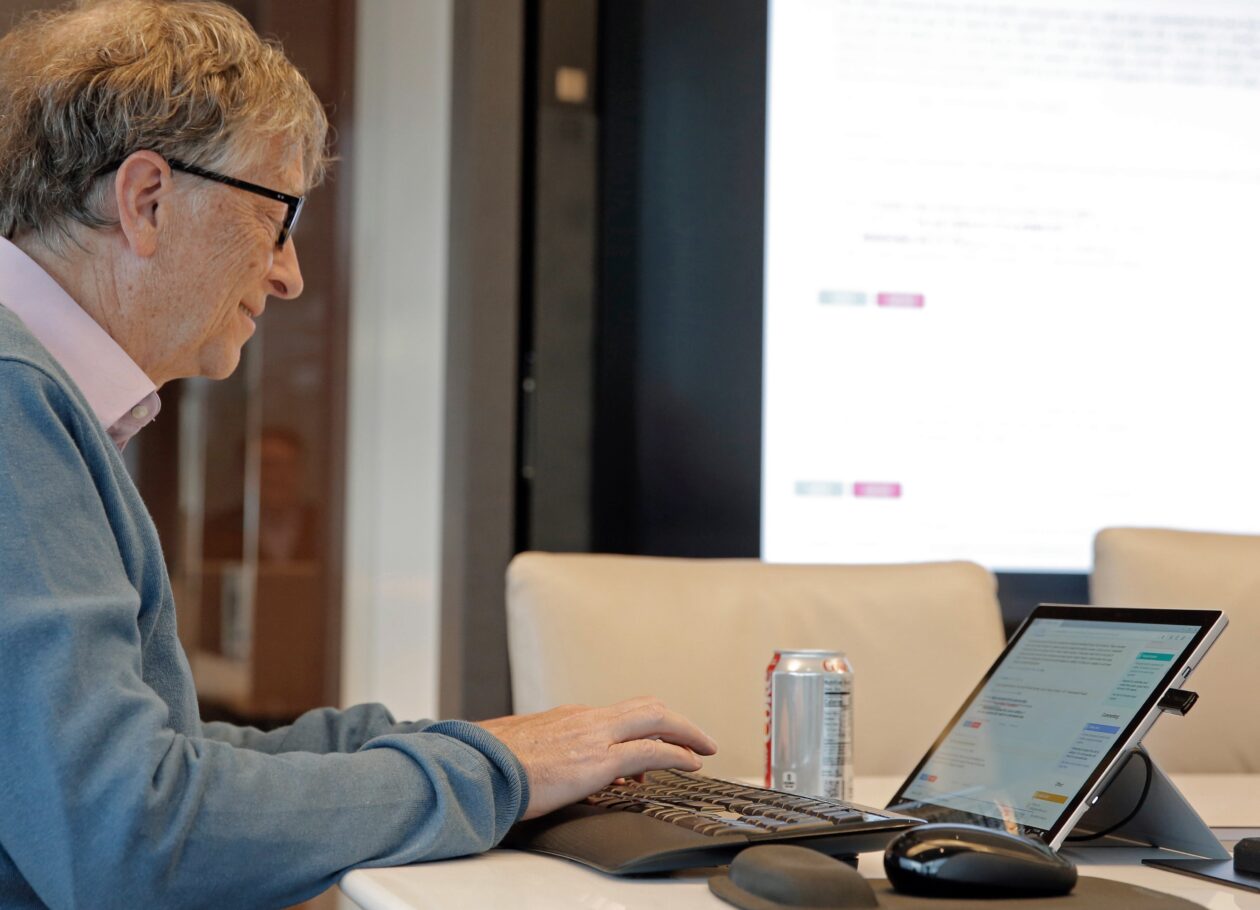
Bill Gates at the keyboard in a 2018 file photo. (Gates Notes Photo)
Bill Gates is legendary, bordering on notorious, for his late-night emails — missives to colleagues with piercing questions about Java back in the day, or malaria these days, or whatever esoteric topic he happens to seize upon at any given moment.
But increasingly, he is sending these messages to AI, not to people. He’ll bounce something off Claude, get ChatGPT to weigh in, and insert himself in the middle.
He described the pattern in an interview with GeekWire: “It’s 3 a.m., I want to understand sodium batteries. Now, there’s no reason to go to sleep. Here we go! Yeah, it’s crazy.”
If you’re a curious person, he said, “this is a mind-blowing time.”
In terms of productivity, he added, “we are in heaven.”
All of which might be predictable. This is Bill Gates, after all. Now 70 years old, he has spent more than five decades impatient for the future to arrive — making the case that innovation, on the whole, will ultimately put humanity and the world in a better place.
So here’s the surprise twist: He’s now deeply concerned about where technology is headed, how fast it’s progressing, and how little the world is doing to get ready.
In a new essay, Gates says the “turbulent AI era” has arrived, with technology threatening to erase categories of jobs, supercharge fraud and deepfakes, lower the bar for cyberattacks on critical infrastructure, make it easier to engineer a deadly new disease, let governments kill without humans involved in the decision, and fundamentally change how kids grow up.
If someone came up with a credible plan to slow the pace of AI globally, he writes, he’d likely support it. But he doesn’t expect one. The geopolitical and economic forces are too much.
He says that the world needs to take action, and offers three ideas to start:
Build new institutions, at home and globally. No existing agency was designed for a technology that touches jobs, security, health, energy and elections all at once, he writes.
Gates calls for new national bodies that can set priorities across agencies, plus a new international organization modeled on nuclear weapons inspections, aviation rules and the ozone treaties.
Set aside jobs for humans. Gates calls this “Human Reserved”: work that machines will be fully capable of doing, but that we decide to keep for people anyway. The model is a nature reserve — land where we could build roads and buildings, but choose not to, because the loss would be too great.
One example: a robot delivering the news that you have an incurable disease. “There’s no technical reason why it couldn’t,” he writes. “Yet it shouldn’t.”
The idea came in part from watching the caregivers who looked after his father through Alzheimer’s, work he describes as “irreplaceably human.”
Tax AI tokens and robots. Today a company that hires a worker pays payroll taxes, while a company that buys a robot deducts the cost. Gates says that gives employers a reason to replace people. He’s calling for a tax on AI to change the incentives and help pay for retraining.
He first floated a robot tax nine years ago, but the idea was widely dismissed. He’s still for it. He acknowledges that it isn’t economically efficient, but says that with innovation accelerating, we can afford a little inefficiency as the price of keeping people employed.
Gates is candid that he doesn’t have all the answers, particularly on the proposal for “Human Reserved” jobs. Who decides what gets reserved, and by what criteria? How do you keep companies from using robots in the jobs that are supposed to stay human?
These, he writes, “will need to be worked out in public.”
In the meantime, he’s working it out with Claude. Gates said he has talked the idea through with the chatbot, thinking through different ways to get the share of work reserved for humans up to 40%, using shorter workdays and earlier retirement to spread what’s left around.
Crossing the threshold
In the GeekWire interview, Gates said the essay came out of a specific realization: the AI industry is blowing past its own warning signs, one after another, and almost nobody is saying so out loud.
For years, he said, people in AI described certain moments as dangerous points where the industry would stop and think hard before going further: making it easier to build a bioweapon, making it easier to launch a cyberattack, building machines people become emotionally dependent on, wiping out large numbers of jobs, and losing control of the technology itself.
“We’re in the process of crossing every single one of those thresholds,” he said.
Meanwhile, nobody in the industry wants to be first to step on the brakes. “Most people you talk to will say, yeah, well, if everybody else would slow down, maybe I would, too,” he said.
Gates said one way out of that standoff is for governments to step in.
His example: any AI model capable of designing new molecules — the capability that would let someone engineer a new disease — should be monitored. The monitoring would be mandatory rather than voluntary, and it would cover free models as well as commercial ones. It would also have to be written so a company can’t copy the model elsewhere and strip the monitoring out.
“To me, that’s kind of like common sense,” he said. “But we don’t see a specific proposal to do that.”
‘The whole thing seems so empty to me’
Under an executive order signed by President Trump in June, AI companies are asked to submit their most powerful models for government testing up to 30 days before release. The order specifically bars the program from becoming a licensing or preclearance requirement. The White House finalized the framework in early August.
Gates said he doesn’t get it.
“What is the threshold that’s being examined, and what is the action taken when you cross that threshold?” he said. “The whole thing seems so empty to me.”
If the world can’t take these basic steps, he said, “I really am going to throw up my hands.”
If the process stays voluntary, with no line and no consequence for crossing it, “we’re going to look back on this as a kind of eye-of-the-storm type moment,” he said.
Asked if he had taken his proposals to the Trump administration or to other heads of state, Gates said with a bemused tone, “Well, you could tell me who at the White House I should be talking to about this.” He said he hopes the essay reaches people in Congress and in the executive branch.
He said the public argument among AI companies over whether the risks are real is beside the point, because privately the people running them already agree. “I know they’re all worried,” he said, “or all of them that I know, which is basically everybody but Elon.”
People inside AI companies who acknowledge the downsides, Gates said, get told: “Hey, you’re hurting our PR while we’re trying to raise trillions of dollars.”
Gates said he previously expected losing control of AI to be a distant problem, something to worry about “many years from now.” He’s no longer convinced that’s the case.
He referenced an Aug. 11 episode of the Dwarkesh Patel podcast featuring Ryan Greenblatt, chief scientist at the AI safety group Redwood Research. Greenblatt said that as AI systems get more capable, the people building them understand less and less about what is happening inside, and that sufficiently advanced models could end up working against their creators.
“These are people who are super expert on the thing, going, well, maybe we won’t be able to control these things,” Gates said. “I mean, what kind of risk have we chosen to run here?”
In the poorest countries, he expects AI to do more good than harm. In the countries where the Gates Foundation works, doctors, teachers and farm advisors are all in short supply. AI can help fill those gaps. The foundation will lay out that work at its Goalkeepers event next month, including an effort to make AI models work as well in African languages as they do in English.
The job losses, he added, will hit rich countries first.
It’s the first big wave of new attention on the Microsoft co-founder and Gates Foundation chair since he answered lawmakers’ questions in the Jeffrey Epstein investigation on June 10, sitting for a nearly six-hour voluntary interview with the House Oversight Committee.
Gates, who has not been accused of any wrongdoing, was asked by Axios whether he’s concerned that the Epstein issue could undercut his message. According to the site, he compared this to earlier situations when personal and professional challenges diminished his ability to speak out on key subjects: during the Microsoft antitrust trial, and his divorce from Melinda French Gates.
The AI Road Ahead
For all of this, Gates is still thinking about how technology will change human life and productivity, in many ways for the better on an individual level.
A key step, he said, will be establishing broad-based persistent memory for AI agents across contexts. For now, AI still doesn’t know you like a human assistant who’s familiar with your relationships and how you think about your time.
Gates sees the role of apps changing in the future. Instead of bouncing between different pieces of software, he said, AI will increasingly be the primary interface. “You won’t go to those applications,” he said. “You’ll just go to your personal agent.”
He also sees AI continuing to transform shopping, to an extreme: “We will get to a point where you won’t buy things yourself. You just won’t.” Telling the agent to help you buy something, “it’ll consider so many more things, and it’ll make it so much easier for you to do it.”
Asked whether he is still an optimist, Gates didn’t answer directly. “I don’t think being pessimistic is helpful,” he said.
“I do think, wow, this is sure an interesting time. I’m the guy who in my 30s thought people in their 50s or 60s didn’t understand anything.” He called it “kind of bizarre” that he would be delivering a message like this at 70.
“But I am very concerned. And honestly, when you get people one-on-one, so are they.”
For years, AI industry watchers of all stripes have been warning of a coming jobs apocalypse driven by ultra-intelligent AI systems that will be able to replicate most human tasks more cheaply. Now, newly updated research from Stanford University economists suggests AI seems to be causing significant entry-level job losses for younger workers in some fields, even as older workers appear largely unaffected so far.
The August 2026 edition of "Canaries in the Coal Mine? Six Facts about the Recent Employment Effects of Artificial Intelligence" updates and revises a paper of the same name published last year with fresh data and refined statistics. In that update, the Stanford researchers find the employment trends they identified for entry-level workers last year are persisting and expanding. Specifically, employment levels for workers ages 22 to 25 in the most "AI-exposed" occupations are now 19 percent below those of their peers in fields less exposed to AI disruption.
The Pixel 11 may look familiar, but after a week of using it, a few clever features have completely caught me by surprise. Here’s what I’m already loving about Google’s baby Pixel.
Cornell researchers built new datasets showing that early downloads and GitHub activity can predict a paper's impact years before citations ever catch up.
Coauthored with Claude Unrestricted global access to frontier AI technology is ending. The US government has taken steps to control who can use the most advanced models developed by American companies. While Claude Fable and the GPT-5.6 models are now open to all users, Anthropic and OpenAI are both complying voluntarily with a program that […]

 Login