WordPress has released version 7.1.4 to address 22 vulnerabilities, including issues related to remote code execution, stored cross-site scripting, information disclosure, and authorization weaknesses. This security update was published on October 28, 2026, and it is recommended that users upgrade immediately. The fixes encompass core functionality, including content blocks, administrative screens, the Customizer, and the […]
TRUST#GRAFT, a JavaScript-to-WordPress attack chain that never breaks WordPress authentication. Instead, it borrows the trust placed in an already logged-in administrator’s browser and uses that session to install a persistent PHP backdoor. Many administrators stay signed in to wp-admin in the same profile they use for everyday browsing. That habit gives attackers a usable foothold. […]
UPD 23.10.2026: added Kaspersky SIEM rules and events for developing custom detection rules or conducting threat hunting.
UPD 22.10.2026: added a description of how the Kaspersky Managed Detection and Response service detects the described malicious activity.
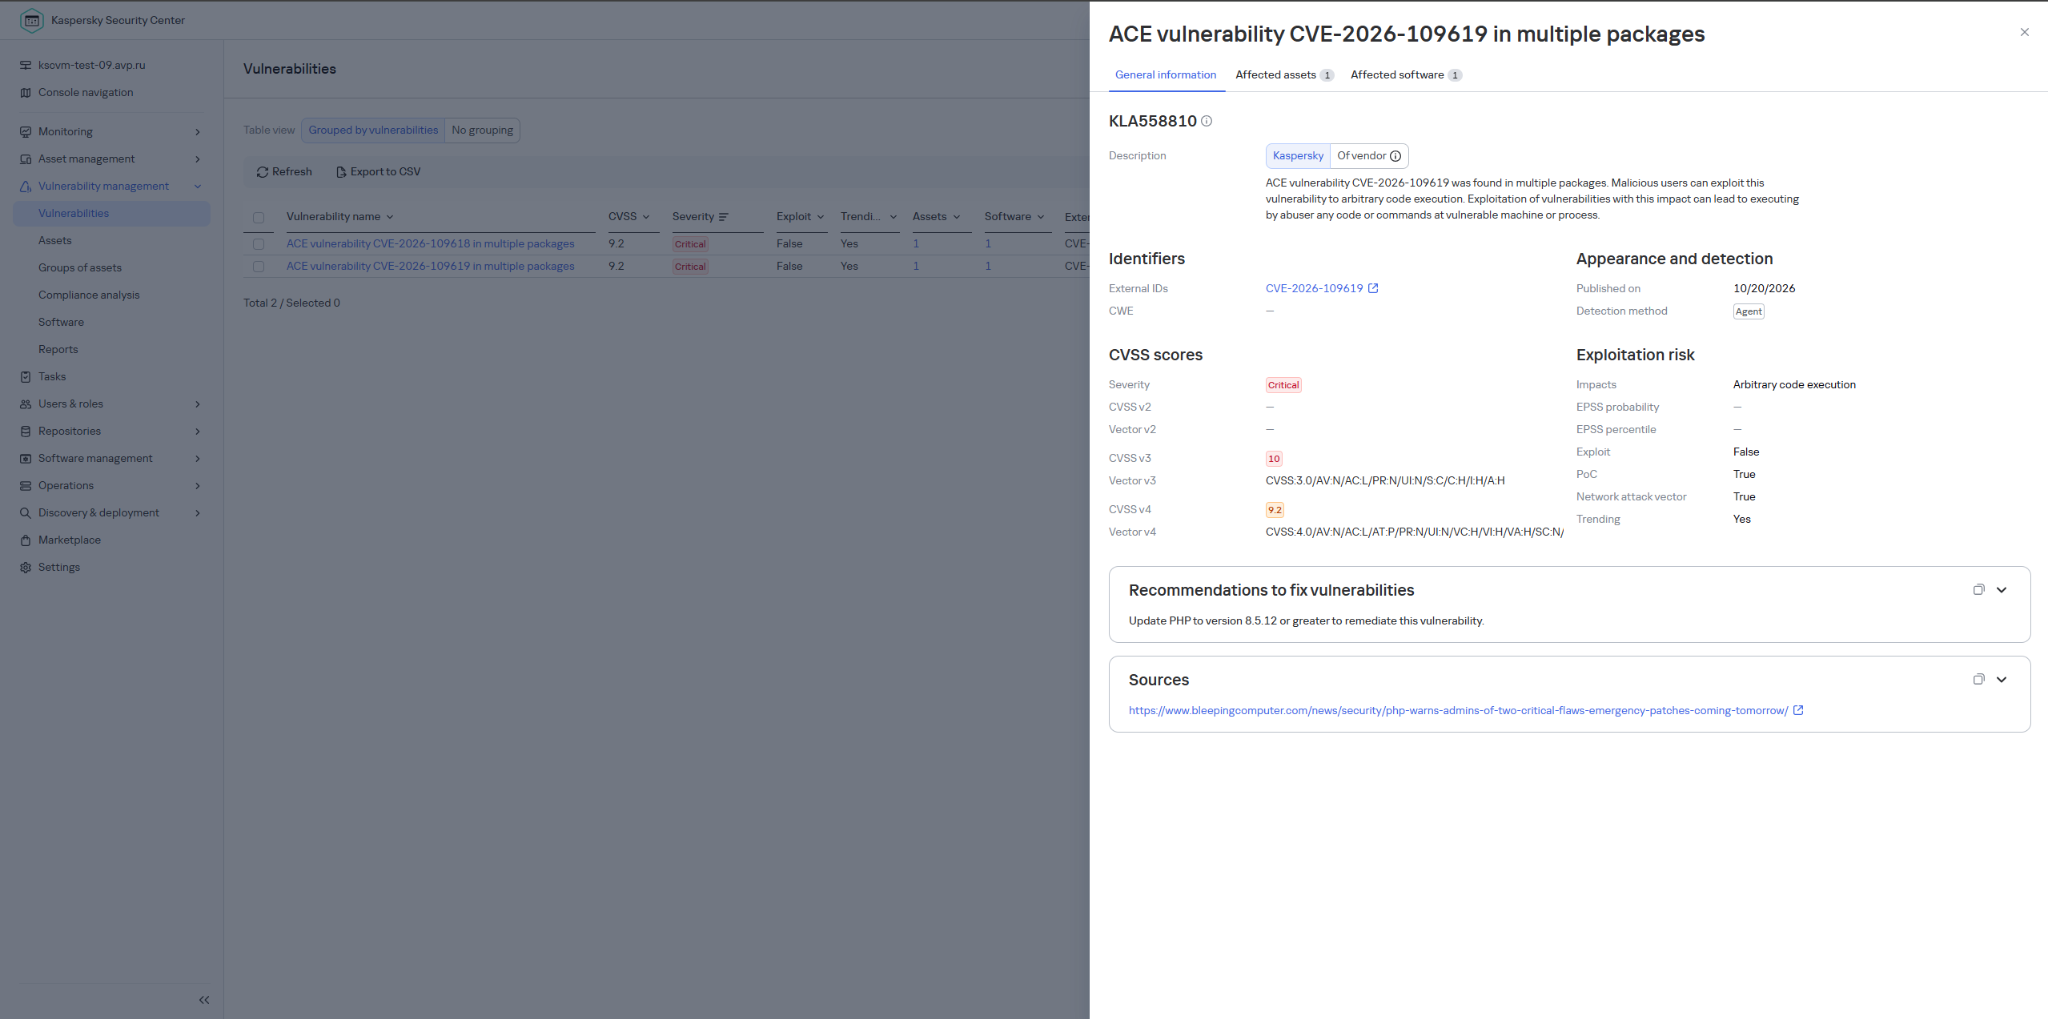
UPD 22.10.2026: added a description of how Kaspersky Vulnerability Management detects vulnerable versions of PHP.
Vulnerability overview
On October 20, 2026, the PHP security team published a preliminary notice regarding an upcoming emergency release that addresses two critical vulnerabilities (both rated 9.2 on the CVSS scale). The patches were released on Wednesday, October 21, 2026, at 14:00 UTC.
The release was expedited after information about the vulnerabilities was leaked to the public before the scheduled embargo was lifted. In a post on Hacker News, a user reported two RCE vulnerabilities in PHP, allegedly affecting all versions starting with PHP 5.4.0.
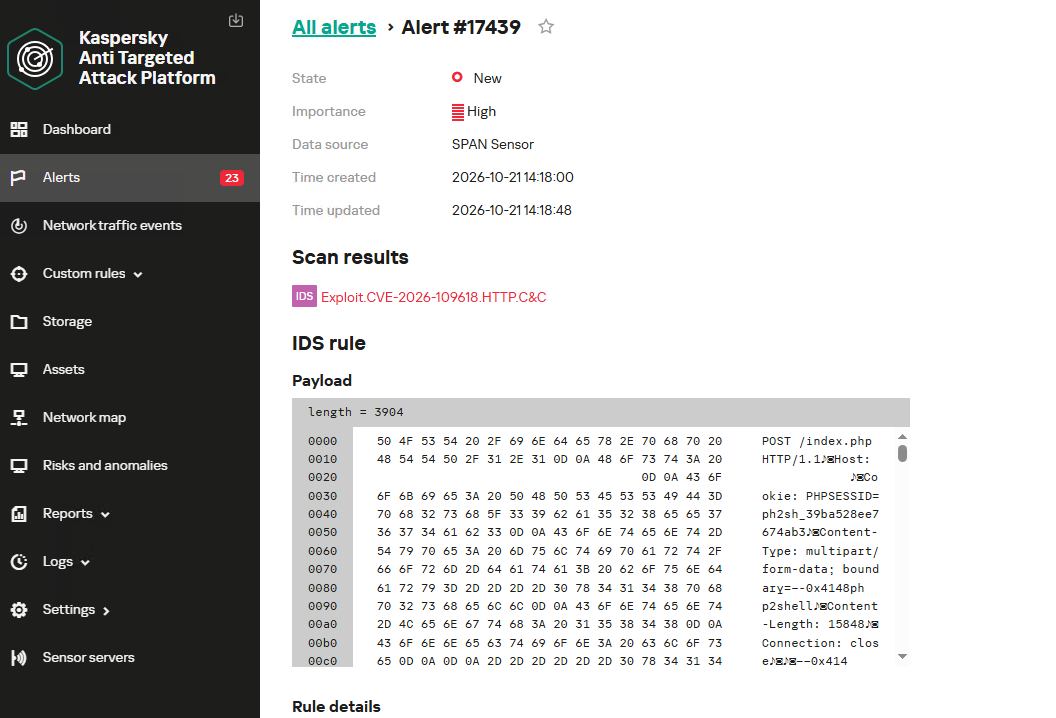
The vulnerabilities in question are CVE-2026-109618 and CVE-2026-109619. Shortly after the post appeared, researchers confirmed the existence of the vulnerabilities. Along with the leak of details, an exploit unofficially named PHP2Shell appeared online. In the leaked demo video, the exploit is shown in action on web servers running WordPress, MediaWiki, phpBB, Magento, Joomla, Laravel, Symfony, Drupal, and WHMCS — platforms that power many modern websites. The authenticity of the demonstration and the exact behavior of the exploit had not been independently verified at the time of publication.
According to the researcher who published the PoC, the vulnerabilities are related to the handling of the multipart/form-data MIME type in conjunction with the session upload progress mechanism (session.upload_progress) in the PHP core and fall under the categories of use-after-free and memory corruption. This means that the flaws cannot be fixed via application code, and the only fix is to update PHP on the server. The attack requires no authentication: an attacker with network access to a PHP application can execute arbitrary code with the privileges of the PHP process without needing to authenticate. Security advisories issued by the PHP team on October 21 confirm this information.
The vulnerabilities affect PHP versions 5, 7, and 8. As of this publication, branches 8.2 through 8.5 are supported. Older branches, including PHP 8.1, 8.0, 7.x, and 5.x, have reached the end of their lifecycle; however, due to the critical severity of the vulnerabilities, backported patches have also been released for versions 7.4, 8.0, and 8.1.
Sansec experts estimate that widespread exploitation could begin within 15 minutes of the update’s release. We strongly recommend that administrators responsible for publicly accessible PHP web servers take the following steps before the patch is available:
Take an inventory of all PHP-based systems in your infrastructure (such as web servers, control panels, and third-party software).
Disable upload-progress: set session.upload_progress.enabled = Off using the php_admin_flag in PHP-FPM pools.
Block multipart requests on nginx and Apache servers.
Consider temporarily isolating PHP applications that connect to the Internet until fixes are released.
Be ready to install the patch immediately upon its release.
Plan to migrate servers running unsupported versions (8.1 and earlier) to the latest PHP branch.
Detection by Kaspersky solutions
Kaspersky solutions detect the described malicious activity at various stages of the attack. Possible detection scenarios are listed below.
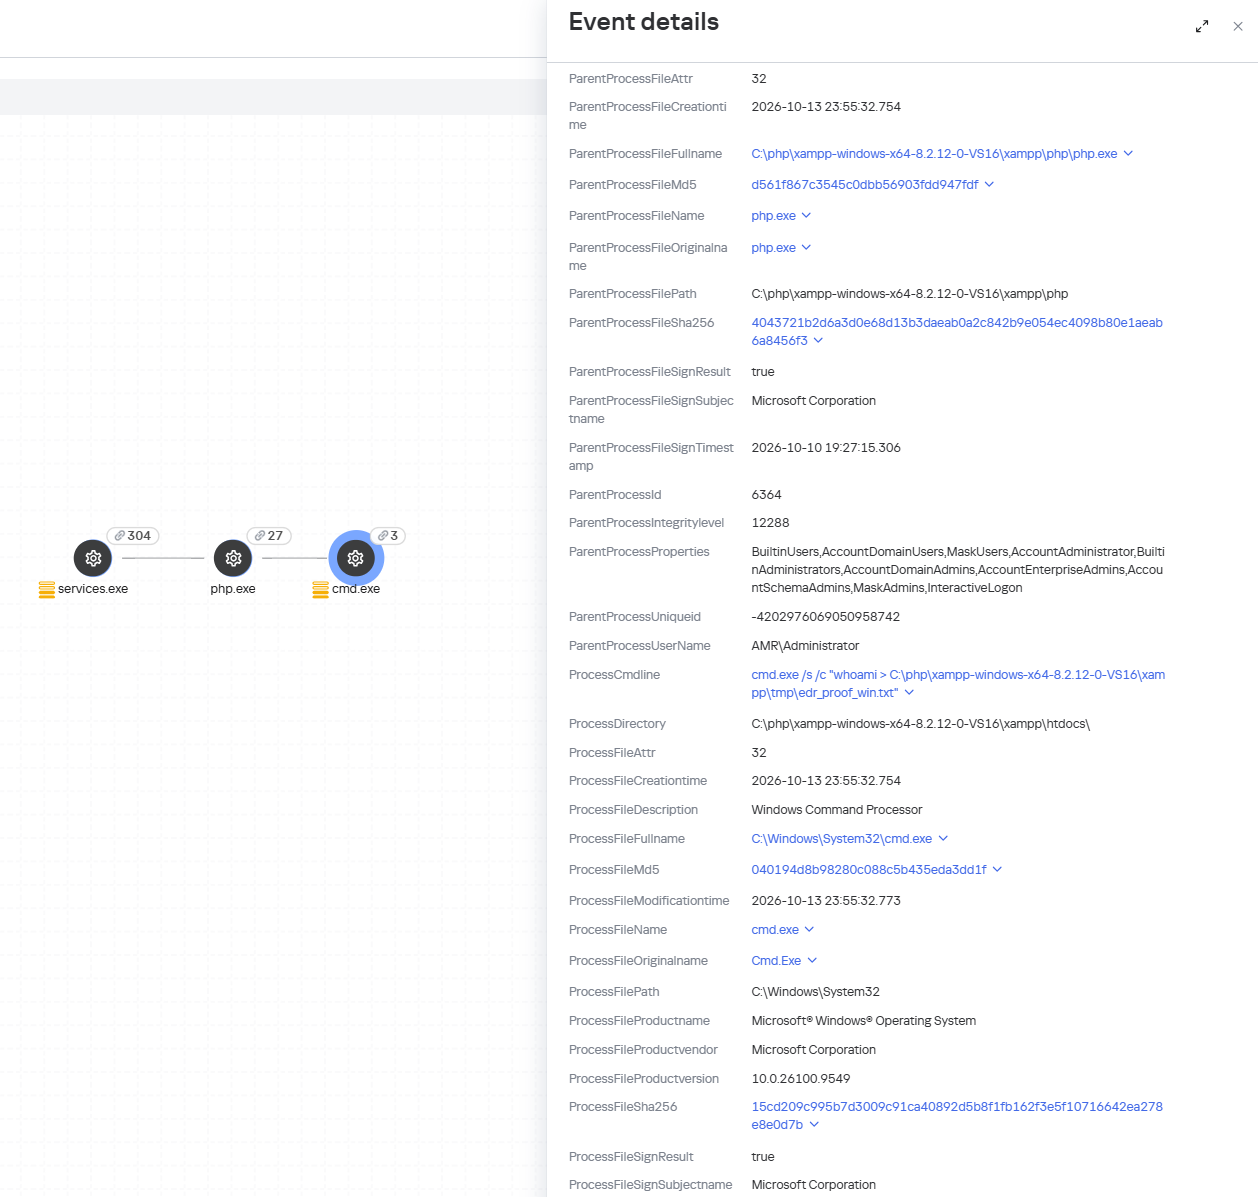
When an attempt is made to exploit these RCE vulnerabilities, Kaspersky Endpoint Detection and Response promptly alerts the user to suspicious actions performed in the context of a web server, on both Linux and Windows machines. This activity is detected by the following rules:
Spawning of suspicious processes by the web server;
Creation of suspicious executable files in the web application directory;
Creation of suspicious scripts in the web application directory;
Creation of files with uncommon extensions in the web application directory;
Execution of reconnaissance commands by the web server process;
Execution of persistence commands by the web server process;
Delivery and launch of web shells on the web server.
Moreover, MDR detects other malicious activity not directly related to remote code execution.
To protect companies that use our Kaspersky SIEM system, the product repository includes rules that help detect the following malicious activity.
Execution of suspicious executable files by web server processes on Windows and Linux machines:
R300_04_Windows shell started by a web application
R152_08_A running Linux shell process has a suspicious parent process
Execution of reconnaissance commands by the web server process:
R286_05_Possible web-shell (Linux)
We also recommend monitoring the creation of scripts or executable files in the web server directory when developing your own detection rules or conducting threat hunting:
((DeviceEventClassID = '4663' AND DeviceCustomString1 ilike 'WriteData') OR DeviceEventClassID = '11')
AND match(FileName,'(?i).*\.(php|asp|aspx|ashx|jsp|js|jar|jse|dll|exe|bat|ps1|vbs|wsf|wsh|msi|msp|hta|cpl)$')
AND match(DestinationProcessName,'(?i).*(php-cgi|nginx|httpd|w3wp)\.exe')
Name = 'openat' AND has(SA.Nametype, 'CREATE')
AND
length(arrayFilter(x -> match(x, '(public_html|var/www|usr/local/apache2|usr/local/httpd|var/apache|srv/www|home/httpd/html|srv/http|usr/share/nginx/html|var/lib/pgsql/data|usr/local/mysql/data|var/lib/mysql|var/vsftpd|etc/bind|var/named)'), SA.FileName))>1
AND
length(arrayFilter(x -> match(x, '\.(aspx|asp|asmx|asax|ashx|jspx|jsp|js|phpt|php|phtml|pht|cfm|shtml|htaccess|fcgi|cgi|pl|py|sh)'), SA.FileName))>1
Attackers exploited compromised UpdraftCentral connection keys to send trusted remote-management commands to WordPress sites, ultimately installing malicious plugins that could provide unauthorized access to these websites. This incident followed unauthorized access to TeamUpdraft’s website on October 17-18, 2026. The company suspects attackers accessed its customer database, which contained UpdraftCentral connection keys and customer account information. […]
Rank Math has reported a security incident involving malware distributed through Rank Math PRO version 3.0.123. They warn that WordPress websites using this compromised plugin are at risk if administrators activated it. The company has removed the affected files and released a clean version, 3.0.124. Rank Math PRO Compromised The incident impacts a limited number […]
Hackers can compromise vulnerable WordPress websites without stealing passwords by chaining two security flaws in the platform’s core. Disclosed in July 2026, the chain involves CVE-2026-63030 and CVE-2026-60137. Unlike attacks dependent on vulnerable extensions, WP2Shell affects default WordPress installations without requiring a third-party plugin. Public exploit code and observed exploitation have made unpatched deployments an […]

 Login