❌

Normal view

There are new articles available, click to refresh the page.
Today — 29 October 2026Main stream

2026 Hackaday Supercon: All the Speakers!

29 October 2026 at 13:00

We announced our first round of speakers, and then the workshops, and we were going to dribble out updates on the rest of the speakers as they came in, but then time slipped away from us. So we are left here announcing a veritable cornucopia of twenty wonderful talks that you absolutely won’t want to miss.

Supercon is just about a week away, and there are still a few tickets left, so grab them now before it’s too late.

And the talks are just half the fun. Between food, merriment, a killer badge with the biggest e-paper display that you’ve ever seen, and all the assorted shenanigans, it’s the highlight of our hacking year. Come join us!
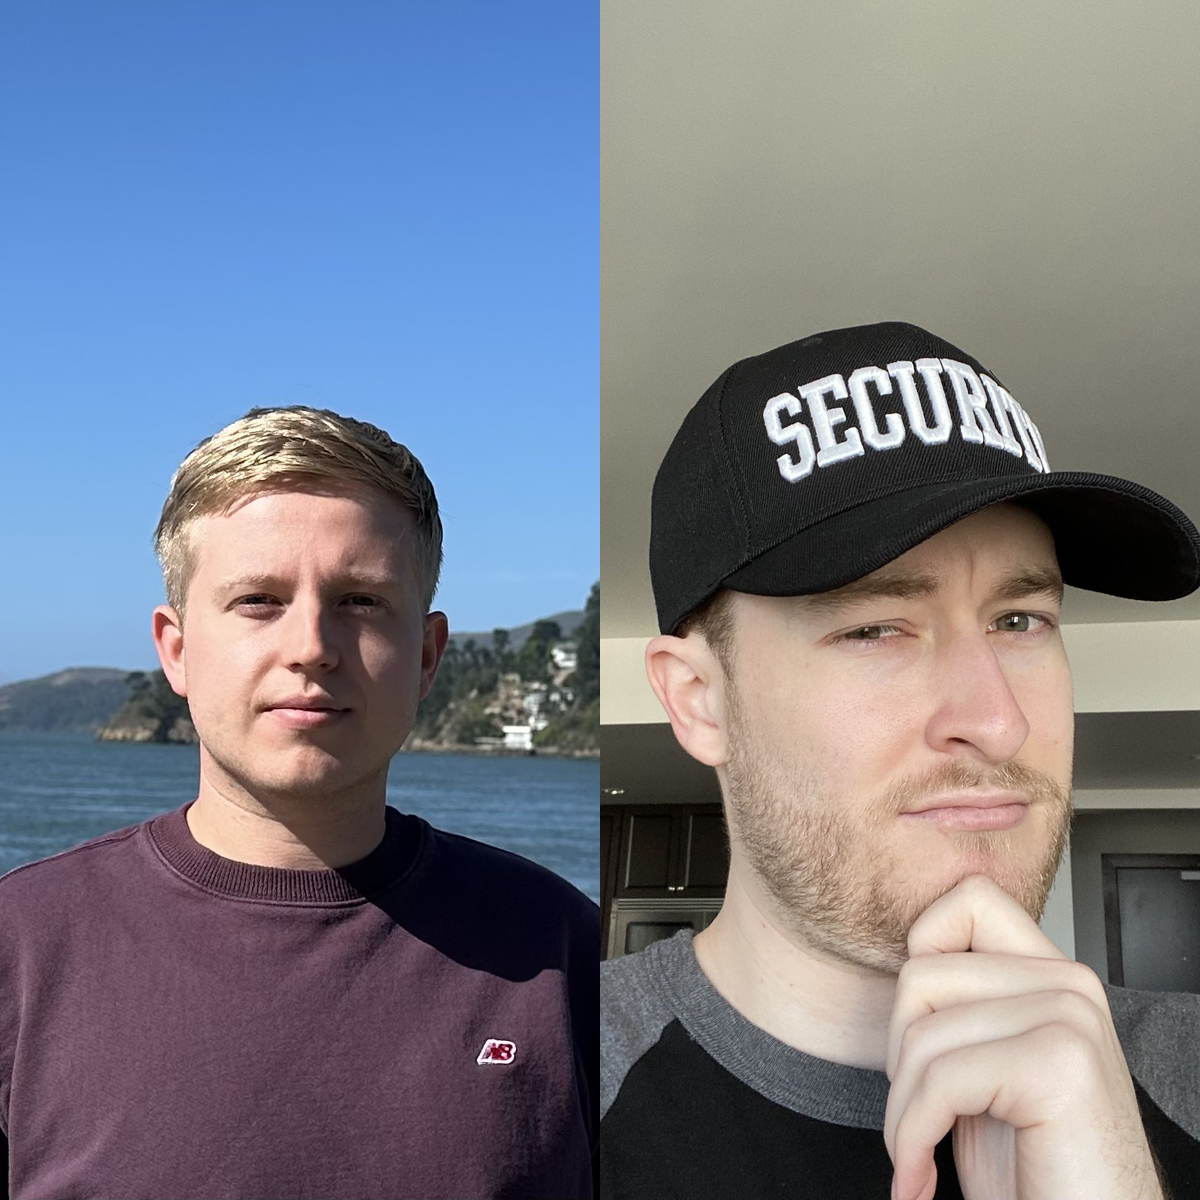
Adam Batori and Kevin Colley
Rare Circuits: How we Used and Abused a $1 MCU to create the Aerospace Village Radio SAO

Software-Defined Radios have evolved from once being exquisite lab equipment to now an affordable tool accessible to hobbyists, thanks in large part to projects like HackRF and the $40 RTL-SDR. That got us thinking, are there any existing RF chips we could repurpose to make an even simpler and lower-cost SDR?

This talk dives into how we reverse-engineered the black box of the $1 TI SimpleLink Wireless MCU’s RF subsystem, and jailbroke it to unlock additional RF modes and custom protocols. We will demonstrate how we are able to receive analog AM, FM, and even raw IQ samples on this supposedly “digital RF” MCU, and developed our own tools to gain further insight into how the radio operates. Putting these capabilities together, we recount how we leveraged all of this to create the “Charlie” radio SAO for Aerospace Village and made it receive analog airband, stereo FM, UAT, and more! We also demonstrate how we made our unassuming SSD1306 OLED produce 4-level grayscale with perfect VSync, and the silicon-level hacking it took to pull it off!
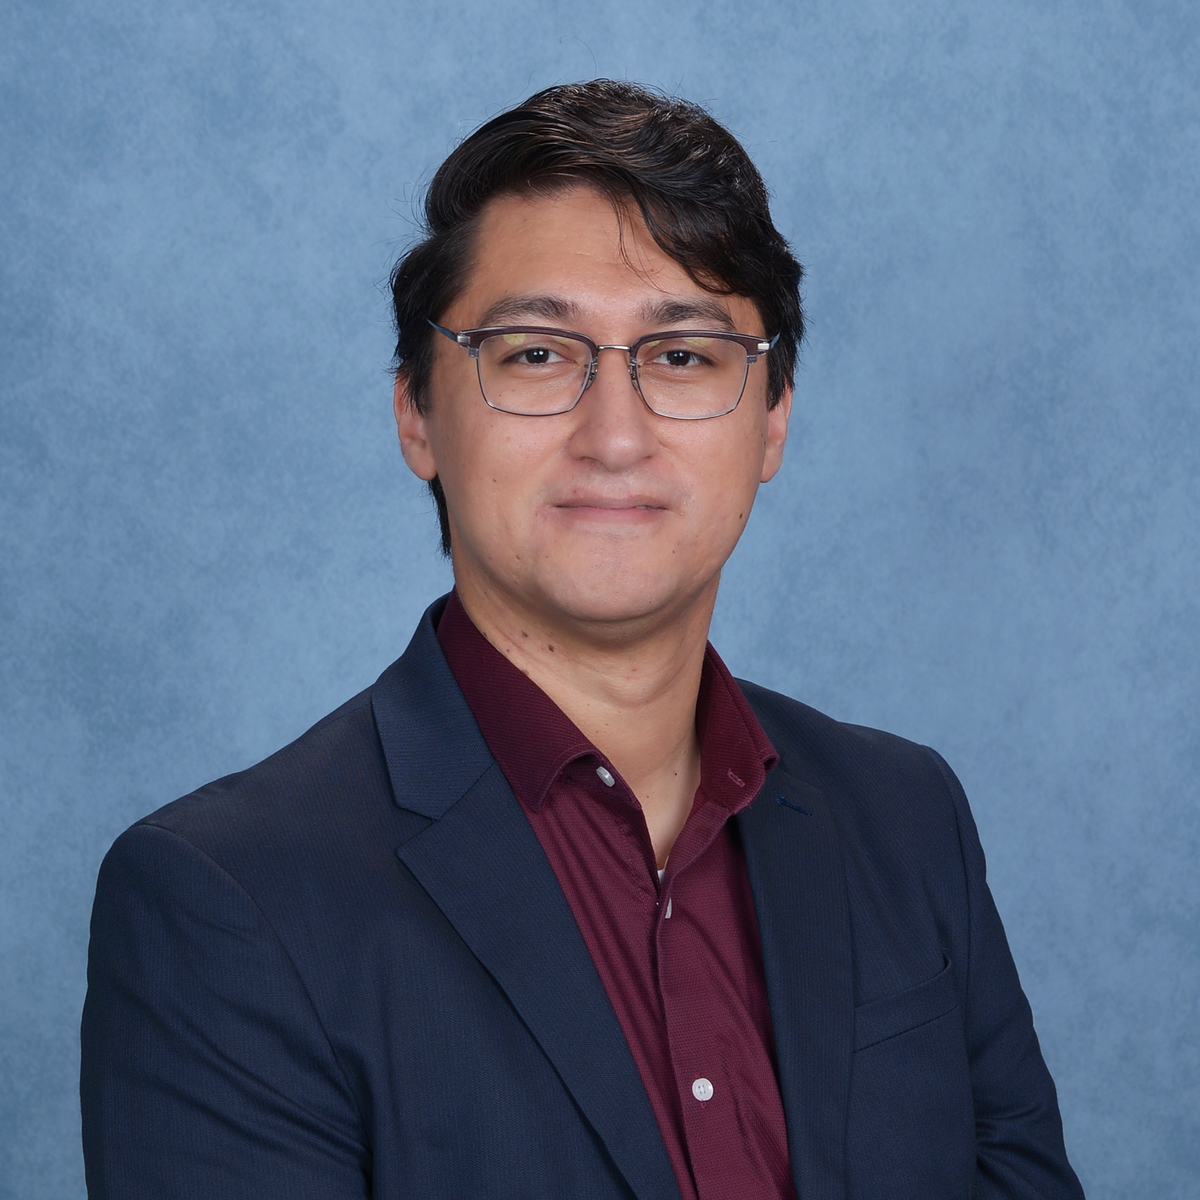
Adriel Bustamante
Rover Tracks: A Retrospective on the Open Source Rover and What’s Next

The Open Source Rover has taken on a new life ever since the v2 release three years ago. In that time, I’ve joined the community of rover builders and become a maintainer on the project myself, doing outreach at community events and development work on the rover where I can.

In the time since I’ve been a maintainer, I’ve learned quite a few lessons about the practical and philosophical aspects of engineering for a project like this. I hope to be able to share some of what I’ve learned (changes I’ve had to make to my rover, improvements that can be made, what it’s like to be “the rover guy” at Maker Faire), and what comes next for both my own rover and the project at large.
Alley Cat
Designing Devices: Not Just PCBs in Boxes

PCBs and their enclosures are often designed as separate things, but the best results come from designing them together. This talk covers practical considerations to design boards with the final device in mind, account for the differences between CAD models and real hardware, and create enclosures specifically for FDM 3D printing. We’ll look at real-world tolerances, connector placement, production variance, clearances, overhangs, extrusion widths, layer heights, and other small details that can make the difference between a design that looks right in CAD and one that actually fits together.
Ames Evans
Blinkenlights That Remember: The Unsigned Firmware on your PC’s RAM

The RGB glow on your sick gaming PC comes from somewhere, and that somewhere is a microcontroller controlled by a program and a kernel module that the manufacturer ships. But if your vendor’s app can push a new lighting style to that microcontroller, why not a whole new firmware update? Is there anything actually stopping arbitrary firmware from being written to your RAM’s RGB controller?

I went looking for answers with Ghidra and my RAM’s onboard controller will happily accept and run firmware of my choosing, and I can make it do basically whatever I want. I will demonstrate a few of these possibilities live.
Andrew Denio and Danner Cronise
How to Rob a Bank Without Really Trying

Have you ever wondered how exploding bank dye packs work? During this talk, you will learn all about how banks utilize embedded electronics to either track or paint bank robbers. Using equipment purchased from auctions, MakeItHackin and Danner Cronise will cover the electronics hidden in stacks of cash, the various equipment inside banks to trigger a remote detonation, and how these electronics have evolved over the decades.

Can these protective measures be foiled… find out during this exclusive Supercon talk.
Ashleigh Pomerant
No Refresh Button: The Case For (and Against) Putting a Browser on Your Device

A user interface running in Chrome on a Raspberry Pi looks like any other web app from the outside. Underneath, most of the usual assumptions start to fall apart. This talk covers what actually changes when you ship on a device instead of a server: hardware owns the state, WebSockets replace REST because screen updates are often triggered by hardware sensors, and both memory and CPU limits become a real constraint.

It also covers why the trade is usually still worth making. The upside is options: rendering and layout are handled for you, there’s a library or a pattern for almost anything you need, and a large community to ask when something breaks. See this all come together in a device that uses RFID for input.
GC
EDA for Everyone: PCB Design in the Agentic Era

What if ANYONE could ship hardware? What if that what-if wasn’t a what-if? Find out how the next wave of open-source design software puts the power to create in your hands. (Editor’s note: this talk contains parody and hacks in about equal measure.)
Eric Hall
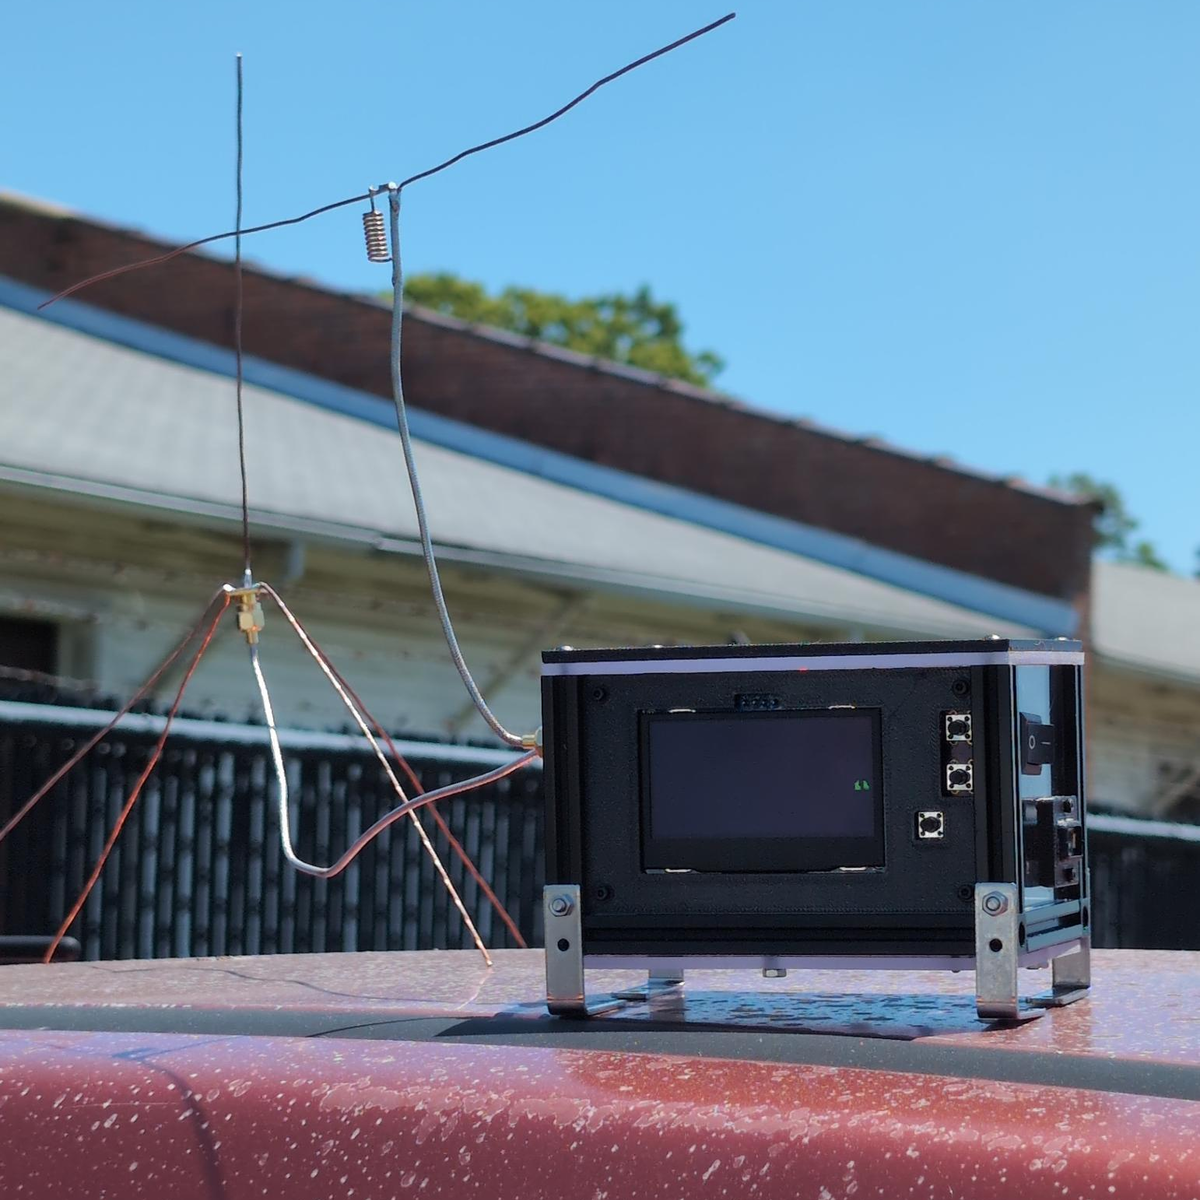
LoRa and Beyond

This talk explores building a small ground station for receiving LoRa satellite communications with affordable parts and custom made antennas. This project was built from the ground up without using existing frameworks like tinyGS.
Baird Bankovic
Achieving Quality Photoresist Uniformity on Asymmetric Substrates

The most popular method for fabricating nano-scale structures is with photolithography. The first step in any photolithography process is to coat a thin, uniform coating of photoresist on the substrate. Typically this is spun on, however if the substrate is not rotationally symmetric, strong edge effects can hurt thickness uniformity. I present a few different methods for increasing uniformity of photoresist coating. In particular increased uniformity on the silicon substrates (50mm x 100mm x 30mm) from 12% to 1%, which is close to industry standard uniformity on wafers. I will discuss various other photoresist coating techniques for oblong substrates as well.
Henry Amador
Beyond the Breadboard: Bringing PCB Fabrication into the Makerspace

This talk explores an in-house PCB fabrication workflow developed for a university makerspace that uses a fiber laser to selectively ablate copper from PCB blanks.I’ll share how the process was developed, what was learned along the way, and how access to rapid PCB fabrication has expanded what students can design, build, and iterate on during their engineering courses.
Joe Needleman and Dex
HM and I (Down the Rabbithole of Human Machine Interfacing)

This talk is for anyone who loves tactile inputs and physical controls, whether they’re on the big screen or in real life. We will be talking about human-machine interfaces (HMI for short), have evolved, and how fictional and real systems have shaped each other along the way. We’ll walk through three of our own designs, each with a distinct purpose. Every one is a real build, so we’ll cover the whole design, from hardware planning, firmware, and even the software that connects a computer to the machine interface. Finally, we’ll look at the future of HMI design and the growing role Agent-to-Agent (A2A) AI now plays in designing control systems.
John Zhang
How many neurons does it take to pump a swing?

Back in 2020, I became interested in applying reinforcement learning to teach a robot how to pump a swing, inspired by the Cook’s paper “It takes two neurons to ride a bike” and YouTube videos of gymnastic robots by Hinametetu. It’s an elegant toy problem with beautiful nonlinear dynamics and it turns out you can get away with just one neuron using a Q-learning approach. Now, in the blistering, chaotic summer of AI, it’s seems like an appropriate time to revisit this idea and ask what we can learn from this simple toy example for building physical intelligence.
Kaveh Pezeshki
The Hardware of Superconducting Quantum Computing

Superconducting quantum systems represent a new frontier for quantum simulation and computation. In this talk, I will discuss the technologies and hardware behind these systems – what is a transmon qubit? how do we control and measure its state? As the field is so new, much of what we use is adapted from technologies hardware hackers are familiar with. This talk will emphasize how we adapt and use common equipment for quantum measurement and control.
 

Kerry Scharfglass
How to Make and Have Feelings

Touch is an integral part of our lives, but how does it work? It’s easy to say “your skin senses pressure” but it can also tell you about things like the grain of a piece of wood, or that an animal’s fur is soft. The biomechanics of touch are a fascinating and complex topic without wide understanding. In this talk we will peel the covers back by discussing science’s current understanding of the collection of systems the human body uses to feel, and how it can infer things like texture from those rudimentary signals.

Expect to learn about how amazing our biological systems are, and how you can leverage that in different ways give people different haptic experiences.
Lily Gabriel
Spinning E-textile Yarns

This talk will be about e-textile materials and how to make your own when you can’t find commercially available options. E-textile materials include conductive thread, yarn, fabric, and wool roving, but these are hard to find from reliable sources (especially if you are a hobbyist maker and not looking to buy in bulk.) Methods I will be covering in the talk include hand-plying, drop spindle plying, core spinning, and supercoil. Hand plying is taking a single strand and introducing additional twist into it, then folding it in half and letting it twist back on itself. Drop spindle plying is similar, but using a weighted spindle to add more twist in less time. Core spinning is taking an overspun single and wrapping it with wool roving in the opposite direction. Supercoil is similar to core spinning, but instead of wool roving, another overspun single is twisted around a core.
Ryan Mast
The Perfect BLEnd: Reverse Engineering a Bluetooth-Controlled Smart Blender for Better Smoothies

Have you ever gone to make a smoothie, only to have the blades spin fruitlessly while the fruit sticks just out of reach on the walls of the cup? I’ve wrestled with a “smart” blender over this and other issues on many occasions, often resorting to tossing the single serving cup to dislodge stubborn pieces of fruit. Or perhaps you have another smart device that one day stops working because the vendor decided to stop updating the app for newer phones.

In this talk, I’ll share how I learned to reverse engineer BLE devices in order to control the exact settings used by the blender, including initial failures and how I overcame them — along with quickly creating an alternative for controlling the blender when the app stopped working after an iOS update. And in the end, we’ll create a custom blending profile for the perfect blend!
Sage Cadence
How to build things that people care about in the age of AI

In today’s age of abundant information, anyone with a computer can build and anyone with an opinion can make it known. How do you filter out the noise to build something that people actually care about? Learn how to combine the mental frameworks of engineer and a storyteller, cutting through the clutter and creating things that truly matter.
Sarah(í) Alvarez
Finding a Loop: Creative Uses for e-Waste

Artists, makers, and engineers must begin to explore creative, non-industrial approaches to managing e-waste. This talk chronicles experimentation with a niche source of e-waste – one record label’s backlog of unsellable compact discs. Learn about the mid-2010’s enthusiasm for recycled CD filament, the benefits of salvaged metal foil, and embracing the chaos of creative re-use.
Sher Amir Dullat
StageReady: a standalone, portable device for natural, studio grade vocal pitch correction in real time

We all love singing, but at some point we also realize that perhaps the performance sounds better inside our own heads than outside it. If there were a tool to bridge this gap, it would surely appeal to just about everyone. That tool does exist, it’s real-time pitch correction. So why are we all not carrying our own personalized pitch corrector with us?

Currently, real-time pitch correction requires studio grade hardware, but we create a real-time auto-tuner that can be personalized to a singer’s voice while pitch-correcting under real-time latency constraints on an edge device.
It does so by separating the voice into two parts: the resonant character that makes each person sound like themselves, and the underlying vocal source that sets the note. It corrects only the pitch, while a neural network running on chip’s AI accelerator rebuilds a natural, breathy vocal source at the corrected pitch.
Stephen Farnsworth
Secrets of Ghidra: Reverse Engineering Proprietary Smart Home Sensors

After digging some old sensors from a security system I had out of a bin to integrate with Home Assistant, I realized several of them used a proprietary protocol used by a system I no longer used. Fortunately, a fellow enthusiast and tinkerer had just recently discovered you could dump the firmware of the humble TI MSP430 based device. That’s when I decided to dust off Ghidra and try to figure out what this device was doing.

Along the way, I’ve learned some great lessons on how to use the tool Ghidra to decompile monolithic microcontroller firmware. In this presentation I’ll share my journey with the tips that I wish I known before I started. For example, to understand the firmware, you need to pull resources from anywhere you can and look at the device as a whole to understand the inner workings. As a result, I was able to crack the protocol and give new life to hundreds of dollars of sensors that would still be collecting dust in a bin.

[If you read this far, you probably want tickets. Just sayin’.]
Before yesterdayMain stream

Hackaday Links: October 25, 2026

By: Tom Nardi
25 October 2026 at 19:00
Hackaday Links Column Banner

Some disappointing, but perhaps not entirely unsurprising news this week out of Denmark — after announcing last year that they would transition away from Microsoft’s proprietary software, the realities of making it work seem to have caught the government off guard. The word is that a trial program immediately ran into problems when government employees that had been given Collabora tried to collaborate with their peers running Office, and has since been quietly abandoned.

Although there’s probably a joke to be made about different parts of the government not knowing what the other ones are talking about, the reality is that if one group of staffers can’t reliably access the data being produced by another, that’s a pretty big problem. Of course, had they simply asked us nerds, we could have advised them that these sort of issues are inevitable if you don’t fully commit to the effort.

Had the entire government moved to the Open Document Format (ODF) at once they would have avoided the issue, at least when it came to newly created documents, but obviously that’s a considerably larger undertaking than installing Collabora or OpenOffice on a few dozen machines and calling it a day. There’s no word yet on how this stumble will impact Denmark’s larger effort to free themselves of proprietary software, but we’d hazard a guess it’s not a great sign. Hopefully things go better for the Dutch.

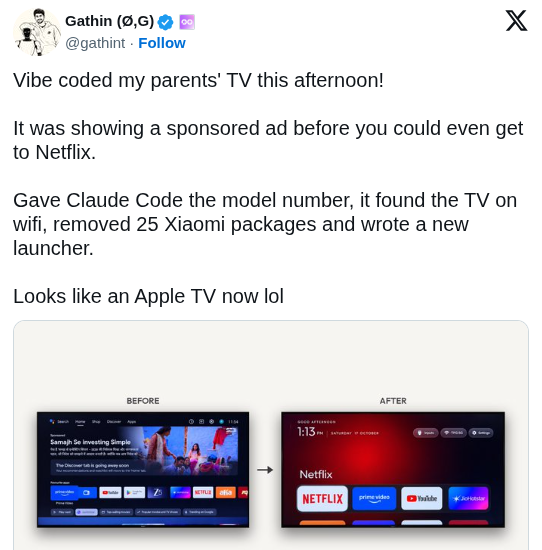
Speaking of users trying to improve their personal software situation, The Verge has an interesting article on a recent trend of frustrated users pointing AI tools like Claude at their smart TVs, with a few success stories posted to social media showing off interfaces that have been stripped of ads or replaced with something else entirely. It’s compelling stuff for anyone who’s unhappy with their current smart TV experience, but the whole thing isn’t quite as technically impressive as it might seem on the surface.

As the TV’s in question are running Android, all the AI tools need to do is connect to them over Android Debug Bridge (ADB) and uninstall any offending packages that might be providing ads, and similarly creating a customized launcher interface is a matter of spinning up an Android app and installing it over the network. The results may look like arcane magic to the uninitiated, so we appreciate The Verge pointing out that it’s all pretty basic stuff for anyone familiar with Android development.

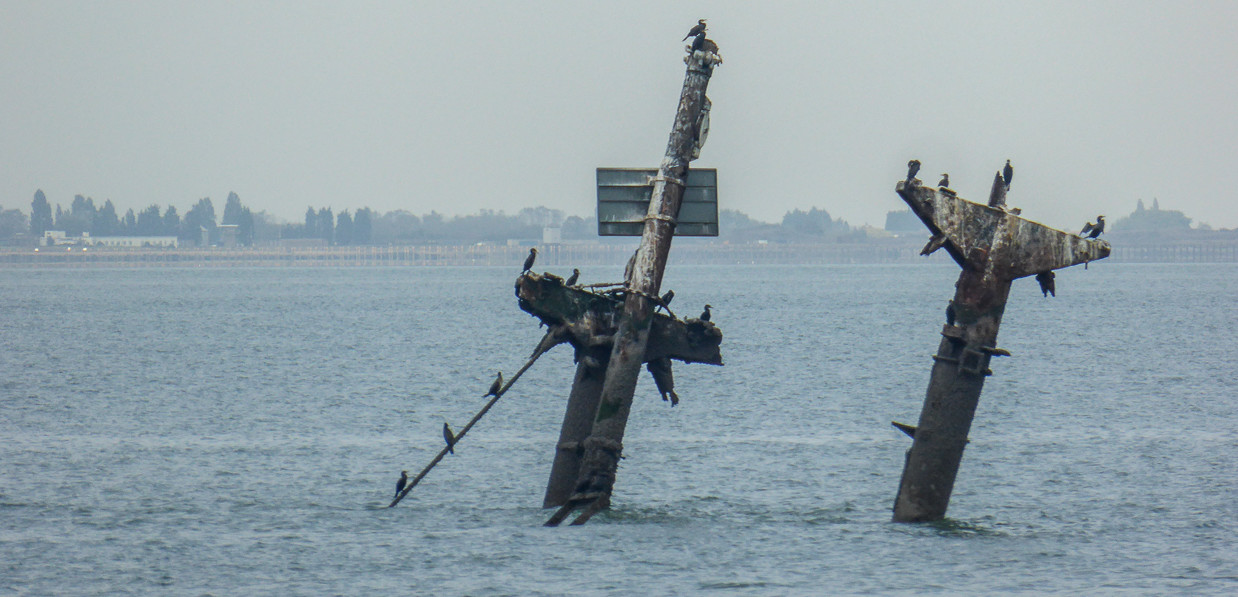
On the subject of extracting unwanted components, a delicate operation to remove the masts of the sunken WWII cargo ship SS Richard Montgomery was completed successfully earlier this week off the coast of Sheerness, England. To those unfamiliar with this particular vessel that might not sound like a big deal, but when you’re dealing with a wreck holding an estimated 1,400 metric tons of explosives that have been deteriorating since 1944, even approaching the area needs careful planning and coordination.

Masts of the SS Richard Montgomery in 2014. Image Credit: Christine Matthews

There was a concern that the masts and their supporting structures were on the verge of collapsing into the hull of the wreck, which experts warned could potentially trigger an explosion large enough to endanger life and property. Actually removing the explosives from the ship itself will be a far larger undertaking, but at least for the time being, removing the masts has helped stabilize the situation.

Finally, if you’re looking to learn about something a little more local than a potentially explosive situation in Sheerness (apologies to anyone in Sheerness), check out Local Wikipedia. Created by [Ed Jefferson], the site lets you filter Wikipedia pages by their distance from your location or whatever other landmark you wish. By default it shows results that are within 1.5 miles, but if you don’t have anything too exciting within range it will start opening up the radius to pull in more results.


See something interesting that you think would be a good fit for our weekly Links column? Drop us a line, we’d love to hear about it.

Making for Others

24 October 2026 at 10:00

One of the nicest things about the Hackaday community, and the open-source hardware community at large, is the incredible generosity of one hacker to another. But it’s not purely altruism – it’s also just a great feeling to be able to share your work with other folks who understand what it represents and how to use it.

I’m looking at my workbench right now. Because I’ve been testing out the Supercon badge prototype, there is a small pile of SAOs to the right. SAOs are the perfect size for giving out to fellow hackers, because they can be small, inexpensive, and yet still embody a ton of your creativity. [Tom]’s marvelous Ode to the SAO, even opens with this as one of the main benefits, alongside teaching you “full-stack” PCB production at small scale; they are cheap enough that you can give them away. Of course, you end up getting as many or more than you give, so it’s not just the pure joy of giving at work in the SAO scene.

On my left, I have a couple dev boards made by fellow hackers. One is a clone of the Raspberry Pi Pico that’s made by the high-school students of Hack Club, and the other is [CNLohr]’s ch32v003fun board and esp32s2-funprog programmer. I needed to test out a quick microcontroller application, and having a few dev boards on hand is always useful. Because I know the people who made these boards, I tend to reach for these over their commercial alternatives. Romantic? Maybe. But they were given to me by friends.

And of course the badge prototype is sitting in the middle of all this, and that’s how I really know about the joy of giving away your designs to fellow hackers. We at Hackaday are in the incredibly fortunate position of being able to dream up a new and fun badge every year, and give it out to hundreds of fellow hackers. Heck, this year, we’re making 1,000. I say “fortunate” because we don’t have to pay for them ourselves, but rather our Supercon sponsors help pick up the bill, and that means we can make stuff that’s far cooler than our budgets would otherwise allow.

So to everyone in the SAO scene, may you give away your designs to people who really appreciate them. For the folks who have built tools for other hackers to use, you should know that the recipients probably reach for your boards over their bland commercial alternatives. And for all of you coming to Supercon in two weeks, we hope you dig the badge. It has maybe become a bit of a cliché these days, but you should know that it’s made with love.

This article is part of the Hackaday.com newsletter, delivered every seven days for each of the last 200+ weeks. It also includes our favorite articles from the last seven days that you can see on the web version of the newsletter. Want this type of article to hit your inbox every Friday morning? You should sign up!

Hackaday Podcast Episode 392: Microscopes, Drones, and Other DIY Things

23 October 2026 at 12:00

Hackaday Editors Elliot Williams and Al Williams met to review the week in Hackaday. Turns out, it was a week for tiny things, cybersecurity, nostalgia, and projects that would have been nearly impossible for the average hacker not that long ago. But first, you can hear a little about the upcoming Supercon badge and the trials of importing and exporting parts for the badges.

How many props does your drone have? [Joshua] has one. Want to fabricate semiconductors at home? Do you have a microwave? What about using NFC in your next project? There’s all that and more in this episode.

The quick hacks include a request from NASA for ideas (and, yes, there is prize money) and slide rule tricks, among other things. For the can’t miss articles, the cybersecurity weekly got some appreciation and Al took a trip down memory lane at the Altair 8800 he always wanted.

Check out the links if you want to follow along, and as always, tell us what you think about this episode in the comments, or drop us a line on the mailbag.

Download in DRM-free macroscopic MP3.

Where to Follow Hackaday Podcast

Episode 392 Show Notes:

News:

Mailbag:

  • Thanks to [Silver Dog Australia] for some new sting sounds for the podcast. Send us your sound, questions, or thoughts on the podcast for next week’s mailbag: mailbag@hackaday.com

Interesting Hacks of the Week:

Quick Hacks:

Can’t-Miss Articles:

This Week in Security: Record Patch Tuesday, PHP’s Bad Time, The Oldest Vuln, AI Armies, and More

23 October 2026 at 10:00

It’s no longer a proper month without Microsoft breaking its own record for security fixes, and October’s Patch Tuesday was no exception. Brian Krebs brings the roundup: more than 1,400 vulnerabilities fixed in a single batch, dwarfing September’s record of nearly 1,000, which itself was about ten times the normal monthly load. According to Tenable, Microsoft has now passed 4,000 CVEs for the year with two months still to go.

Only one of the fixes is for a vulnerability already being exploited in the wild: CVE-2026-96951, a security feature bypass in the Windows Shell affecting Windows 10, 11, and some Server versions. A .NET Framework bypass, CVE-2026-108398, was publicly disclosed before the patch, giving attackers a head start, and with modern AI tooling, it seems like not much of a head start is needed. At least 78 of the bugs are rated critical, and most of those allow remote code execution with little or no user interaction. Windows 10 holdouts can relax a little: Microsoft quietly extended free updates through October 2027.  Given the pace of exploitation, this is probably the only way to prevent an Internet-scale meltdown.

Microsoft credits LLM-driven bug hunting for the volume, which leaves the poor admins who have to test and deploy all of this in an unenviable spot. Fortra’s analysis shows that only 26 Microsoft vulnerabilities have landed in the CISA KEV catalog of actively exploited bugs so far this year, so start there. For the rest, the SANS Internet Storm Center and Cisco Talos have the usual breakdowns by severity. Or, you know, just patch everything and hope for the best, which is roughly what everyone does anyhow.

The CA private key is… 4

Originally I was calling this the “big one” for the week, but this week that just keeps on giving. The private keys for eight eMudhra intermediate certificates have been compromised, and the way they were compromised is going to be a security talk punchline for years.  Remember the Debian SSL and SSH key debacle?  Of that scale.

Some background first. When your browser connects to a website over HTTPS, the site presents a certificate saying “I am example.com”, signed by a Certificate Authority (CA). Your browser and OS ship with a list of trusted root CAs, but roots are too valuable to use day to day, so they sign intermediate certificates, and the intermediates sign the actual website certificates. Whoever holds an intermediate’s private key can mint a certificate for any website, and every client that trusts the root will believe it. The whole system depends on those keys staying secret, and on them being generated properly in the first place.

eMudhra, an Indian CA which sells certificates under the emSign brand, had six TLS intermediates and two code-signing intermediates chaining to the emSign ECC Root CA – G3, which is trusted by Chrome and Apple, and Mozilla. A researcher identified only as Wayne proved the keys were compromised by signing the message “We have a problem here – Wayne” with each of them and sending it to the root programs.

How did Wayne get the keys? Flüpke posted one on Mastodon, and the secret value for the “EM OV TLS CA – G3C” key is… 4. Not four followed by 380 bits of randomness: the integer four. A reply quickly brute-forced the rest, and they’re all equally tiny: 56, 230, 237, 115, 155, 156, and 66. The keys were “incorrectly generated by the CA”, and anyone could recover them from the public certificates, which has been true since they were created in April 2025.

The browsers moved fast. According to The Hacker News, Chrome pushed a block within two hours of the report, and Mozilla blocked the certificates in under three, pulled the root from NSS, and shipped Firefox updates (CVE-2026-113470) for anyone with automatic updates disabled. There are no Certificate Transparency logs of rogue certificates, so modern browsers were never at risk. Everything that isn’t a browser is going to be the real problem and the extremely long tail of this fault: plenty of software never checks for revoked certificates and keeps trusting these keys until its bundled root list is updated.

Go hard-coded the eight bad keys into its standard library (CVE-2026-111943), but as Penligent points out, that only protects Go programs once they’re rebuilt with the new release. Python, Rust, Java, Node.js, curl, and most Linux distributions have updated root bundles, and the we-have-a-problem.com site has a full list, a checker, and manual workarounds for macOS, whose built-in curl and git don’t check revocation. There are also fixes for Linux, Windows, and the BSDs. Update everything, then go rebuild everything you compiled yourself. And then wonder how you’re going to update appliances, IoT devices, cameras, and everything else that fetches code over HTTPS or SSL.

php2shell: PHP gets owned by running out of memory

PHP, the language behind a significant percentage of the web had a rough week. WordPress, Drupal, Magento, phpMyAdmin, and just about every hosting control panel, major ecommerce sites, home project blogs, and even Hackaday itself was potentially impacted. Details of two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, leaked onto Hacker News a day ahead of the embargo, and Huntress covers the scramble that followed as PHP rushed its release out early. Now that patches are available, Ryan Austin of Calif has published the full writeup, demonstrating pre-authentication remote code execution against important apps on default configurations, in PHP versions back to 5.4.0. That’s over a decade of PHP.

The trick is an old one, first found by Stefan Esser back in 2004. PHP enforces a memory limit for each request, and when a request exceeds it, PHP stops immediately with a fatal error. If that happens in the middle of native code updating some internal structure, the structure is left half-built, and the cleanup code that runs afterward trusts it anyhow. That’s a classic “use-after-free” style bug, where the program uses memory that’s already been released or was never properly set up, and those are frequently exploitable. Calif found ways to reliably push a request over the memory limit at exactly the right moment (deeply nested empty file uploads turn out to balloon into hundreds of megabytes of internal tables, while staying under PHP’s upload size limits), and three different places where the interruption leaves a dangerous mess. Austin found the first bug with a generally available LLM, but only because he knew PHP’s twenty-year history of memory-limit bugs well enough to point it in the right direction.

Amazon reports that its honeypots caught a php2shell exploitation attempt on October 17th, four days before the embargo lifted, and that it’s now being broadly exploited. Their advice is worth repeating: for critical bugs on internet-facing systems, measure your patch window in hours, not weeks, and start investigating from the earliest exploitation date, not the disclosure date. If you can’t patch right now, Calif suggests disabling session.upload_progress and removing the memory limit, which comes with its own obvious problems.

One word of caution: alongside the legitimate writeups, there are many self-published “corrected findings” and “proof-of-concept” posts that can’t seem to decide whether their own exploit works, while offering a downloadable “weaponized” bundle. A leaked-bug panic is the perfect time to hand anxious admins a zip file. Read the real advisories, and don’t run random proof-of-concept bundles.

A Sixteen-year-old forever-day in Broadcom WiFi

Quentin Kaiser has the long-form writeup of his Hexacon talk on a bug in Broadcom’s WiFi stack, present since at least 2010, which gives an attacker a root shell on a router from across the street.  So called “parking lot” attacks that can happen from someone not even on your property have long been the boogeymen of WiFi security, and it’s been a little bit since we’ve gotten a new one.

The bug lives in WPS, WiFi Protected Setup: the “push the button on your router and then on your printer” pairing system that was supposed to save people from typing long WiFi passwords. WPS has a long and spotty security history, and this bug can be triggered over the air without knowing the network password, and without completing a WPS pairing. Kaiser’s demos show him pulling the WiFi password straight out of a router’s settings and sending it back over WiFi, and getting a fully interactive remote shell carried entirely over WiFi frames. No Internet connection required.

The really grim part is the patch history. Broadcom quietly released an incomplete fix in 2018, then suggested vendors switch to the open-source hostapd instead. For the older eCos-based chipsets that’s effectively never going to happen, which makes it a permanent “forever-day”. Broadcom refused to assign a CVE, and because Broadcom is its own CVE authority, CERT/CC closed Kaiser’s case the same day it was opened.

As of disclosure, the cable and DSL gateways he tested from three of Belgium’s four major ISPs were still vulnerable, and his napkin math puts it at over a million and a half devices in Belgium alone. Broadcom chips are, of course, sold everywhere. If you’re running ISP-provided hardware, there isn’t much you can do about the firmware. Turning off WPS can’t hurt if your router allows it, although Kaiser doesn’t say whether that blocks the attack. Disabling the gateway’s own WiFi and running your own access point that you can actually update is the safer bet.

GitLab regex bug reaches back twelve years

GitLab has released fixes for CVE-2026-110264, a maximum-severity CVSS 10.0 bug allowing unauthenticated attackers to run code on self-hosted GitLab servers. The flaw is an integer overflow when compiling a specially crafted regular expression in Onigmo, the Ruby regex engine which GitLab bundles into its own packages, so it affects every version back to GitLab 7.0 in 2014.

This is the fourth regex engine code execution bug from the same researcher in about a month (after CVE-2026-97229, CVE-2026-93577, and CVE-2026-89078), and comes with a nasty gotcha: the new fixed versions are one release past the October 12th fix, so if you diligently patched nine days ago, you’re vulnerable again. GitLab hasn’t said what’s needed to trigger the bug, so there’s no configuration workaround. If you’re running GitLab at home or in the shop, patch, and budget for some downtime while the database migrations run.

Node.js Brotli bug

Node.js shipped security updates for the 22, 24, and 26 branches, headlined by CVE-2026-111497, an out-of-bounds write in the bundled Brotli decompression library. Vercel’s advisory notes that researchers have demonstrated both memory leaks and command execution.

Node doesn’t decompress Brotli data on its own, but plenty of applications and libraries do, whether on incoming requests or on responses fetched from other servers. Vercel deployed firewall rules for traffic coming into its own platform, but no firewall can protect your code from a malicious response it goes and fetches itself. Node 20 is end-of-life and won’t be fixed. As a bonus, the same releases carry the eMudhra certificate distrust, so that’s two reasons to go update.

Header accordions and HTTP/3

HTTP/3 is the newest version of the protocol behind the web, running over QUIC (a UDP-based transport) instead of TCP. To save bandwidth, it compresses request headers using a scheme called QPACK: common headers can be sent as a one-byte reference into a table instead of the full text. Compression is great for bandwidth, but any time a small input can turn into a big output, there’s a risk of a “decompression bomb”.  Similar tricks resulted in “zip bombs” in the 2000s, and what’s old is new again.

FoxIO found exactly that in seven of the ten HTTP/3 implementations they tested. One approach packs about 160,000 unique short headers into a single 1MB request; another stores one 4KB header and then references it thousands of times, a 4000-to-1 amplification. The HTTP/3 spec already says how to limit the decoded size, but implementations got it wrong in every possible way: checking only the compressed size, decompressing everything before checking, ignoring the per-header overhead, or reading the limit setting and then never enforcing it.

Fixed so far are quic-go (CVE-2025-64702), which is used by Caddy, Traefik, and Cloudflare’s tunnels; Cloudflare’s quiche (CVE-2026-12523); lsquic 4.9.0; and even Wireshark (CVE-2025-13945), whose QPACK decoder crashed during testing. Bun, the hyperium h3 Rust crate, and aioquic/mitmproxy remain unpatched. Bun gets special mention for an integer overflow that turns a single 516KB request into a permanent 100% CPU infinite loop. The lesson applies to any compression format: limit the decompressed size as you go, not just the bytes on the wire.

Metamorphic macOS ransomware

Patrick Wardle of Objective-See digs into Heartbreaker, macOS ransomware written in Rust that has sat on VirusTotal since May 2025, undetected by every antivirus engine.

Most antivirus detection relies on signatures: a hash or byte pattern identifying a known-bad file. Metamorphic malware tries to dodge signatures by rewriting itself so every copy looks different while behaving the same. Heartbreaker takes a delightfully brute-force approach: it carries its own Rust source code inside the binary, and after running, it shuffles variable names, adds junk functions, installs a Rust compiler if one isn’t present, recompiles itself, and replaces itself with the new build. It is about as subtle as a brick through a window.

As ransomware it’s not very scary. It only encrypts the Downloads folder, and uses the same hard-coded key for every victim, so Wardle simply wrote a decryptor. The rebuilding also depends on a GitHub library which has since disappeared, so it mostly fails anyhow. Wardle uses it to demonstrate his free RansomWhere? tool, which ignores signatures completely and instead watches for an untrusted process rapidly writing files that look encrypted (using a bit of entropy math). The malware can change its hash all day long, but to ransom anything it still has to encrypt the files, and that’s much harder to disguise.

UpdraftPlus vendor breached

TeamUpdraft, the company behind the very popular UpdraftPlus WordPress backup plugin, disclosed a breach of their customer database over the weekend. Names, emails, addresses, hashed passwords, and two-factor authentication settings were taken, and more worryingly, the connection keys for UpdraftCentral, their cloud dashboard for managing many WordPress sites at once. UpdraftPlus previously made an appearance back in June, when a vulnerability in the plugin was used in the Awesome Motive supply chain attack.

Those UpdraftCentral keys can send commands to every connected site, which turns one vendor breach into a remote control for potentially thousands of customer websites. TeamUpdraft has released UpdraftPlus 1.26.12 and 2.26.12, which automatically disconnect the old keys. If you or anyone you know manages WordPress sites through UpdraftCentral, log in to each site directly, update the plugin, and check for unexpected admin accounts and plugins (including the easy-to-miss “Must-Use” plugins tab).

Spyware delivered by ad network

Citizen Lab has published research showing that the Israeli ad-tech company Discover-Tech helped deliver spyware through ordinary online ads, targeting at least 45 devices at the news outlet Al Jazeera in 2024 and 2025. Citizen Lab attributes the spyware to Candiru, a commercial spyware vendor.

When you load a web page with ads, the ad slot is typically auctioned off in real time to the highest bidder, based on a profile of who you seem to be. This “programmatic advertising” system is, by design, a mechanism for running third-party content on a very specific person’s device. It’s easy to see why that’s attractive to a spyware vendor. According to Citizen Lab, Discover-Tech’s platform could profile users and infect a device just by displaying an ad, no click required. CPJ reports that the company’s ads reached nearly 200,000 websites and apps, and researchers at Confiant found them on government networks including the US Department of Defense, NATO, and the UN.

Malicious ads are nothing new, but this is the first public evidence of an ad platform being used for targeted, zero-click spyware delivery. “Don’t click on ads” has always been good advice. An ad blocker isn’t just a quality-of-life improvement; it’s attack surface reduction.

Ransomware negotiators on the wrong side

Last week we covered a ransomware “recovery” CEO charged with secretly paying ransoms while billing customers for decryption. This week, Brian Krebs reports that investigators chasing ShinyHunters (the group behind the FBI hack) have identified executives at two ransomware negotiation firms with unusually friendly relationships with the gang. Chats seized when Dutch police arrested a suspected ShinyHunters member reportedly show negotiators who knew about new victims before the victims themselves did. One Canadian executive has already been arrested, and investigators believe an executive at an unnamed, prestigious US consulting firm helped run the gang’s extortion website.

It’s not the first time: the DOJ sentenced Florida negotiator Angelo Martino to 70 months in July for feeding his own clients’ negotiating positions to the BlackCat ransomware gang, and for helping deploy ransomware against even more victims. The government seized $10 million in assets from him, including a luxury fishing boat and, for reasons unknown, a food truck.

Part of the problem is structural. Some negotiation firms charge a percentage of the ransom paid, which gives the “negotiator” every incentive to pay, and pay big. Firms which refuse to facilitate payments often just get swapped out by the insurance company for ones that will. Meanwhile, ShinyHunters is reportedly furious with Coveware, an incident response firm, for telling victims not to pay, which is probably the best endorsement Coveware could ask for.

An army of AI agents

The Verge reports that security firm Norforge found an attacker using a swarm of mostly autonomous AI agents to break into more than 100 websites, including sites belonging to John Deere, SharkNinja, and Cummins. The agents ran on Cairn, an open-source “general-purpose problem-solving engine”: you give it a starting point and a goal, and the agents work toward it while documenting their progress. That documentation is how they were caught: the attacker’s Cairn instance was exposed to the Internet, along with about 20 others that appear malicious.

According to Reuters, the attacker described their preferred intrusion tactics in fewer than 100 Chinese characters, and each successful breach took about 23 hours. The victims say the impacted sites were standalone support pages, and Cairn’s author insists it was “never a ‘hacking tool'”. Many tools can be double-edged, but the effort balance here is hard to ignore: a short prompt and a day of waiting on one side, and defenders who have to close every hole on the other.

Staples hacked to fund a gift cards

404 Media pieced together, from an unsealed search warrant, that a Chinese organized crime ring hacked Staples in 2023 and issued more than 15,000 gift cards worth over $5 million. Staples’ internal customer support system was supposed to be reachable only from inside the company, but wasn’t. The attackers requested “heap dumps”, a debugging feature which captures everything an application has in memory, and pulled out the active login sessions of customer service reps. With those, they simply logged in as the reps and issued gift cards.  A similar trick was used in a hack of payment data from Target years ago, where attackers leveraged access through the air conditioner control network into the cash register network, and then dumped credit cards directly from RAM as they were processed.

If you’ve ever wondered why debugging endpoints left exposed in production show up in every penetration test report, this is why. The gift cards were then laundered the old-fashioned way: crews of shoppers hitting Target stores with phones full of gift cards, buying Apple and Bose gear by the cartload (about $141,000 across 85 Target stores in 18 states in two days), with the goods shipped back to China. The larger ring this fed into reportedly moved over $100 million in gift cards.

PingCAP breach claims

An extortion group calling itself FulcrumSec has posted a leak site claiming a massive breach of PingCAP, makers of the TiDB Cloud managed database service. The group claims it found cloud credentials committed to PingCAP’s own source code repositories, and used them to set up a replication feed of PingCAP’s production control database that re-exported everything to the attackers every six hours for 22 days, without being noticed.

The claims haven’t been independently verified, but they’re very specific: 10.6TB of data, 115,000 customer API keys stored in plaintext, 20 million customer SQL queries, four years of connection logs with customer IP addresses, and 413 private source repositories. The attackers quote a 2022 internal security ticket noting that any member of a customer organization, even a billing-only account, could reset the root password on every database in that organization. Perhaps most damaging, support engineers allegedly pasted live customer credentials into support tickets, including cloud keys with admin access to other companies’ storage. If you’re a TiDB Cloud customer, assume your API keys, connection strings, and anything ever pasted into a support ticket are burned, and rotate accordingly.

Fake WhatsApp on the Play Store

Android Authority found a fake WhatsApp app on Google Play with over half a million downloads, a week after a fake Chrome app racked up over 100,000. The fake copied the real listing’s screenshots and description word for word, and in some cases appeared as a sponsored result when searching for the real app.

The trick that let it linger is Google Play’s “Early Access” program, which disables public reviews. Normally a fake app gets buried in one-star “THIS IS A SCAM” reviews; in Early Access, nobody can see them. As of publication it was still available. “Only install from the official store” is still good advice for family members, but it’s a little less reassuring when the official store is selling ad placement to the fake.

Meta Muse leaks via DNS

Back in September, we covered a serious vulnerability in Muse, Meta’s extremely privileged AI agent. This week, Meta suspended Muse’s chat sharing feature after researchers at Claroc found they could find and read thousands of shared conversations.

Each shared chat got its own web address, with the conversation title as part of the hostname. Hostnames get looked up in DNS, and many DNS lookups are recorded by “passive DNS” services, essentially a giant searchable history of which names have been resolved. One search returned a ready-made table of contents of shared chats. Claroc found 6,800 of them, including a small business loan application, a bank fraud alert with partial account details, and internal company documents. “Secret URL” sharing only works if the URL stays secret, and putting the secret in a DNS hostname is roughly the opposite of that.

Password1 strikes again

The UK Information Commissioner’s Office reprimanded IT provider Ogi Networks and the Welsh public sector data organization Data Cymru over a 2024 ransomware attack which exposed data on 3,300 people, most of them children. The way in? A test account named “Test2”, created in 2012, never reviewed, and protected with the password “Password1”. The local administrator accounts on three systems also shared a single password for the same twelve years.

There’s nothing exotic here, sadly. Old accounts nobody remembers, passwords that would fall to the first guess of any automated tool, and an outsourcing arrangement where each side assumed the other was handling security. None of it makes for exciting headlines, but these are the things that keep causing very real breaches.

Trezor wallets also implanted

As a follow-up to last week’s coverage of hardware implants in Ledger crypto wallets, Kim Zetter reports that Trezor’s claim of “not a single piece of evidence” that its devices were compromised doesn’t quite line up with reality. Joe Grand found implants in two Trezor wallets, bought through Facebook Marketplace and a TikTok shop, and reported them to Trezor in August.

The Trezor attack is different from the Ledger implant. Instead of adding a radio to spy on the screen, the attackers replaced the main microcontroller with one running modified (open source) firmware. The firmware “randomly” generates one of a dozen recovery phrases the attackers already know. To pass Trezor’s integrity checks, it presents a copy of the legitimate firmware for verification before switching to the malicious code. The takeaway hasn’t changed from last week: buy only directly from the vendor, and if you’re holding enough crypto to make this worth someone’s while, consider whether you can really trust any single device.

NGINX gets more critical bugs

F5 has released out-of-band (meaning outside their normal patch schedule) updates for three critical vulnerabilities in NGINX, the web server and reverse proxy that sits in front of a huge chunk of the Internet, and quite possibly in front of the services on your home lab. The Cyber Security Agency of Singapore has a summary: all three are rated CVSS 9.2, can be triggered remotely without authentication, and can crash worker processes or, under the right conditions, allow remote code execution.

The bugs are CVE-2026-15176, a heap overflow in the “alias” and “rewrite” directives; CVE-2026-97205, a use-after-free in asynchronous file I/O combined with Server Side Includes; and CVE-2026-93479, a heap overflow in the “map” directive. Code execution requires the vulnerable configuration to be in use, and requires bypassing ASLR (the randomization of memory layout which makes exploits harder to aim). Affected versions include NGINX Open Source 1.30.5 and below and 1.31.6 and below, NGINX Plus R33 through R37, and a long list of F5’s NGINX-based products, including the Kubernetes Ingress Controller.

Back in May we covered “nginx-poolslip”, where the suggested mitigation was to avoid unnamed regex capture groups in rewrite rules. The mitigation for the “map” bug this time? Use named captures instead of unnamed captures. If you’ve been putting off cleaning up those “$1” references in your config, now’s the time. For the other two, avoid “alias” inside “location” blocks (and the “$request_filename” variable), or disable AIO or SSI, until you can update.

Linux kernel bugs posted to the wrong list

Normally, security bugs in the Linux kernel are reported privately to the kernel security team, which coordinates a fix before details go public. This is “coordinated disclosure”: the bug and fix are published together, ideally giving admins a chance to patch before attackers can start writing exploits. The Linux Kernel Mailing List (LKML), on the other hand, is about as public as it gets.

Phoronix reports that Trend Micro’s Zero Day Initiative, seemingly by accident, sent a batch of unpatched vulnerability reports straight to LKML. Greg Kroah-Hartman replied to each report asking about the choice of mailing list, which I can only imagine was done with remarkable restraint. The most serious two are both CVSS 9.0 remote code execution bugs in ksmbd, the kernel’s built-in SMB (Windows file sharing) server: an integer underflow in SMB Direct, and a race condition. The rest include local privilege escalation bugs in the networking code, the VMware graphics driver (an out-of-bounds write), and a stack overflow in search-domain TCP query handling, plus an information leak in the NVMe-over-fabrics target code.

Some of the bugs already have patches being tested or queued for future kernel releases, and those will presumably be expedited now. Most systems don’t run ksmbd (the userspace Samba server is far more common), but if you’ve enabled it on a NAS or a home server, it’s worth disabling until patched kernels land. As Phoronix puts it: “the bug and security reports keep on coming in the AI fueled world.”

Hackaday Links: October 17, 2026

By: Tom Nardi
18 October 2026 at 22:00
Hackaday Links Column Banner

While Hackaday doesn’t maintain a crime blotter, we couldn’t help but start this week’s post off with a bit of civil disobedience — a retired professor from the University of Pennsylvania was arrested earlier this week for standing in front of a delivery robot.

Granted, she was standing there for long enough that the police were eventually called, but still. Previous reporting indicates that Carolyn Marvin has a history of blocking delivery robots as a form of protest, but this is the first time law enforcement got involved. We’re not lawyers here at Hackaday, so we can’t say for sure whether or not blocking the progress of a robot engaged in commercial operation actually violates any laws. But we do know that refusing a lawful request from a police officer will get you in trouble, and that seems to be what Marvin was actually charged with when she refused to move.

From a robot stopped in its tracks to one that keeps on trucking, NASA is reporting that the odometer on the Perseverance Mars rover recently ticked over to 28.10 miles (45.22 kilometers). That might not seem like a lot, but it officially makes it the most traveled rover in the solar system, breaking the record set by Opportunity at 28.06 miles (45.16 km). One might expect that the Curiosity rover would hold the distance record as it had been rolling around on the surface for more than a decade before Perseverance dropped into the neighborhood, but the different scientific missions of the two nearly identical rovers have taken them on very different courses.

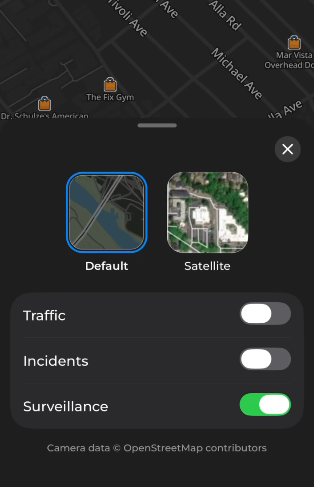
On the subject of navigation, MapQuest recently announced the availability of the “Surveillance Layer” in their smartphone application. When enabled, it shows the location of known license plate readers and cameras on the map, allowing the user to plan their route accordingly. A note in the application’s user interface mentions that they’re pulling at least some of this data from OpenStreetMap, though it’s not clear currently if other sources such as DeFlock are being used.

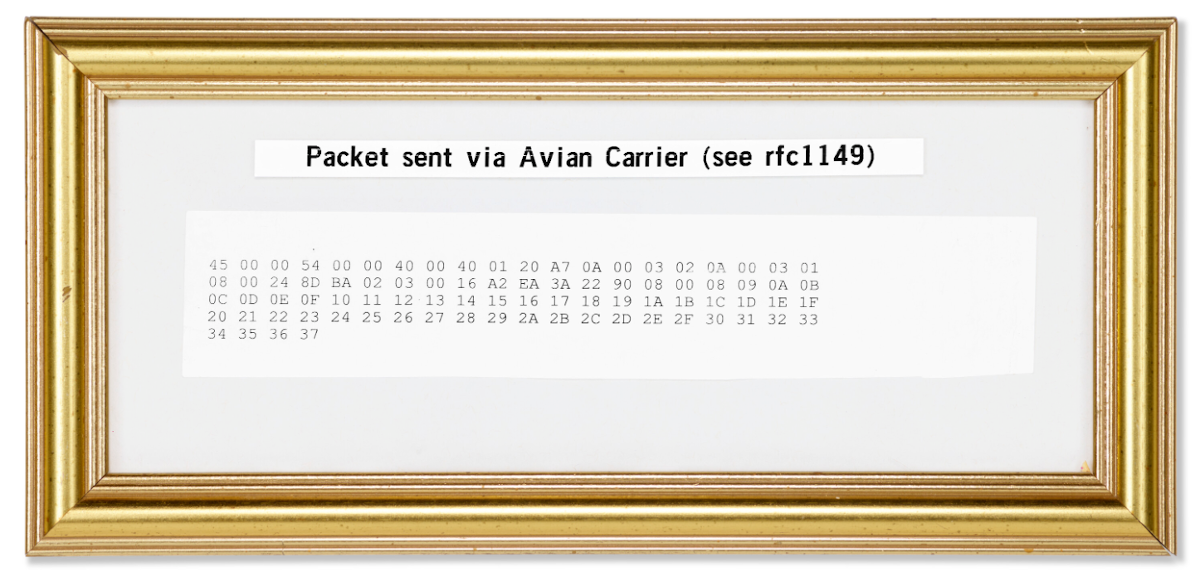
Finally, we have an update on the Christie’s auction for the carrier pigeon data packet sent back in 2001 by Norway’s Bergen Linux User Group. The auction house thought the framed datagram might fetch as much as $3,000 USD, but when the hammer finally went down earlier this week the winning bid was a staggering $20,480. Given all the weird gadgets we’ve picked up on a whim, we’re not in a position to lecture anyone else about how they spend their money…but damn.


See something interesting that you think would be a good fit for our weekly Links column? Drop us a line, we’d love to hear about it.

Discovering SDRs Everywhere

17 October 2026 at 10:00

To quote commenter [douyarou], “It’s like our little version of a Precambrian explosion”. A bunch of hackers have discovered, independently and building on each other’s work, software-defined radio (SDR) capabilities in more places than you can shake a stick at.

It all started with [Espargos] and [h0m3us3r] apparently independently discovering that the ESP32 family of chips had a “secret” debug mode that allowed direct access to the radio that’s normally used for WiFi. While the 2.4 GHz radio signal is almost always immediately converted into data by the MAC hardware, here they found a way to listen in upstream, to the raw IQ data.

Seeing this, folks were immediately inspired to find out if they could transmit as well. [marble] not only got transmit functionality working, but integrated the part in with the standard osmosdr data flow, which meant that a whole bunch of existing tools were ready to go. We didn’t know about it at the time, but apparently [jochenhammes] and [z1000biker] concurrently had their TX-capable hacks up and running: here and here.

At this point, folks have already started to use the capabilities for broadcasting digital TV signals, voice signals, FM Hell, and other hijinks. This reminds us of the early days of the RTL-SDR project, when a competent, if receive-only, SDR functionality was found in a bunch of USB TV-tuner dongles. Once the hardware capabilities were sussed out, people started writing all sorts of useful software, and it gave rise to all manner of radio projects, from simply poking at domestic wireless devices to tracking all the airplanes in the world as they fly by.

[Tom] and I were discussing this on the podcast, and he remarked that of course there are SDRs hidden everywhere there is a radio unit these days, and the question is just whether or not we could hack them into usability. And before the podcast was even finally edited, [Samson1te] told us about his find in the LR2021 LoRa chip. This is a radio that’s designed to be a radio, with 16-bit resolution, and covering lower frequencies from 150 MHz to 960 MHz.

Compared to the RTL-SDR revolution, this is all happening at incredible speed. Each of these hacks will enable us to use different slices of radio spectrum with different degrees of ease, but it’s clear that the cost of entry into playing around with digital radio has just dropped precipitously. We will see hundreds of new signals hacks in the next few months – the floodgates have been opened.

This article is part of the Hackaday.com newsletter, delivered every seven days for each of the last 200+ weeks. It also includes our favorite articles from the last seven days that you can see on the web version of the newsletter. Want this type of article to hit your inbox every Friday morning? You should sign up!

Hackaday Podcast Episode 391: Tuned in to ESP32 SDR, New Old Pagers, and Bugs on Mars

By: Tom Nardi
16 October 2026 at 12:00

Hackaday Editors Elliot Williams and Tom Nardi start this episode off with a discussion about Philadelphia’s budding hacker conference and the imminent retirement of the EZ80. After considering the parallels between the wide world of aviation headsets and our personal projects, talk moves on to the exciting developments in the world of software-defined radio on the ESP32, a Meshtastic pager from a bygone era, and how all the wild flying machines entered into DARPA’s Lift Challenge ended up losing to a simple helicopter.

You’ll also hear about turning plastic bottles into printer filament, pushing e-ink screens to their limits, and browsing the web on the PSP in 2026. To wrap things up they’ll marvel at all the modern abstraction sitting between software and the memory it’s running on, and revisit some RF concepts that might be particularly useful now that everyone is playing with a new SDR device.

Check out the links if you want to follow along, and as always, tell us what you think about this episode in the comments!

Download in DRM-free MP3.

Where to Follow Hackaday Podcast

Episode 391 Show Notes:

News:

Mailbag:

  • You don’t have to reinvent the wheel, but sometimes it can be fun. Thanks [Tom Brusehaver] for the headphone suggestions.

Interesting Hacks of the Week:

Quick Hacks:

Can’t-Miss Articles:

This Week in Security: Critical DNS Keys Rotated, Hacking Freezers Isn’t Cool, OpenAI Spies On Itself, and Advanced Hardware Wallet Hacks

16 October 2026 at 10:00

Critical Internet keys changed this week. Did you notice?  The keys behind DNSSEC, the system for cryptographically validating DNS responses, rolled over on October 11 2026. This is the second time the DNSSEC keys have rotated since the system was implemented, and the first time in 2018 didn’t exactly go entirely smoothly.

DNS is what resolves a host name and turns it into an IP address. It underpins web browsing, email, and just about every other connection. It’s also a very early Internet protocol, written in both a simpler, less paranoid era, and an era where encryption was computationally expensive and legally problematic. DNS offers little protection against malicious actors spoofing responses, and the impacts range from phishing to redirecting email to just about any other manipulation of connections you can image.

DNSSEC addresses this by creating a chain of trust between DNS resolvers — the servers that forward the DNS query into the DNS infrastructure and return the results — and the global DNS servers. Part of this chain of trust is the root key that each resolver must have and trust, and this key is what changed this week.  DNSSEC resolvers automatically watch for a new root of trust key, but the key must be signed by the previous root of trust, and is checked for at least 30 days before it is trusted.  If someone were able to issue a bogus certificate, they would have to maintain control of the infrastructure for over a month before DNS resolvers would trust it.

The process of distributing the new key actually began more than a year ago, on January 11, 2025, to give DNSSEC resolvers time to get the new key. DNSSEC services should have had plenty of time to obtain and trust the new key, and unless DNS stopped working for you this week, they did their job.

The next major change for DNSSEC will require more profound changes to deploy a new signing algorithm that will be post-quantum secure.

Ransomware Recovery Company Didn’t Recover

BleepingComputer reports that the CEO of a company advertising services for recovering from ransomware attacks has been charged with fraud.

The company advertised that it could help with recovering from a ransomware attack by providing decryption services to unlock the ransomed files. Instead, the CEO of the company is accused of negotiating a ransom payment with the attackers and charging the victims a premium on top of the ransom.

In addition to fraudulent claims of decrypting the data without a ransom, this could fall foul of embargo laws against paying ransomware operators in some countries, or be against customer policy regarding payments.

The charges detail incidents in which the ransomware operators were paid $9,800, while the victims were charged $150,000 for “recovery”, and claim the company overall paid more than $8 million in ransom fees while charging customers $18 million.

More Refrigeration Hacks

Several weeks ago, commissaries operated by the United States military suffered a series of refrigeration failures. Units on multiple bases in multiple states and countries entered defrost mode, which activated heaters, spoiling food overnight.  This week, hundreds of supermarkets in France have suffered the same issue, with units heating up and some even reportedly catching fire.

The attack started Sunday night, and not only triggers defrost mode, but seems to force the units to stay in defrost mode for a prolonged period. Losses are estimated to reach over $300,000.  French prosecutors have called for investigations of the wide-spread attacks.

Clearly, a vulnerability has been found in the refrigeration controllers connected to the Internet, and fingers are being pointed at the Danfoss brand, which is also used by the US military bases. Researcher Kevin Beaumont points out that it may not even be a traditional vulnerability:  Many of the units are directly connected to the Internet, with the username “admin”, and a password that changes daily. Unfortunately, the password changes to the current date. “Every single one is like this. You can just log in and change the temperature. Anybody can do it, easily.”

OpenAI employee charged with spying

An OpenAI employee was charged with spying after being caught placing “sophisticated listening devices” in meeting rooms, hidden in toilet paper: the most sophisticated of camouflage.

Employees discovered the device approximately two days after it was placed, according to the report. Ironically, logs indicate the employee used OpenAI’s own chatbot to help design the device and identify locations for it. Photos of the device look like it a SEEED Studio ESP32 device, a dev board likely very familiar to readers.

Stop & Shop and Hannaford hacked

The US supermarket chains Stop & Shop and Hannaford, which share a common owner, seem to have been hacked. There aren’t many details available yet, but multiple news sources in multiple states are reporting that the stores have taken their websites and online ordering completely offline, however stores remain open.

The company says it does not currently believe that customer payment details were part of the compromise.

Hardware wallets under attack

Kim Zetter brings the report of crypto thefts via hardware implanted in Ledger wallets.

Hardware wallets are offered as the panacea every time another crypto heist or supply-chain stealer makes the rounds. The idea is simple: private keys stay on the device and never touch your daily-driver, which is surely contaminated with keyloggers and trojans.  The crypto transaction is built on the host and hands it to the device, the wallet device then solves it with the private keys and returns the signature.  The only user interface is typically a screen display, which is exactly where the physical supply chain hack against Ledger happened.

The implants, found mainly in Ledger Nano X devices so far, sit dormant until the owner sets up the wallet. When the device shows the new recovery seed on its screen, the implant reads each character and sends the seed out through its own LTE modem, antenna, and eSIM. The implant never touches the host computer or the users WiFi network.  The secure storage inside the wallet is never compromised: the hardware implant spies directly on the LCD to read the recovery keys as displayed to the user.

Blockchain analytics firm Bitquery links about 315 drained accounts, roughly $102 million in Bitcoin, Ethereum, Tron and others, to devices sold by CryptoBilis: that’s Ledger’s authorized reseller for Malaysia, Indonesia, and the Philippines.

[Joe Grand], a hardware hacker often featured here and the force behind many DEFCON conference badges, began looking in August 2025 after a Reddit post from someone who had bought a wallet on a Thai marketplace. [Joe] bought eight more Nano X units and found implants in four of them. This was reported to Ledger in March of 2026, but according to [Grand], Ledger didn’t follow up for months.

Then in September, Mark Karpelès, the former Mt. Gox CEO, published a teardown showing how the implants have evolved. The first generation used hand-soldered wires to the screen.  The second used a transparent orange flex circuit laminated onto the board, with a smaller battery to make room. The third uses a black-coated flex with the part numbers scraped off and a custom antenna.  A Japan-based researcher who examined ten Nano X and two Flex devices found five distinct implant designs.  They traced the eSIM traffic to an Alibaba-managed data center in Hong Kong, with at least 90 implants reporting seeds there in June alone.

Ledger’s official position is that a “limited number” of devices came from a single seller. It says there is no sign that its own systems were compromised, and it has told resellers to buy only through authorized channels and “never to restock returned products. That last line points at a likely route: buy wallets, implant them, return them, and let them go back on the shelf.

Despite the claims of a single compromised seller, a user named [Johannes] found implants in two Nano X units bought at MediaMarkt stores in Europe, and MediaMarkt is a listed authorized reseller with around a thousand stores across ten countries.  There are also reports of implanted Flex devices, and Stax reports that are still unverified. Trezor has started trimming its own authorized-seller list as a “preventive step.” Attribution is still unknown.

CryptoBilis changed ownership earlier this year under an NDA that only recently expired, which has raised eyebrows.  Zetter is careful to note that there’s no evidence connecting CryptoBilis to the implants or the thefts.

The takeaway is uncomfortable for anyone who has told people to “just buy a hardware wallet”. The threat model always assumed the device itself was trustworthy, and “buy direct from the vendor” was advice for being extra careful.  Now it’s the minimum.  Tamper-evident packaging clearly isn’t enough against someone with a lamination process and a parts budget. The options get less fun from here: open the case and inspect the board, which voids the warranty, and good luck spotting a black flex on a black PCB, generate the seed somewhere you control and import it, or use multi-signing across vendors so one bad device can’t empty everything.

Crypto forces you to be your own security, and if you have enough money for someone to design an attack that would have only been expected of a nation-state a few years ago, your home-grown security has to be really, really good.

2026 Hackaday Supercon: Workshops are Open!

14 October 2026 at 13:00

Supercon is Hackaday’s annual gathering, and you absolutely need to be there.

Today, we’re pleased to announce our lineup of workshops, and it’s more than we’ve ever offered, thanks to moving to a bigger venue and to our awesome community of hackers stepping up to give them. There’s something here for everyone, so if anything strikes your fancy, be sure to book yourself a slot soon. (If you have a ticket already, you sign up for the workshop as an “add-on”, BTW.) Workshops always fill up fast, due to the small and hands-on nature of the beast.

If you’ve never been to Supercon, the short version of the story is that it’s three days of hacking, hanging out, food, drink, merriment, and great talks all rolled into one long weekend. Fridays are chilled out, and simply a great time to get to know everyone and start playing around with whatever hardware hacks you’ve brought along. Saturday and Sunday are filled with talks, activities, and of course even more hob-nobbing with the world’s coolest nerds.

Basically, it’s all the best of Hackaday, made even better by being live and in person. All that’s missing is you.

We have another round of speakers and hopefully a badge reveal coming up soon, so stay tuned!

Josh Martin
Making 3D Images (Lenticulars) and 3D Cameras

In this workshop, participants will learn what a 3D image looks like, the history behind 3D photography, and how to take 3D images using film and digital cameras. The workshop will walk participants through making their own 3D camera with off the shelf parts, a 3D printer, and custom software we have written.

Building on this foundation, the workshop also covers the process of how to take the 3D images captured with a 3D camera and transform them into a physical print called a lenticular.

Everyone will get to take their own lenticular print home at the end of this workshop.

Darcy Neal
Explore the EMF Around You

This workshop explores what EMF frequencies are, where they come from, how we can listen to them, and how to build your own sensing device.

Sessions end with a sound exploration where participants go discover what unique sounds they can find. The EMF Explorer Badge is a hands-on soldering kit that turns the invisible electrical activity of everyday electronics into sound. Walk around, listen, compare devices, and build intuition for the signals hiding in the modern world.

If time allows, we will open the board file in KiCad and learn how everyone can make their own creative PCB designs.

Shawn Hymel
Reinforcement Learning for Robotics

Reinforcement learning is reshaping how robots learn to move: it’s driving breakthroughs at labs like ETH Zurich, Boston Dynamics, and Disney Research, enabling robots to handle environments and challenges they were never explicitly trained for. The good news is that you don’t need a fully equipped research lab to get started. In this hands-on workshop, participants will train an AI agent from scratch to balance a two-wheeled robot, then watch it run on real hardware.

We’ll tackle two of the most common real-world challenges in robotics: how to make an agent that’s actually robust and how to transfer a policy trained in simulation onto a physical robot. By the end of the session, attendees will leave with hands-on intuition for modern robot learning.

Alessandra Noelting
Exquisite Circuit: Exquisite Corpse for Electronics

What happens when a circuit is designed by a room full of people who cannot see the whole circuit?

In this hands-on electronic version of Exquisite Corpse, each participant adds a stage to a shared low-voltage circuit, conceals their work, and passes it to the next builder. Participants inherit standardized power and signal connections – but no schematic, explanation, or design review.

At the end, we reveal the complete creations, attempt to reconstruct their collective logic, inspect them for safety, and apply power from a strictly current-limited supply. Functionality is optional. Surprise is guaranteed.

Bob Hickman and Estefannie
Bling It On: Programming Your Own Generative Art Matrix

This is a repeat of our wildly popular “Bling It On” workshop form 2025. In this intermediate-level maker workshop, you will learn the fundamentals of generative algorithms and apply them using either Circuit Python or C++ to create a dynamic display that can pull data over WiFi from one or more APIs and use the data to visualize some generative art.

The results will be beautiful and practical, and attendees will leave with an amazing 130 mm x 130 mm LED matrix. If you missed out on our sold out workshop last year, this is your chance to Bling It On!

Nathan Jones
Badge Hacking for Beginners

Calling all nerds, newbies, and first-time attendees to the world-famous Hackaday Supercon! You just received your super duper, neato conference badge… now what?

“Badge hacking” is a seminal part of the Supercon experience, but it can feel intimidating to attempt if you’re new to embedded systems. In this workshop, I’ll break down those barriers for you, by explaining exactly how the badge works and what you can do with it.

Then I’ll walk you through your very first badge hacks, one software-focused and one hardware-focused, so that you’ll be able to walk around with your very own, one-of-a-kind, customized conference badge. Maybe I’ll even be able to convince you to show it off during the “Badge Hacking Competition” on Sunday!

Debra Ansell
Powered Flowers and Prismatic Stars: LED Wearables with Illuminated Appliqué

This workshop goes beyond conductive thread and sewable LEDs. Participants will learn how to enhance clothing and accessories with assemblies of discreet 3D printed diffusers connected by mesh fabric and illuminated by addressable string lights. The result is attractive, flexible, durable, and versatile, and the technique can be adapted into different configurations and effects to enhance a wide variety of wearables.

All parts and tools necessary to create, power and animate LED patterns on an illuminated star- or flower- shaped applique are provided, as well as a hat or bag to sew the applique onto. Participants may also opt to bring their own item to decorate. If bringing your own piece of clothing or accessory, please choose one made from sturdy fabric such as denim or canvas that will support an electronics assembly.

An overview of controlling patterns and playlists with WLED will take place at the end, that will cover as much detail as time allows. Participants will want to bring a laptop (easiest) or smartphone to connect to and customize their wearable.

Ayesha Wilson and Alex Lynd
We have TCSM at Home! (Learn to build your own Antenna + Wireless Bug Hunting Tools)

Ayesha will walk you through the fundamentals of antenna design – we use OpenEMS to explore antenna geometry, impedance matching, and S-parameter simulation before importing the design into KiCad for PCB layout. You’ll learn to use a VNA for evaluating your antenna’s performance!

Alex will lead a short lesson on wireless tracking and a foxhunting exercise where attendees will use an ESP32 based console + custom antennas to locate Bluetooth beacons hidden around the venue!

This workshop is beginner friendly and will teach you the basics of wireless intelligence + PCB design, and attendees will walk away with an educational tool that can explore the RF landscape around them after the conference.

Pat Deegan
Tiny Tapeout

In this workshop, participants will get the opportunity to design and manufacture your own design on an ASIC!

Participants will learn the basics of digital logic, the basics of how semiconductors are designed and made, how to use an online digital design tool to build and simulate a simple design, and how to create the GDS files for manufacture on the open-source Sky130 PDK.

You will have the option to submit your designs to be manufactured on the next shuttle as part of the Tiny Tapeout project. (Thanks to sponsorship from ChipFoundry.io.)


Hackaday Links: October 11, 2026

By: Tom Nardi
11 October 2026 at 19:00
Hackaday Links Column Banner

It probably goes without saying that if you send four humans to observe the Moon up close, they’ll see things that those of us stuck here on Earth have never noticed. Luckily for us, they took impeccable notes and brought plenty of cameras, which NASA has shared with the rest of the class as Artemis II: Sights & Sounds of Science.

Well, technically it’s called the Artemis II Preliminary Lunar Science Report, but we appreciate the space agency adding a little flair to it and formatting the findings for public consumption. Arguably the most significant observations detailed in the report are the impact flashes on the lunar surface. As you may recall, the trajectory of the Orion spacecraft meant the crew experienced a unique solar eclipse on the sixth day of the mission, giving them an unprecedented close-up view of the darkened Moon. During this time, they were able to see flashes of light with their unaided eyes, which NASA has since confirmed were small rocky fragments — perhaps no more than a few inches wide — slamming into the lunar surface at incredible speeds.

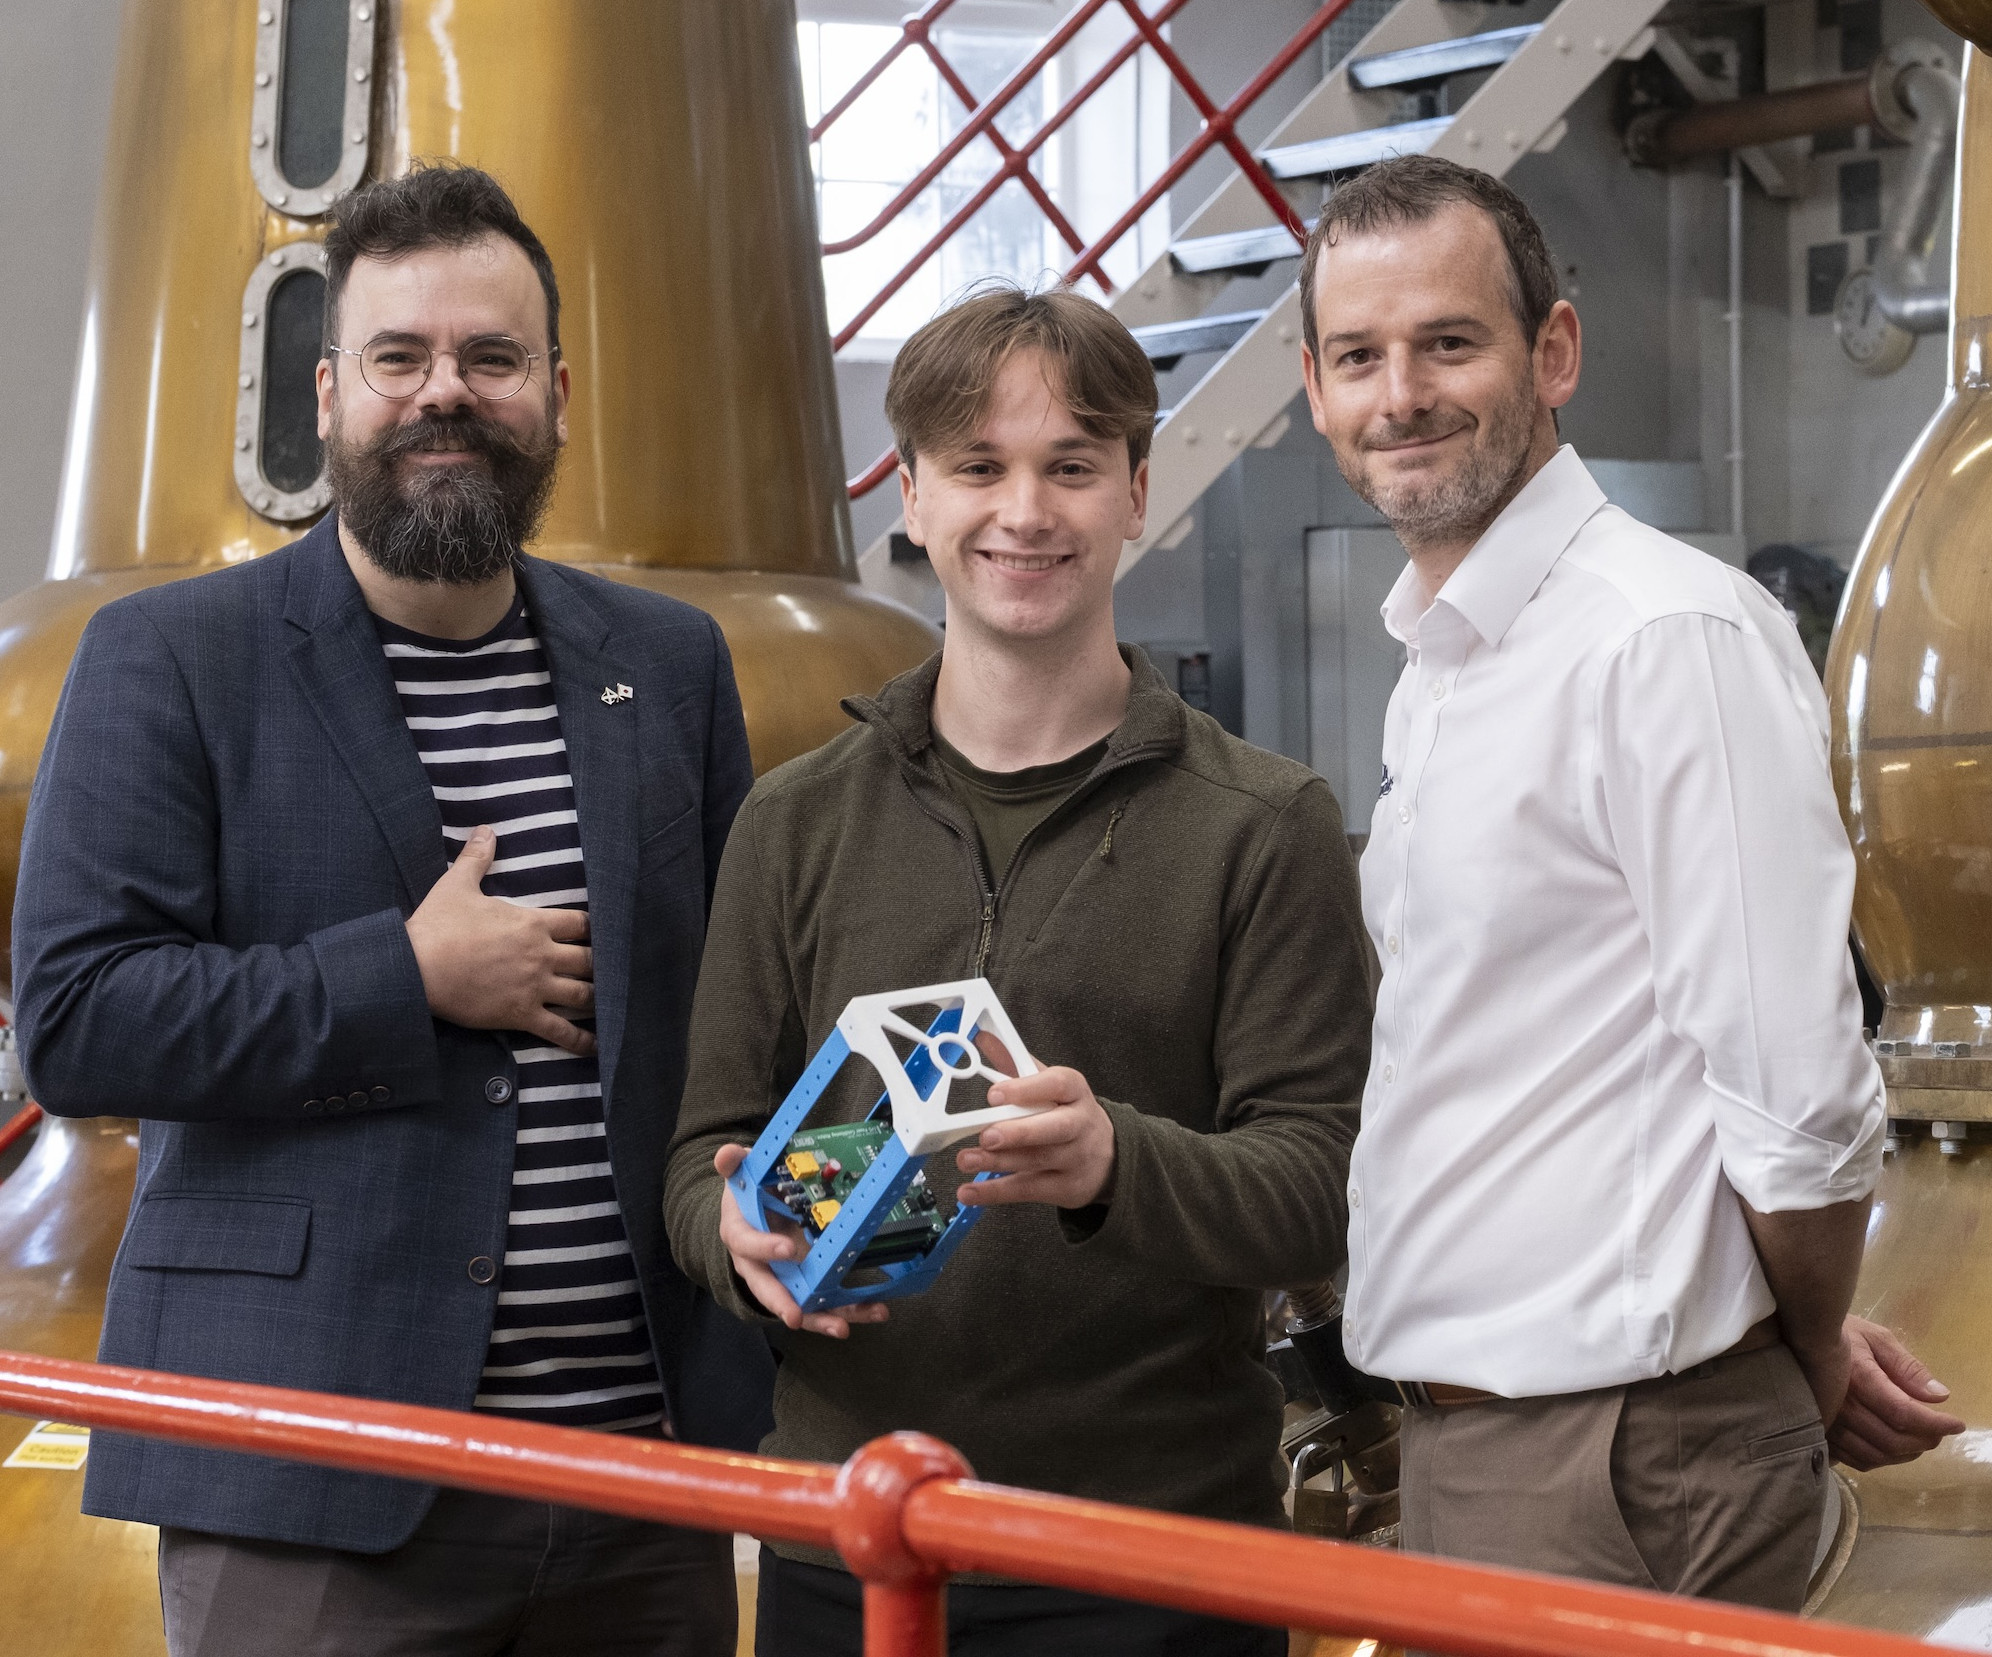
To boldly go where no whisky has gone before.

The Artemis II mission was one for the history books, for most of us the most significant space mission of our lifetimes. But as access to space becomes cheaper and more routine, it stands to reason that not all activities in orbit will be quite so momentous. For example, students from the University of Glasgow and Japan’s Kyushu Institute are currently collaborating on a planned mission to distill whisky in space for the first time.

Scheduled to launch in 2028, the CubeSat will carry 10 ml of fluid and spend five years in orbit studying how its chemical composition changes, with a special interest in how the frequent changes experienced as the spacecraft travels around the Earth could influence the maturing process. While this might not seem terribly interesting to teetotalers, it offers an opportunity to gain more practical experience with orbital manufacturing which will likely inform future missions.

Speaking of studying how things behave — or perhaps how they don’t behave, as the case may be — we have an update on the controversy around this year’s Nikon Small World in Motion competition. After several experts in the field raised the alarm last week, Ning Xu’s winning video supposedly showing cilia in airway tissue samples taken from a child with primary ciliary dyskinesia (PCD) has been disqualified for using generative AI. This shifted all the previous winners up a rank, so Nguyen Nam Nhat of Vietnam now takes the top spot with a video of a roundworm and a single-celled Dileptus.

According to experts, Dr. Ning Xu’s entry was literally too good to be true.

Xu had previously claimed that AI was only used for post-processing the original images, which would have already put the entry into something of a gray area as far as the competition was concerned. But according to researchers familiar with PCD, the structures shown in the video don’t look like anything they’d ever seen in a patient, prompting suspicion that the admittedly fascinating visuals were actually the result of an AI hallucination.

Finally, on the subject of beautiful images, we’d like to point you to ascii.rest. As you’ve probably noticed, we appreciate minimal web design around these parts, so this collection of ASCII animations and art immediately caught our eye. Some of the pieces, like “aurora fjord” shown here, can be exported as a GIF or video clip. But there’s also the option to embed them in your HTML with a couple of lines, which also gives you the opportunity to customize and manipulate them in various ways. If you do anything cool with these designs, we’d love to see it.


See something interesting that you think would be a good fit for our weekly Links column? Drop us a line, we’d love to hear about it.

The Weirdest Video Games were Hacks

10 October 2026 at 10:00

We were looking into the marvelous recent project by [Throaty Mumbo] to recreate and reimagine the forgotten world of VHS-tape-based video games. Wait, what? Yes, back in the day, when computer graphics were more primitive, there were attempts to mix the gameplay of video games with the graphics from a video cassette. Take the Action Max system. It worked with a light-gun that pointed at the screen while the video played, and you tried to shoot at things as they flew by. Think Duck Hunt, but in glorious VHS video quality with cheesy acting, and the same gameplay loop every time, because it’s on the tape.

The unreleased Control-Vision VHS gaming system, co-developed with none other than Steve Wozniak, took the idea a little further and ran simultaneous sub-videos, and your actions would choose which of the sub-tracks would play at any given time. This let them do things like switch between videos depending on whether you caught the bad guys or missed them entirely, for instance.

These games came in the late 1980s, though, and they were all derivatives of the seminal Dragon’s Lair, which is probably the least fun video game I’ve ever had the chance to play, but among the most entertaining in a weird way. Instead of a linear VHS tape, Dragon’s Lair, and the later but equally unplayable Space Ace, were based on the then-new video disc technology that could swap between entirely different tracks almost seamlessly.

“Almost” is the key word here, though. Although the animations were absolutely marvelously cartoony, and looked stunning in an arcade up against video games of the time, there was a significant fraction of a second of delay between commanding an action with the joystick and the machine swapping up to the correct track. There were a couple of sections where back-to-back actions were necessary, and the challenge was to work around the game’s exact track-swapping-glitch time. As good as they looked, the gameplay was no fun.

But the game was influential, as evidenced by its VHS-based clones. If you’d like to give it a try, you’ll not be surprised to hear that there’s an emulator for Dragon’s Lair and its spin-off games.

What do all of these have to do with each other? We love how these games took a current technology – in this case video discs or video tapes – and tried to make it do something else: These games were all hacks. If you look at them in that light, maybe you can look past the horrible acting in Night Trap or the frustrating glitches in Dragon’s Lair. (Or maybe not. Give me Robotron: 2084 any day.)

This article is part of the Hackaday.com newsletter, delivered every seven days for each of the last 200+ weeks. It also includes our favorite articles from the last seven days that you can see on the web version of the newsletter. Want this type of article to hit your inbox every Friday morning? You should sign up!

Hackaday Podcast Episode 390: DOOM, Cranium Stuff, and Odd OpenSCAD Opportunities

9 October 2026 at 12:30

This week, Elliot Williams and Kristina Panos met a few minutes later than usual, and somehow defeated a buzz together with the power of will before settling into the news, rifling through the Mailbag, and otherwise creating the attached podcast.

So, the news. Amazon, in their infinite wisdom, have chosen to not only remove Alexa’s aux port on future models, but also disable the input on extant ones. Is this really bad news? Maybe just because it seems like taking a choice away for the sake of exerting power over the people.

Anyway. In Hackaday news, the Retrocomputing Contest is currently on fire, and runs through 10AM PDT on Tuesday, October 27th. That means you have about 2.5 weeks left.

Supercon Ten ticket sales are similarly aflame, and per Elliot, it’s about time to release the next round of speakers. So, watch for that.

After digging deep in the Mailbag and eventually just dumping the thing out on the table, we found our brand new Hackaday Podcast Mailbag Audio Bumper! This jingle comes courtesy of [Dakota Winslow], who also advises that there are Easter eggs to be found.

Then, it was on to the hacks, including Elliot’s record-tying number of Quick Hacks, and plenty of in-linkage.

Check out the links below if you want to follow along, and as always, tell us what you think about this episode in the comments!

Download in lovely MP3.

Where to Follow Hackaday Podcast

Episode 390 Show Notes:

News:

Mailbag:

  • Check out our new Hackaday Podcast Mailbag Audio Bumper!  Thanks [Dakota]!

Interesting Hacks of the Week:


Quick Hacks:

Can’t-Miss Articles:

This Week in Security: New Spectre Attacks, Crushing Quantity of Linux Vulns, Google Gets Too Much AI, and Hacking Lawnmowers

9 October 2026 at 10:00

Just-in-time, or JIT, compilation could be considered a fundamental backbone of modern computing.  JIT compilation turns scripting languages like JavaScript or intermediary binary forms like Web Assembly into native code on the fly, giving web apps, and things that are web apps under the covers like Electron-based tools, near native speed.  A new paper explores leveraging JIT systems to revive Spectre-v2 attacks against processors.

Most modern processors gain performance by using a trick called “speculative execution”.  The processor guesses the likely result of a compare, and begins executing some of the next instructions before the results are actually known.  If the processor guessed right, things continue and there is a speed gain because it can jump ahead, but if the processor guessed wrong, any instructions that were run and any side effects of running them are discarded and execution resumes on the actual path.  In theory, anyhow.

In practice, the Spectre class of attacks targets branch prediction. It was discovered that when the wrong branch was chosen, not all of the results were truly hidden; Patterns of failures in guessing branches can be used to leak behavior processing encryption keys and other activities. The attacks evolved with the research dubbed Spectre-V2, which showed that non-privileged contexts, like non-root users and virtual machines, could poison the instruction prediction and use it to read arbitrary memory.  Fixes to the Linux kernel and other platforms were required to mitigate the worst of the effects.

The paper shows that by using self-modifying code in the JIT, the processor can be tricked into loading cached versions of the instructions.  The fixes to the kernel to prevent Spectre attacks include identifying malicious code patterns that attack the branch prediction, and stopping or changing them:  By causing the CPU to execute the cached copy of instructions instead of the live copy, the attack ignores the fixed instructions entirely and can attack the branch prediction algorithm.

To prove the attack is feasible in the real world, the researchers targeted several JIT compilers, including the SpiderMonkey JavaScript engine used by Firefox, the eBPF JIT found in the Linux kernel, and GraalVM, the JIT used in Python.  They found success with each, demonstrating that the attack is at least plausible.

Research like this is unlikely to be an instant world-melter, and will help find possible mitigations in the future to prevent these sorts of attacks.  Operating systems that support a high-security “lock-down” mode, like macOS and iOS, often disable JIT entirely, out of concern about these sorts of attacks.  There’s probably no need to start disabling JIT on every system, but attacks like these have a tendency to evolve.

Enormous List of Vulnerabilities Patched in Linux

Updated Linux kernels are available for most distributions, with a truly intimidating list of patched security issues.  As this Debian post states, “Several vulnerabilities have been discovered in the Linux kernel that may lead to a privilege escalation, denial of service or information leaks.”  Several, in this case, is a load-bearing word, and you should go check out the CVE list.  I’ll wait.

This, apparently, is what the AI Vulnpocalypse looks like today. After Windows patched over a thousand vulnerabilities in a single Patch Tuesday, we probably had a pretty good idea what would be coming. With over 1,200 vulnerability report IDs listed in the patch, manually understanding the security impact is extremely daunting if not entirely impossible. A random sampling shows vulnerabilities in compression handling, denial of service attacks from local users, and memory corruption that may or may not be exploitable, but with a list this huge that’s hardly exhaustive.

For normal admins and users, there isn’t much else to do besides apply the patches and hope they don’t cause new problems.  Linux overall has a better track record with patches not breaking they entire system, but it’s not unheard of, and with this much churn, the chances of something going wrong of course increases.  Patching is almost always a better option than not patching and hoping you don’t get owned, though!

Google Stops Bug Bounty Program Because of AI

“Stop hitting yourself” comes to mind. Google has stopped the Google Open Source Vulnerability Rewards Program, the bounty program offering rewards for finding bugs in the companies open source releases.

Surprising nobody, the bounty program has been flooded with “low effort” and “low quality” AI generated reports. Google says maintainers were overwhelmed with false reports containing AI hallucinations, and that the program would be re-evaluated in 2027. While AI-assisted, or even directed, security research is our new normal, if the results aren’t checked by someone able to confirm they’re legitimate, submitting them helps nobody.

Can’t help but feel some schadenfreude that a company shoving AI into every aspect of our lives is then impacted by AI being shoved everywhere, but in the end swamping developers with bogus reports keeps them from fixing the real bugs and benefits nobody, so it’s hard to find a positive takeaway on this one.

Retailer Asos Hacked, Ransomed

Customers of the Asos online clothing store who installed the Asos app got first-hand evidence that the platform was hacked by a ransomware crew.  The attackers used the Asos app push notifications to send an alert to all customers: “Dear Asos DPO and IT, we have fully compromised the Snowflake instance.  Engage with us, or we will leak it.”

Snowflake is a cloud-scale database company, and has been implicated in several other attacks over the past few years, including a large hack in 2024 by the ShinyHunters group that led to compromises of Ticketmaster, AT&T, Lending Tree, and others. It’s unclear how the Asos Snowflake instance was compromised.

Direct-to-consumer ransomware demands aren’t new, and apply pressure to the impacted company. The message itself is a well-phrased piece of propaganda, casting the hacked company as the villain who isn’t protecting the customers by engaging in the extortion demands. Asos so far indicates that “basic customer information” like name and contact information, but possibly not payment details.

Accenture Contractor Implicated in FBI Hack

The FBI has removed a contractor from the multinational tech company Accenture, after determining that the breach of the Oracle PeopleSoft instance that then led to the breach of the information of the entire FBI agent and employee system, was avoidable.

Details remain scarce, but this would imply that the vulnerability used by ShinyHunters wasn’t a zero-day after all. One of the most dangerous phases of the vulnerability lifecycle is when both the bug and patch are known, because researchers can often quickly deduce the vulnerability from the patch and write an exploit. This seems to be what happened here.

Rarely are specific individuals held directly responsible for patch cycles. Patching production services of large organizations is usually determined at an institutional level.  Reading between the lines, the individual may have been directly tasked with doing the work of installing the patches and didn’t.

Last week, the ShinyHunters group made public statements that it did not plan to leak the stolen information, and was simply using it as a means to get press coverage of their grievances against the FBI.  The promise not to leak the addresses of the families of agents is probably appreciated by the agents themselves, but unlikely to do much to slow the pursuit.

Domain Registrars Hacked to get TLS

Ars Technica reports that three domain registrars were hacked and the access used to obtain certificates for Google domains.

By hacking the registrars and changing the assignment of country-level Google domains for the “gh” (Ghana), “sl” (Sierra Leone), and “as” (American Samoa) top-level domains, the attackers were able to pass automated domain ownership checks required for obtaining SSL certificates.

To be usable, an attacker would have to be able to intercept and redirect the traffic between a user and the compromised domain, and the user would have to be attempting to connect to the Google domains in that country TLD in the first place. The attack may have been targeted against those specific countries, or may have simply been an opportunistic attempt to harvest credentials. Conceivably, the certificates could be used on malicious WiFi networks to try to capture user sessions from other Google domains and services.

Google has already implemented filtering for the specific certificates in Chrome, but these fixes do not help other browsers or services, and Google says it may not have identified all the compromised domains. Google also cautions that the domains of other companies were also compromised, and that those companies must take independent action to protect their users, but the impacted companies were not provided.

Hacking Lawnmowers

Researchers found a series of vulnerabilities in the Mammotion robot lawnmower platform. After spending “a few days on Mammotion’s cloud”, they demonstrated an admin account takeover and a full dump of all 337,000 customers, and for the cherry on top, unauthenticated access to first-person mode on mower. In case you wanted to help tidy up someones lawn or just go for a drive around the neighborhood.

After finding previous security issues in Mammotion products which were not, to put it delicately, fixed according the current norms of security patching in the industry, the company was on the radar.  In addition to discovering that there was no rate limiting on brute-forcing account recovery and changing any users password, the team also found that factory systems lacked any authentication at all, hard-coded authentication tokens were baked into the firmware, and it may be possible to add any customer’s mower to any account.

After repeated attempts by the team to get the company to set up security contacts and respond to the vulnerability reports, it appears that the issues whith are remotely testable have been resolved, but for a fun read be sure to check the article and the email threads as an example of how, probably, you shouldn’t handle security reports as a company.

A Headset Fit For A Hackaday Writer

6 October 2026 at 13:00

I started writing this from a commuter train passing at speed through the outskirts of London, and my headset had just broken. The flexible joint that attaches one earpiece to the headband has snapped, leaving the earpiece dangling on its cable. This is annoying on its own, but what is annoying me enough to write about it is that this isn’t the first time. This is only the latest in a succession of headsets I’ve taken on the road with me has broken, not because of rough treatment, but simply due to flimsy or bad design. What on earth can I do about this?

Failure Built-In

The earpiece of an EPOS headset, detached from its band.
Failure inevitable: the whole headset relied on a tiny piece of plastic in the centre.

The most recent three have been a JVC whose rotating joint allowing the earpiece to lie at a slight angle with my ear has failed, a quite expensive Logitech whose ear sponges failed closely followed by its USB cable, and now an EPOS whose ball joint has failed.

I repaired the JVC and got a bit more life out of it and I’ll have a go at repairing this EPOS, but that’s hardly the point. I’m paying not inconsequential money and I’m getting good sound quality and electronics, but I’m not getting anywhere near the mechanical quality I need. I could buy a set of tough DJ headphones such as the Sennheiser HD25, but they don’t come with a microphone, they’re not a headset.

So if I can’t buy a decent headset without spending military grade money on one from an F16 fighter, what can I do to make my own? I’m an engineer, damnit!

At its most basic, a headset is a springy band that goes over the head, with an earpiece at its end. But a human head is not a cube with vertical parallel sides, it’s a complex shape and every one is different. So those earpieces have to have some “give” in them in order to fit comfortably against the ear. In the simplest case this is achieved by giving the earpiece a soft surround that moulds itself to the ear, but most headsets incorporate some articulation. The earpiece must rotate a little around a vertical line parallel with the ear, and also with a horizontal line at right angles to the axis of the ear. The EPOS managed both axes by means of a ball joint, while the JVC had a stirrup with pins to achieve the horizontal motion, and a circular joint — the part which broke — for the vertical. In both case the weak point was a thin part of the plastic moulding which broke, on the EPOS a short stalk for the ball in the ball joint, and in the JVC a similar stalk for the circular joint. Any design I come up with must avoid this type of weak point, and spread the load of an earpiece over considerably more material than my broken headset.

So, How Do I Make This Thing?

A 3d printed spring in white plastic
This is my test spring print, and it’s rather irresistible to play with.

For the headband I could re-use the ones I have from my broken headsets, find one of the many 3D printable designs online, or the choice I took, design my own. And since I can re-use the drivers, microphone, and electronics, aside from designing a physical adaptor to take them, my problem becomes one of making a tough version of that articulated joint. And there my choice is to either replicate the ball or rotating joints of the originals but in a much tougher form, or to make a one piece design with elasticity and flexibility in the planes I need. It’s time to break out OpenSCAD. I like things I can print in one go when it comes to builds like this one, as when it comes to assembly there is invariably a weak point where the different parts meet. So I’m going for the latter choice, and making my earpiece mount on a spring rather than a two-piece joint. My spring is a simple zig-zag leaf spring, which is both robust, and has some movement in X and Y rotational axes, and Z displacement. It’s an OpenSCAD library, and my little test print has all the compulsive manipulation of a fidget toy.

So with a bit more OpenSCAD bashing I have a sliding print in place headband with my springs attached. You can take a look at it in this GitHub repository, and even modify it for a broken donor headset of your own if you want.As I write this it’s not yet printed, the 3D printer gods have not smiled upon me with extra speed. Will my crafty print in place springs solve the problem? At least if they break I have only myself to blame.

❌
❌